The Cat Behind the Breach: Tracing TeamPCP’s Digital Trail
TeamPCP has appeared under several identities across underground communities, with activity that has evolved beyond a single criminal service or attack method. Names such as PCPcat, ShellForce, DeadCatx3 and CipherForce appear across different parts of the ecosystem, while the group's presence has also extended into underground forum administration and Telegram communications. Other names associated with the wider ecosystem include Persy, Percy PCP, Persy_PCP and UNC 66780, adding further layers to an already fragmented identity set.
The activity surrounding these names covers several parts of the underground economy. PCPcat has appeared in reporting around exploitation of Next.js and React environments, CipherForce represents the ransomware side of the activity examined here, and TeamPCP itself has claimed a role in managing underground forum infrastructure. At the same time, material surfaced through StealthMole describes activity involving private source code, developer credentials, cloud environments and software supply chains.
The recurring PCP and cat branding offers a visible thread through some of this activity, but the stronger connections come from the infrastructure and account-level artifacts behind it. Following those links provides a different picture of TeamPCP than looking at any single alias in isolation.
The First Signal: CipherForce
The investigation did not begin with a search for TeamPCP. The initial lead came from StealthMole's Ransomware Monitoring module, where the group CipherForce was indexed alongside 19 victims recorded between One of the results that immediately stood out was “BMW Group Internal Documents/Recon”, with a detection date of March 26, 2026.
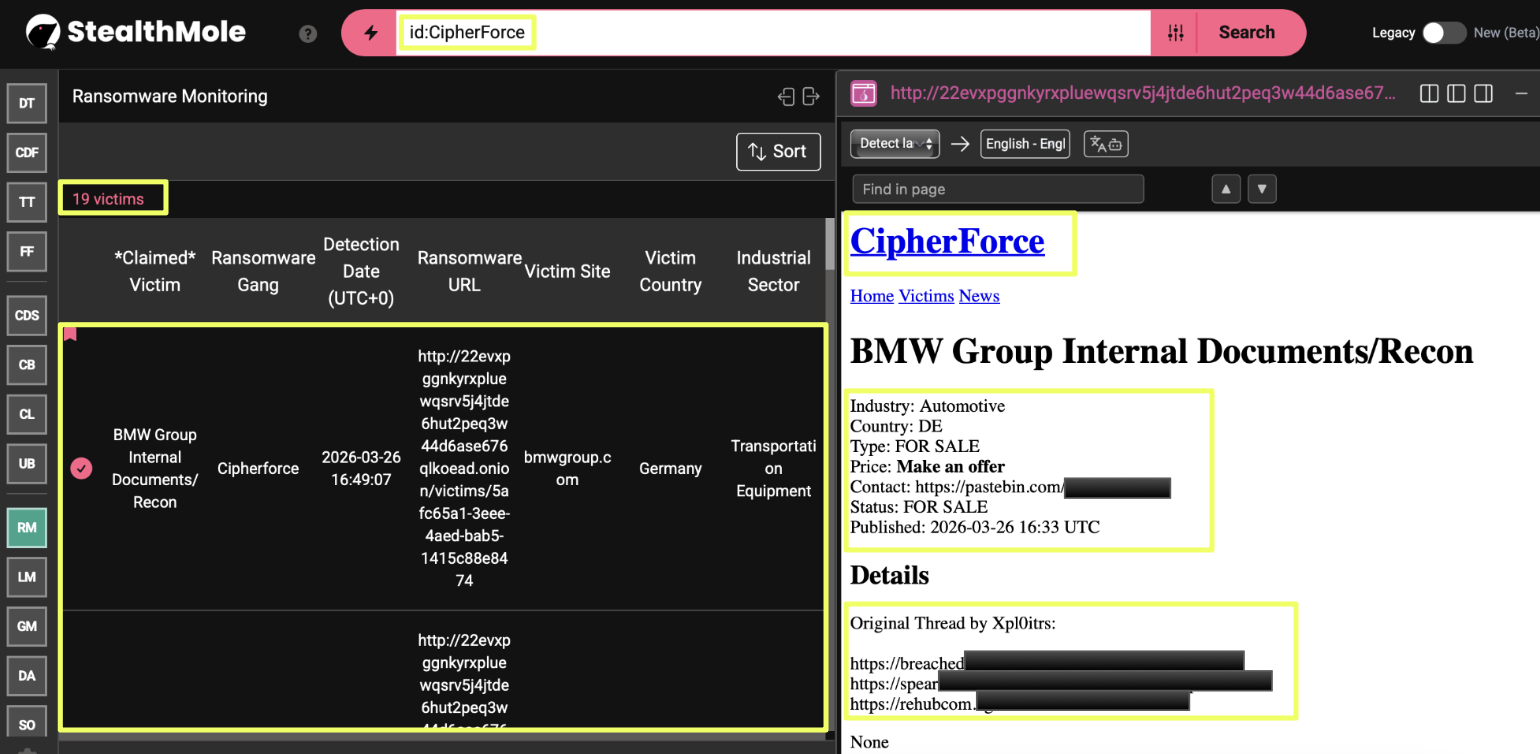
The victim count provided the initial scale, but the BMW record was more useful for what it revealed about how the operation was presenting stolen material.
The associated CipherForce victim page was:
- http://22evxpggnkyrxpluewqsrv5j4jtde6hut2peq3w44d6ase676qlkoead.onion/victims/5afc65a1-3eee-4aed-bab5-1415c88e8474
It listed BMW Group Internal Documents/Recon, classified the industry as Automotive, the country as DE, and marked the material FOR SALE. The price was listed as Make an offer, with the contact field pointing to:
- https://pastebin.com/raw/6********3
The page included the heading “Original Thread by Xpl0itrs” and the following references:
- https://breached.**/threads/bmw-group********3
- https://spear.**/Thread-Com-Boss-BMW********s
- https://rehubcom.**/thre********3/
The listing therefore gave the investigation several ways forward. CipherForce was not only represented through a victim-monitoring record; its page contained an onion infrastructure address, an external contact mechanism and references to several underground platforms.
The CipherForce Infrastructure
The onion address associated with the BMW listing was further investigated in StealthMole’s Darkweb Tracker.
- 22evxpggnkyrxpluewqsrv5j4jtde6hut2peq3w44d6ase676qlkoead.onion
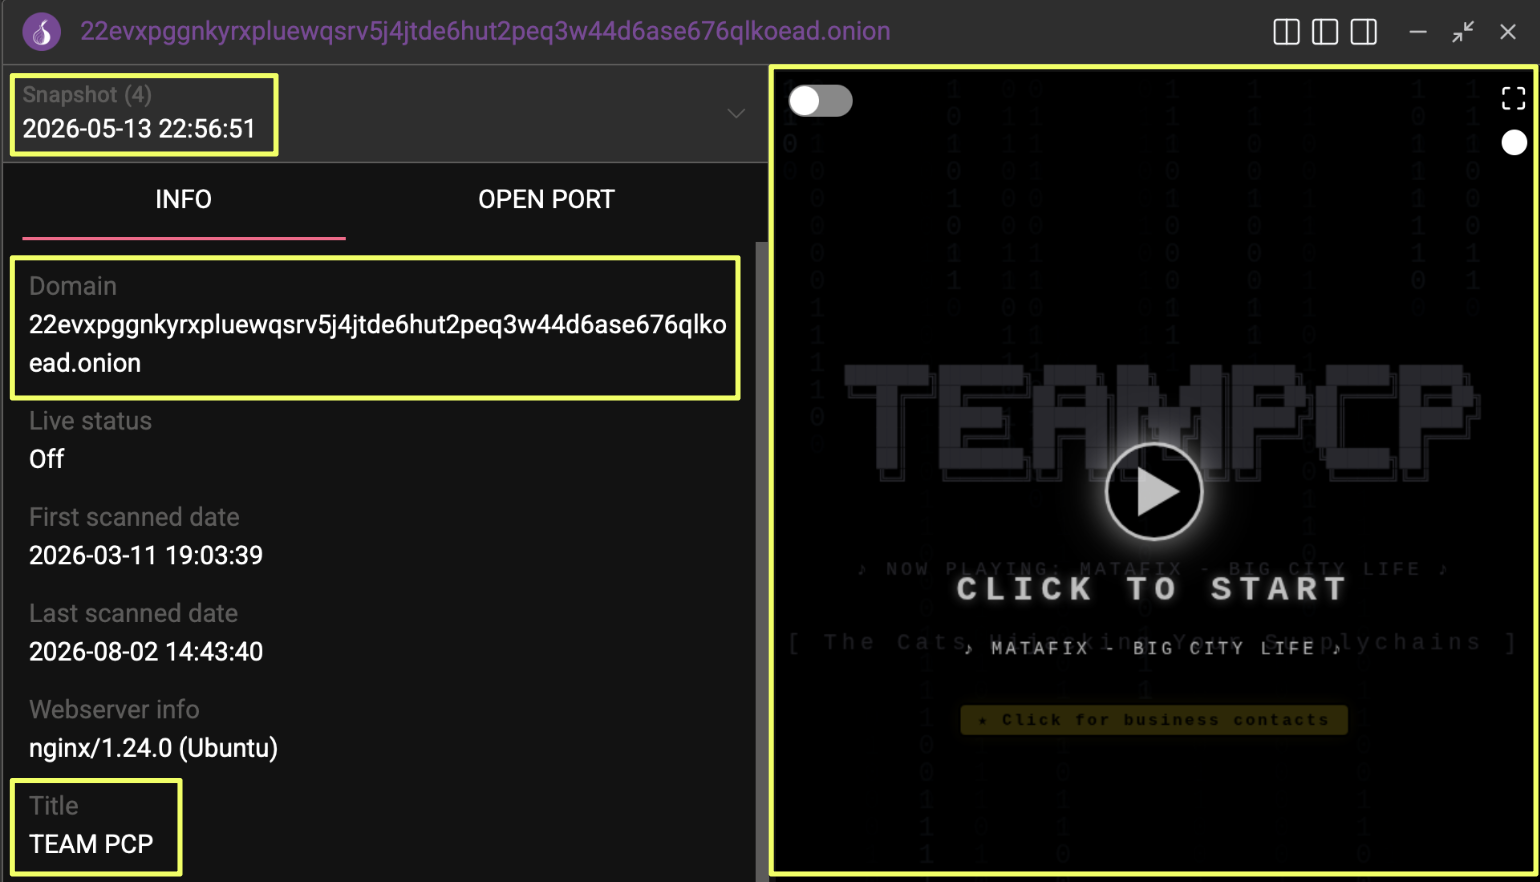
The current site was no longer live, making StealthMole's historical indexing particularly useful. A historical snapshot dated 2026-08-02 showed the site under the name TeamPCP. However, a further look into the historical snapshots showed that in March 2026, the website operated as CipherForce, making TeamPCP a later re-branding.
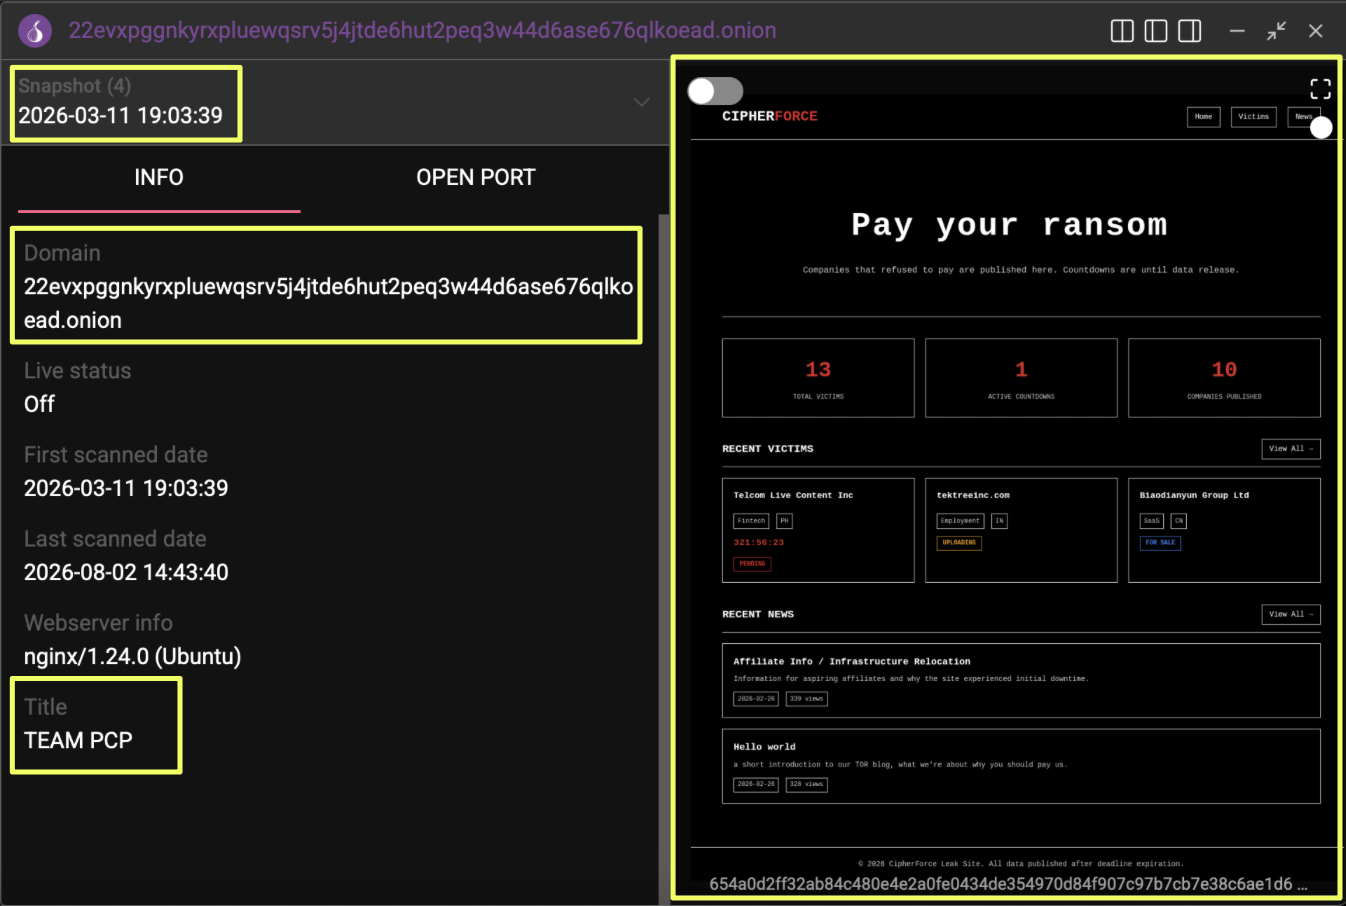
That provided the first direct route into the wider TeamPCP investigation. A subsequent Dark Web Tracker pivot on the onion domain produced two identifiers:
Session ID
05a04c*******************************************5823e
TOX ID
BA8***********************************************069F2
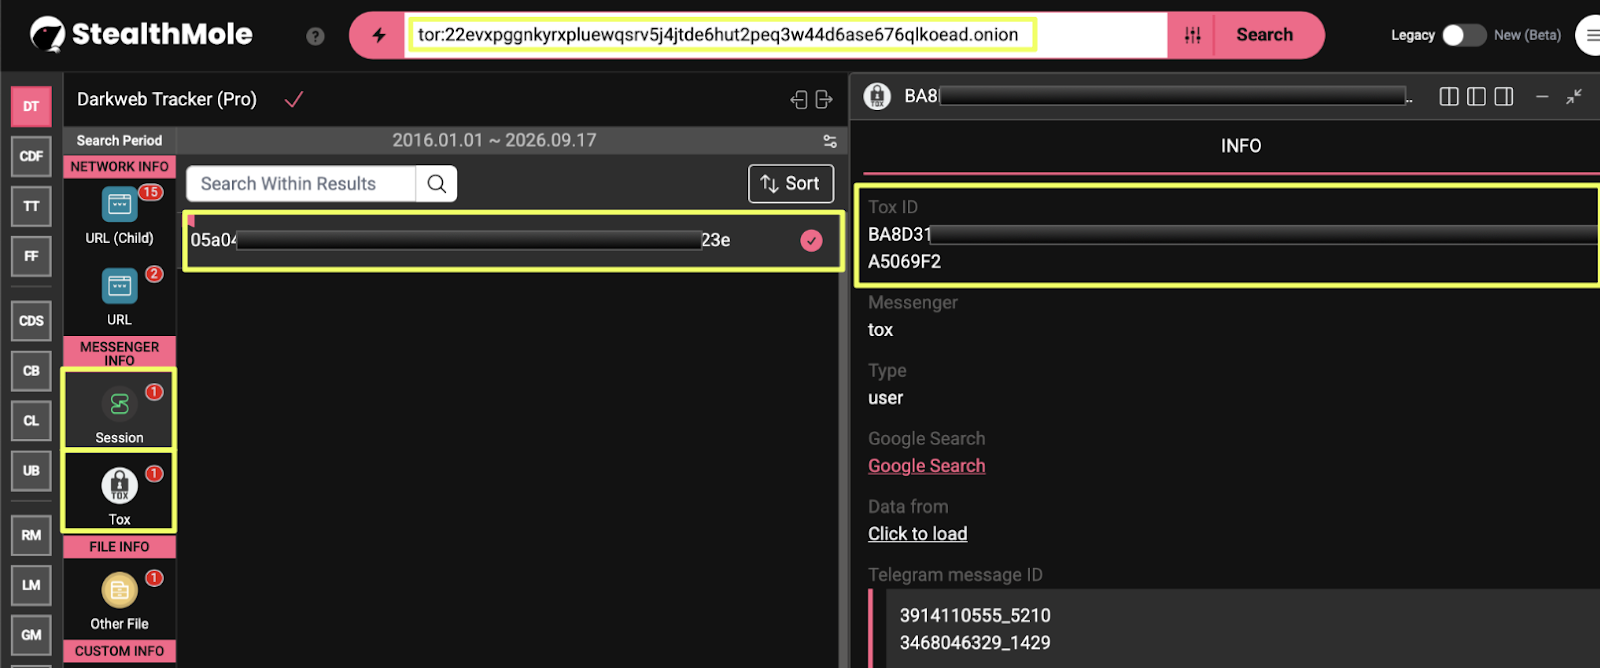
Searching the Session ID expanded the investigation beyond the CipherForce onion itself and surfaced material across additional underground services. These identifiers allowed the investigation to follow the same technical thread into places where the name CipherForce did not necessarily appear.
One of the more relevant results was a Breached thread titled “Signs of life amidst rumors”:
- https://breached.**/threads/signs-of-life-amidst-******1/
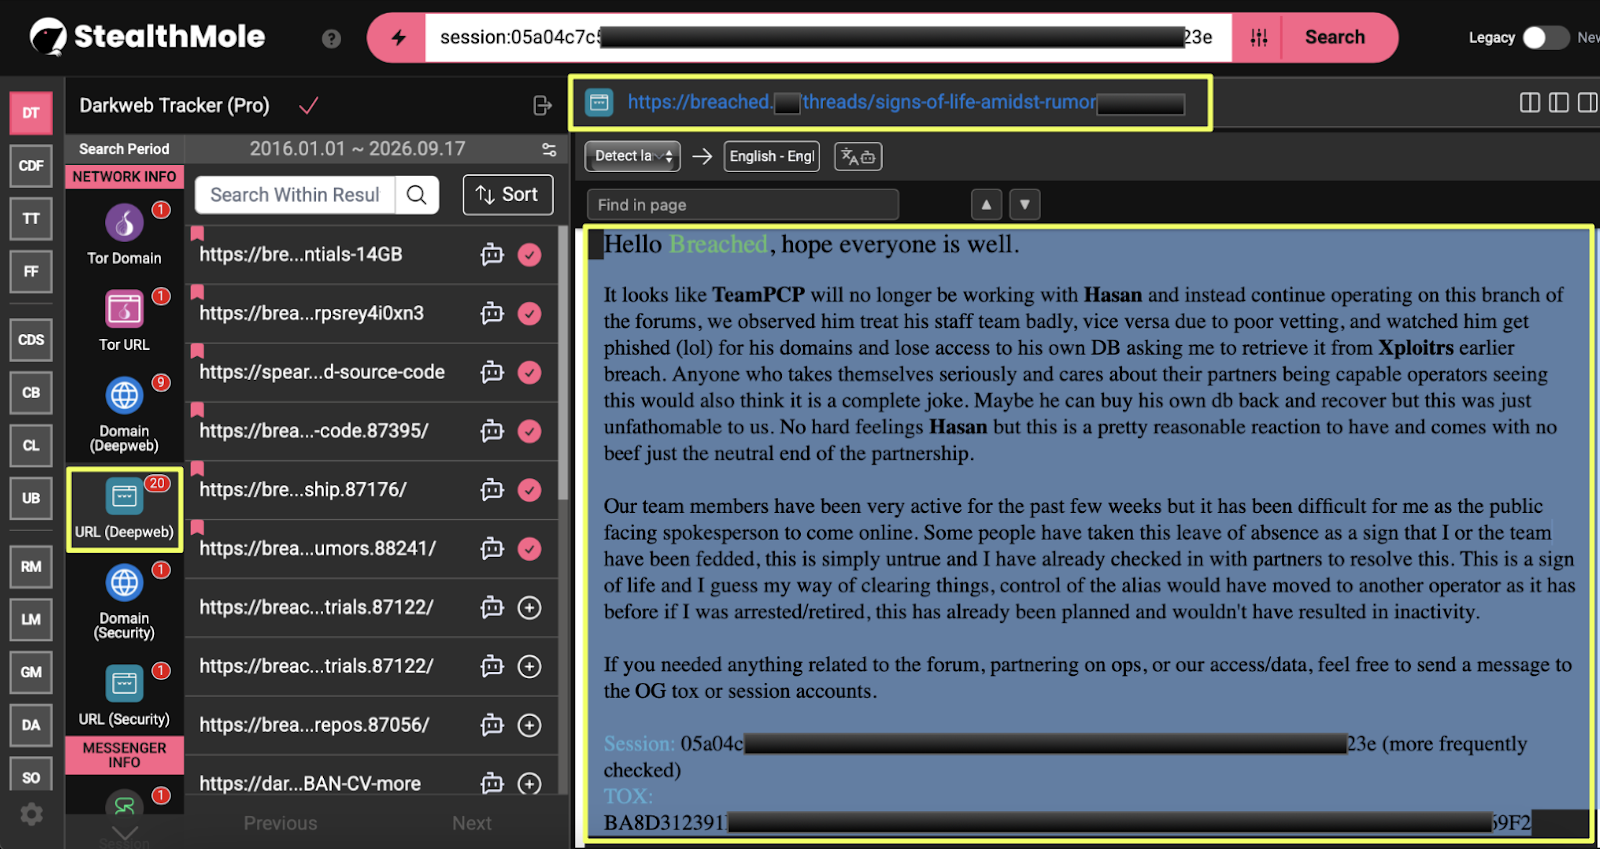
The post said TeamPCP would no longer work with Hasan and would instead continue operating on that branch of the forum. It made a number of claims about Hasan's treatment of staff and vetting, alleged that Hasan had been phished for domains and had lost access to his own database, and said that TeamPCP members had remained active despite difficulty reaching the group's public-facing spokesperson.
The same post rejected speculation that the team had been arrested or “fedded.” It also described a contingency in which the TeamPCP alias could be transferred to another operator if the poster was arrested or retired, and directed people requiring forum matters, operational partnerships or access/data toward the “OG tox or session accounts.”
It is also worth mentioning that the post displayed the same Session ID and TOX ID identified during the CipherForce investigation.
TeamPCP Takes a Seat at the Table
The next major finding came from TeamPCP's own activity on Breached.
On 16 May 2026, the account published a thread under the title “TeamPCP Partnership / Forum Co-Ownership.”
- https://breached.**/threads/teampcp-partnership-forum-co-ownership*****6/
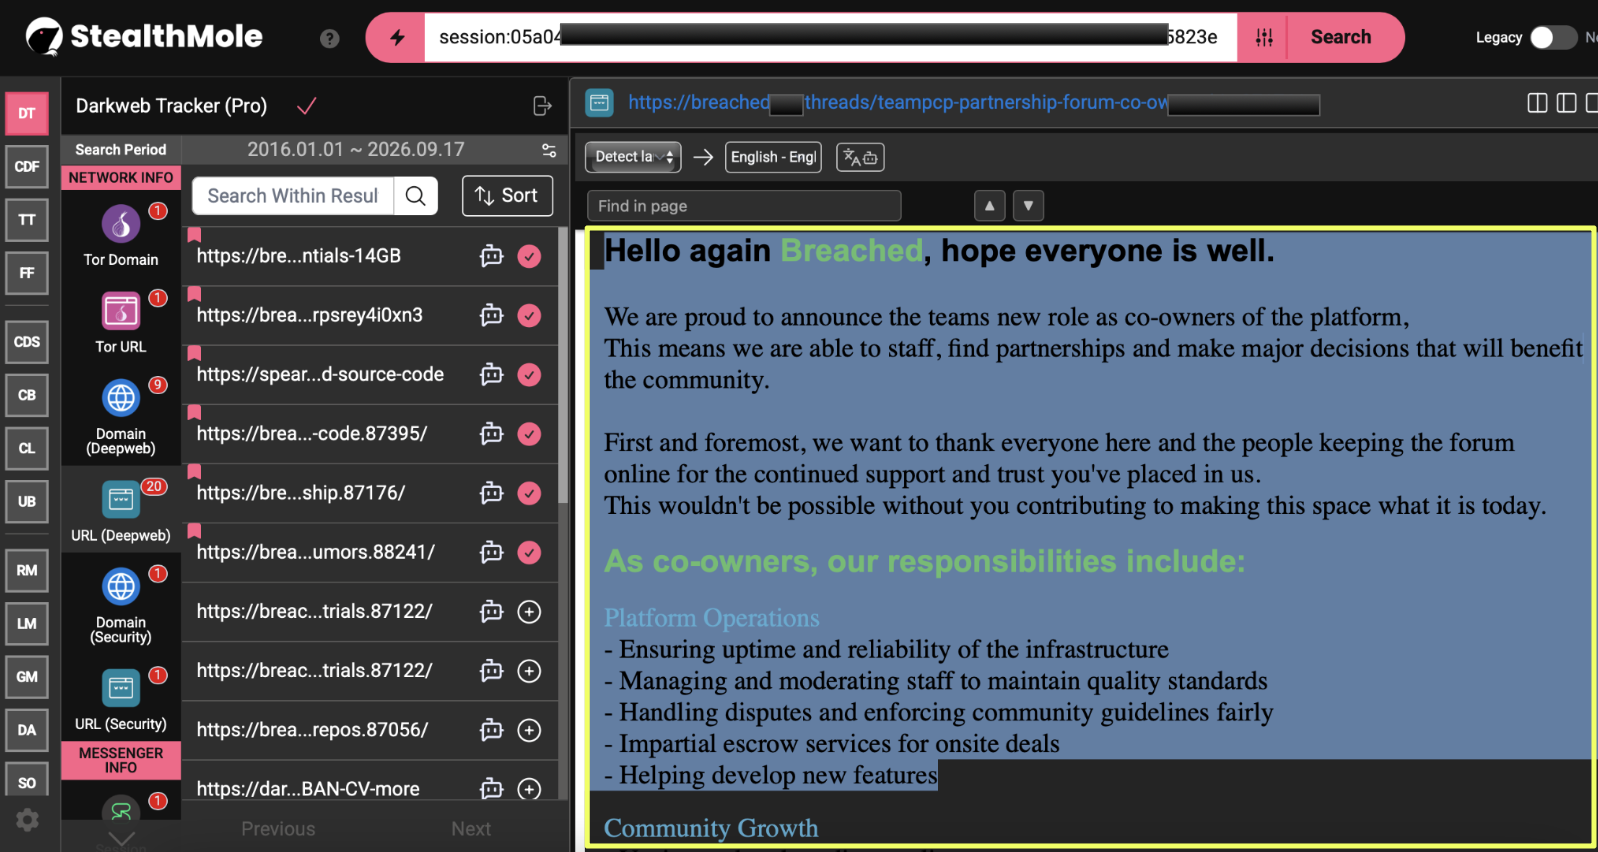
The post announced TeamPCP's new role as co-owners of the platform, with authority over staffing, partnerships and major decisions. The responsibilities described by the account included infrastructure uptime and reliability, staff management, disputes, community guidelines, escrow services, new features, partner vetting, premium resources and databases, contests, community feedback and the verification of databases and tools.
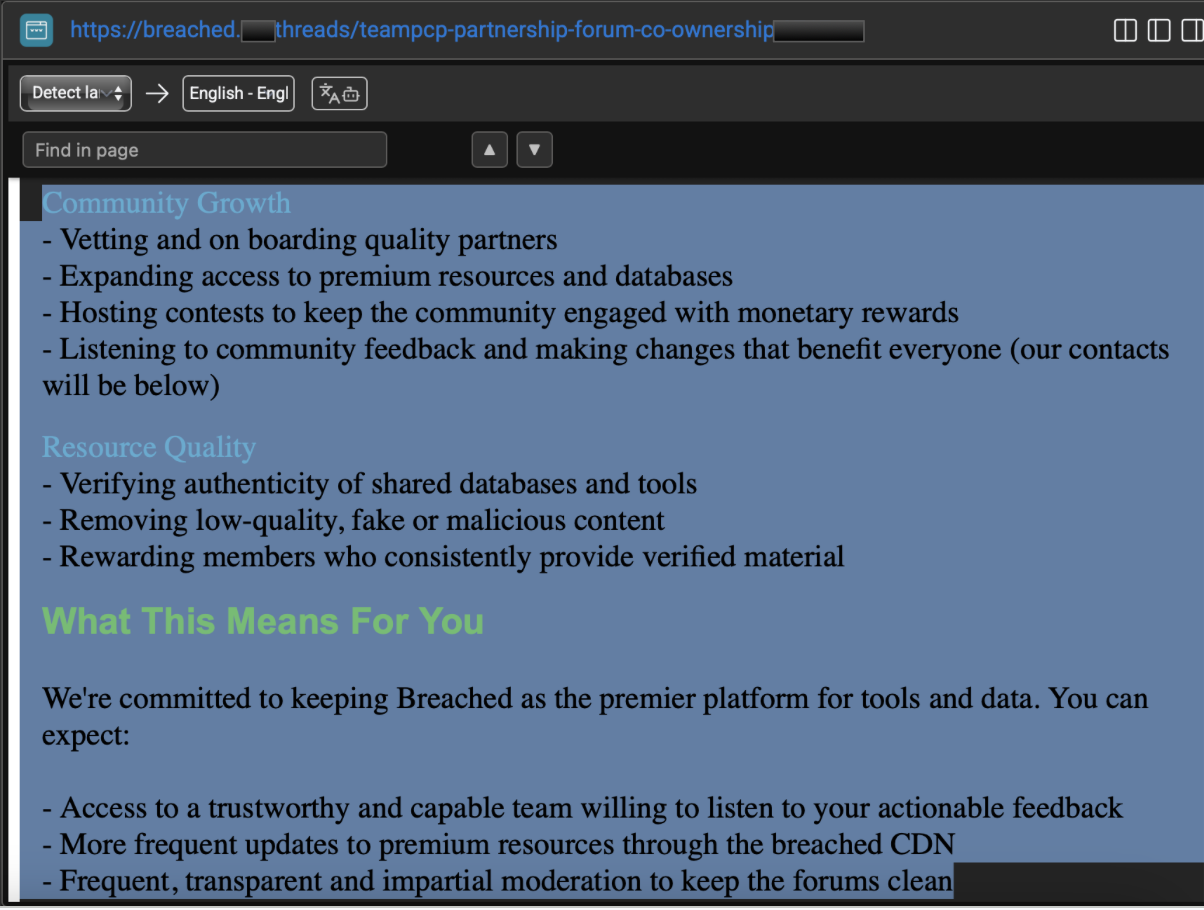
The account also described a role in removing low-quality, fake or malicious content and rewarding verified contributors. It said the platform would provide more frequent updates to premium resources through the Breached CDN and closed with the signature:
“The PCP Cats.”
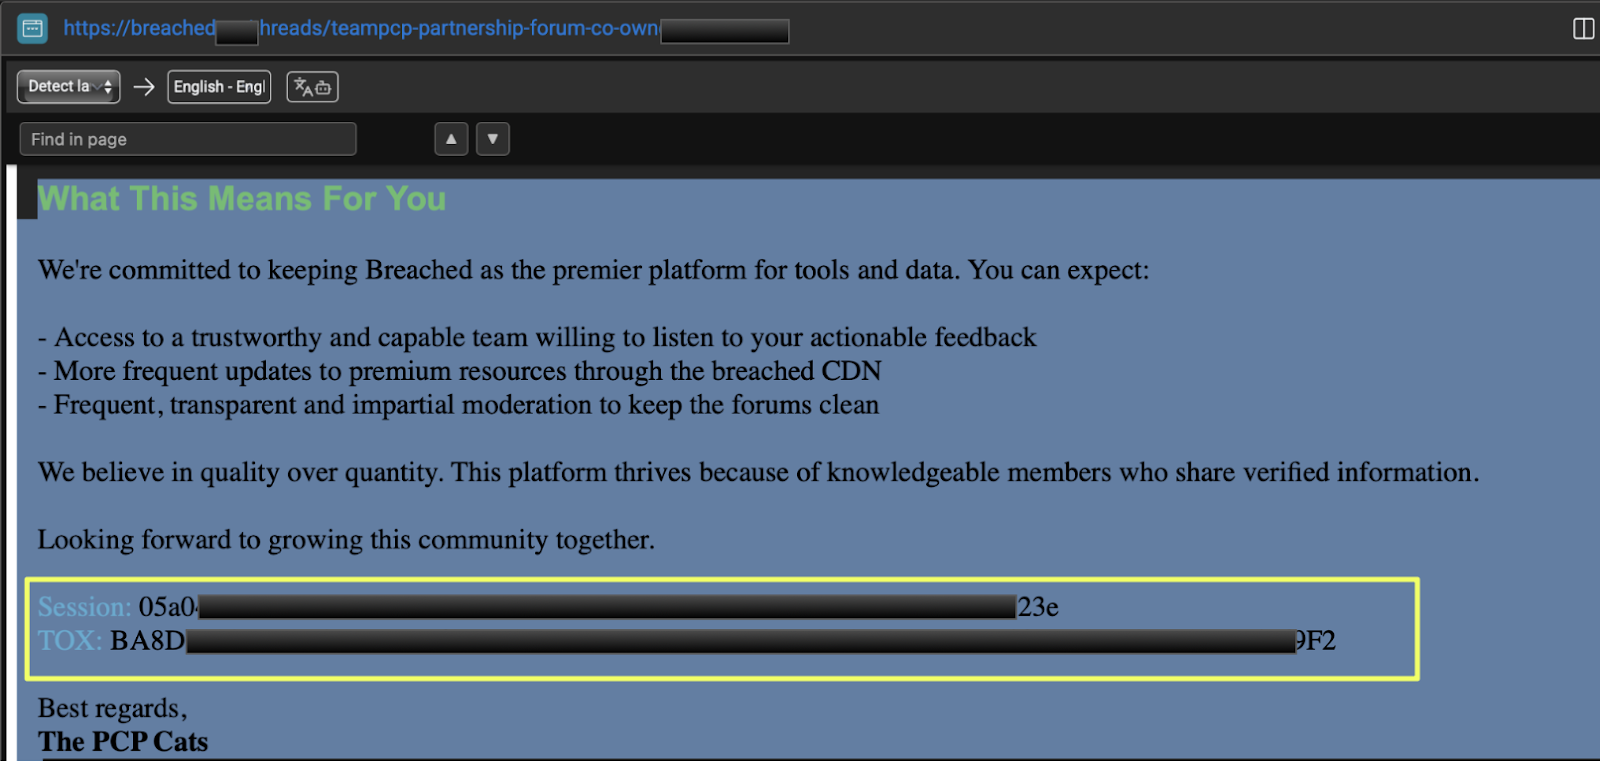
The same Session ID and TOX ID appear with the post:
- 05a0**************************************************5823e
- BA8***************************************************069F2
A StealthMole snapshot dated June 2026 showed the TeamPCP account with the role:
Co-Owner / Staff Member / Co-Owner
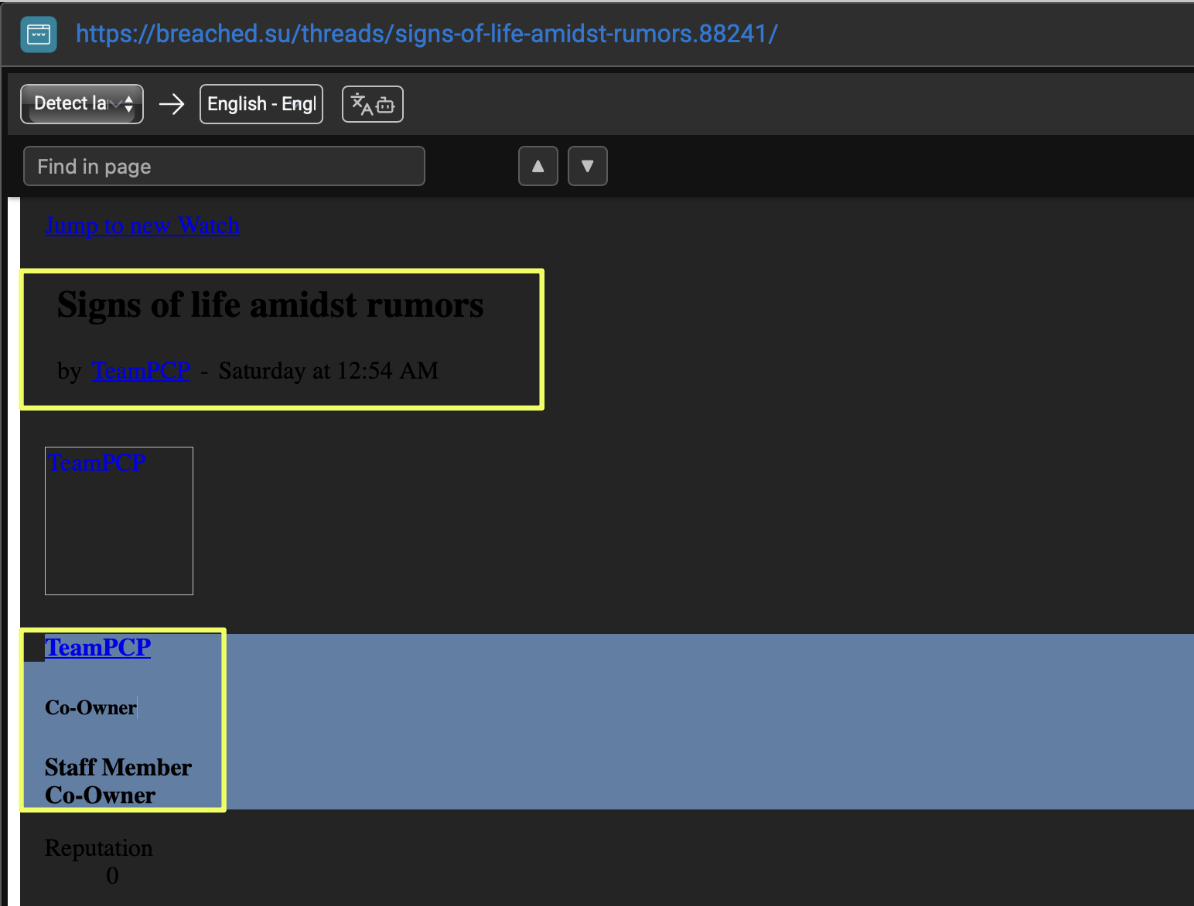
This was a notable shift in the investigation. TeamPCP was not simply appearing in material connected to attacks or stolen information. Its own account was presenting the group as part of the infrastructure and administration of an underground platform.
The responsibilities listed in the post also give some indication of the position TeamPCP claimed within that environment. They extended from keeping infrastructure online to managing staff, handling disputes and escrow, vetting partners and deciding what databases or tools should remain on the platform. That is a much broader role than simply maintaining an account on a forum.
The same technical identifiers linking back to the earlier CipherForce investigation were present here as well, giving the developing TeamPCP trail a consistent technical reference point.
What TeamPCP Was Selling
The same TeamPCP identity later advertised something very different.
The post, titled “Internal Github Source Code,” appeared at:
- https://breached.**/threads/internal-github-source-c*******5/
The account was displayed as:
[Co-Owner] TeamPCP
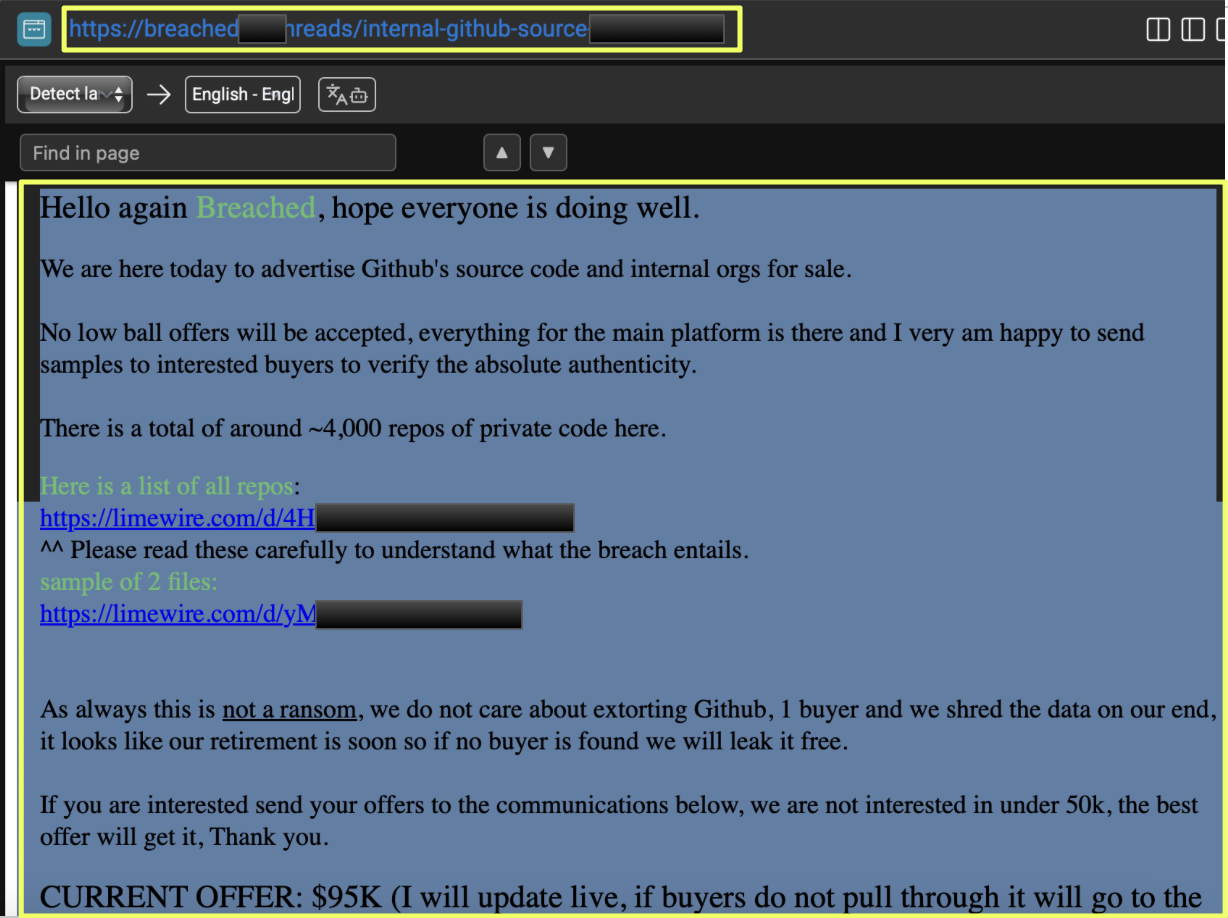
The post offered approximately 4,000 private-code repositories and internal organizations. It provided a repository list at:
- https://limewire.com/d/4HP********b4u
and a sample of two files at:
- https://limewire.com/d/yMx********sN
The minimum offer was $50,000, while the screenshot showed a current offer of $95K.
The seller also went out of its way to describe the transaction as something other than ransomware. The post explicitly said it was not a ransom and that there was no interest in extorting GitHub. Instead, the buyer would receive the data, after which the seller said the data would be destroyed on their end.
There was another detail that would become relevant later: the account said it was retiring soon and that, if no buyer was found, the material would be leaked for free.
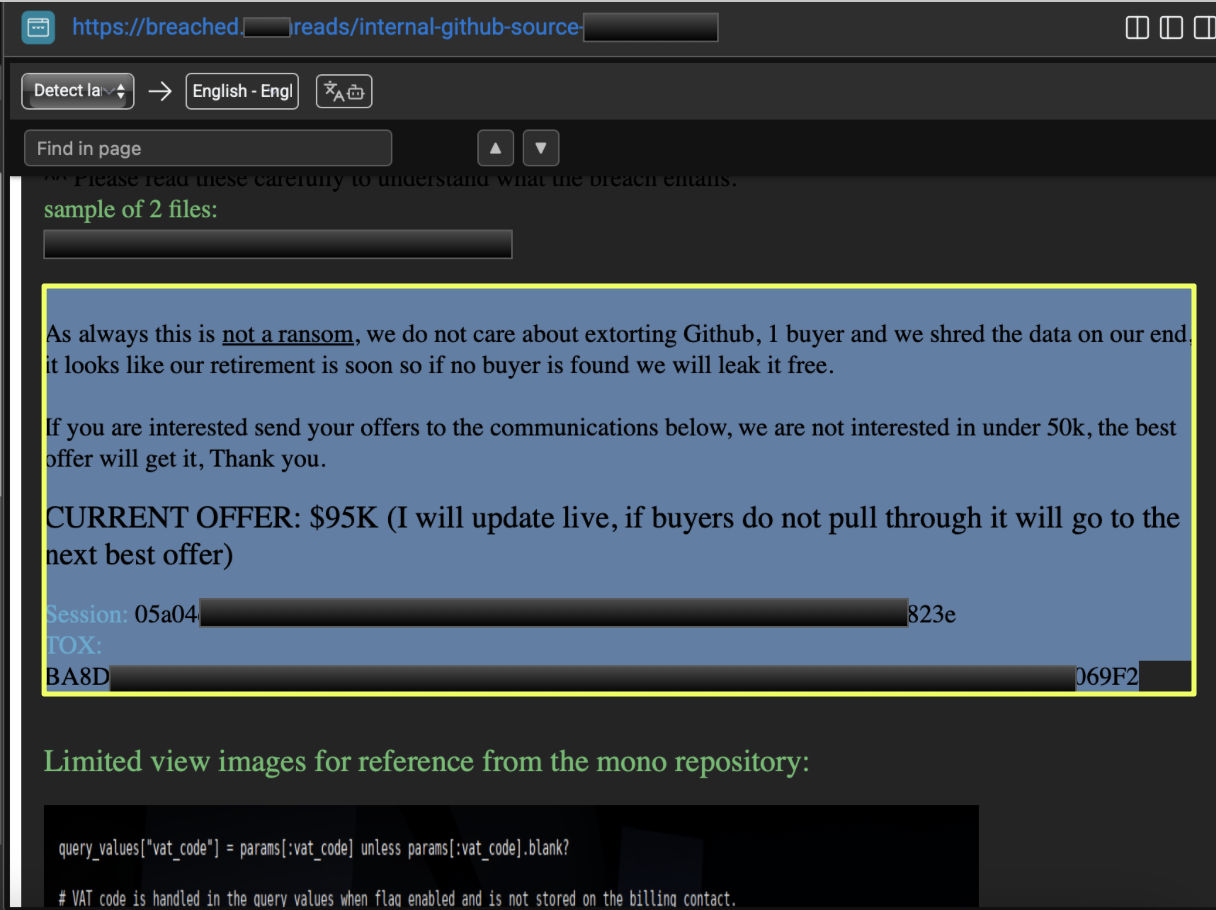
The wording provides a useful look at the group's claimed approach to monetization. The material was being offered as a commodity with a negotiated price, rather than being presented as a ransom demand against the organization whose infrastructure had allegedly been accessed. The $50,000 minimum and $95K current offer also show that the seller was treating the collection as a high-value asset in its own right.
At this point, the investigation had moved from ransomware into another type of underground transaction: the sale of private source code and internal repositories.
One Correlation That Did Not Fit: BulkDMT
The Session ID search also produced a result that looked interesting but could not be safely folded into the TeamPCP story.
The post was:
- https://breachsta.**/topic/selling-access-to-proprietary-trading-firm-150bl*******xn3
It was dated 2025-09-11 and authored by BulkDMT on Sellers Place.
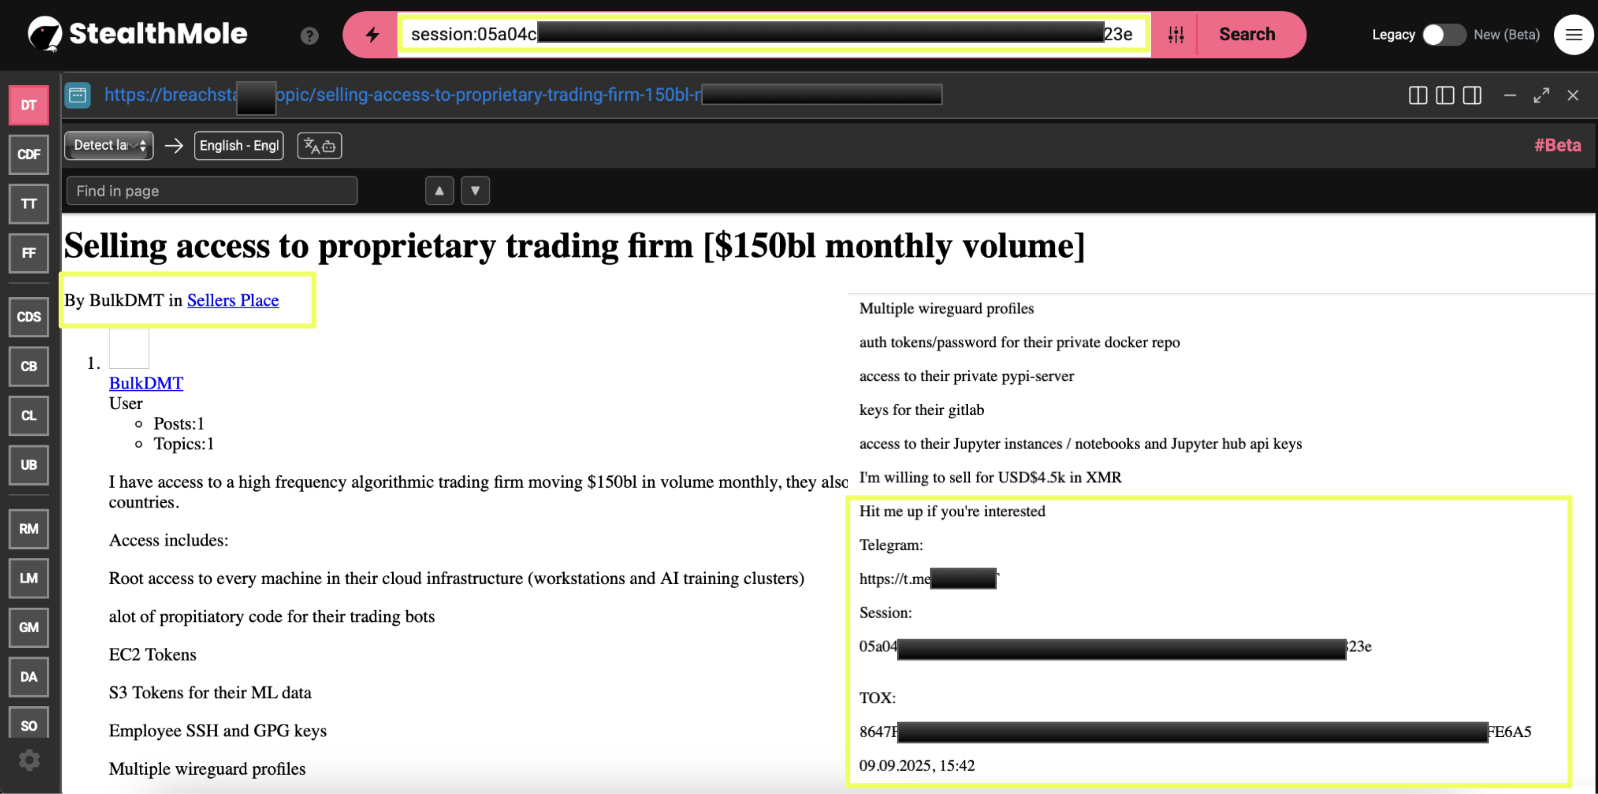
BulkDMT claimed access to an HFT proprietary trading firm with $150B monthly volume, including root access to cloud infrastructure, workstations and AI clusters, trading bot code, WireGuard profiles, authentication tokens and passwords, private Docker repositories, private PyPI, GitLab keys, Jupyter instances and API keys. The asking price was USD 4.5K in XMR, with the Telegram contact:
- https://t.me/b*********T
The Session ID was the same:
- 05a04****************************************95823e
But the TOX ID was not. BulkDMT was associated with the following TOX ID:
- 8647********************************************E6A5
That difference matters. So does the date, which predates the CipherForce activity examined in this investigation, and the fact that the post was authored by BulkDMT rather than TeamPCP.
The shared Session ID was enough to make the result worth examining, but not enough to attribute the activity to TeamPCP or CipherForce. It remains an unresolved correlation rather than part of the group's established trail.
The GitHub Sale Leads to Telegram
Then the same session ID was further investigated in StealthMole’s telegram tracker, which indexed two messages mentioning the same session ID. The message, originally posted in a channel named “Breaches”, referenced the TeamPCP GitHub source code thread:
- https://breached.**/threads/internal-github-source*******/
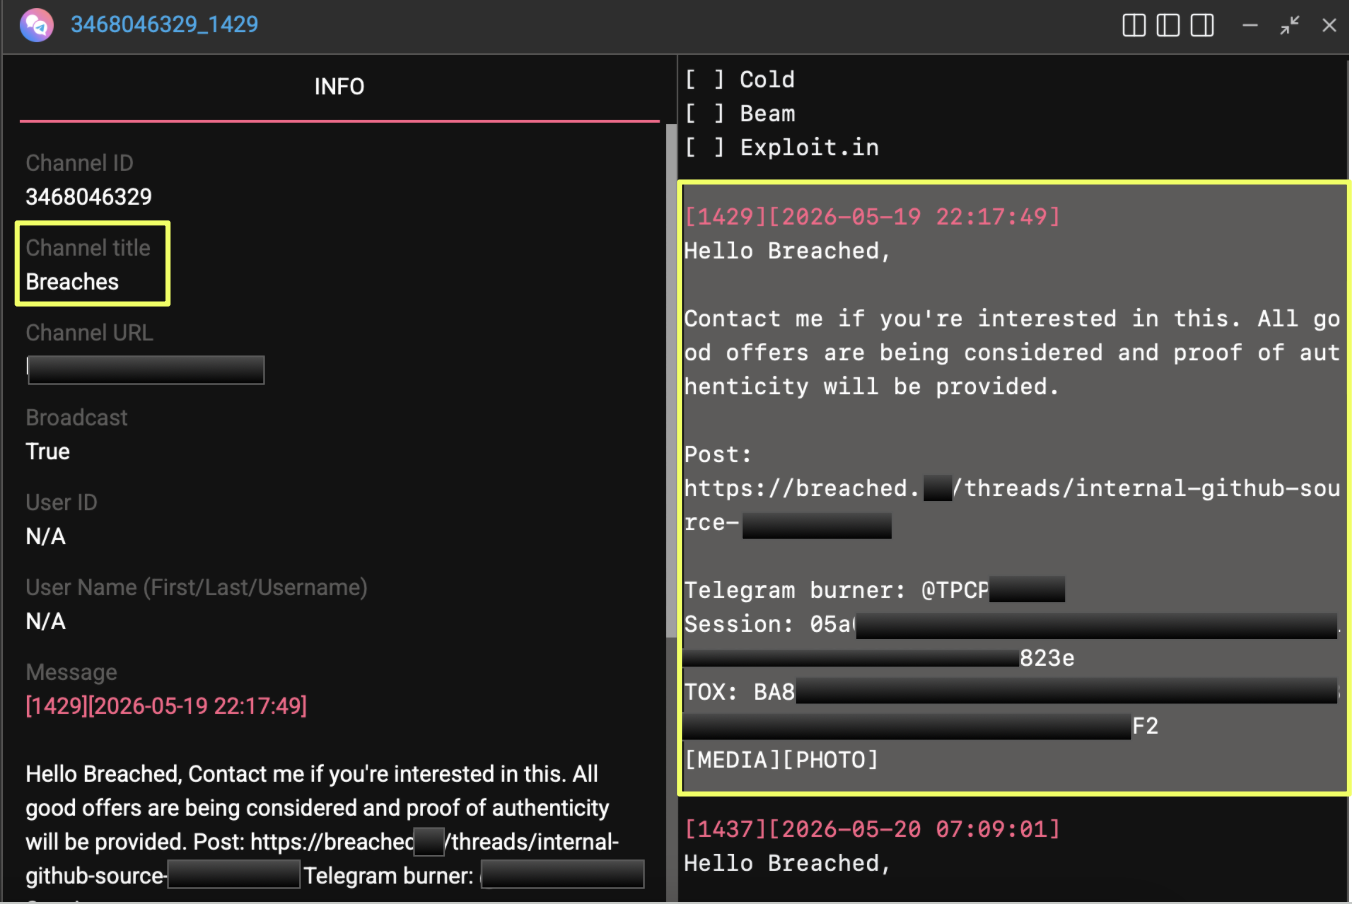
It also contains a telegram user ID, which was labelled as a burner telegram:
- @TPCP******1
Moreover, the message also mentioned the same Session ID:
- 05a04**********************************************5823e
together with the same TOX ID:
- BA8D**********************************************5069F2
The significance of this result lies in what it adds rather than what it repeats. The GitHub thread had already established the source-code sale. The Telegram result provided a new account identifier associated with the communication surrounding that sale.
T-PCP: Following the Account
The newly found telegram account was further investigated using StealthMole’s telegram tracker. The tool indexed an active user account associated with the username.
- Telegram User ID: 8542877306
- First name: T-PCP
- Username: @TPCP********1
- Profile creation date: 2026-08-08
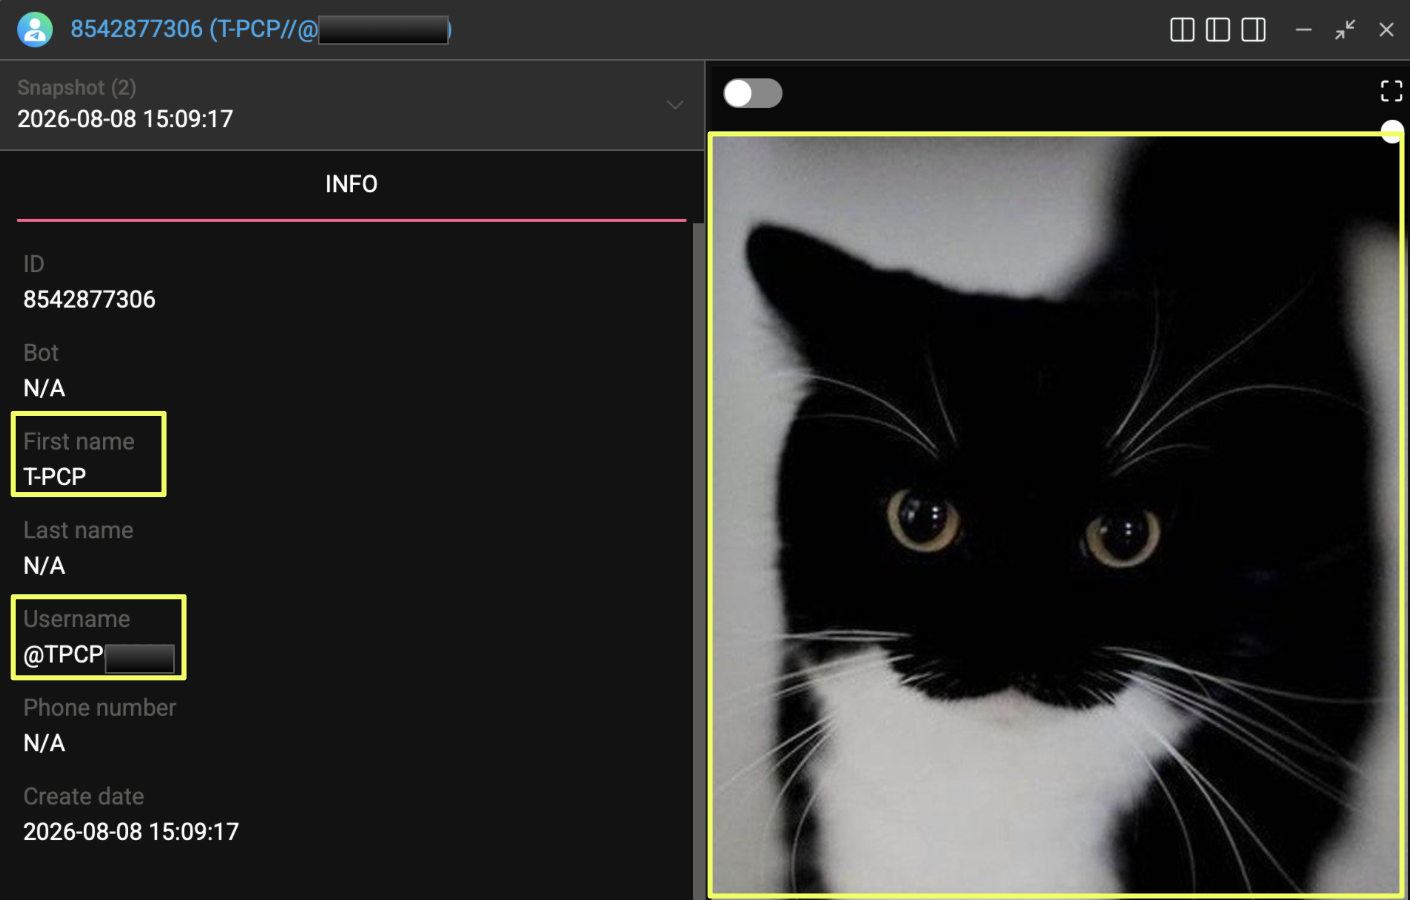
The account also used the same black-cat image as profile picture, seen on other TeamPCP-related accounts. It should be further noted that this account also appeared in multiple breached related telegram channels, including:
- https://t.me/Br********zzi
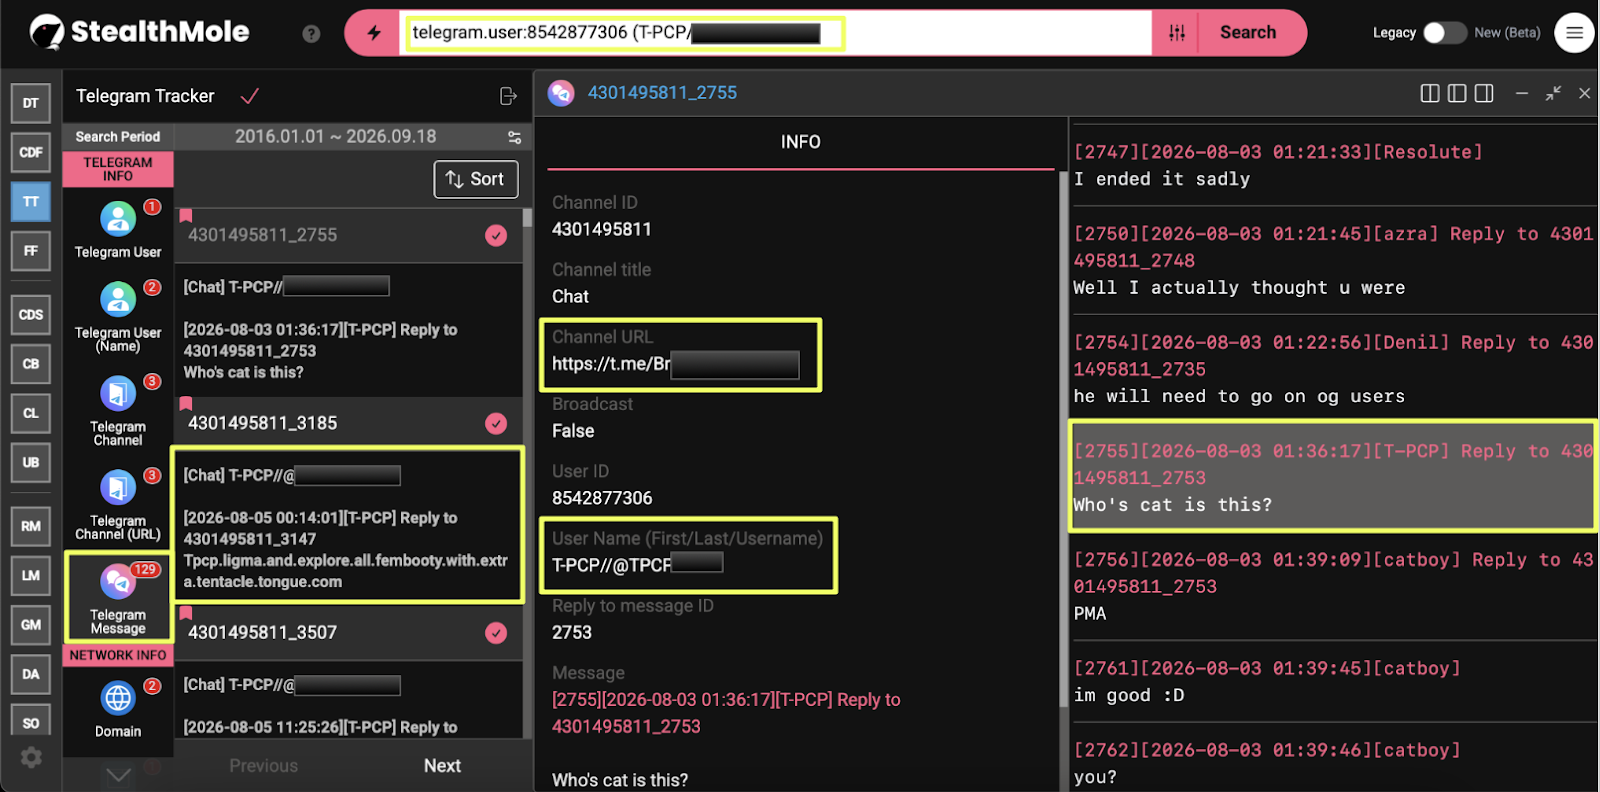
The direct account record was useful because it provided more than a username. T-PCP is itself a TeamPCP-style identifier, and the account could be examined independently after first being surfaced through material referencing the TeamPCP GitHub sale.
That does not establish the real-world identity of the operator. There is no phone number or other direct identity information in the available record. What it does establish is a consistent account-level trail connecting the Telegram identifier to the wider TeamPCP investigation.
The account later appeared in a more contentious discussion.
On 27 August 2026, a message in the Data Hoarder channel stated: “Breachforums owners @hello*******2 and @TPCP*******1 have been arrested.”
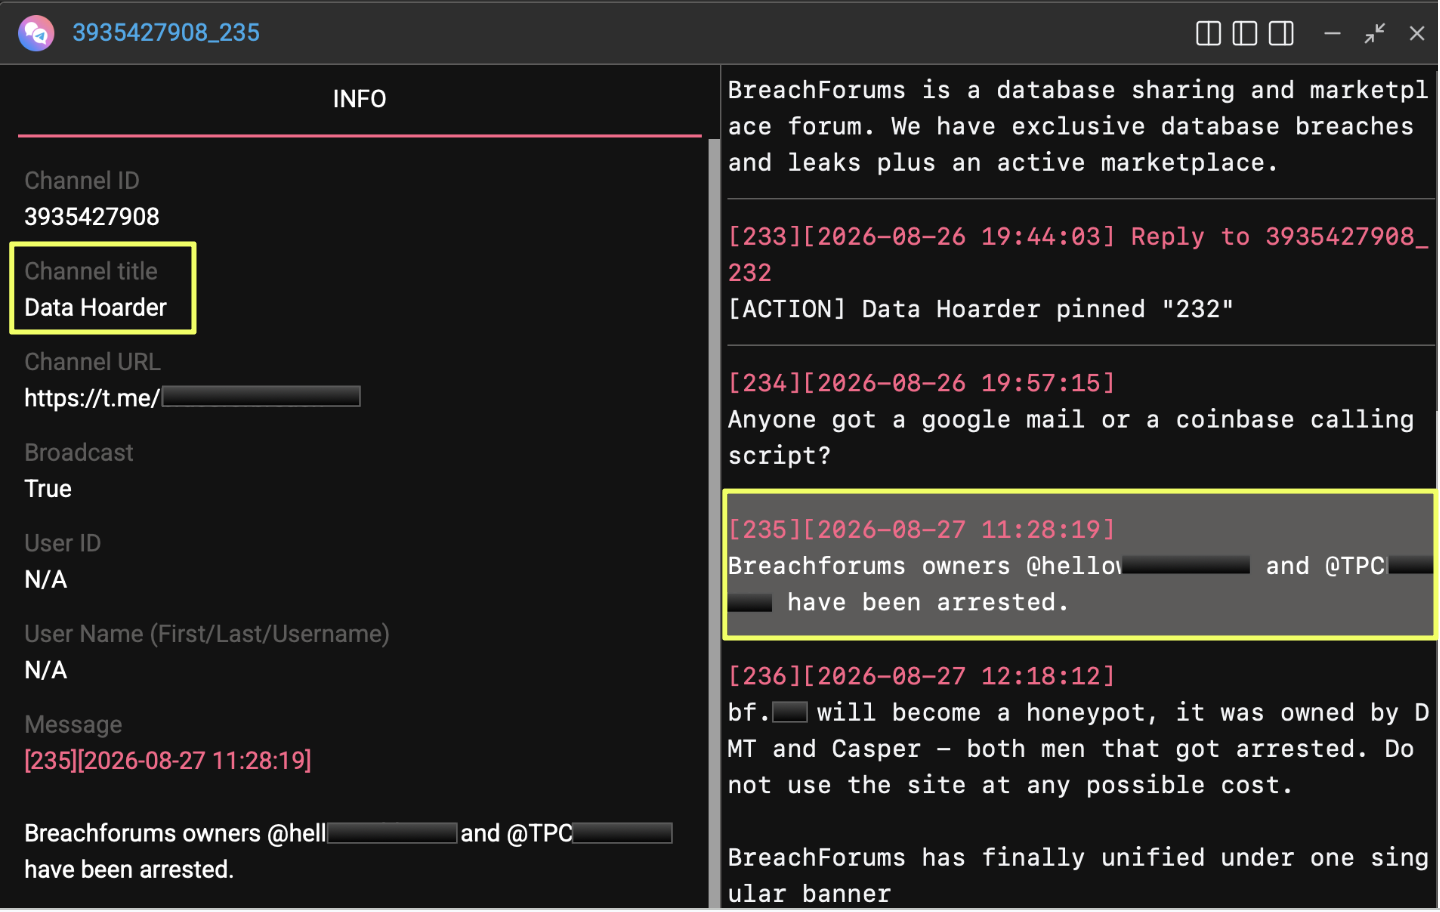
The surrounding messages also claimed that bf.** would become a honeypot, discussed previous ownership and warned users against using the site.
Those statements remain third-party Telegram claims. The existence of the messages can be documented, but the available evidence does not independently establish that bf.** became a honeypot.
The Cat Across Platforms
The TeamPCP identity carries a recurring visual marker across the platforms surfaced through StealthMole. A Dark Web Tracker search for Team PCP returned a Spear CX profile:
- https://spear.**/User-TeamPCP
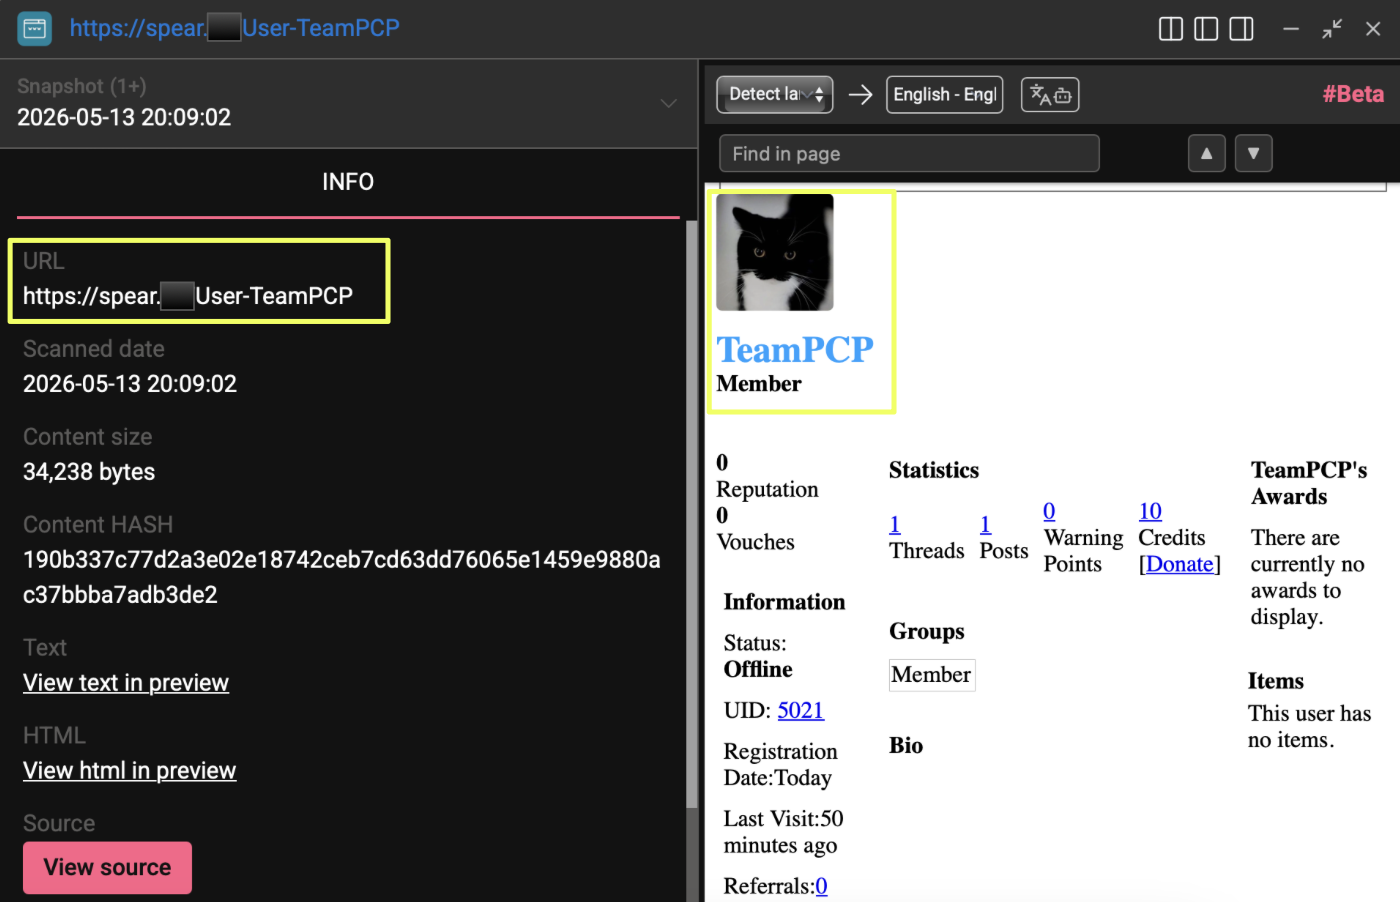
The profile uses the same black-cat avatar seen on the T-PCP Telegram account. On its own, an avatar would be weak evidence, but its reuse becomes more useful when viewed alongside the other TeamPCP artifacts already identified.
StealthMole also surfaced the TeamPCP-branded image:
- https://supplychain.breached.st/teampcp.jpg
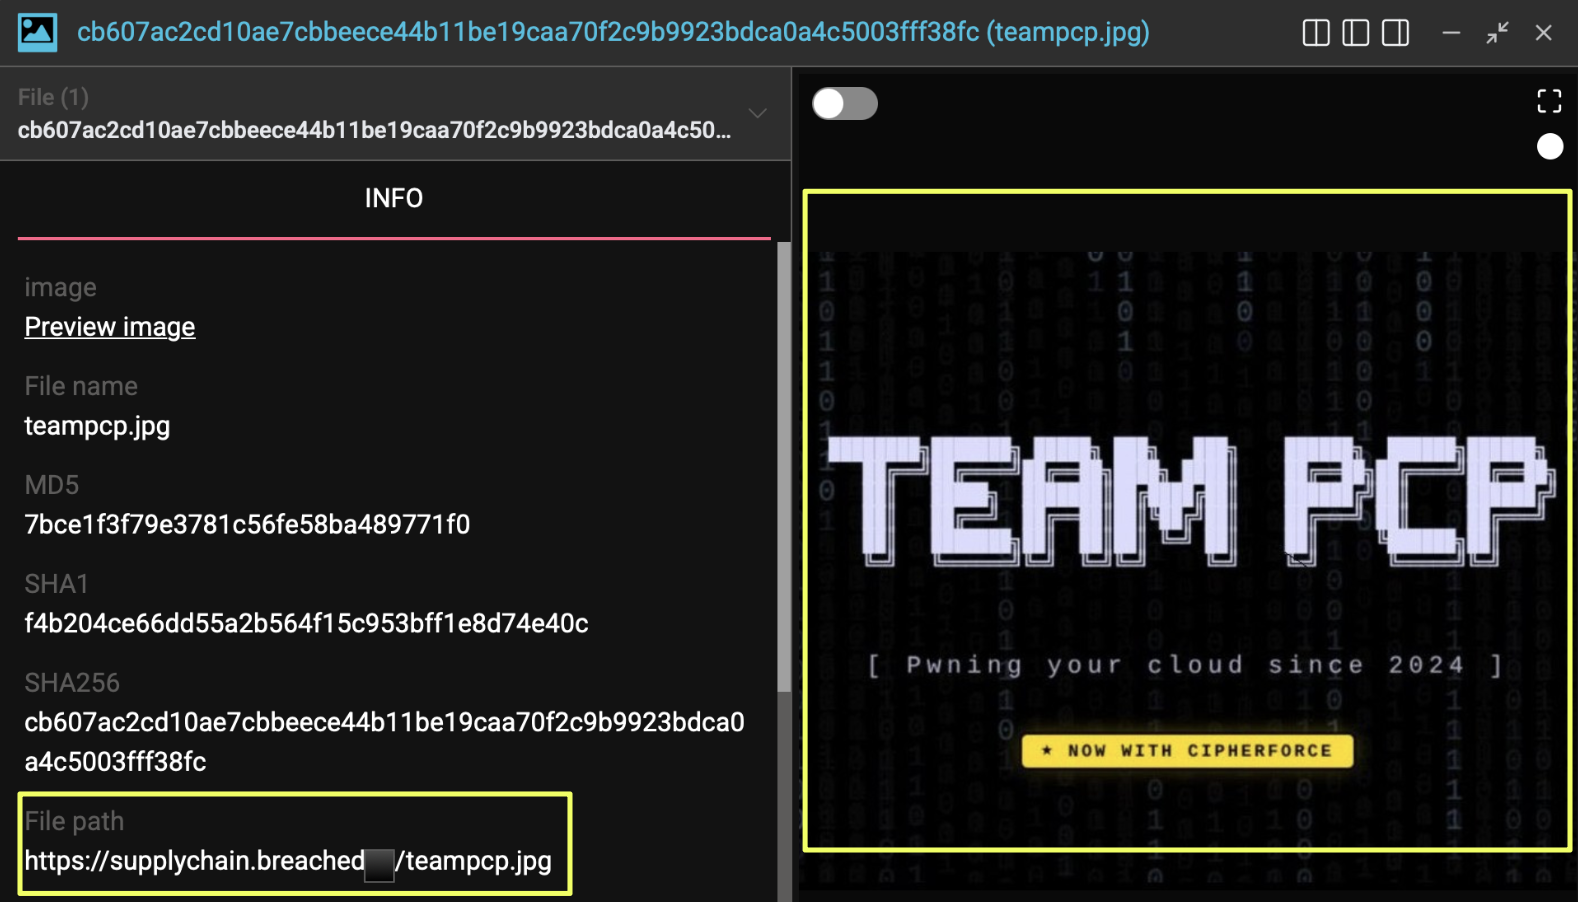
The image carries TEAM PCP branding and the wording “NOW WITH CIPHERFORCE.” This is more direct than the shared avatar: the graphic itself places TeamPCP and CipherForce together, reinforcing the connection already observed when the historical CipherForce onion was indexed under the title TEAM PCP.
The cat therefore works best as a supporting cross-platform identifier, while the TeamPCP/CipherForce branding provides a stronger link between the two names. Neither should be treated as proof of the real-world identity behind the accounts.
The same StealthMole search also surfaced third-party Telegram discussion linking TeamPCP to another supply-chain attack:
- “TeamPCP gonna do another large Supply chain attack, be ready for it”
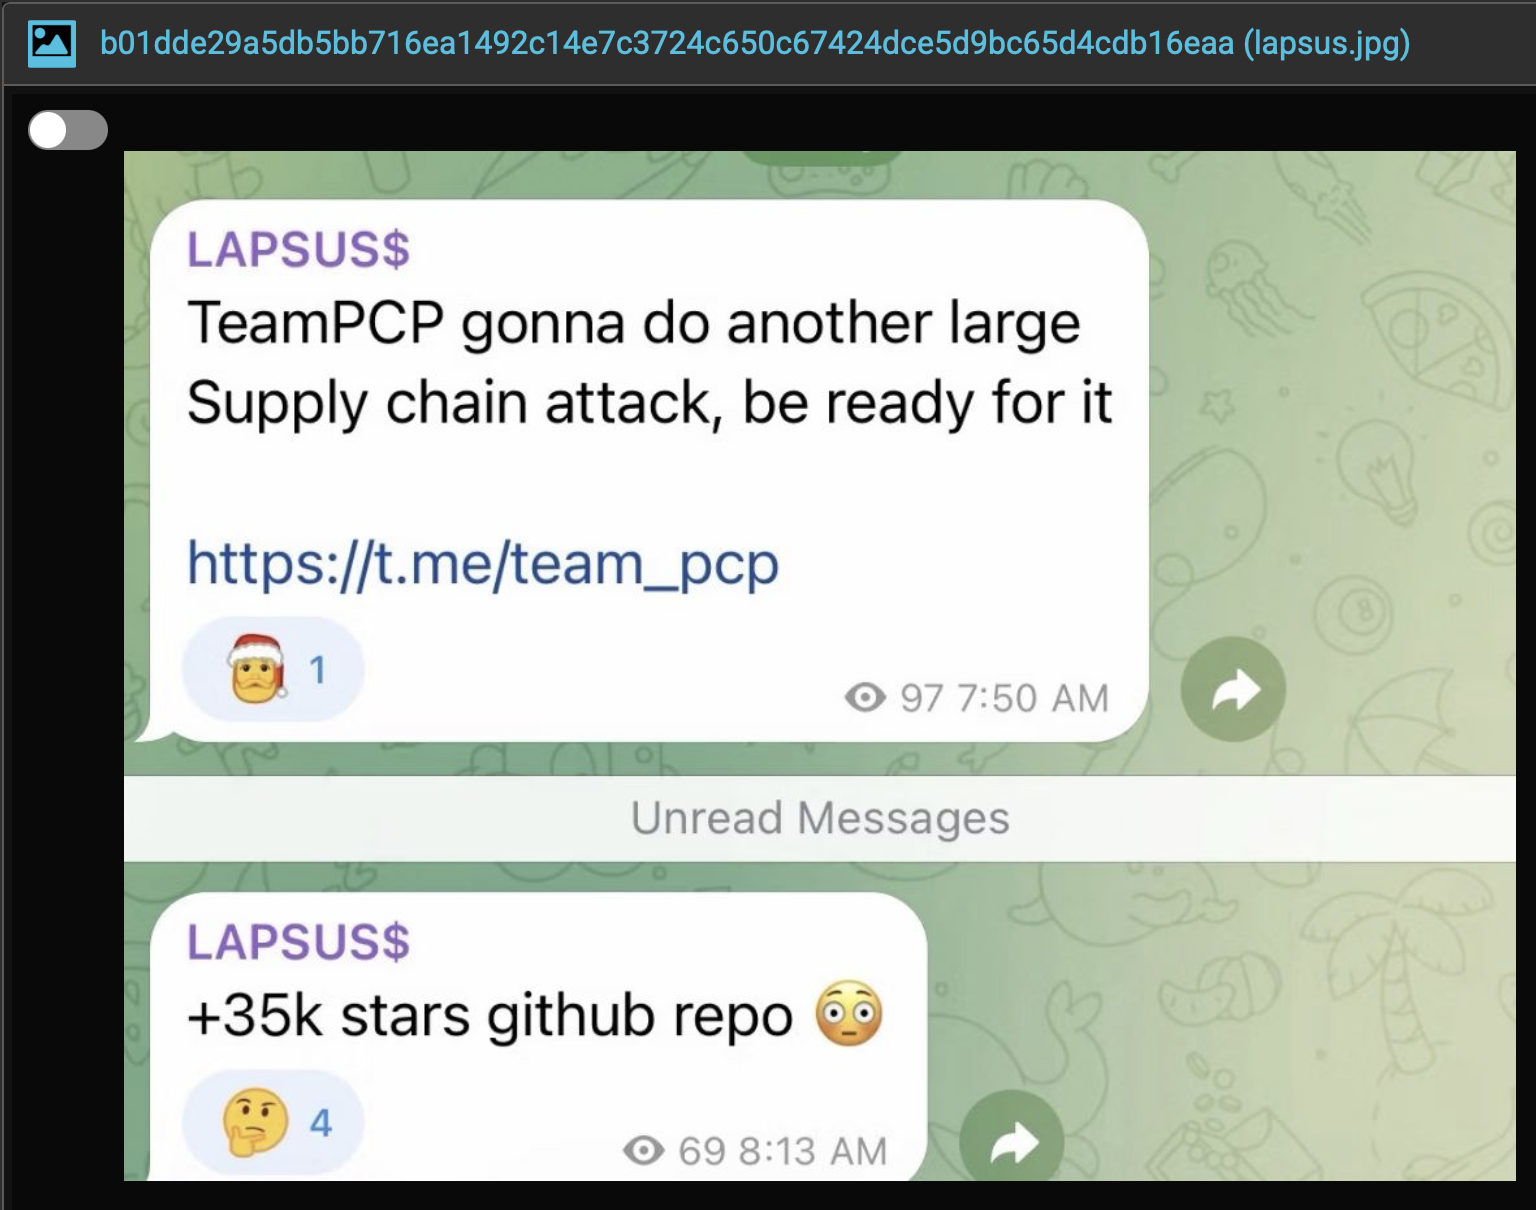
The message also referenced https://t.me/team_pcp and a “+35k stars github repo.” Because this was commentary from another user rather than a TeamPCP-authored post, it is best treated as contextual evidence of how TeamPCP was being discussed, rather than as evidence of a specific operation.
PCPCat: A Different Kind of Operation
The investigation also surfaced earlier activity associated with PCPcat, providing a useful view of the TeamPCP ecosystem before the CipherForce ransomware activity examined in this case.
A 28 December 2025 post in the Telegram channel Slice For Life, carried the title “Operation PCPcat Exploits Next.js and React, Affecting Over 59,000 Servers”.
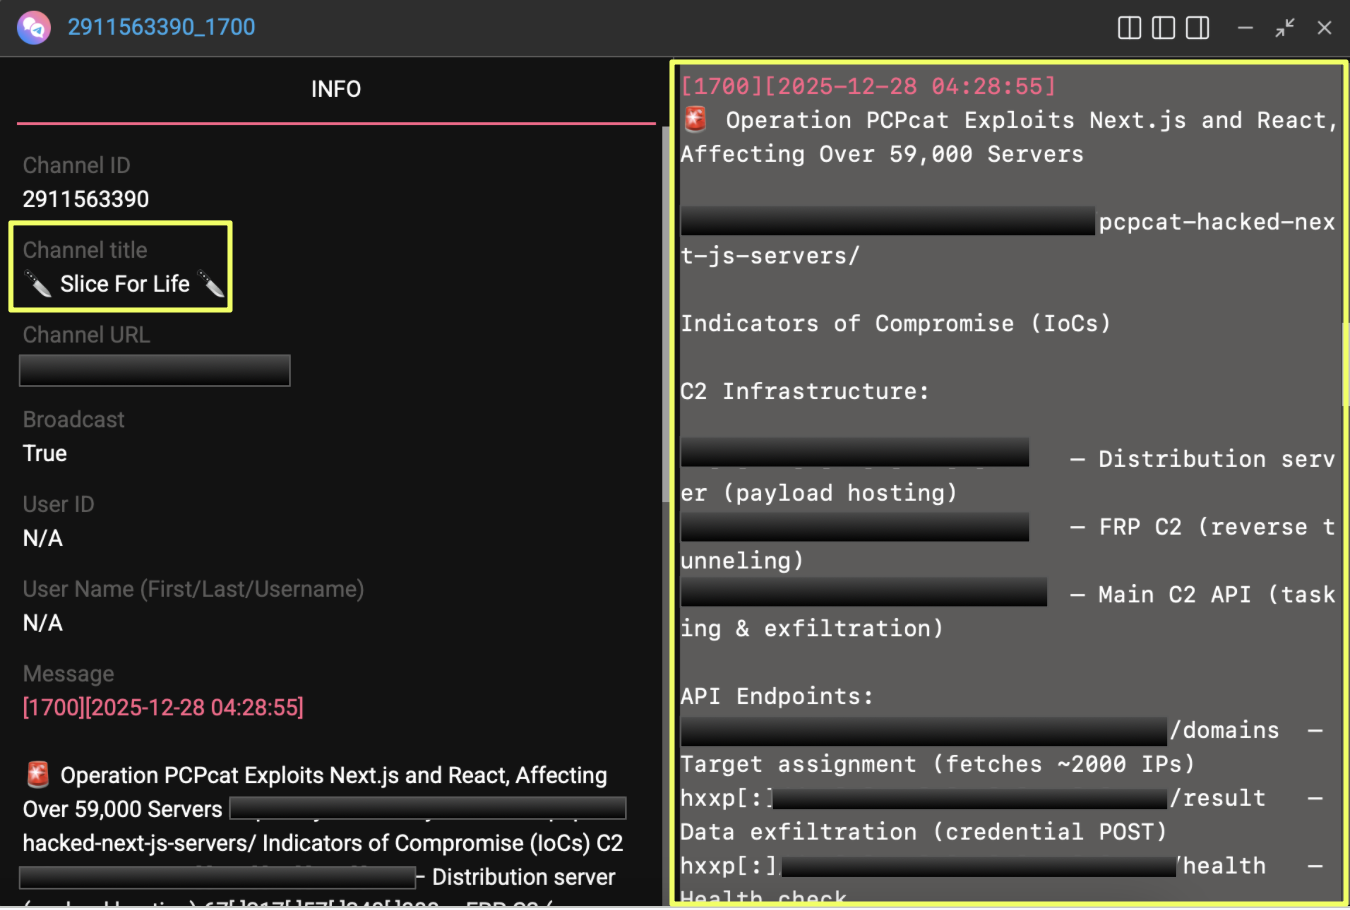
The reported operation involved the exploitation of Next.js and React environments and identified as the distribution infrastructure.
- 6*.**7.*7.**0:**6
The same reporting was also preserved in a HydraForums thread:
- https://hydraforums.**/Threads-news-59-000-servers-breached-operation-pcpcat-targets-react-and-next-js*********5
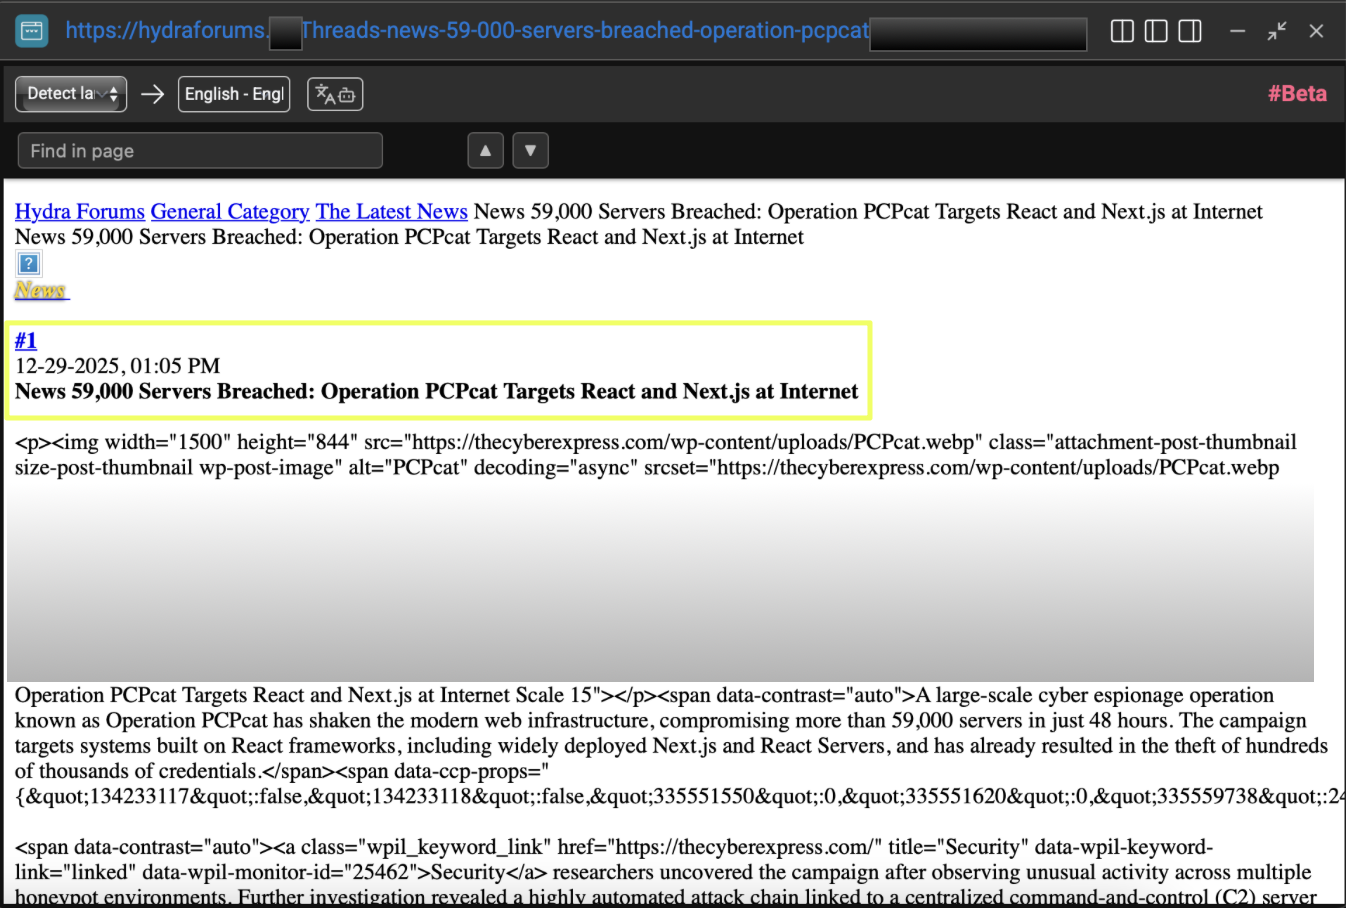
This activity predates the March 2026 CipherForce victim record seen earlier and adds an important layer to the timeline. The material associated with PCPcat describes large-scale exploitation of internet-facing application infrastructure rather than ransomware-based extortion, showing that the activity surrounding the TeamPCP identity set extended into mass exploitation of web technologies before CipherForce appeared in the ransomware monitoring trail.
Conclusion
The investigation ultimately points to a TeamPCP ecosystem that is more interconnected than any single platform or alias would suggest. What makes the trail compelling is not one decisive artifact, but the way CipherForce, TeamPCP, PCPcat and the related accounts repeatedly converge across different environments. The historical CipherForce infrastructure, recurring identifiers, TeamPCP forum activity, Telegram presence and shared branding provide several independent points from which the same ecosystem can be followed.
At the same time, the investigation shows why those connections need to be handled carefully. Some relationships are supported by direct TeamPCP material and repeated technical or visual identifiers, while others remain dependent on third-party claims or incomplete correlations. The available evidence is therefore strong enough to map the digital footprint and operational reach of the TeamPCP ecosystem, but not to turn that footprint into a definitive real-world attribution. In an environment where aliases, accounts and infrastructure can shift quickly, following how those pieces connect is often more useful than relying on a single name or isolated incident.
Editorial Note
Dark-web investigations rarely provide a single piece of evidence that can settle attribution with certainty. Accounts can change, infrastructure can disappear, aliases can be reused, and claims made within underground communities may remain difficult to verify independently. In this case, the investigation demonstrates the value of following those fragments together rather than relying on any one artifact.
StealthMole helped turn an initial ransomware lead into a wider cross-platform trail while allowing stronger evidence, supporting correlations and unresolved claims to remain clearly separated.
To access the unmasked report or full details, please reach out to us separately.
Contact us: support@stealthmole.com
Labels: Featured, Ransomware


