The Many Hats of Lupin: Tracing a UK Password Dump Back to a Personal Telegram Past
Underground data sellers rarely stay in one place for long. A single actor might post a sale on one forum, run a storefront through a Telegram channel, and keep a personal account tucked away on a platform that has nothing to do with stolen data at all.
The identities used across these spaces are not always consistent either. Usernames get banned, channels get taken down, and the same person quietly resurfaces under a new name while keeping the same branding, the same contacts, or the same habits that gave them away in the first place.
One such actor is ImLupin, a seller who first surfaced through a leak posted on the forum patched.to. What began as a single UK email and password dump grew, over the course of the investigation, into a much wider picture of who this actor is, how their operation is structured, and where the trail eventually thins out.
This report follows that investigation from the original post through the Telegram infrastructure built around it, into a personal account that predates the ImLupin persona by years, and finally into the leaked data that was examined for attribution and found wanting.
The First Trace of Lupin
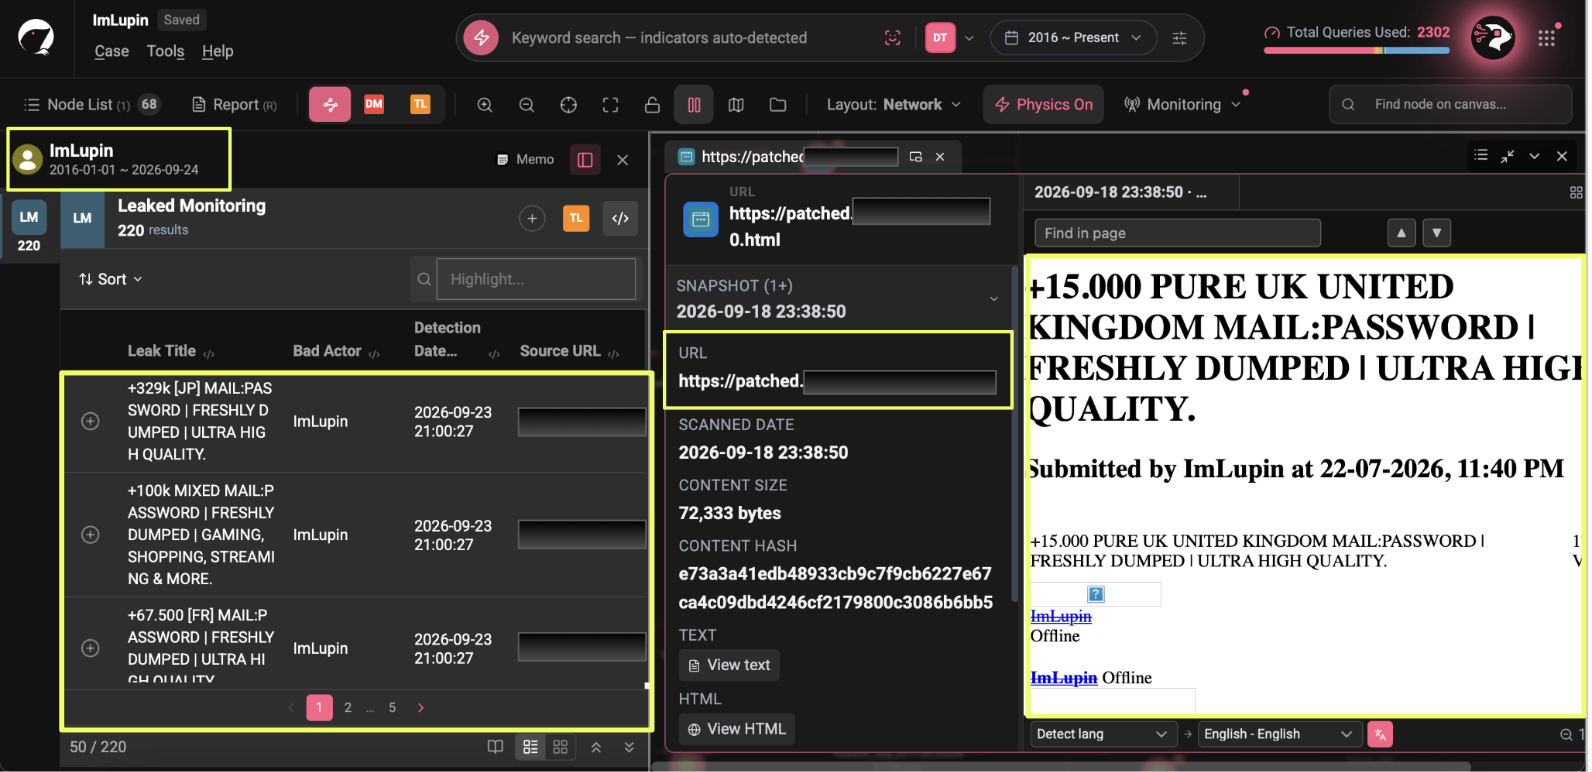
The investigation began with StealthMole's Leaked Monitoring tool, which had indexed a post from a seller operating under the name ImLupin on the patched forum. The thread advertised a fresh dump of UK email and password combinations, one of 208 similar listings tied to the same actor inside StealthMole's monitoring results.
- +15,000 PURE UK UNITED KINGDOM MAIL:PASSWORD | FRESHLY DUMPED | ULTRA HIGH QUALITY
- https://patched.**/thread-3******0.html
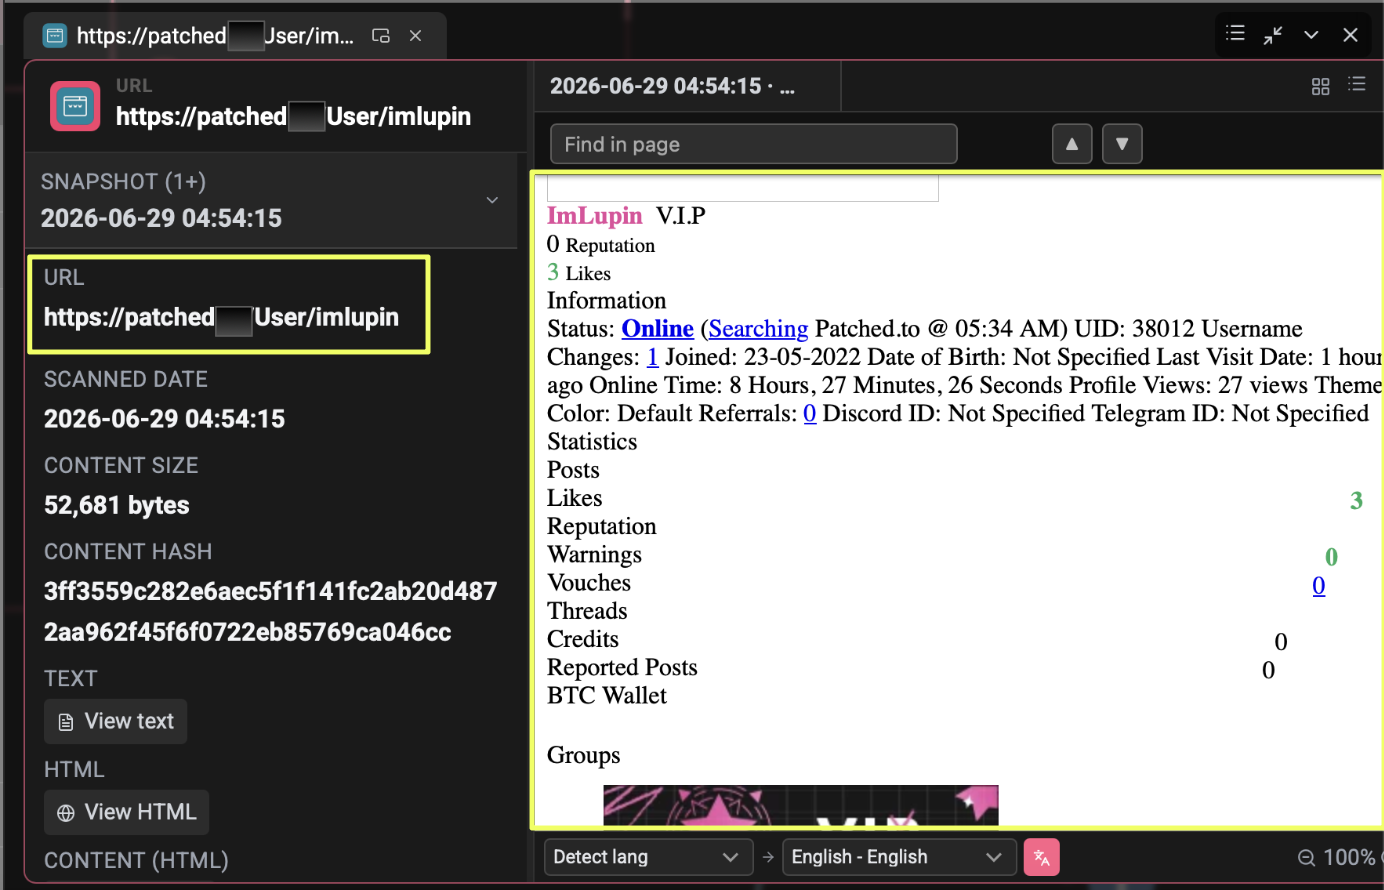
The forum profile behind the post told its own short story. ImLupin had joined the patched forum in May 2022, carried a negative reputation score, and was already marked as banned by the time the thread was captured. The account itself showed as offline.
None of that was unusual for a seller working the leak forums, but it was enough to justify a closer look at what the actor had left behind inside the thread itself.
Following the Storefront
Buried inside the thread was a set of contact links, the kind of detail a seller leaves behind so buyers know where to find them once a listing goes cold or a forum account gets banned.
- Telegram: https://t.me/Lu*******e
- Telegram: https://t.me/O********s
- Discord: https://discord.gg/Tw********KU
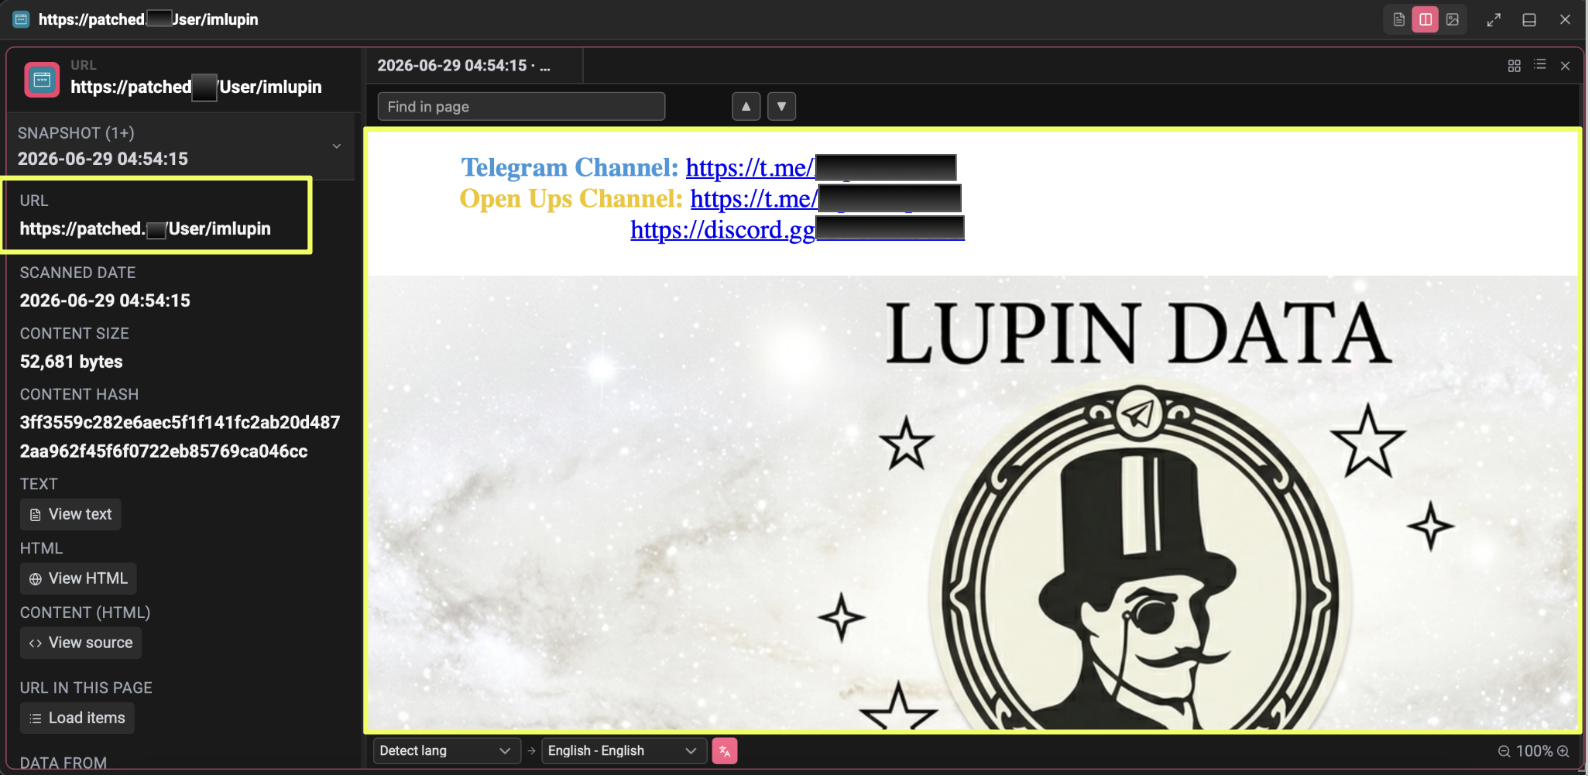
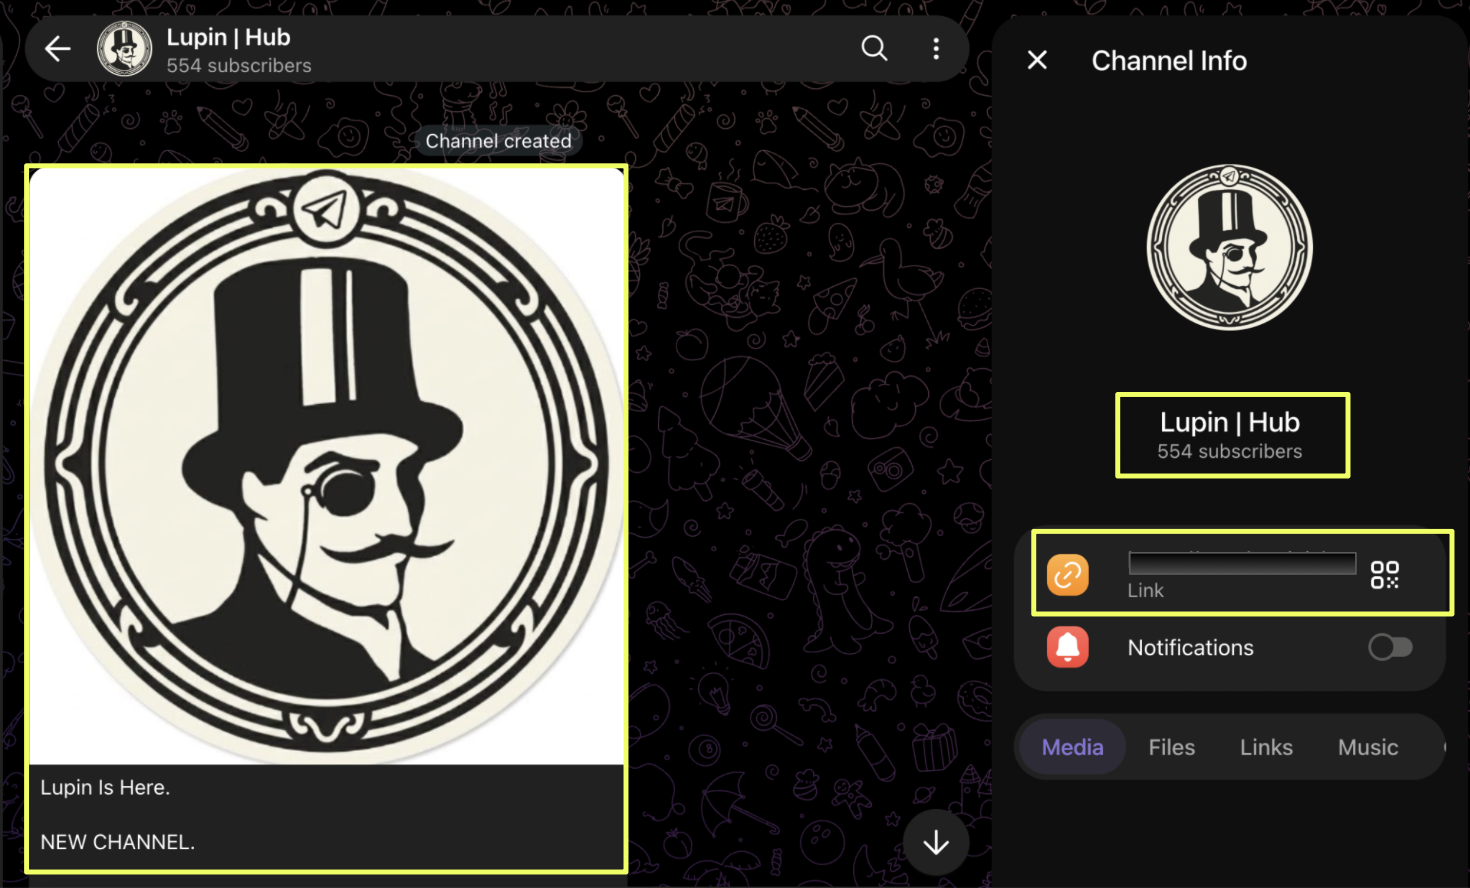
The telegram link t.me/Lu******e was further investigated in StealthMole’s Telegram Tracker, which led us to channel called Lupin | Hub. This channel carried the same branding, a top hat and monocle logo that would turn out to be a consistent signature across everything ImLupin touched.
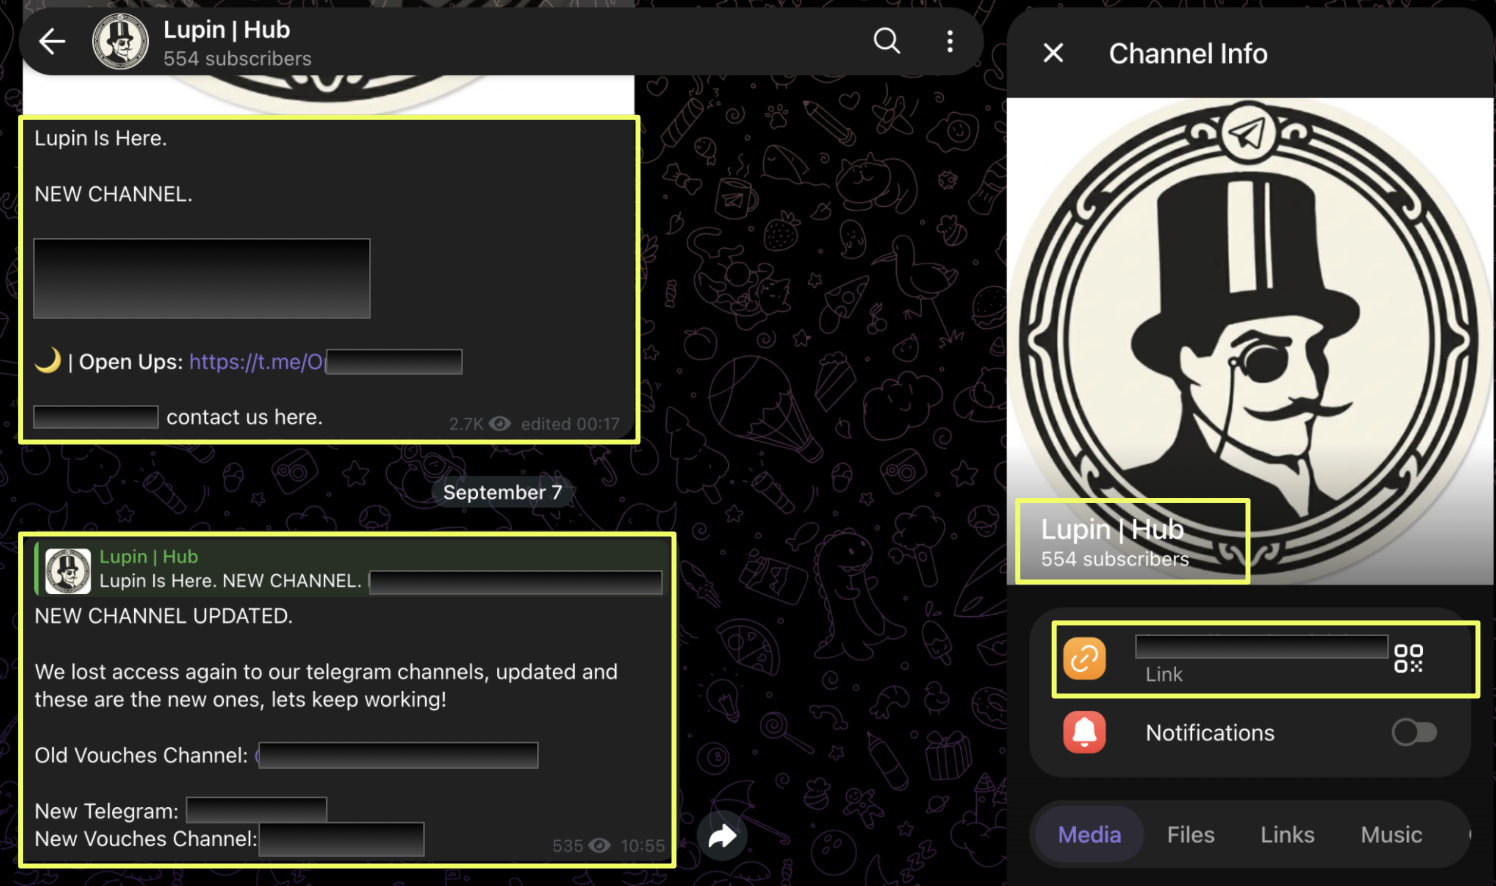
Inside the channel, a message from September announced that the operator had lost access to their previous channels again and was posting new ones to replace them, listing an Open Ups channel at @Op*****n and a contact handle at @Lupin*****k. That single phrase, losing access again, would repeat itself several more times before the investigation was finished, and it became one of the clearer behavioral markers tying the different channels back to the same operator.
A Name Behind the Alias
The Telegram handle @Lu*******e was further run through StealthMole's Telegram Tracker, which returned something the forum posts never could: a numeric Telegram user ID, permanent and far harder to fake or recycle than a username.
- Telegram User ID: 5717234229
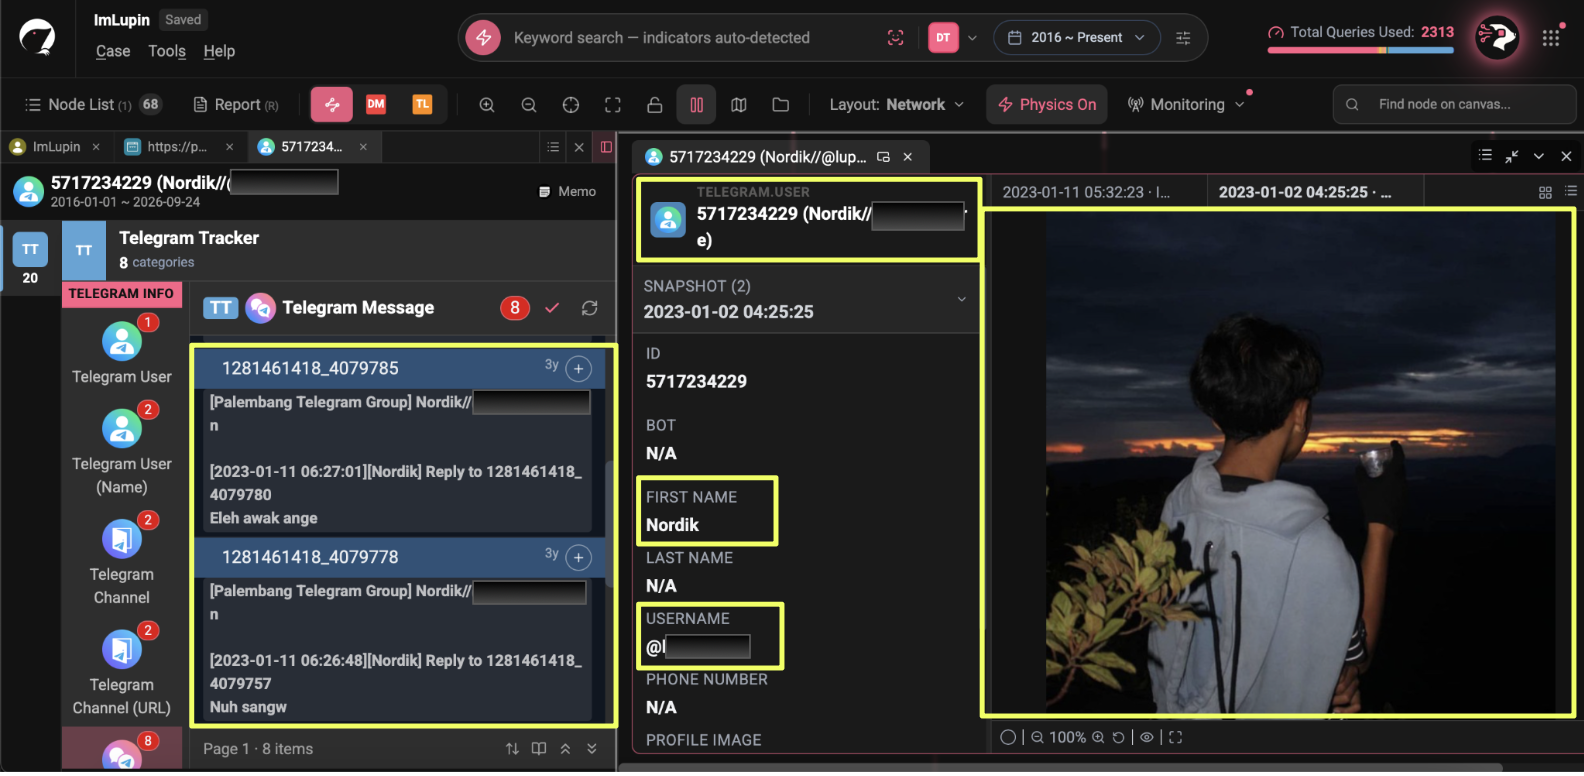
StealthMole's historical indexing held two snapshots of that ID. In the earlier one, dated 2 January 2023, the account carried the username @lu********e and a first name of Nordik, with a profile photo of someone standing outdoors at sunset, their back to the camera.
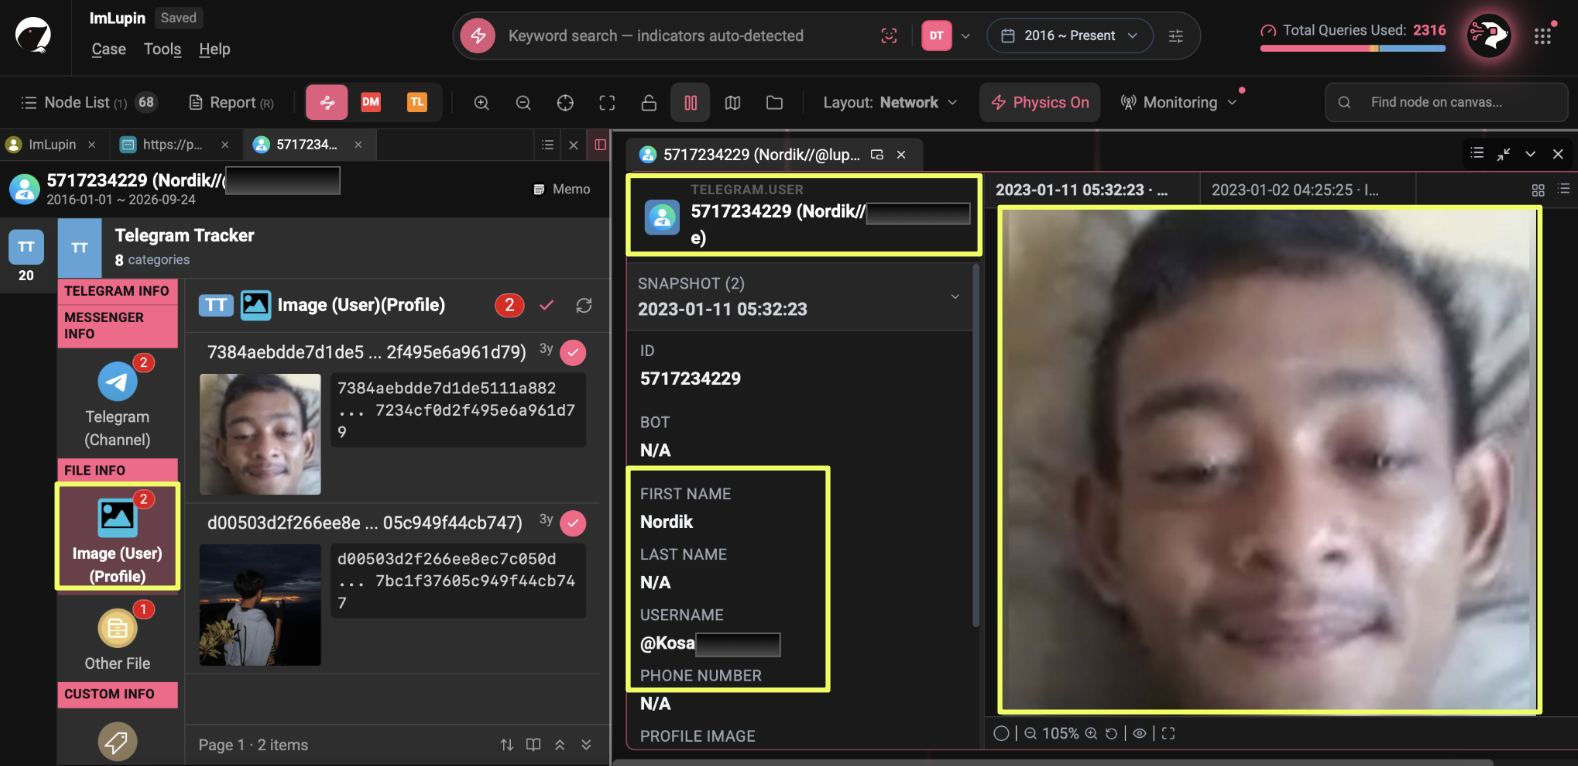
Nine days later, the same numeric ID showed up under a new username, @Kos*****un, this time with a close, face-forward photo. The first name Nordik stayed constant through the change, and because the underlying ID never moved, the two snapshots could be tied together with real confidence rather than a guess based on a shared display name.
This was the first indication that ImLupin was not simply a forum handle invented for the purpose of selling data. Behind it sat a Telegram account with a history stretching back years before the patched.to thread was ever posted.
A Voice in a Palembang Group Chat
StealthMole's Telegram Tracker also indexed messages sent by the user across the channels it had participated in. Eight results came back, several of them from a community called the Palembang Telegram Group, posted the same day the username changed to @Kos******un.
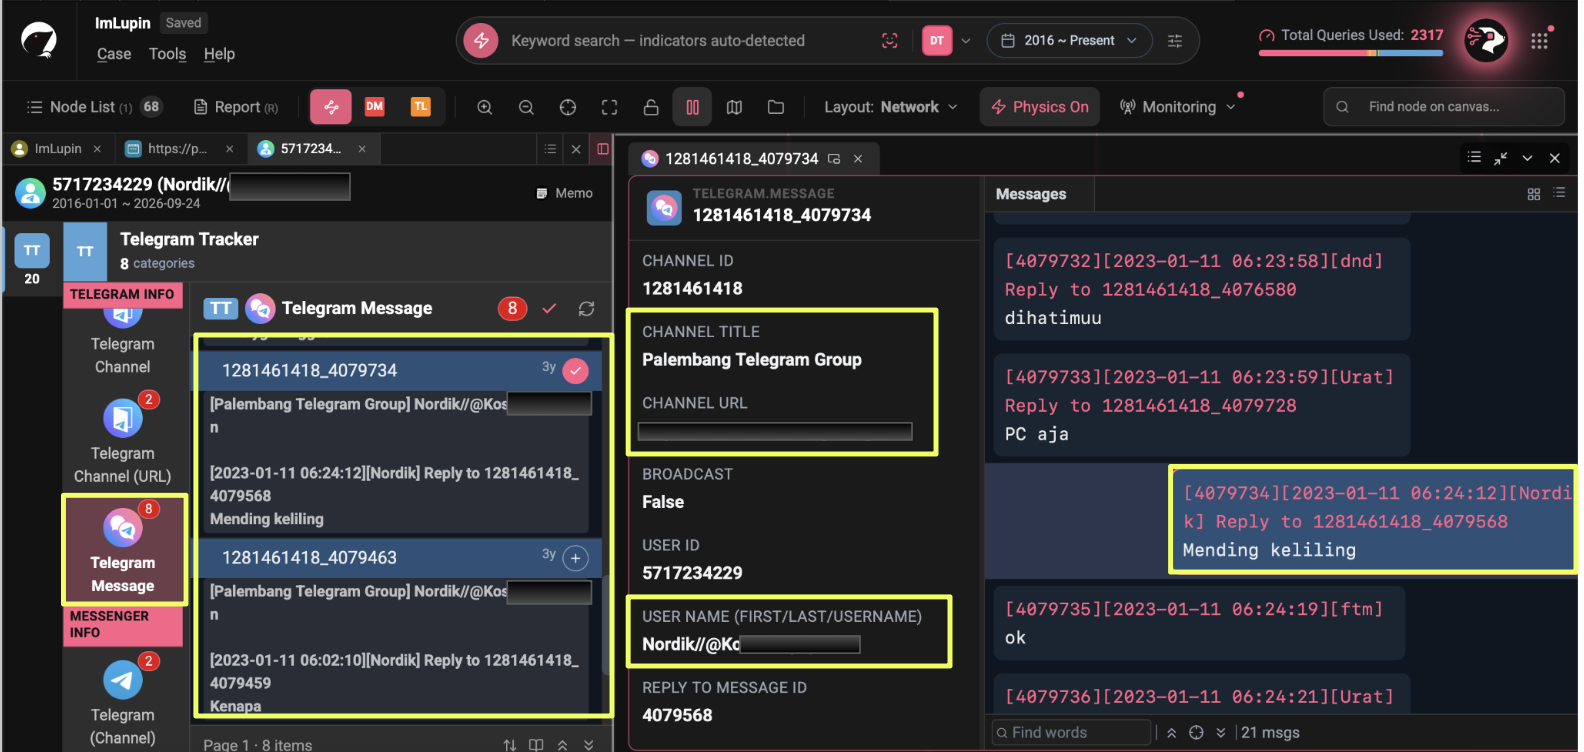
It is worth mentioning that Palembang is a city in South Sumatra, Indonesia, and the messages themselves were written in casual Indonesian slang, the kind of unguarded chatter that has nothing to do with a criminal persona and everything to do with an ordinary local group chat.
Actors rarely apply the same discipline to their personal accounts that they apply to their sales fronts, and this group, joined under the real-looking name Nordik rather than a leak-seller alias, was a small but genuine crack in that discipline. Taken together with the group's name, it points toward Indonesia as the actor's likely home base, a detail that would later sit alongside, and in one case complicate, a separate lead pulled from leaked breach data.
Rebuilding After Every Ban
Returning to the storefront side of the investigation, StealthMole's Dark Web Tracker was used to pull the full history behind the Telegram channels ImLupin had built. A clear pattern of rebranding emerged, each cycle triggered by the same complaint: access lost, channels rebuilt, buyers redirected.
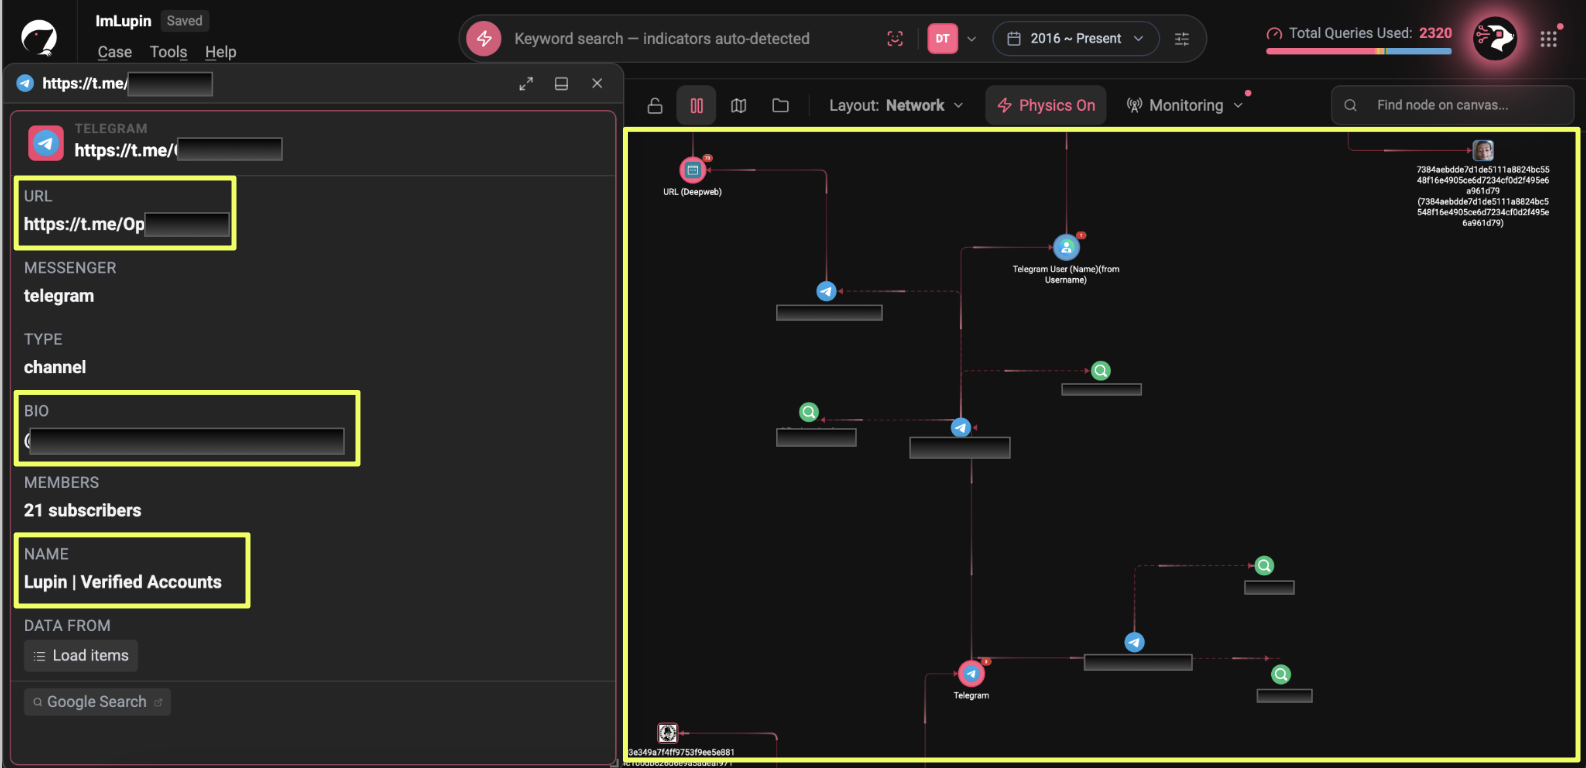
- Personal contact: @Lu*****a (old) leading to @Lu*****k (current)
- Vouches channel: @Lu****t (old) leading to @Vou*******n (interim) leading to @Re*********n (current)
- Storefront channel: Lupin | Hub, then Lupin | Verified Accounts, then Your best option, 441 subscribers at time of capture
A channel called HitR, 74 subscribers and linked in its bio to @Lu*****k, added a different kind of detail. Rather than sales copy, the channel carried forwarded output from credential-checking tools, one run posted by an account called Chodev showing plaintext hit results, and another forwarded from a source labelled DATA LOOKUP showing a checker processing thousands of records with a live hit count. Neither Chodev nor DATA LOOKUP has been resolved to the same operator yet, but both represent a plausible next pivot into the tooling side of the operation rather than just its storefronts.
Two Storefronts Behind One Persona
The Dark Web Tracker also surfaced two dedicated websites operating under the Lupin branding, each a step up from a simple forum listing into something closer to a functioning storefront.
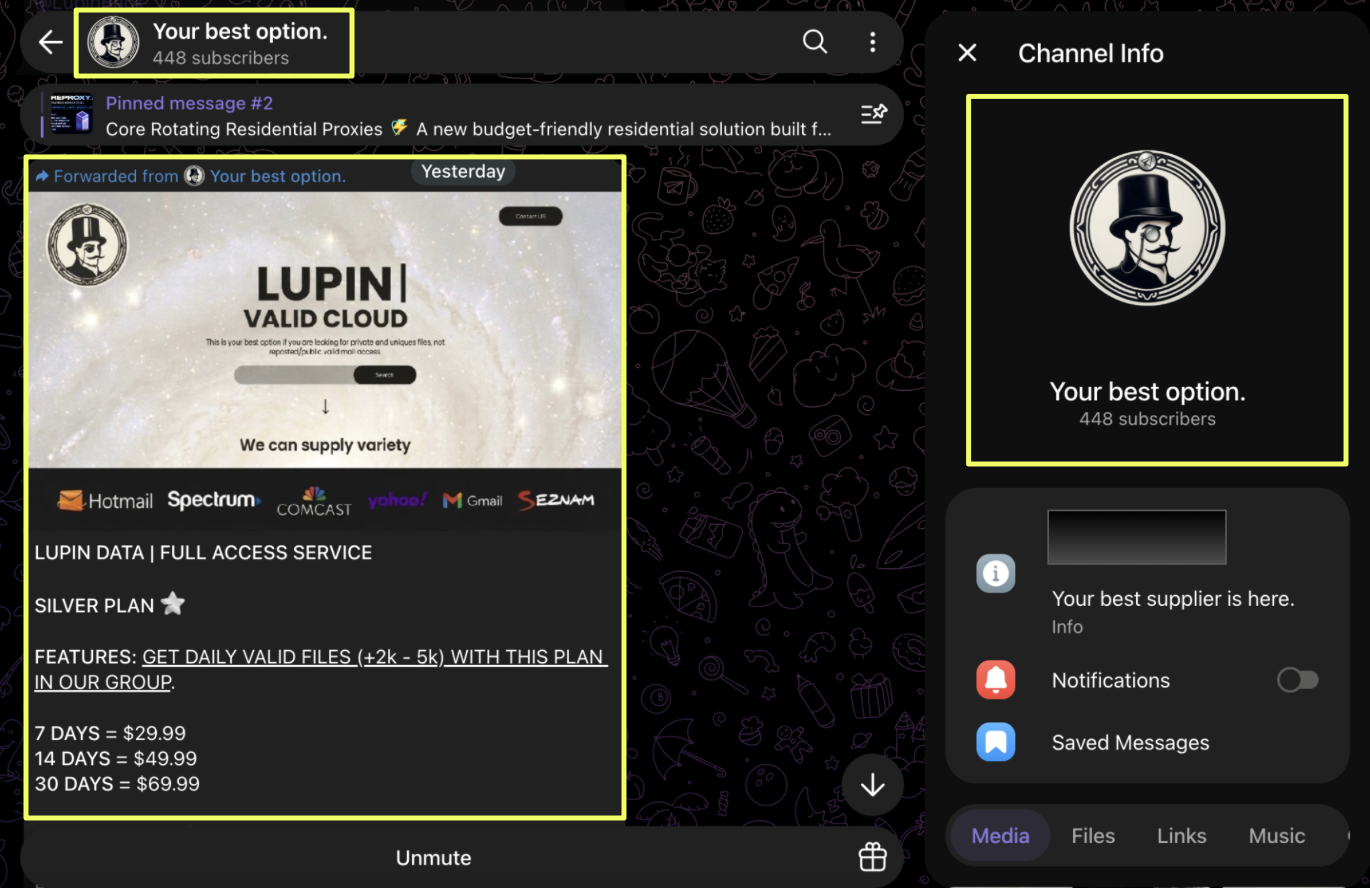
- Lupin | Valid Cloud, a subscription service selling checked mail access across Hotmail, Spectrum, Comcast, Yahoo, Gmail, and Seznam, priced from $29.99 for seven days up to $69.99 for thirty
- Lupin Open Ups, a marketplace for verified accounts across major banks, payment processors, crypto exchanges, and OnlyFans, accepting Bitcoin, Litecoin, Ethereum, and USDT
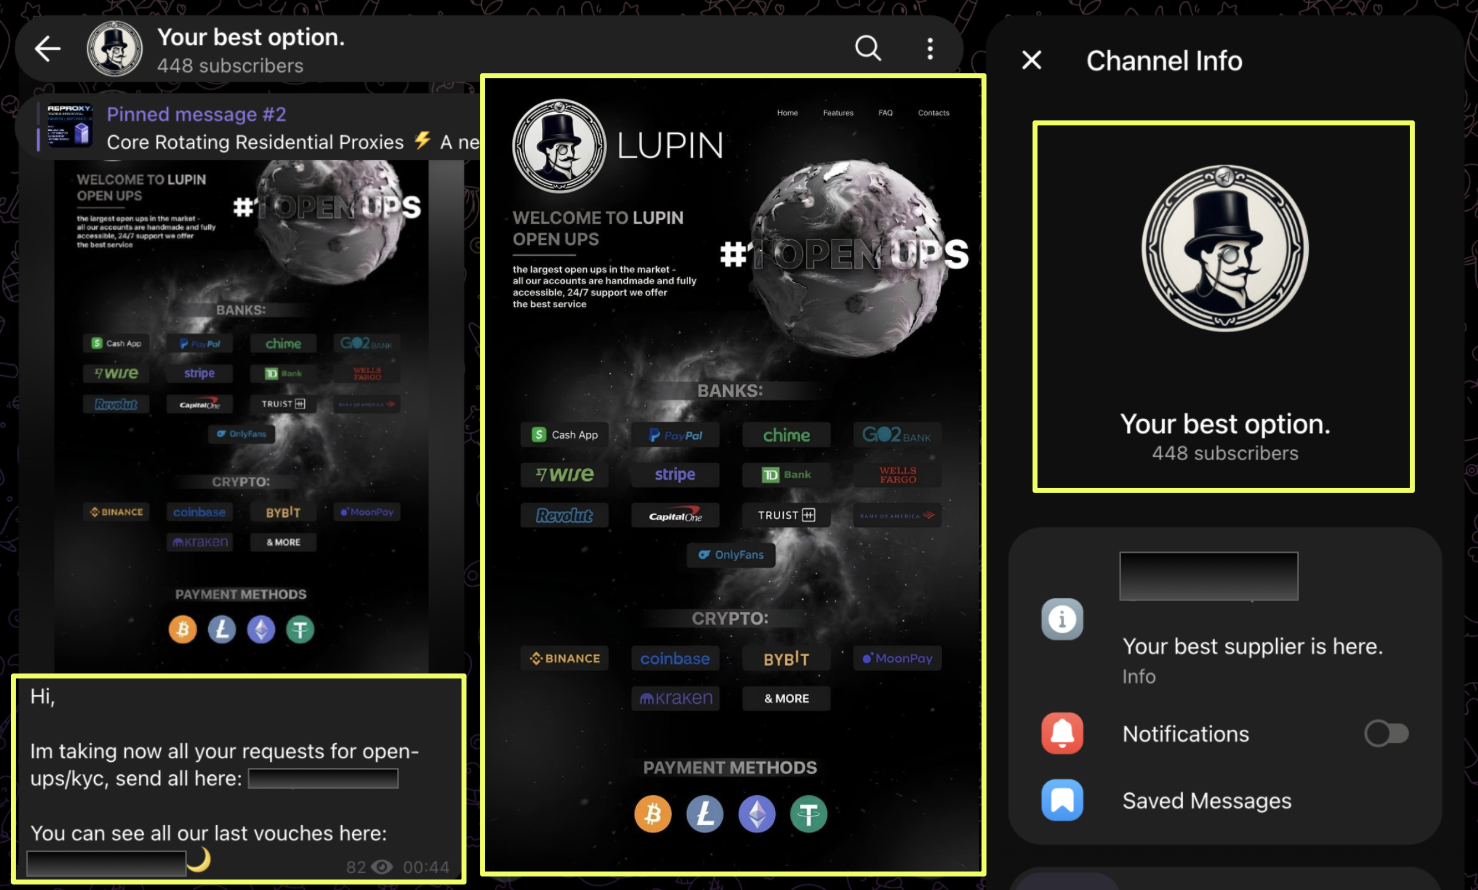
Neither site was a one-off listing. Both were built to look permanent, with pricing tiers, feature lists, and ongoing support, and both carried the same top hat and monocle branding seen everywhere else in the investigation. Whatever ImLupin's role in the wider leak-selling ecosystem, this was not a single seller posting one thread and disappearing. It was a small, maintained business.
A Trail Across the Forums
With the Telegram side of the operation reasonably well mapped, the investigation turned back to ImLupin's presence across the wider forum ecosystem. ImLupin username was further investigated in StealthMole's Dark Web Tracker, which led to a further set of profile pages, spread across underground platforms like cracked.**, xreactor.***g, niflheim.****d, xforums.**, leetforums.**, voided.**, and spear.**.
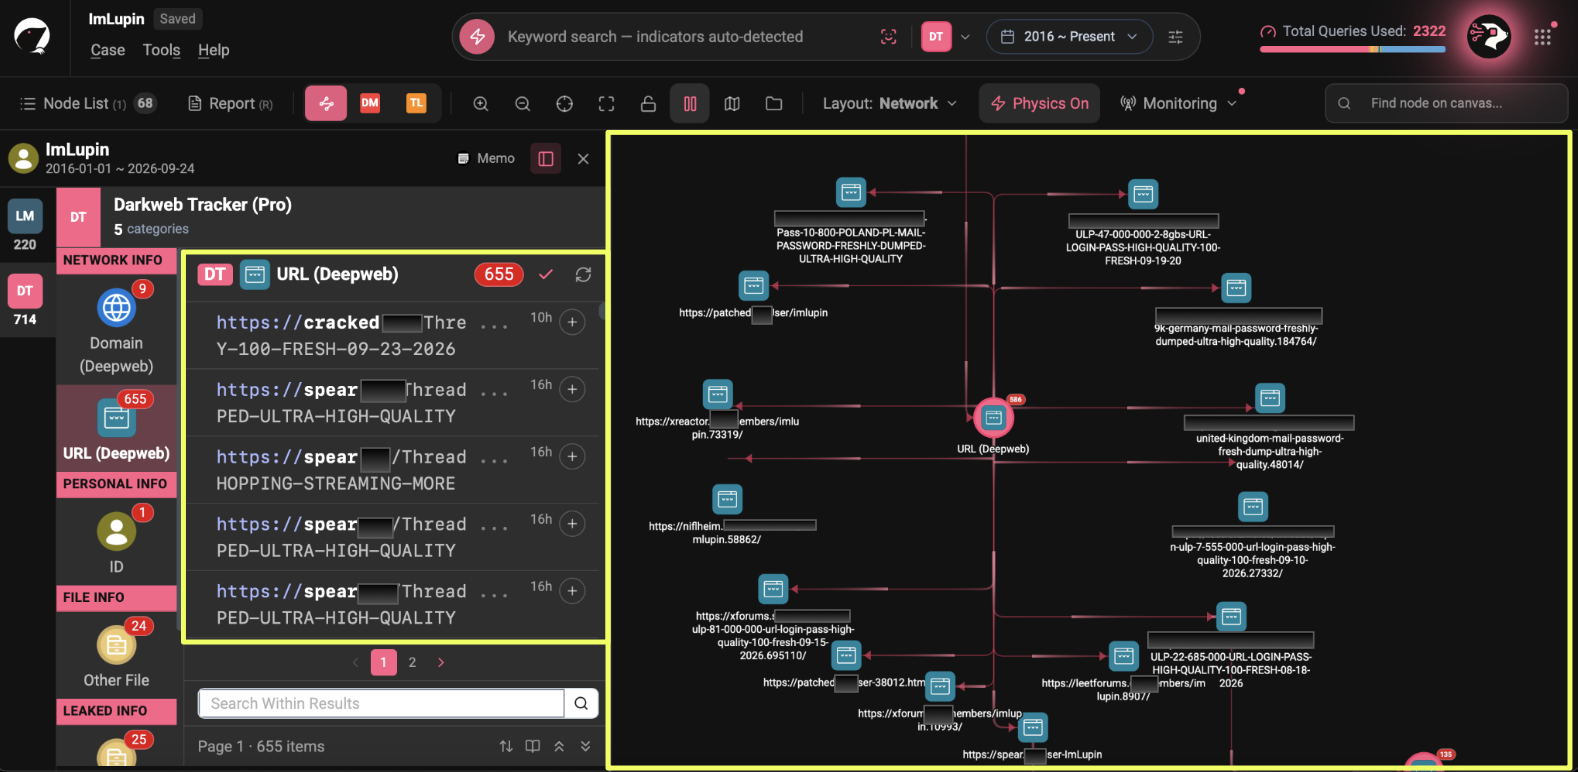
- cracked.**/ImLupin - 17 July 2022
- leetforums.**/members/imlupin.8***7
- xreactor.***/members/imlupin.7****9
- niflheim.*****d/members/imlupin.5****2 - 26 July 2026
- voided.**/ImLupin - 26 July 2026
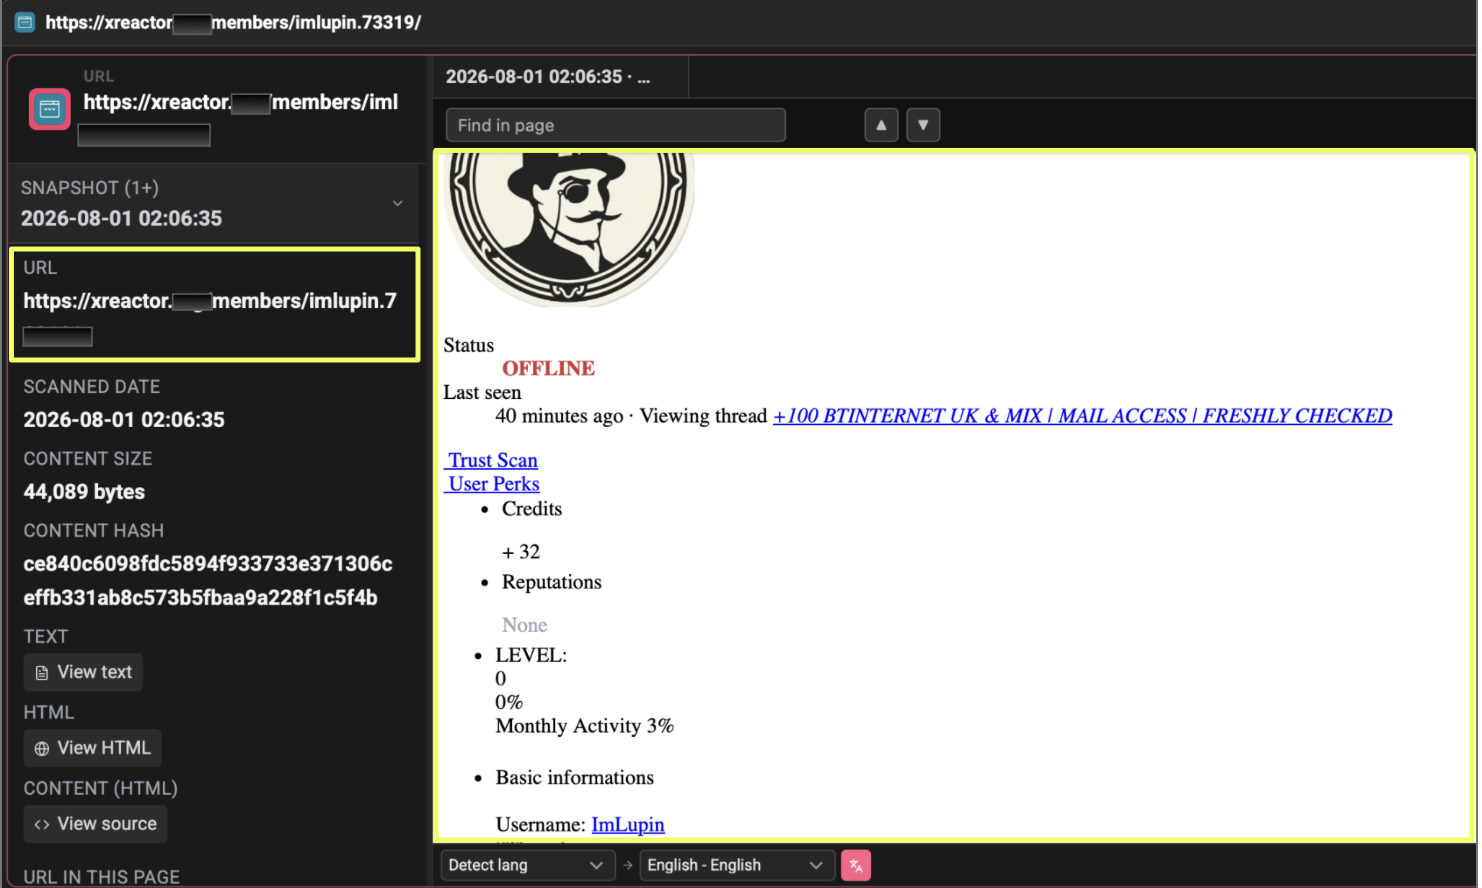
The recurring join date across nearly every one of these forums, the 26th of July 2026, stood out more than any single profile did on its own. Registering across five separate forums within a day or two is not typical browsing behavior. It reads as a deliberate, coordinated rebuild, consistent with an actor re-establishing themselves after losing access elsewhere, the same pattern already seen playing out repeatedly on the Telegram side. The voided platform profile's recent threads told the rest of the story in numbers: a steady cadence of dumps through late August.
Conclusion
This investigation began with a name attached to a single UK password dump on patched.to. By the end of it, that name had unfolded into a Telegram operation rebuilt through at least three separate bans, two functioning storefront websites, a presence across seven underground forums registered within days of each other, and a personal Telegram account, tied to a permanent numeric ID, that traced back to an ordinary group chat in Palembang, Indonesia, years before any of the selling began.
Not every lead closed cleanly. The leaked MemeChat record offers the most credible thread toward a real identity, corroborated across two independent sources, but a second email search against it came back empty. The YouNow record introduced a different name that could not be tied to ImLupin with any confidence, and the shared IP address behind it argued against the connection rather than for it. What the investigation does establish, with a reasonable degree of confidence, is the shape of the operation itself: a single, persistently rebranded seller running a Telegram-based storefront and credential business, most likely operating out of Indonesia, whose full real-world identity remains an open question.
Editorial Note
Attribution in cyber investigations is rarely straightforward. Usernames change, channels disappear, and leaked data can produce misleading connections, which is why weaker leads in this case were treated with caution. StealthMole helped connect the original leak to the actor’s wider forum, Telegram, and storefront activity while separating corroborated findings from simple matches. The result was a clearer picture of the operation without overstating what the evidence could prove.
To access the unmasked report or full details, please reach out to us separately.
Contact us: support@stealthmole.com
Labels: Featured, Threat Actor


