Banned, Renamed, Repeat: Tracing the Accounts Behind Rockhavks

On underground forums, a ban is rarely the end of a seller. It is closer to a change of clothes. The account disappears, the reputation resets to zero, and a few days later a new name starts posting the same kind of listings, often to the same buyers, through the same back channel. Forum moderators know this, buyers know this, and the sellers know that everyone knows it. What keeps the cycle going is that each new account, on its own, looks unremarkable.
RockHavks looked unremarkable too. It was a DarkForums account barely a month old, with zero reputation and a run of database sales covering customers of loan providers, job portals, travel companies and government bodies across a dozen countries. Nothing about the account suggested a history. Its profile listed no username changes, no bio and no links, and its posts read like the output of any one of hundreds of small-time data brokers active on the forum this year.
This report follows what happened when we stopped treating RockHavks as a new seller and started following the contact details it left behind. Using StealthMole's Leaked Monitoring, Darkweb Tracker and Telegram Tracker, those details led back through several earlier forum identities, a string of bans, and a single Telegram account whose own message history shows how a self-described novice in late 2024 became a persistent data seller by late 2026.
A Loan Database and Three Ways to Pay For It
The investigation started with a routine keyword search. Running Rockhavks through StealthMole's Leaked Monitoring returned a listing detected on 25 September 2026, with Rockhavks recorded as the author.
- https://darkforums.**/Thread-120k-United-States*******transacti
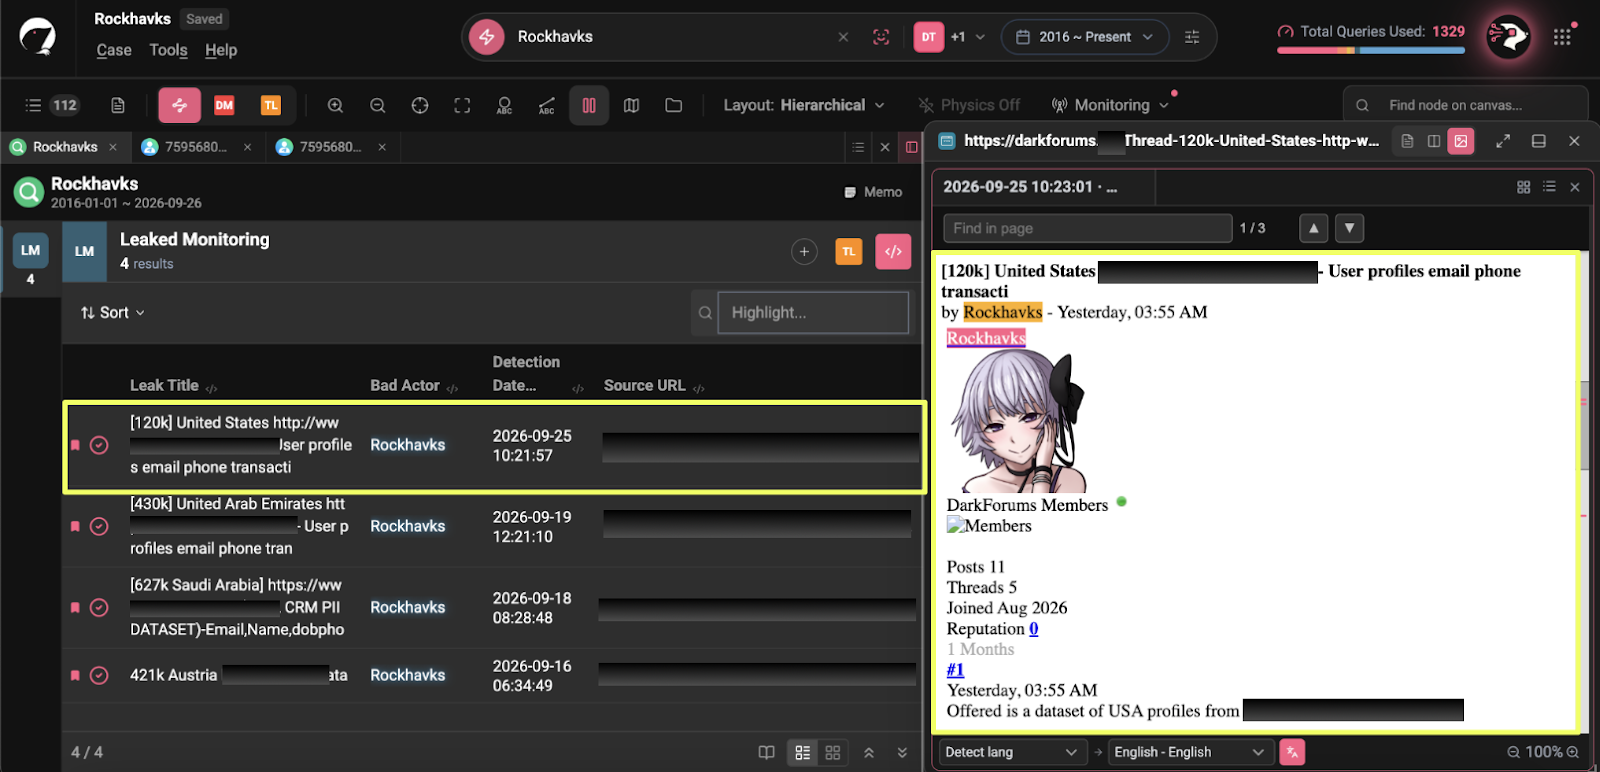
Opening the thread showed what was on offer. RockHavks described the data as US customer profiles and listed the fields, which went well beyond contact details:
- Application ID | First Name | Last Name | Street Address | Annual Income | Loan Amount Requested | Housing Status
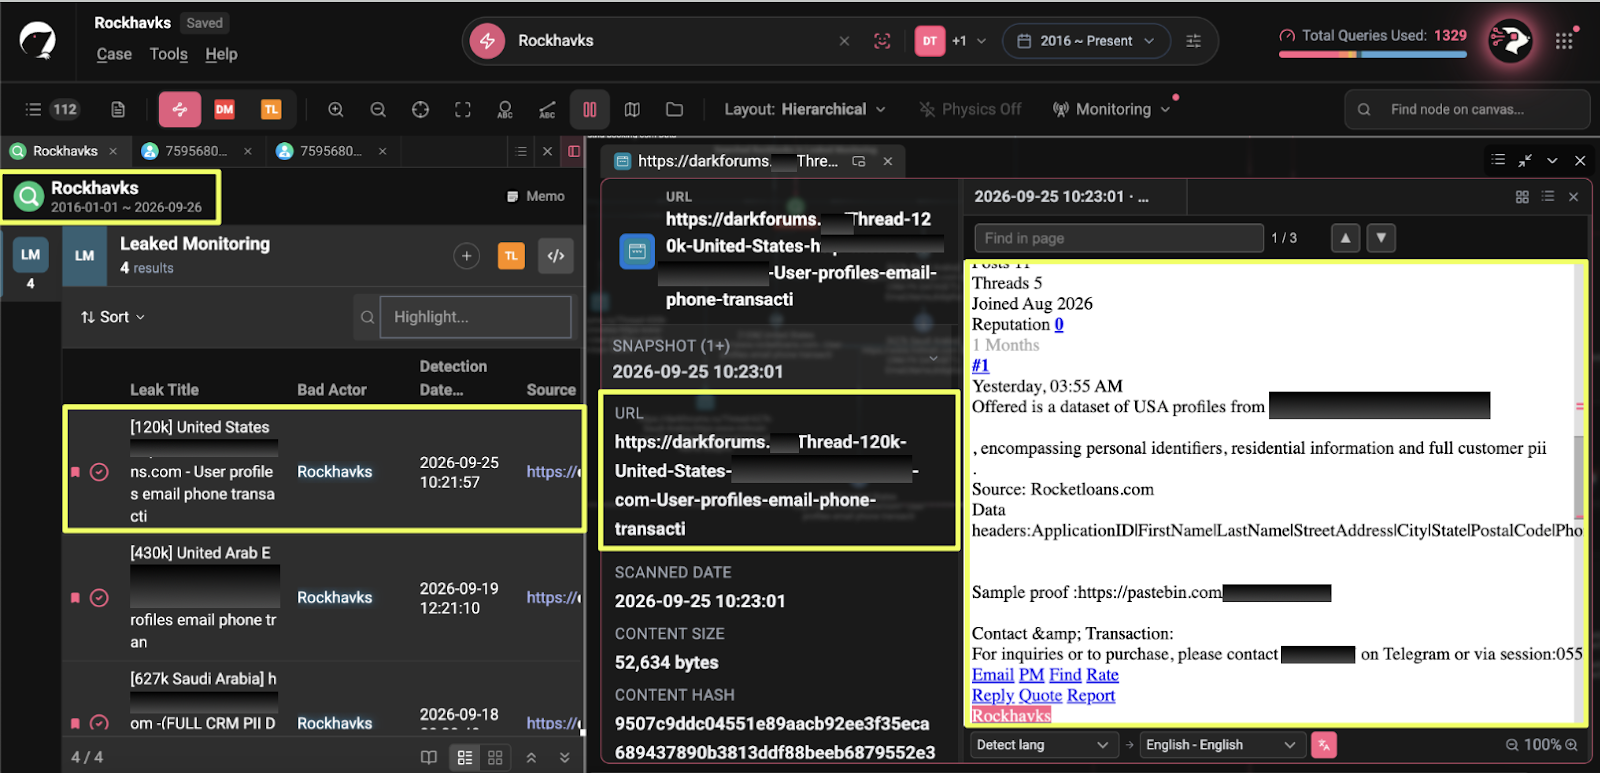
If genuine, a dataset with income, debt-to-income ratio and exact credit scores is a fraud toolkit, not a marketing list. It tells a buyer who is financially stretched and how to impersonate them convincingly.
The post closed with three ways to reach the seller:
- Sample proof: https://pastebin.com/q********D
- Telegram: @un*****7
- Session: 0553***************************************ebc10
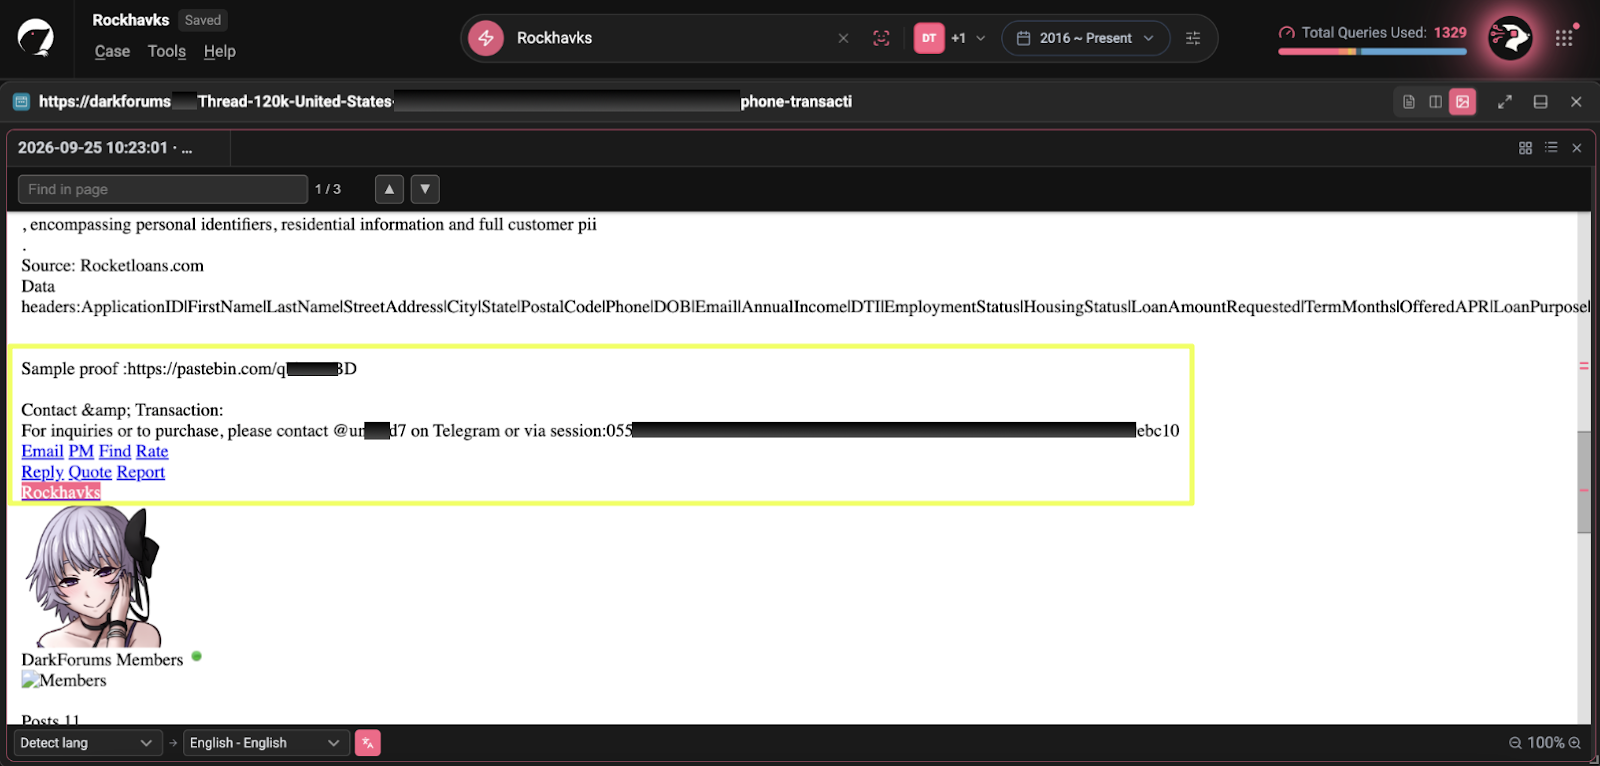
These three artifacts did not carry the same weight. The Pastebin link had been indexed by StealthMole but held no retrievable content, so it went no further. A Telegram username can be changed in seconds, which makes it a useful lead but a weak anchor.
The Session ID was different. It is a 66-character public key tied to an account on the Session messenger, and a seller cannot change it without abandoning the account and telling every past buyer where to find them now. Sellers tend to keep these for a long time, and that persistence made it the most promising thread to pull.
Before searching it any further, we checked the account itself. StealthMole held a snapshot of RockHavks' DarkForums profile from 18 September 2026:
- Profile Link: https://darkforums.**/User-Rockhavks
- Joined: 17 August 2026
- User ID: 137***3
- Username Changes: 0
- Time Spent Online: 49 minutes, 16 seconds
- Threads: 2, Posts: 3, Reputation: 0
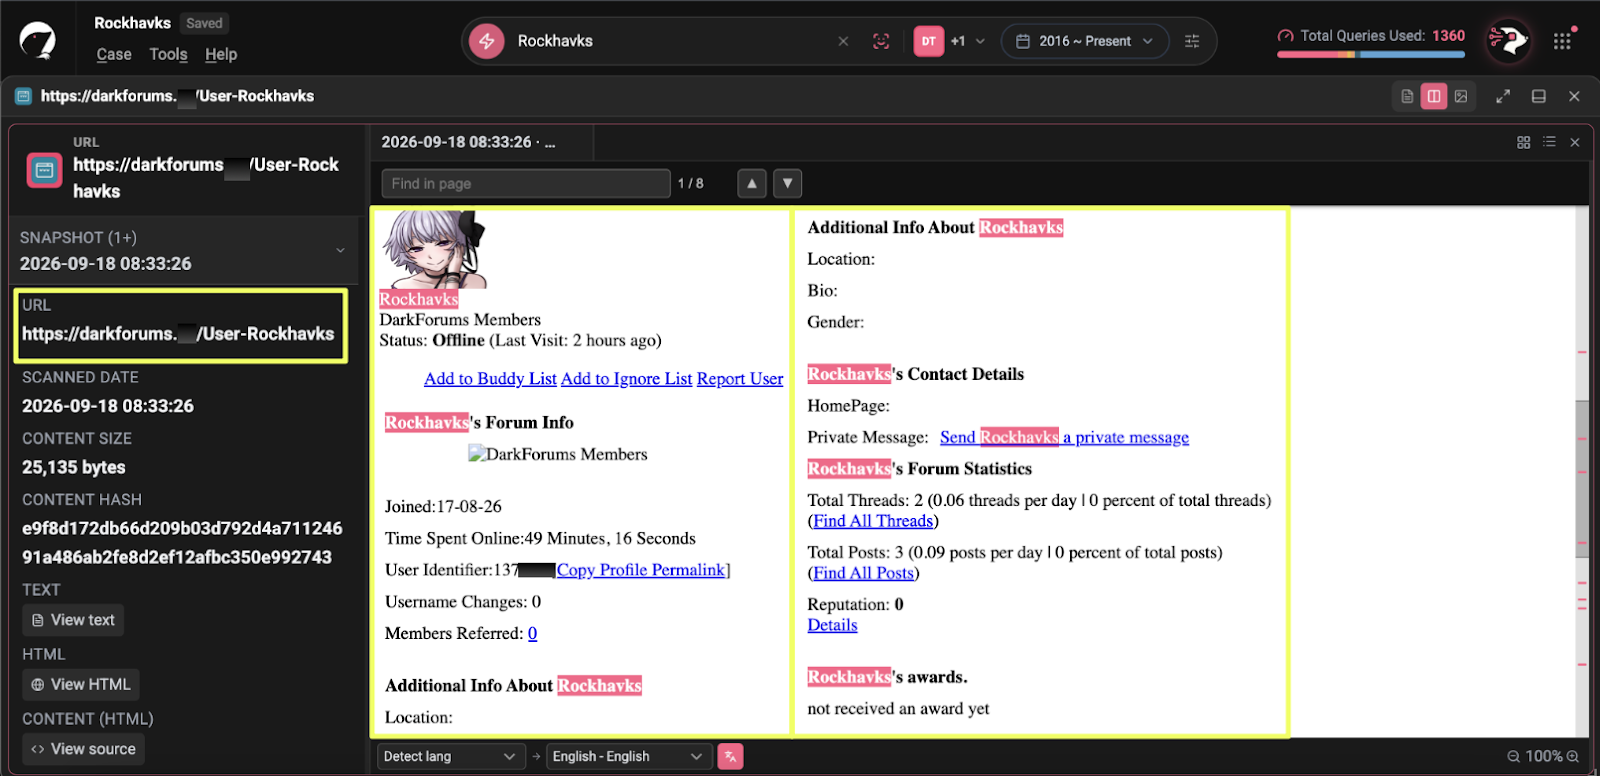
A month-old account with under an hour logged in, and already selling a six-figure financial dataset. That gap between how new the account was and how confidently it was trading was the first thing about RockHavks that did not quite fit.
Seven Weeks, Seventeen Listings
RockHavks was not a one-listing account. A fresh search across Leaked Monitoring and Darkweb Tracker returned 10 Leaked Monitoring entries attributed to RockHavks and 27 Darkweb results. Most of the darkweb results were DarkForums pages that simply showed RockHavks in the list of online users, but filtering those out left a clear trail of the account's own threads. Telegram Tracker returned nothing for the name, which already hinted that RockHavks was a forum-only persona and that its Telegram life ran under another label.
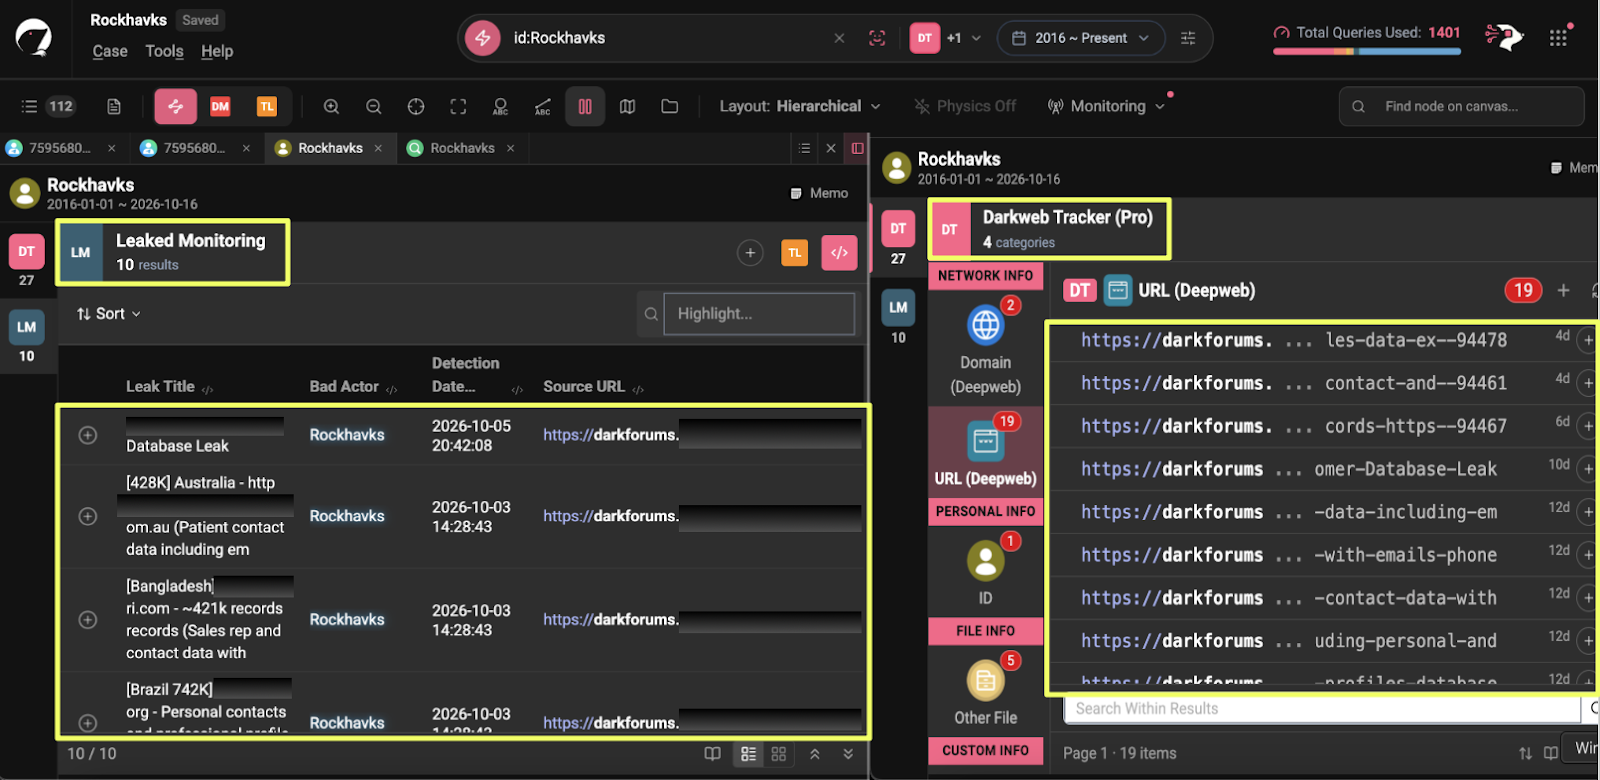
Opening each thread resulted in a clear understanding of RockHavks operational footprint from 16 September to 9 October 2026. It is worth mentioning that the dates listed below are StealthMole's detection dates.
Detected | Listing | Claimed size | Asking price | Sample or proof offered |
2026-10-09 | Passenger and booking records (Norway) | 614k | $1,100 | https://gofile.io/d/o*****O, https://gofile.io/d/zy******* |
2026-10-05 | Customer database (Portugal) | not stated | "varies on quantity" | https://pastebin.com/2a***Z |
2026-10-03 | User accounts (China) | ~478k | $1,300 | https://gofile.io/d/c***Lv |
2026-10-03 | Property and contact records (Canada) | 742k | $900 | https://gofile.io/d/x****I9, https://gofile.io/d/O*****1, https://gofile.io/d/W*****E |
2026-10-03 | Private company contacts (Brazil) | 742k | $1,200 | https://gofile.io/d/h****U, https://gofile.io/d/w6****9, https://gofile.io/d/M3****9 |
2026-10-03 | CRM contacts (Bolivia) | 437k | $1,300 | https://gofile.io/d/rz*****R, https://gofile.io/d/Ce****m, https://gofile.io/d/Oe*****v |
2026-10-03 | Sales and contact data (Bangladesh) | ~421k | $1,300 | https://gofile.io/d/kZ*****j, https://gofile.io/d/C*****N, https://gofile.io/d/S*****v |
2026-10-03 | Hospitality contacts (Austria) | ~278k | $1,200 | https://gofile.io/d/B******8, https://gofile.io/d/4P*****Y, https://gofile.io/d/C8*****A |
2026-10-03 | Patient contacts (Australia) | 428k | $1,100 | https://gofile.io/d/s*****0 |
2026-10-03 | Email contacts (Argentina) | 478k | $900 | https://gofile.io/d/8*****Z, https://gofile.io/d/eB*****Q, https://gofile.io/d/Y******B |
2026-10-02 | Admin access (Canada) | access | negotiable | https://www.pasteboard.co/3x********Ju.png |
2026-10-01 | Cloud access (India) | access | negotiable | https://www.pasteboard.co/GS********vP.jpg |
2026-09-25 | Loan applicants (US) | 120k | not stated | https://pastebin.com/qb*****BD |
2026-09-23 | Employee records (Saudi Arabia) | 80k | not stated | https://pastes.io/kb*****D |
2026-09-19 | User profiles (UAE) | 430k | not stated | https://pastebin.com/9E****3u |
2026-09-18 | CRM and candidate data (Saudi Arabia) | 627k | not stated | sample rows pasted into the post |
2026-09-16 | Booking Data (Austria) | 421k | not reviewed | snapshot not opened |
After this, it became clear that the US loan company post that started the investigation was one entry in a much longer catalogue, and the catalogue has a visible pattern. The early listings in September arrived every few days, each with its own description. Then, on what the forum recorded as the night of 3 October, seven threads went up between 02:41 and 03:01, one every two to four minutes.
All seven follow the same structure: a dataset line, a three-part structure description, a price, "Contact & Transaction", "Secure Transaction", and a nearly identical promise of escrow or a trusted middleman. Four of them still carry the template's own placeholders. Some of the posts quote a price followed by [Insert Your Price Here], while others follow theirs with [Your Offer]. Someone was filling in a form at speed and not reading the output.
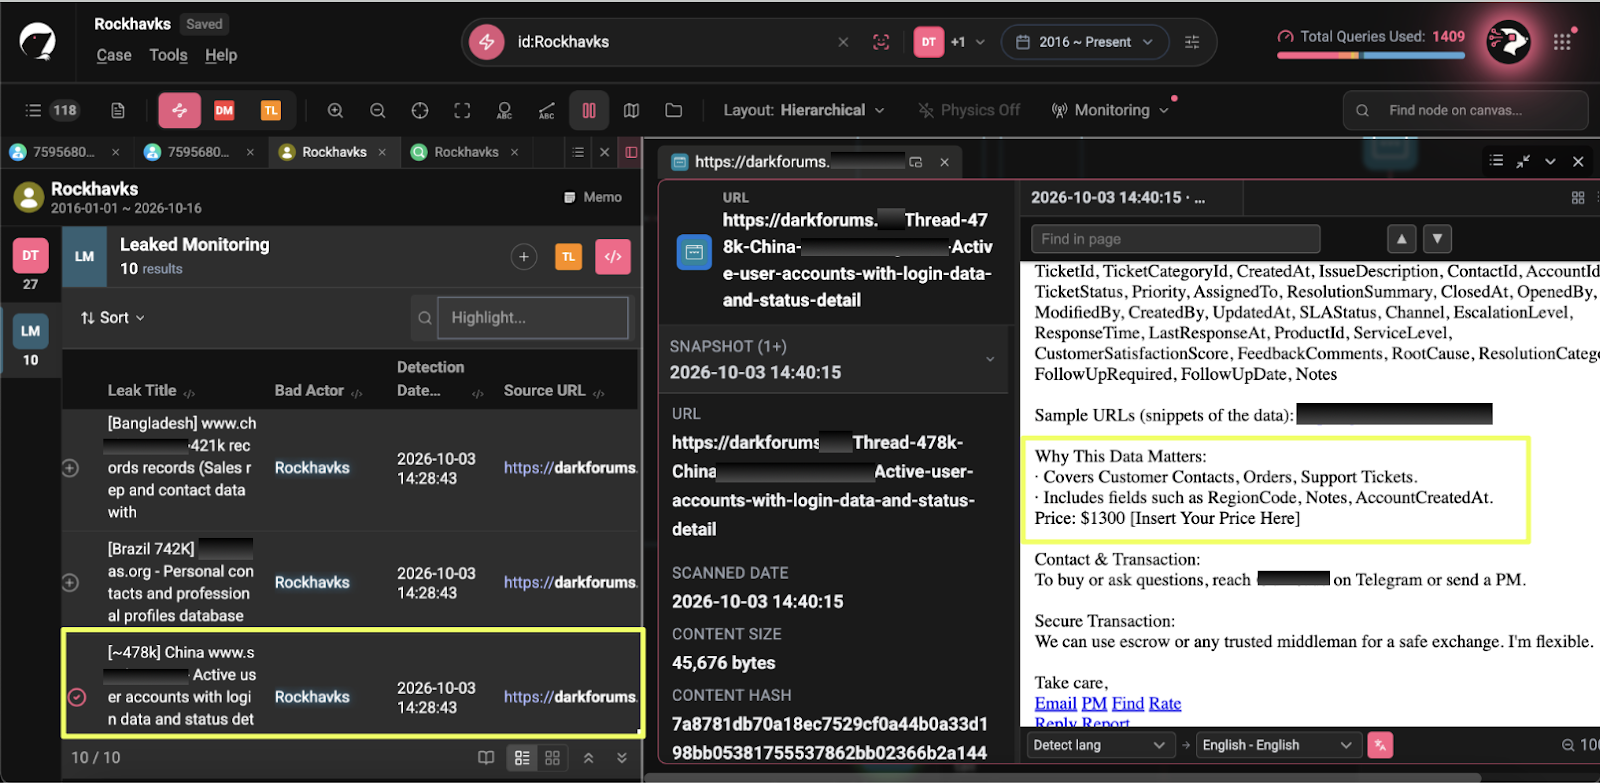
The forum's own counters track the acceleration. When StealthMole captured the Mihnati thread in mid-September, the account showed 3 posts across 2 threads. By 3 October, it stood at 22 posts and 16 threads, by 5 October at 33 and 27, and by 9 October at 44 and 37.

The numbers inside the listings deserve as much attention as the pace. Two unrelated companies in two different continents, Brazil and Canada are both offered at exactly 742k records. Argentinian and Chinese companies are both roughly 478k. Booking data in Austria and sales data in Bangladesh both sit at 421k.
Prices barely move with the content: a set of Australian patient records is priced the same as a South American email list. Genuine breaches rarely line up this neatly, and sellers who know what they hold usually price sensitive data higher. The pattern is more consistent with a seller who is recycling figures across templates, padding volume, or reselling material they have not closely examined. The investigation did not test the samples, so the data's authenticity remains open, but the listings themselves give a buyer good reason for doubt.
Two listings break the pattern. On 1 October 2026, Rockhavks advertised access to an Indian government cloud login portal, with a title promising that "classified documents" had been revealed. A day later came admin access to a Canadian property company with "full backend control". Neither came with a dataset or a Session ID, only a pasteboard image as proof and a line inviting buyers to negotiate on Telegram. These are claims of live access rather than leaked files, and they represent a step up in what the seller says they can offer.
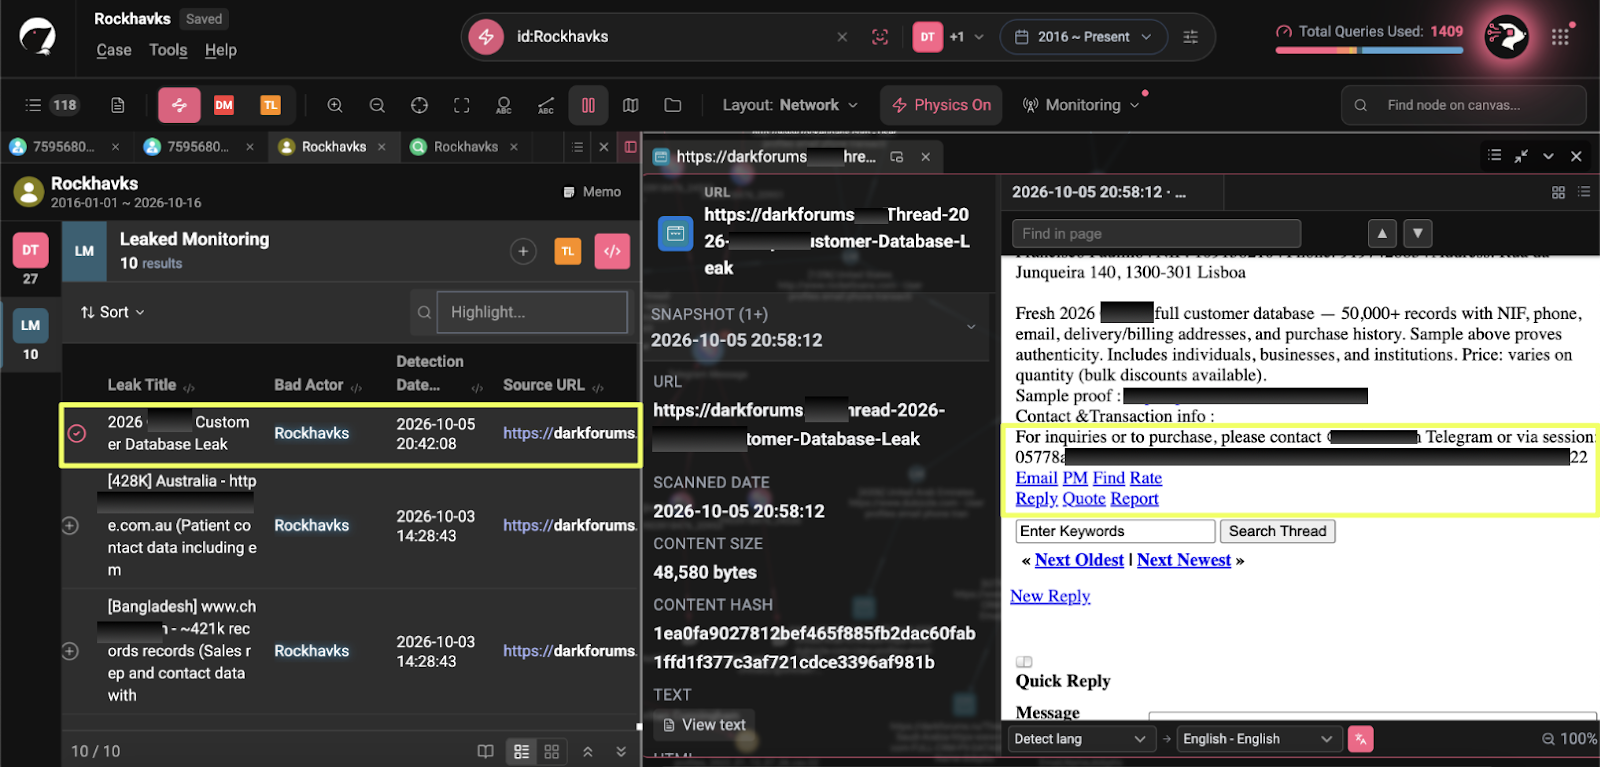
One small inconsistency also surfaced. The Portugal customer database listing on 5 October replaced the usual Session ID with a different one:
- 0577**************************************************7322
Further investigating it across StealthMole returned only that single thread. It may be a backup account, or the start of a migration away from the first one. Nevertheless, it has no recorded history yet so the original session ID remained the contact point worth following.
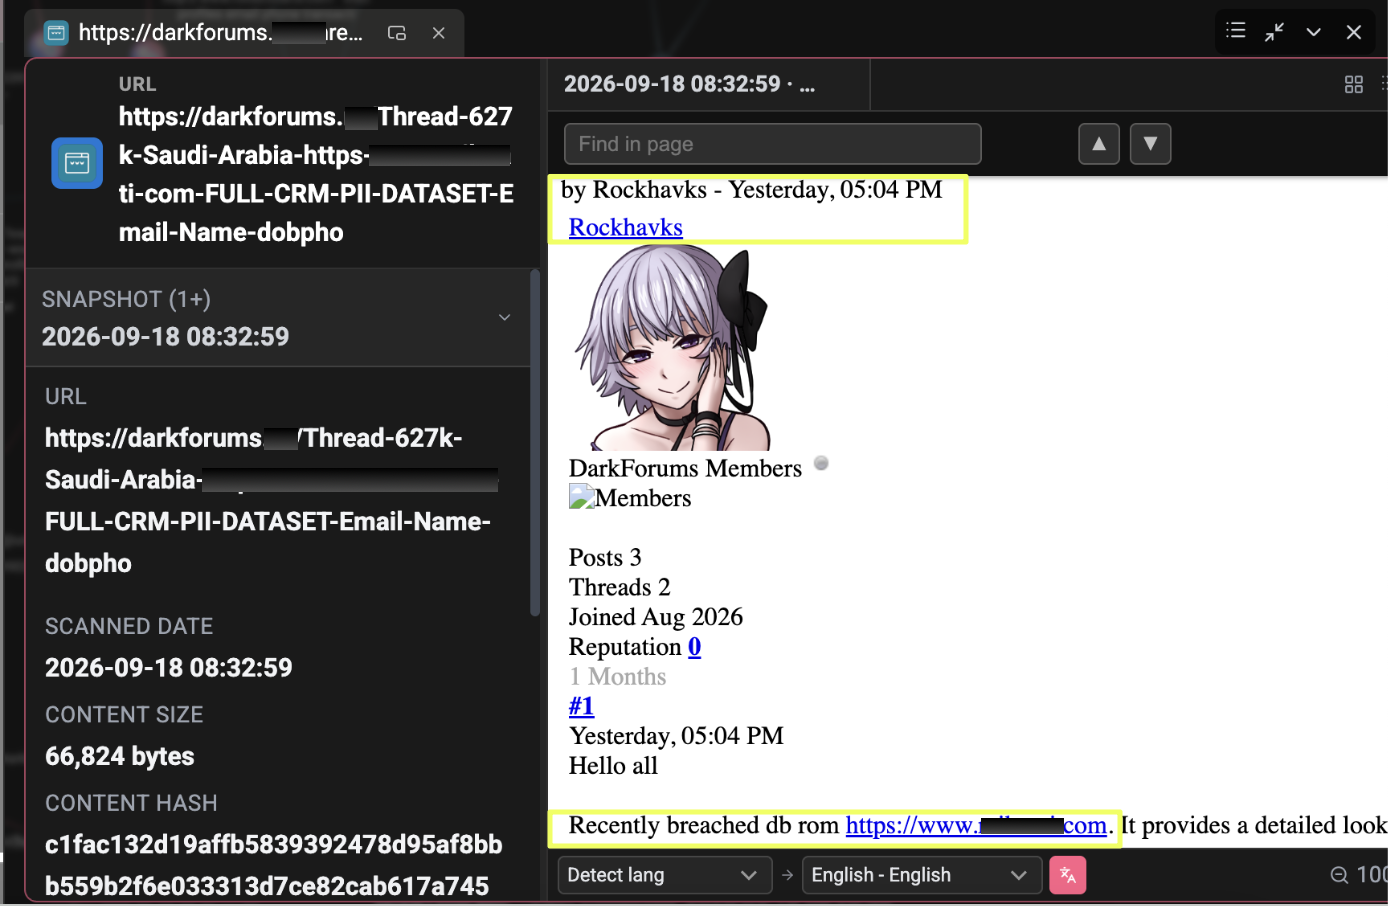
Moreover, the Saudi Arabian CRM Database thread also surfaced something interesting, that would matter later. The thread was opened with a sentence, “Hello all Recently breached db rom https://www.mi********i.com”, containing a typo. On its own, it has no value as anyone can make a mistake while typing, however, cross-searching the exact text on darkweb will add more to the investigation.
- breached.**
- breached.**
- Pwnforums.**
- darkforums.**
- darkforums.**
- darkforums.**
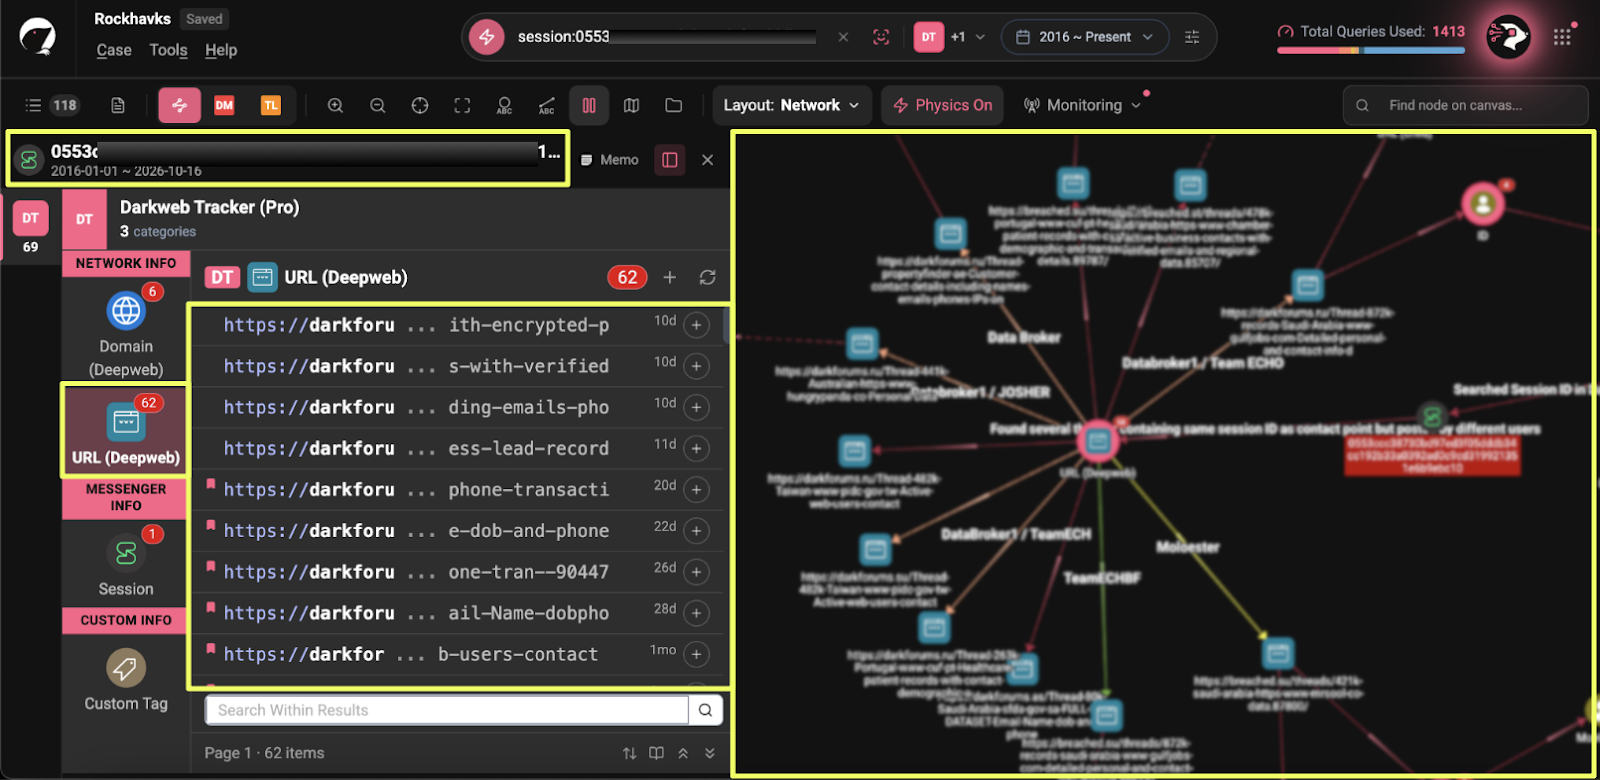
Every one of them was a sales thread listing the same Session ID as a way to buy. Only a handful were posted by RockHavks. The rest belonged to other accounts and unfolded another layer of this investigation.
Account | Forum | Seen from | Telegram contact in posts | Listings opened |
Moelester | BreachForums | 27 Mar 2026 | @bat**kb_f, later changed to @df****ta | cha****.sa (Saudi Arabia), m****ti.com, zal****do.com, jus*****t.co.uk |
Gtaviispeak | DarkForums (joined Nov 2025, now banned) | 2 Apr 2026 | @bat***kB_F | cha*****r.sa, j*.t**s-***ia.org (Japan), ver******pa.com (Finland) |
Databroker1 | DarkForums (joined Apr 2026, now banned) | 9 Apr 2026 | @df****ta, @bat***kB_F | p****c.gov.tw (Taiwan), si****en.se***s.pi.gov.br (Brazil), B**l.com (Belgium), pro******er.ae |
Bfdf2 | PwnForums (joined Apr 2026) | Apr 2026 | @df*****ta | mi******ti.com |
TeamECHBF | BreachForums | 25 Jul 2026 | @Te*****O1 | Gulf Jobs (Saudi Arabia) |
RockHavks | DarkForums (joined 17 Aug 2026) | 16 Sep 2026 | @un****7 | see previous section |
A shared Session ID on its own could mean several things. It could be one person running several forum accounts. It could equally be a broker or middleman who handles sales for several unrelated sellers, which is common enough in these markets that the overlap alone would not justify linking the accounts. What moves the picture beyond that is what the accounts reused besides the contact point.
The clearest example of this is the last sentence mentioned in the previous section. On 13 April 2026, Moelester posted the Saudi Arabia Dataset on BreachForums. Around the same time, an account called Bfdf2 posted it on PwnForums. Five months later RockHavks posted it on DarkForums.
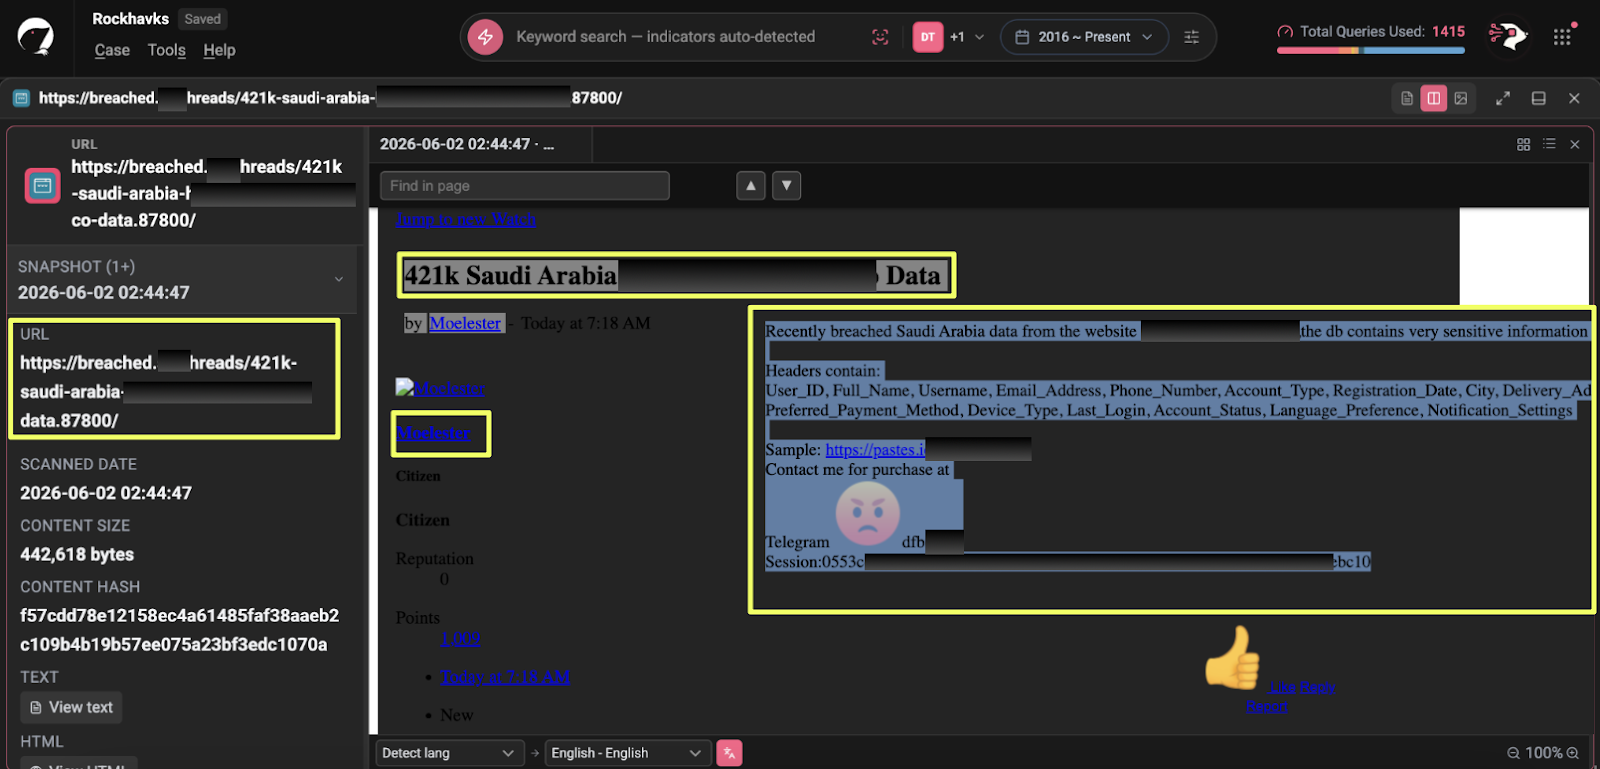
All three posts offer the same 627k-record dataset, all three list the same Session ID, and all three open with the same typo: "Hello all Recently breached db rom https://www.mi******ti.com". A broker relaying other people's listings might reuse a contact line. However, carrying a misspelling across three forums and five months is far harder to explain that way.
The sample links tell the same story. Moelester's chamber.sa listing on BreachForums and gtaviispeak's chamber.sa listing on DarkForums, posted a week apart, both point buyers to the identical file:
- https://gofile.io/d/Y8******eO
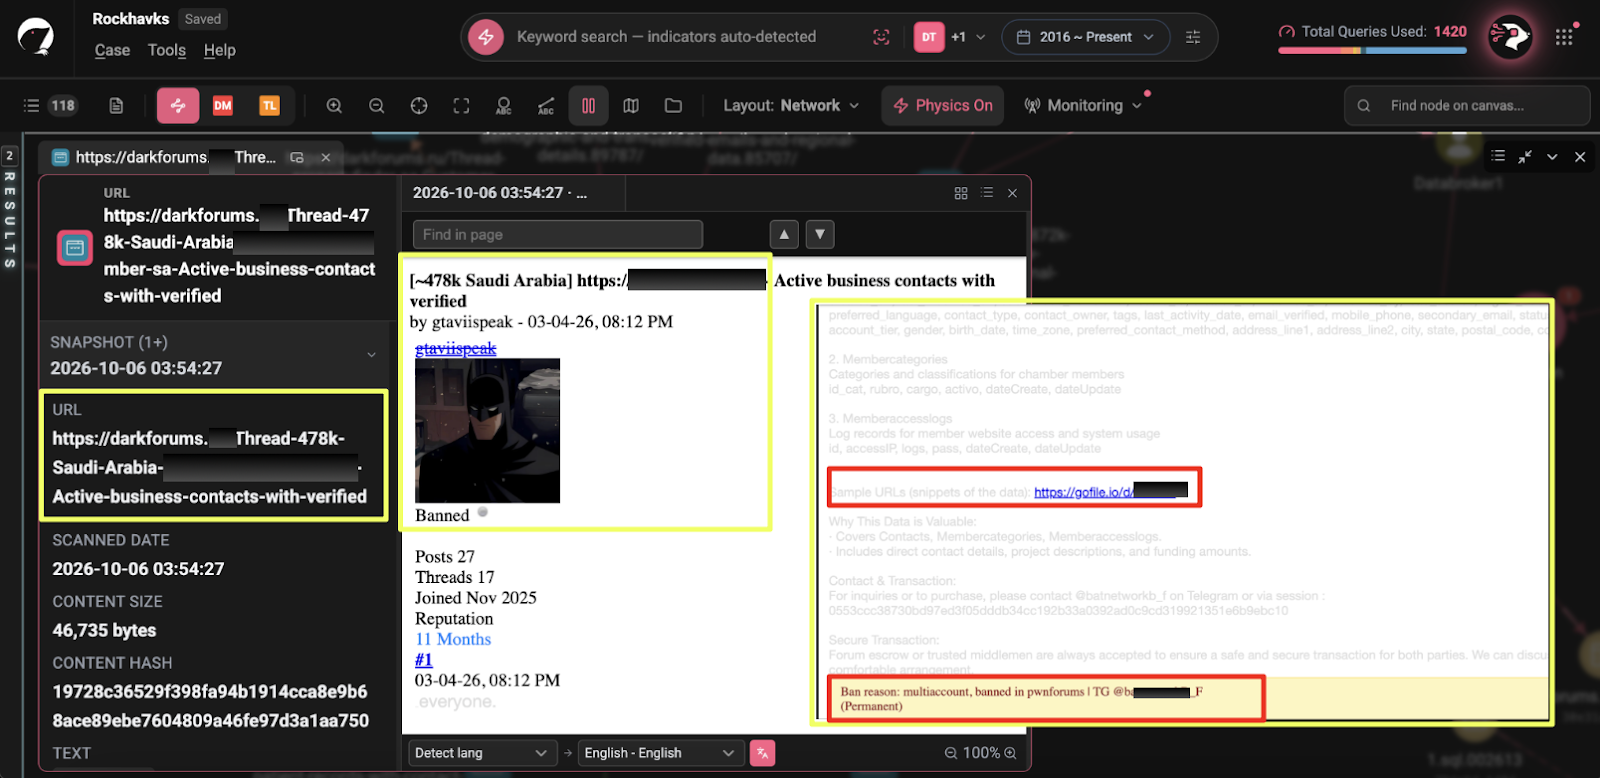
Gtaviispeak's three listings from early April also share a single construction, posted on consecutive days with the same opening "Hello everyone. Offering a dataset originating from…" and the Finland listing splits its sample into three gofile parts, the same habit that resurfaces across RockHavks' October posts. The forum names change; the shop window does not.
The Telegram contacts add a timeline of their own. In March and April 2026 the posts point to @bat*******kB_F. From April, @df*****ta starts appearing, sometimes alongside it. By September, RockHavks points only to @un*****7. The Session ID remained the same through all of it, which is exactly what you would expect if the Telegram handles were the disposable layer and the Session account was the one the seller could not afford to lose.
Team******F is the exception in this group. Its Gulf Jobs listing uses the same Session ID but a different Telegram contact, @Tea******O1, and there’s no shared typos, files or templates tying it to the others.
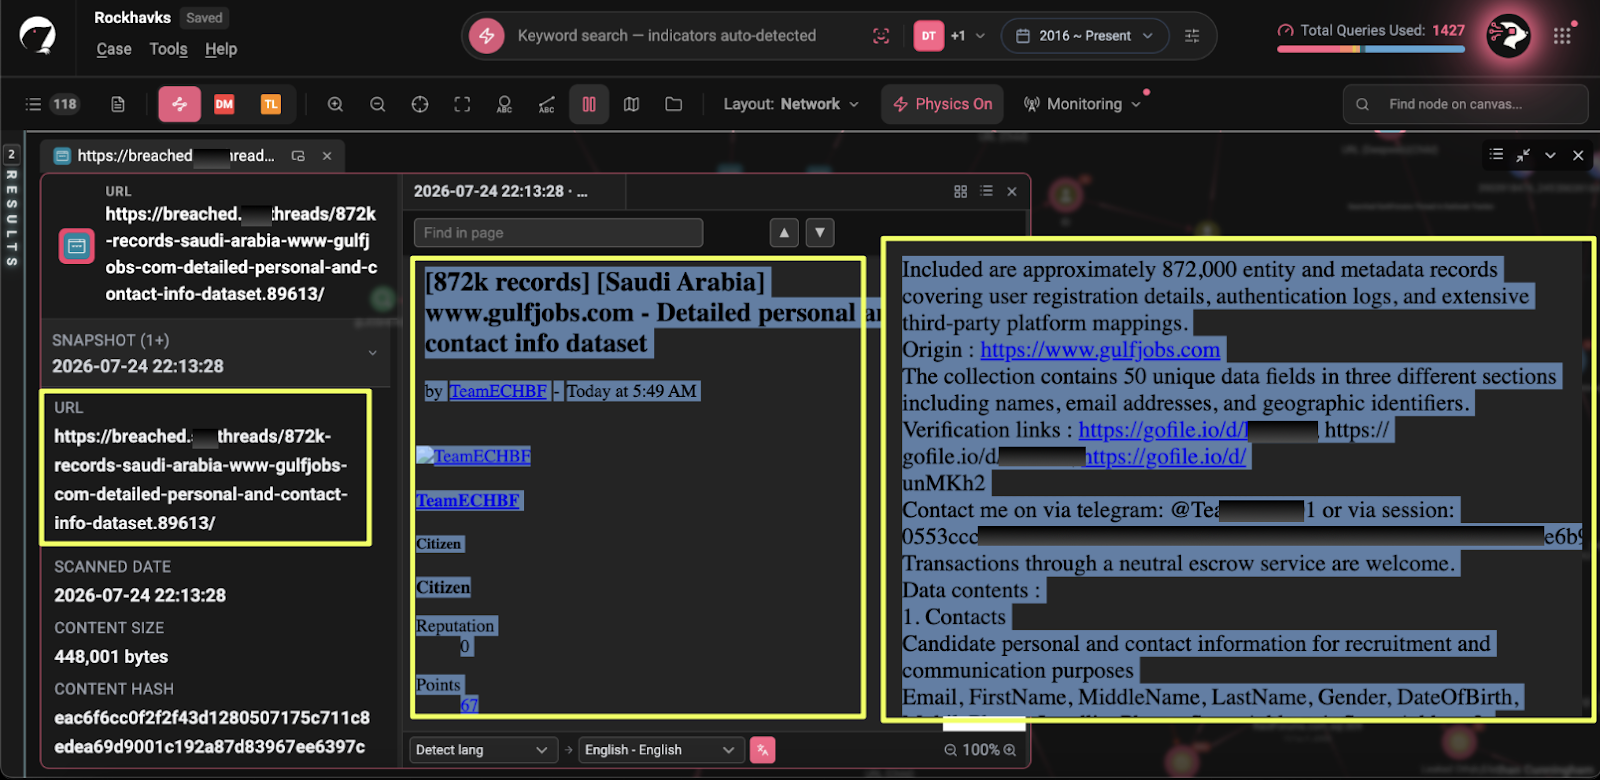
A further search for Te******O1 returned 20 Darkweb results and two Telegram file results that were not triaged. Team******F may belong to the same operation or may be a separate seller using the same contact point, and the evidence here does not settle which.
The Moderators Got There First
The strongest link between these accounts did not come from our own correlation. It came from DarkForums staff.
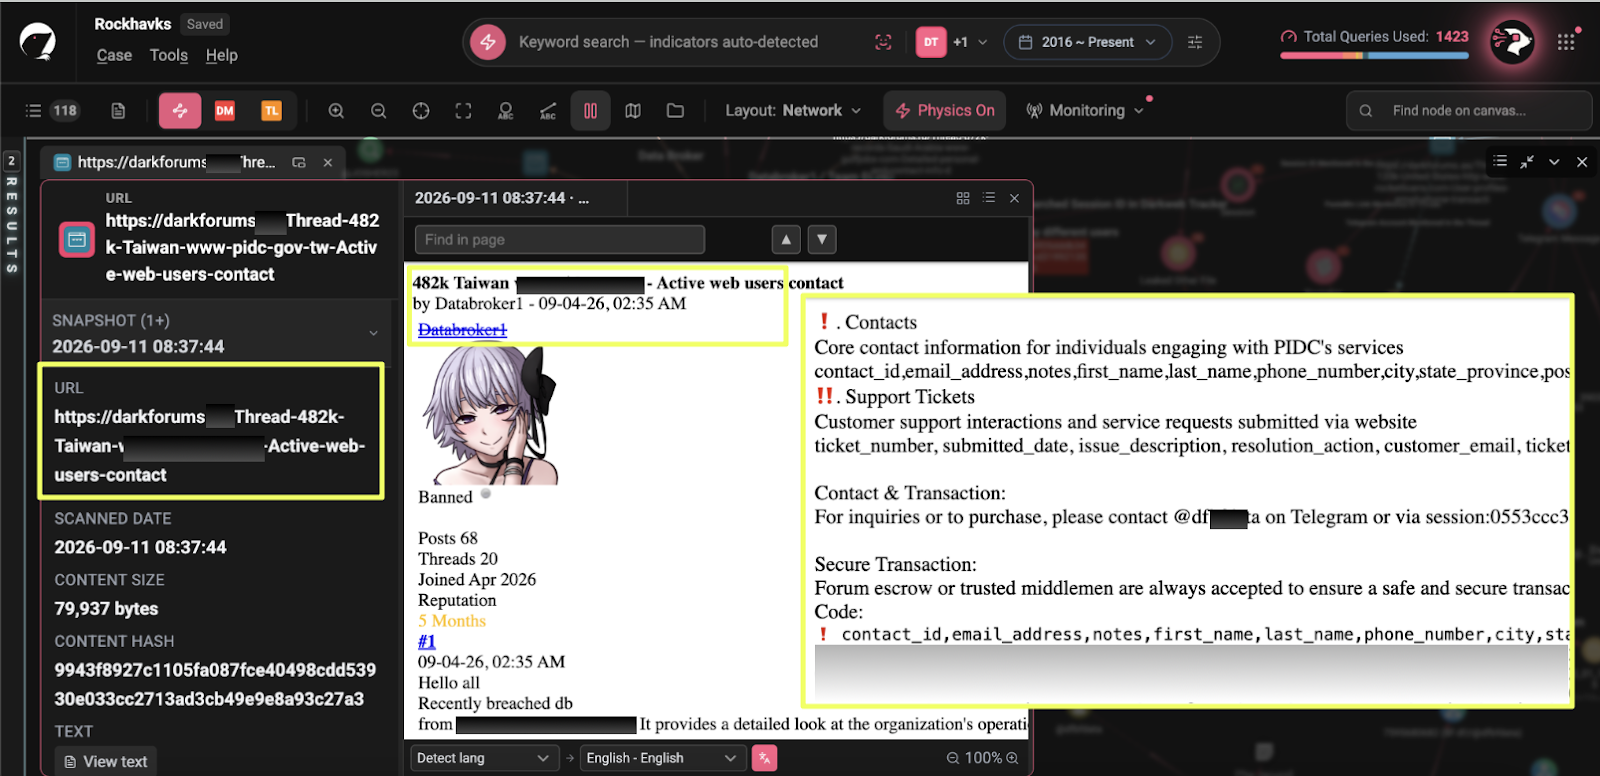
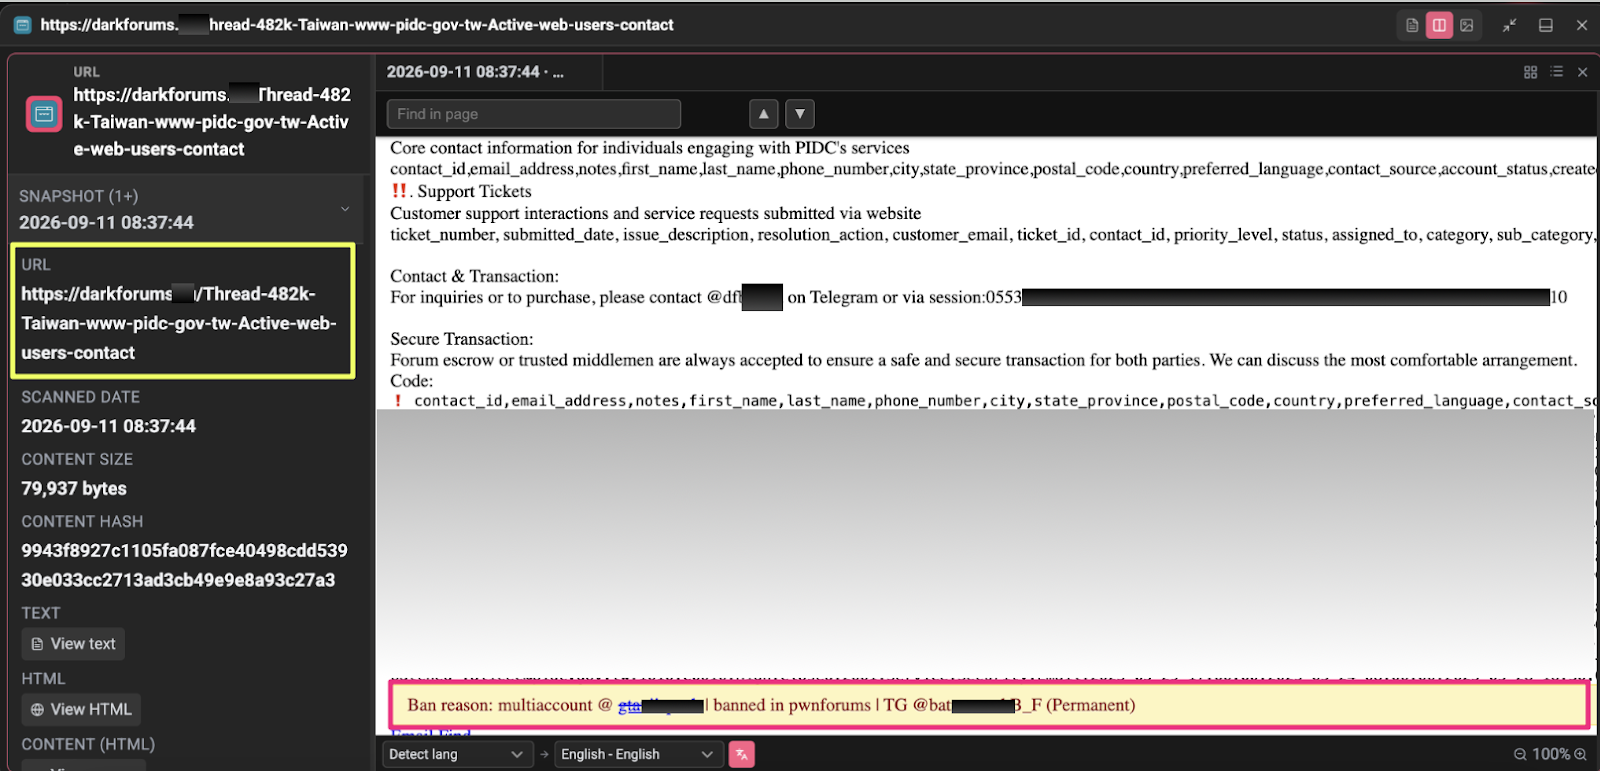
StealthMole's snapshot of Databroker1's Taiwan thread, captured on 11 September 2026, shows the account marked as banned, with the moderator's reason printed under the posts:
- Ban reason: multiaccount @gt*****ak | banned in pwnforums | TG @bat*****kB_F (Permanent)
Gtaviispeak's own threads carry an almost identical note:
- Ban reason: multiaccount, banned in pwnforums | TG @bat*****kB_F (Permanent)
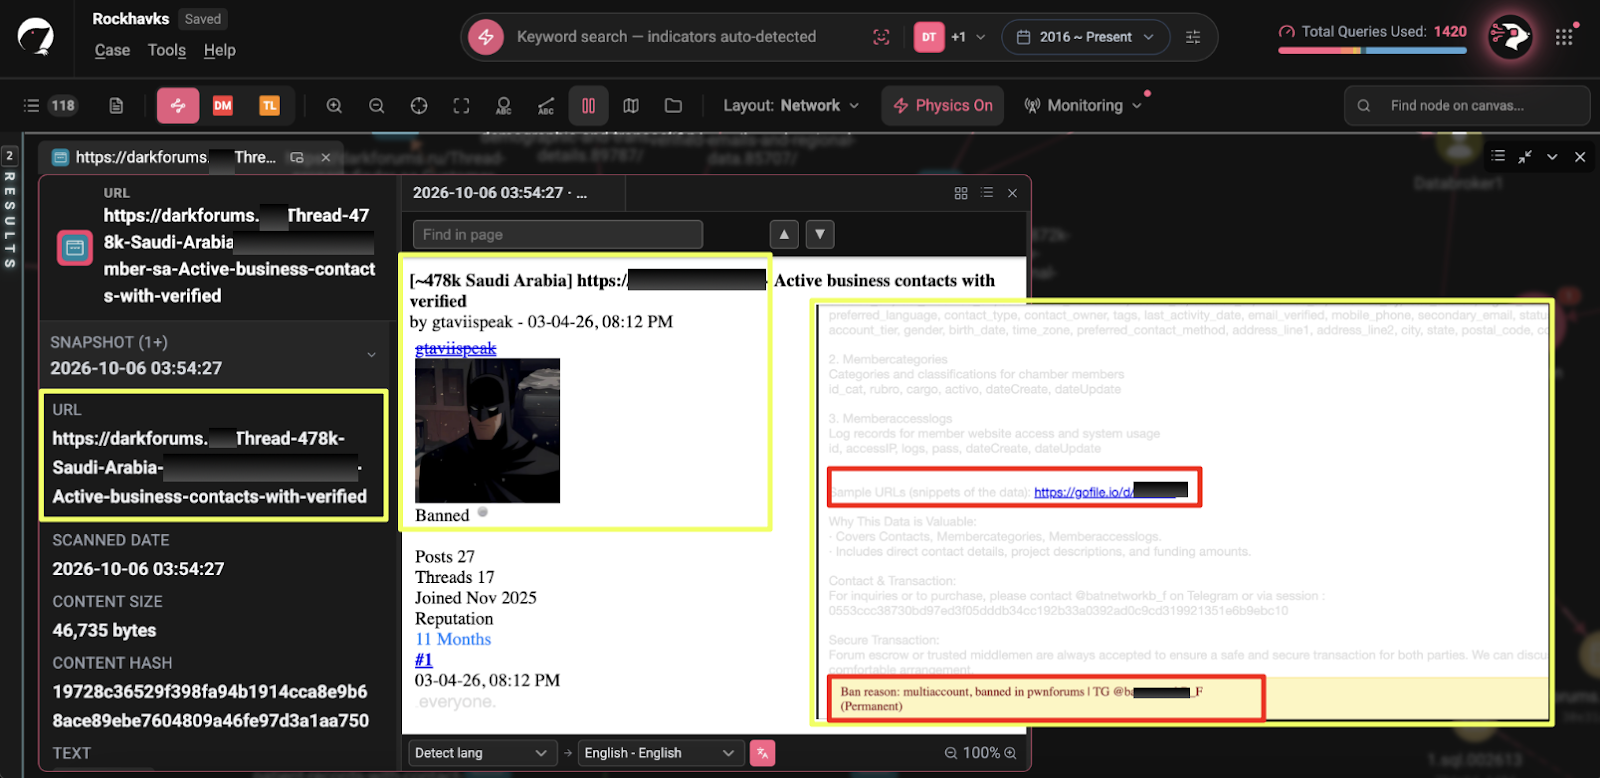
In other words, the forum had already concluded that Databroker1 and gtaviispeak were the same operator, that the person behind them had been banned from PwnForums, and that the Telegram account @bat********kB_F tied them together.
Moderators on these forums have access to things outside investigators' reach, such as registration IPs, browser fingerprints and private messages, and their judgment is not always right. However, in this case, it lines up exactly with what the indexed data shows independently: the same Session ID, the same Telegram contact, and listings recycled between the two accounts. Two separate routes reaching the same answer makes the link considerably more reliable than either would be alone.
The timing around Databroker1's ban is also telling. It was shown as an ordinary member through August, still posting listings for Brazilian prison records and customer data, with its post count increasing from 60 to 63. By 11 September, it was banned at 68 posts. RockHavks had registered on 17 August 2026, while Databroker1 was still active, and posted nothing that StealthMole indexed until 16 September. An account opened weeks in advance and switched on just after its predecessor disappears looks less like a new seller than a spare key cut before the old lock was changed.
The pattern of losing an account and starting again was not new for this operator. The Telegram account behind @df******ta had been complaining about it in public for a year.
One Telegram Account, Four Names
While forum identities and accounts can easily be discarded and replaced, a Telegram user ID remains unchanged, even when the account’s display name and username are modified. Further investigating @df***ta in Telegram Tracker resolved it to user ID 7595680682. Moreover, StealthMole indexed 75 messages from that ID across underground chat groups, covering nearly two years and four different usernames: Anos, Kneeguard, GROCK and Bfdf.
Anos: From Forum Discussions to Data Sales (November 2024 to Early November 2025)
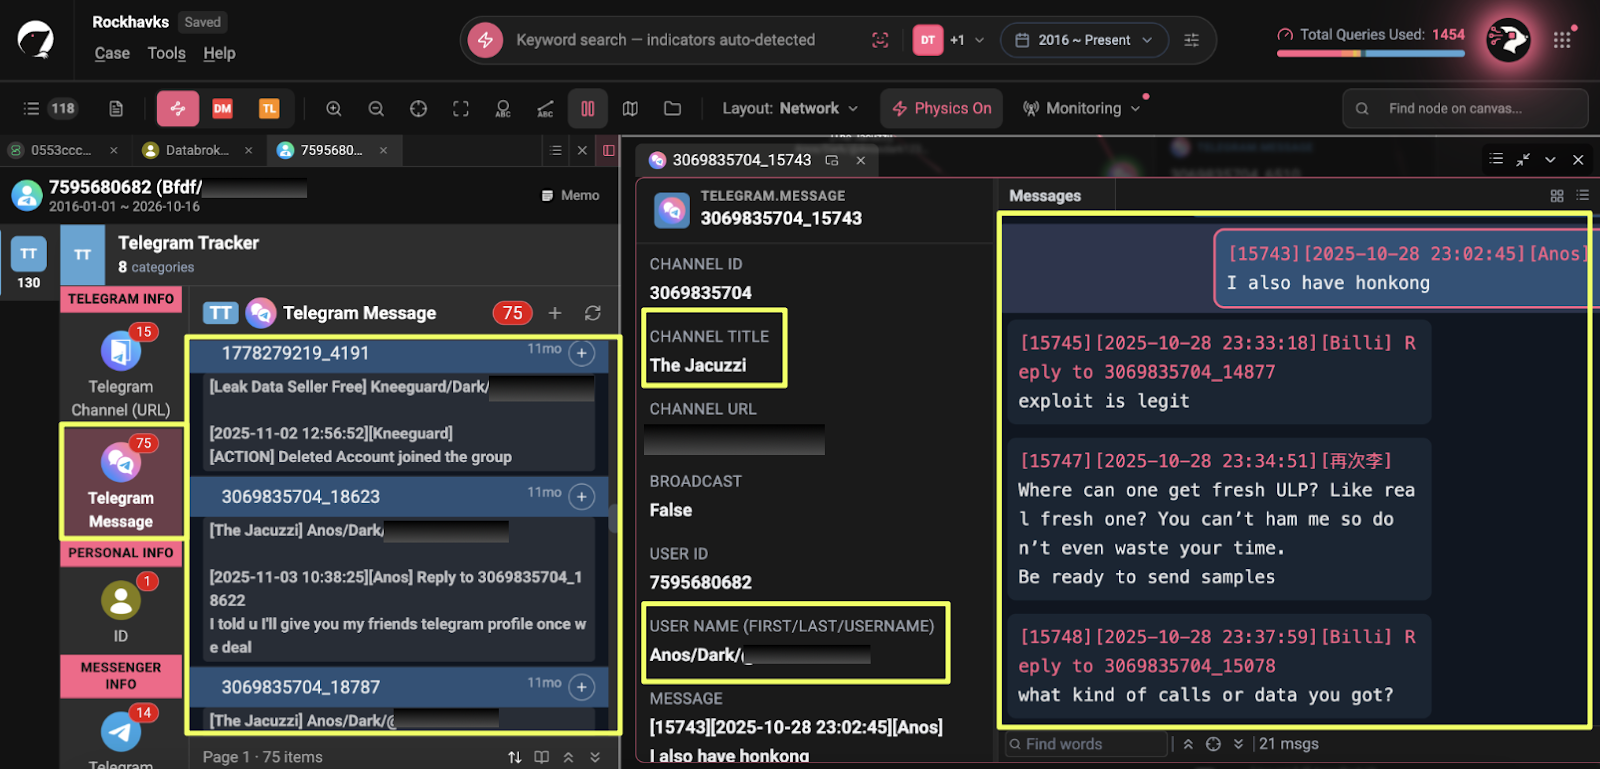
The account first appeared in Jacuzzi 5.0 on 13 November 2024, without a username, asking, "Does anyone here know how to hack??" It soon expressed interest in finding "a tool that's not known by many people" and, two days later, complained about being broke. By May 2025, using @Anos******3, it was discussing active breach forums in The Jacuzzi.
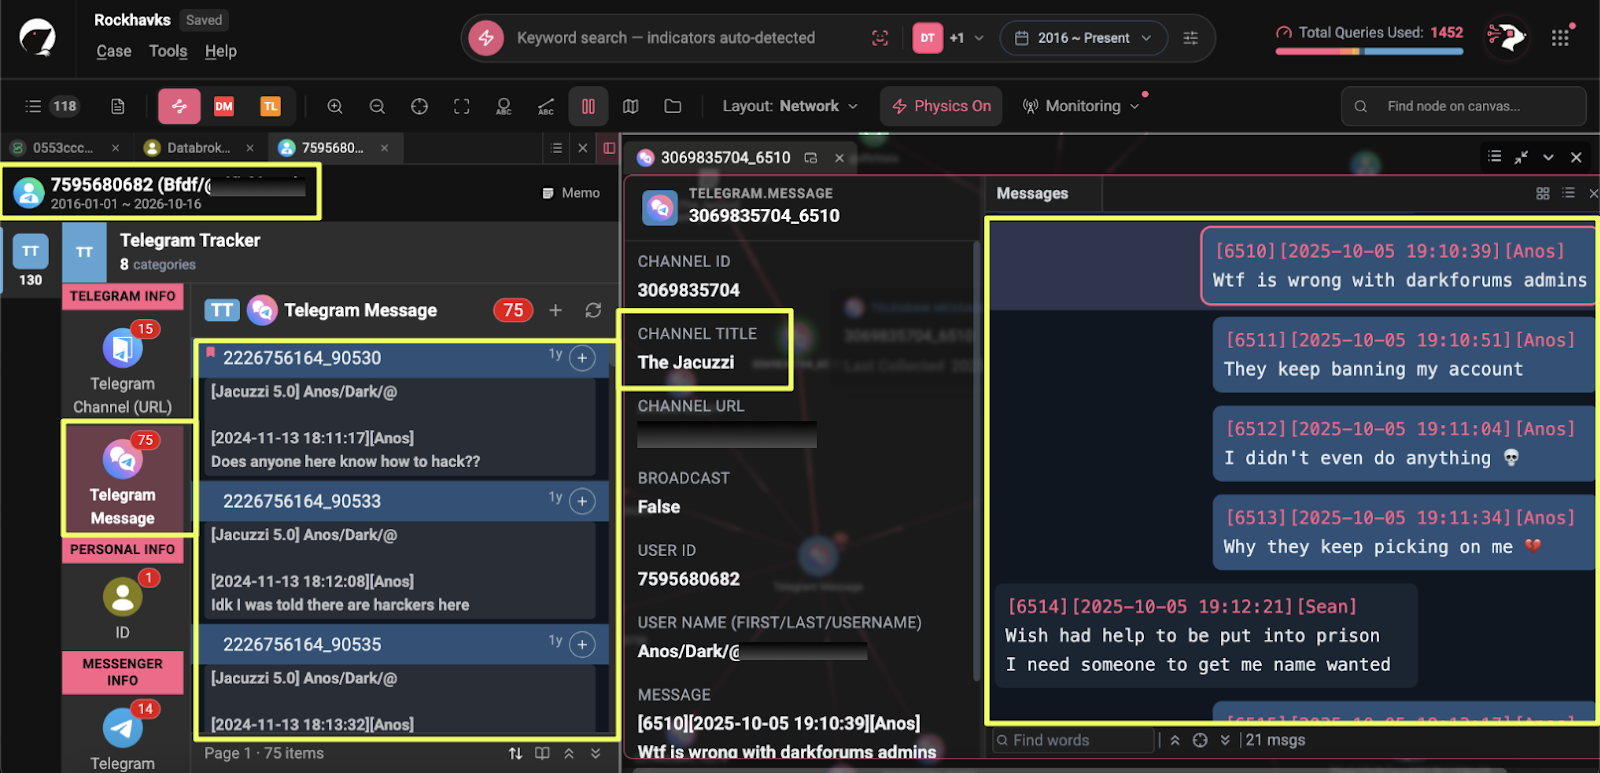
By September and October, the messages reflected growing frustration with DarkForums administrators. On 5 October 2025, the account complained that its accounts kept getting banned, followed by another appeal on 14 October. Later that month, its activity shifted towards data sales. On 28 October, it posted, "I also have honkong", followed by repeated invitations for interested buyers to message privately.
Kneeguard: Selling Bundled Databases (November to December 2025)
In early November, the account adopted the name Kneeguard and username @Gt*****ak. On 17 November, it advertised a package titled "10 Chinese Database in 1, Price: $2000", listing databases associated with China-based banking, UnionPay, Yuantong Express, WeChat and China Telecom, among others. The post added, "MM is always accepted".
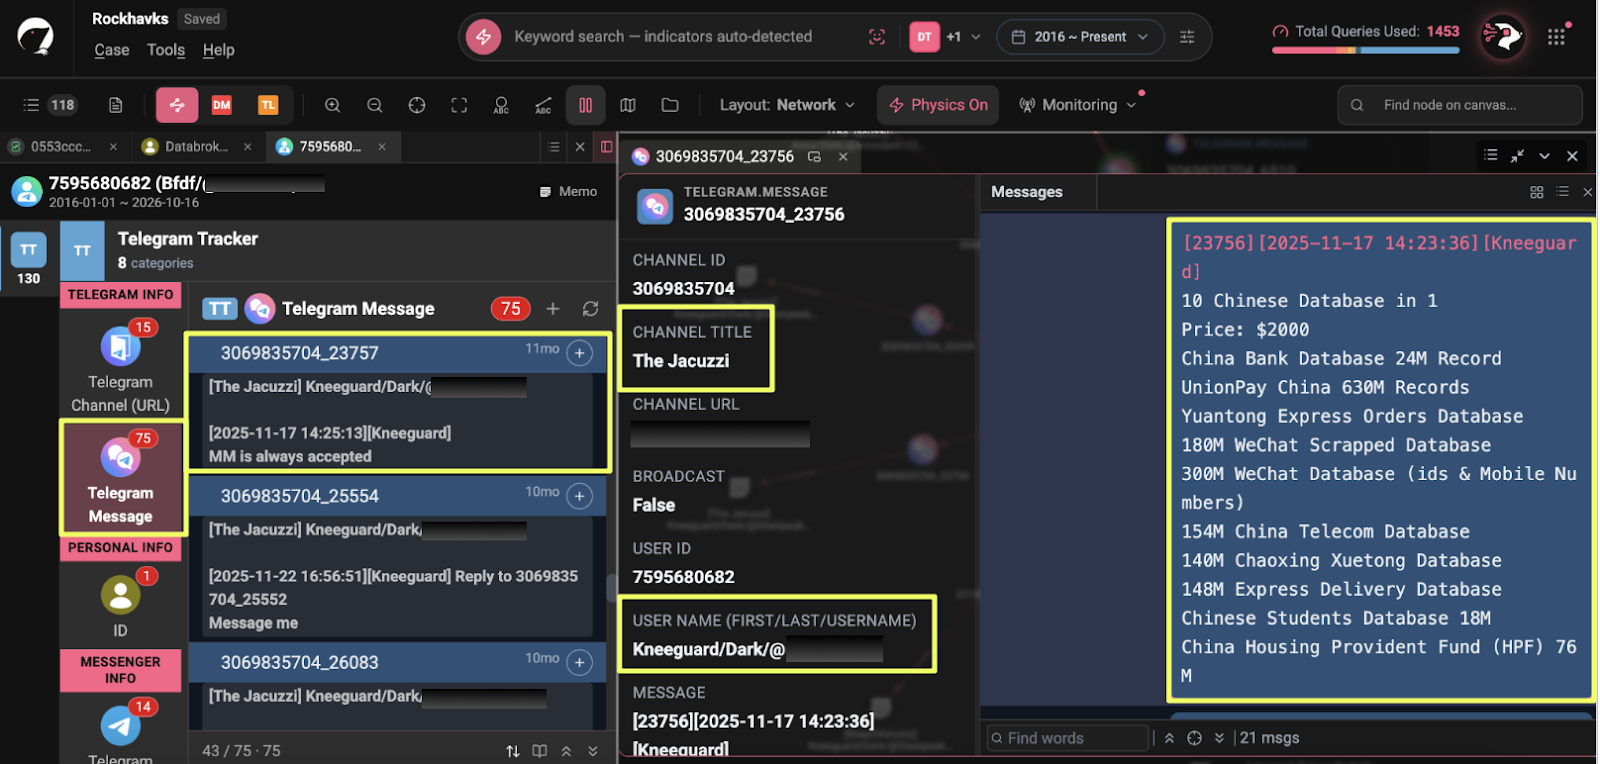
Subsequent messages provide a glimpse into its dealings with buyers. On 26 November, it disputed a delivery complaint, writing, "I sent u the db u just stupid", and described an arrangement in which it had given someone "$1k for 50" because there was no trust between the parties. On 21 December, it told a member of a BreachForums community group that it had sent its wallet address privately.

The Telegram username also bears a resemblance to gtaviispeak, a name registered on DarkForums in November 2025. The spelling and timing make the connection worth examining, but they do not establish that the two accounts belong to the same operator. The available ban note associates gtaviispeak with @bat********kB_F, rather than directly with Kneeguard. The proposed link therefore remains tentative, with the shared Session ID and overlapping sales activity providing additional context for the wider investigation.
GROCK: Operating Within Trading Communities (January to February 2026)
In January 2026, the account changed its display name to GROCK, using @cha*****bq and later @non******urp. Its messages in Jacuzzi 2.0 and a BreachForums group focused largely on disputes over transactions and alleged scams. It accused one user of scamming, mocked another for attempting to scam someone for $11 using fake escrow, and advised others to use escrow services.
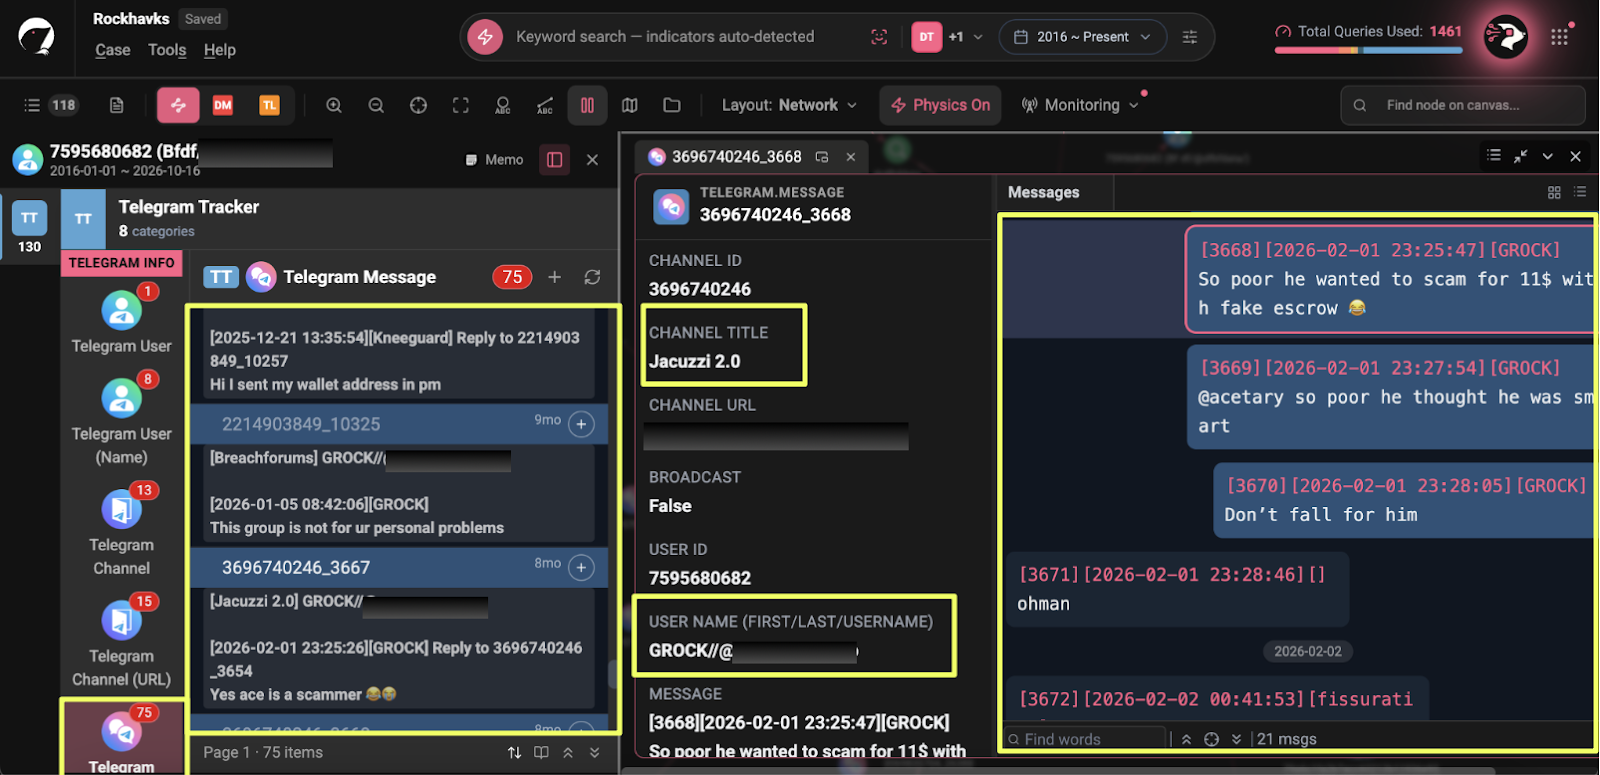
These exchanges show the account participating in the community's trading disputes, although they do not independently establish how many transactions it completed or whether its advice reflected its own business practices.
Bfdf: A Recognised Name in Sales Threads (April to August 2026)
By 9 April 2026, the account was using the name Bfdf and username @df*****ta. In a BreachForums group, it asked, "Escrow by @cupid?" During the following months, Moelester, Bfdf2 and Databroker1 included this handle in their sales threads.
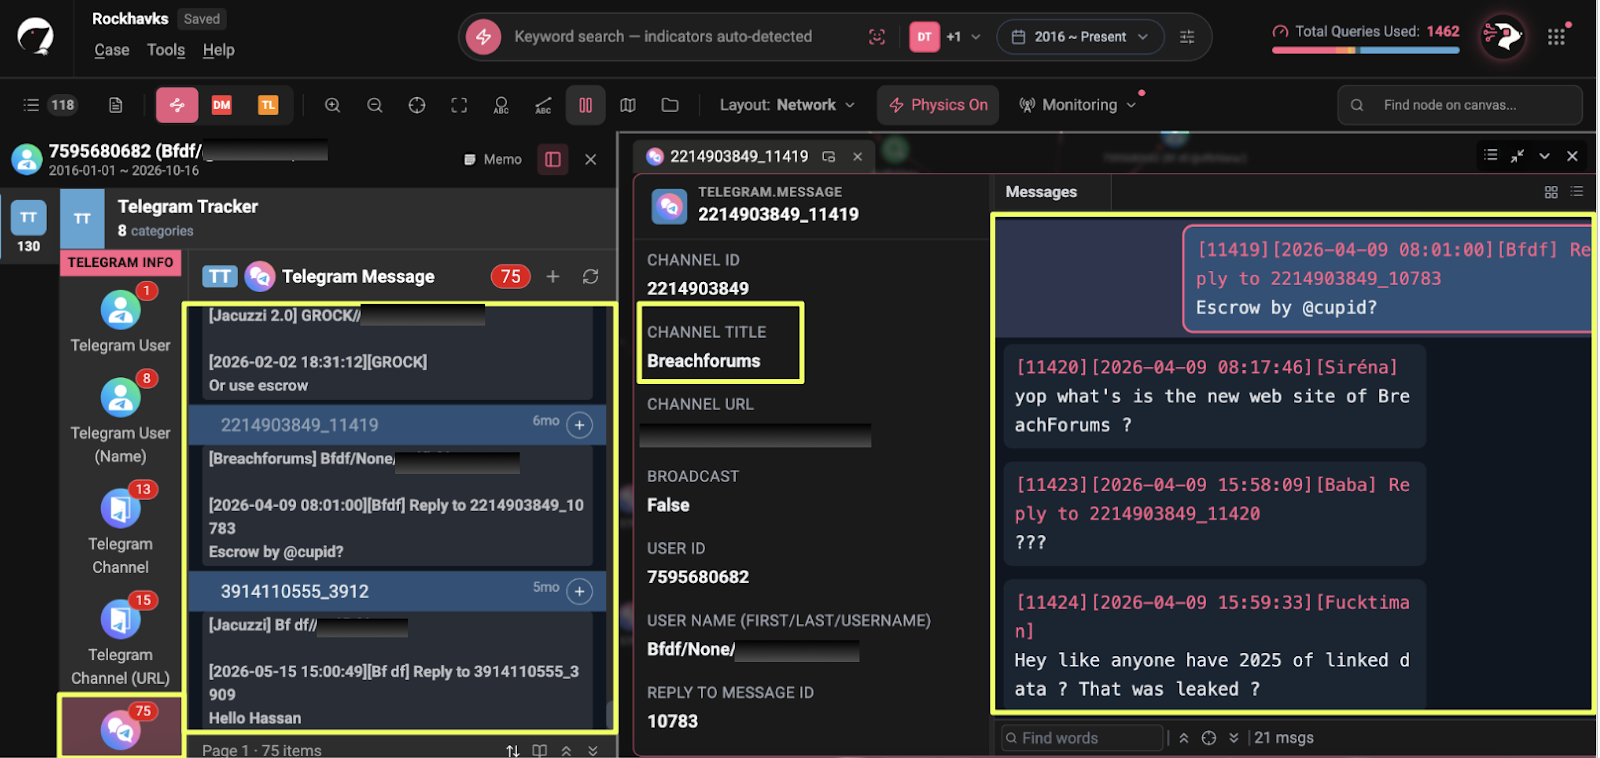
The Bfdf name also resembles the PwnForums account Bfdf2, but the naming similarity alone is insufficient to confirm common ownership. The more firmly established link is the continuity of Telegram user ID 7595680682 across the account's changing identities.
The Separate Bat Network Account
A second Telegram account complicates the picture. @ba******k*F resolves in Telegram Tracker to a different user ID, 8439065746, displayed as Ba*******k*F, with 14 indexed messages. On 5 February 2026, it advertised "Email and company data from these countries available" alongside an image in Jacuzzi 2.0, where GROCK had also been active earlier that week.
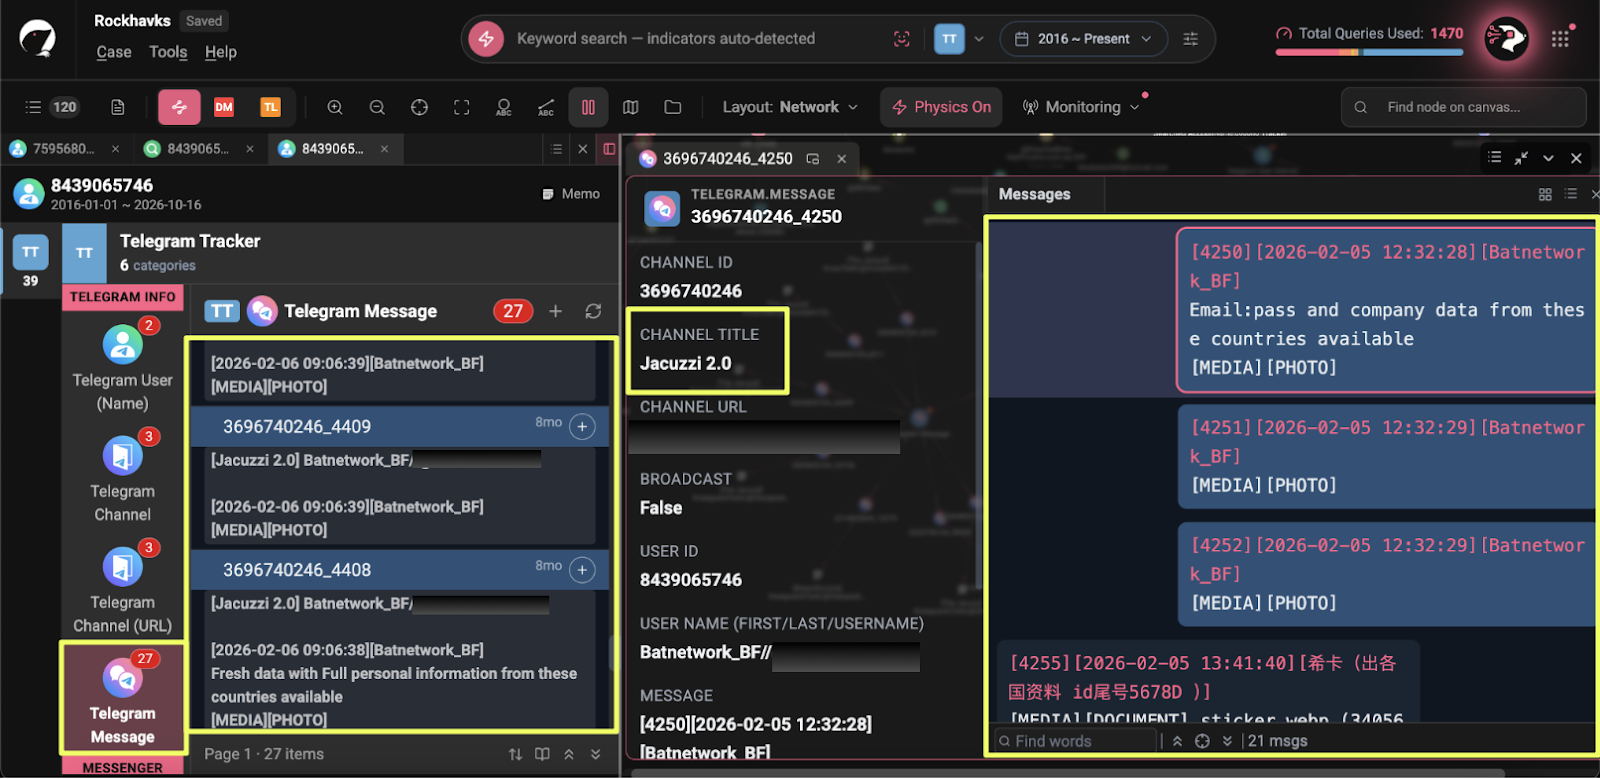
The two accounts should not be treated as identical. Their activity in the same trading community and the references connecting @bat**********F to forum moderation provides grounds to investigate a possible relationship, but the available messages do not establish whether the accounts share an operator, belong to associates, or operate independently. The sales threads' use of both handles in related contexts supports further examination, not a definitive attribution.
Enter Unload: The RockHavks Connection (August to October 2026)
The Telegram contact advertised by RockHavks resolves to @un*****7, with the display name Unload and numeric user ID 8654837808.
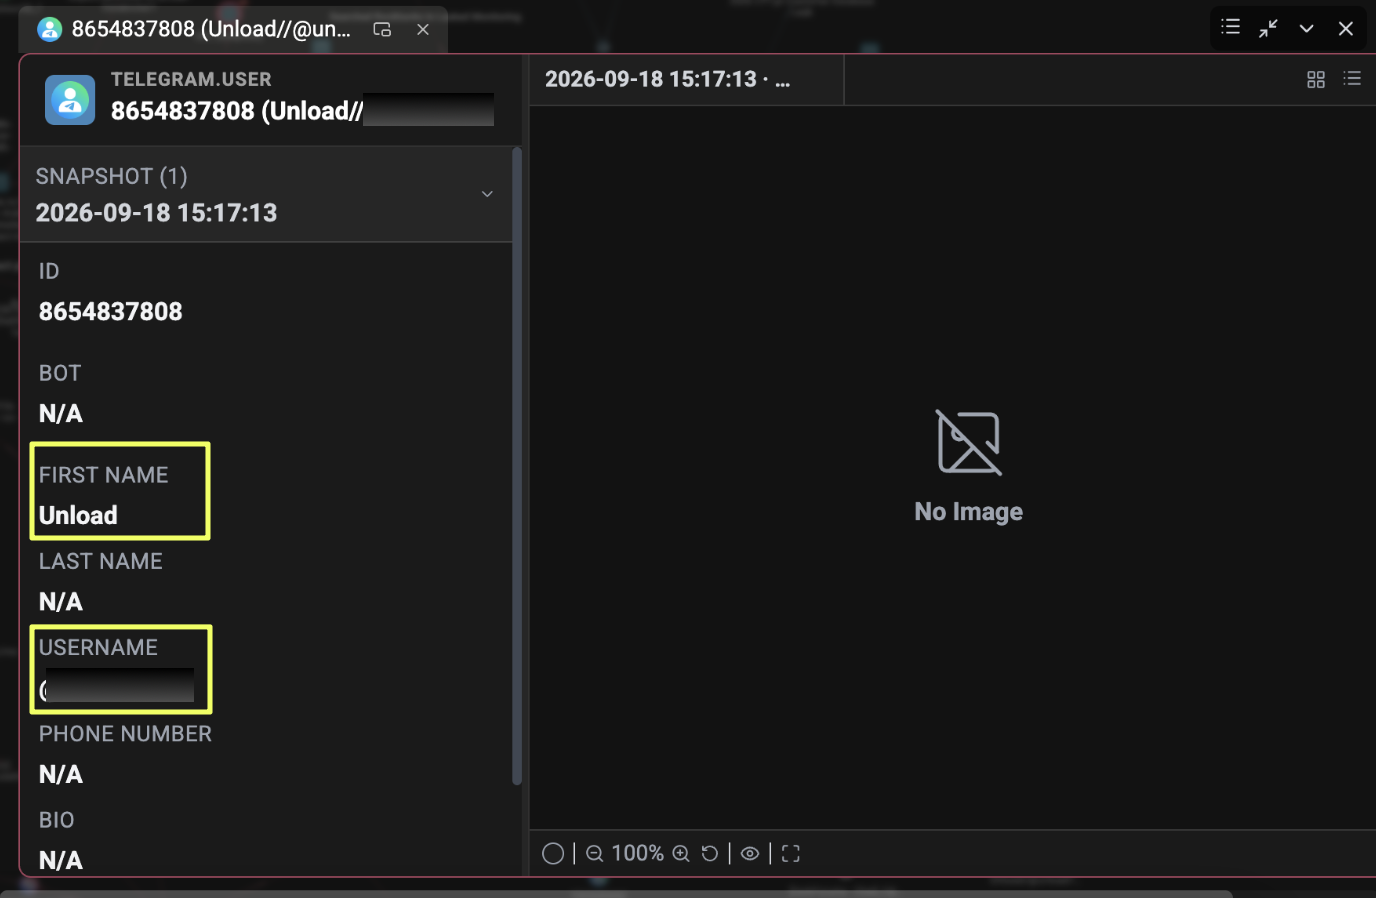
Its earliest recorded messages, posted on 30 August 2026 in a group called DarkForums, show the account asking for the forum's current URL.
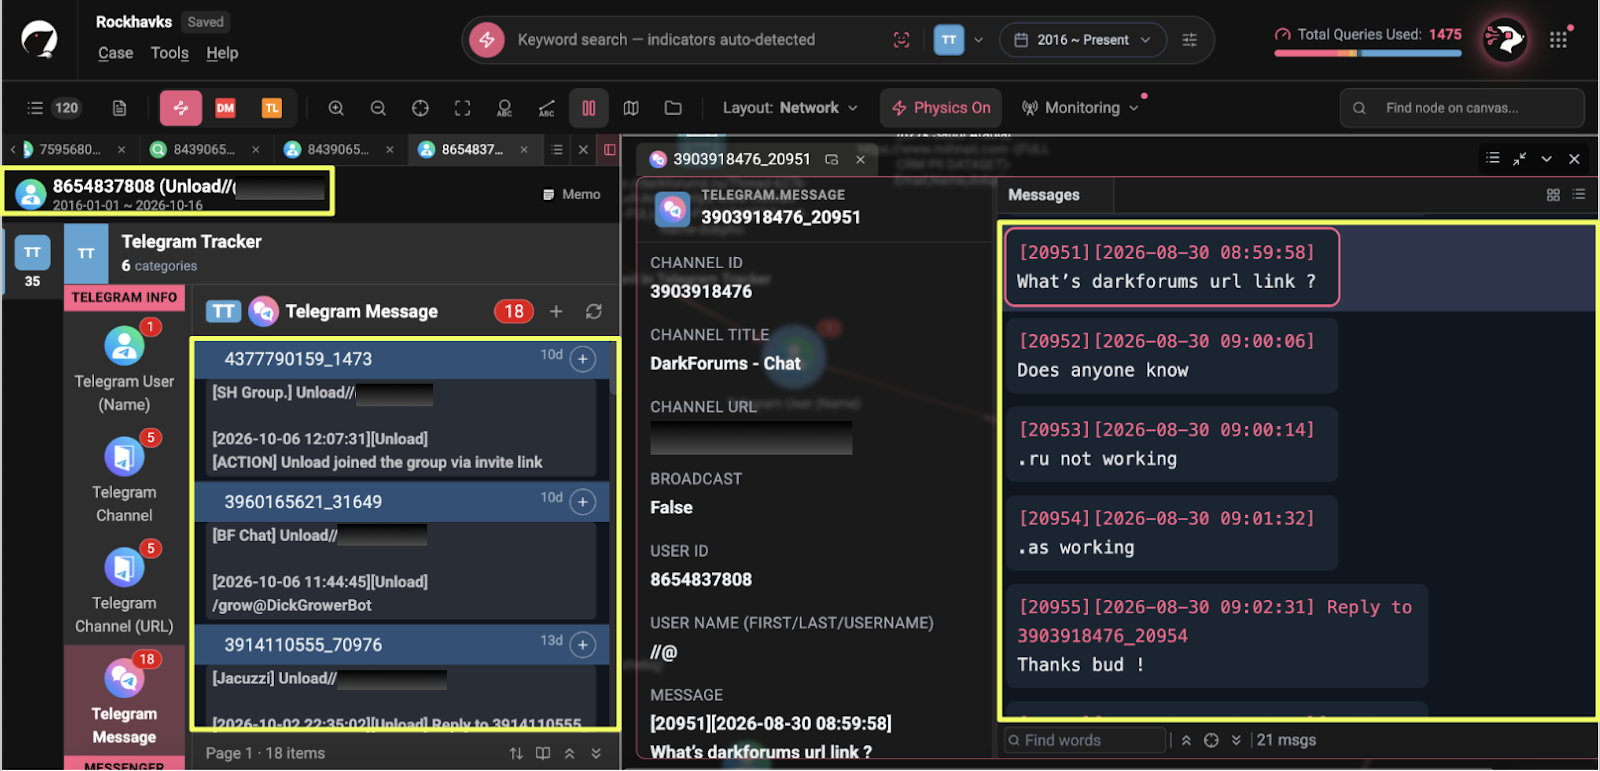
The exchange is unremarkable in isolation. Its timing is more relevant: RockHavks had registered on DarkForums thirteen days earlier, while Databroker1's threads were still active. The account's search for a working forum address is consistent with someone trying to regain access to the community, though it does not establish that @un*****7 was preparing a replacement storefront.
Later messages place @un*****7 in several of the same underground chat environments associated with the earlier accounts. On 18 September, in DarkForums, it asked, "Why would mod scam for 20?" and posted, "Indians just be saying shit". On 27 September, it commented in another group, "Mosad life is filled with a lot of comedy 😭". On 2 October, in Jacuzzi, it asked, "What's this Indian spamming for".
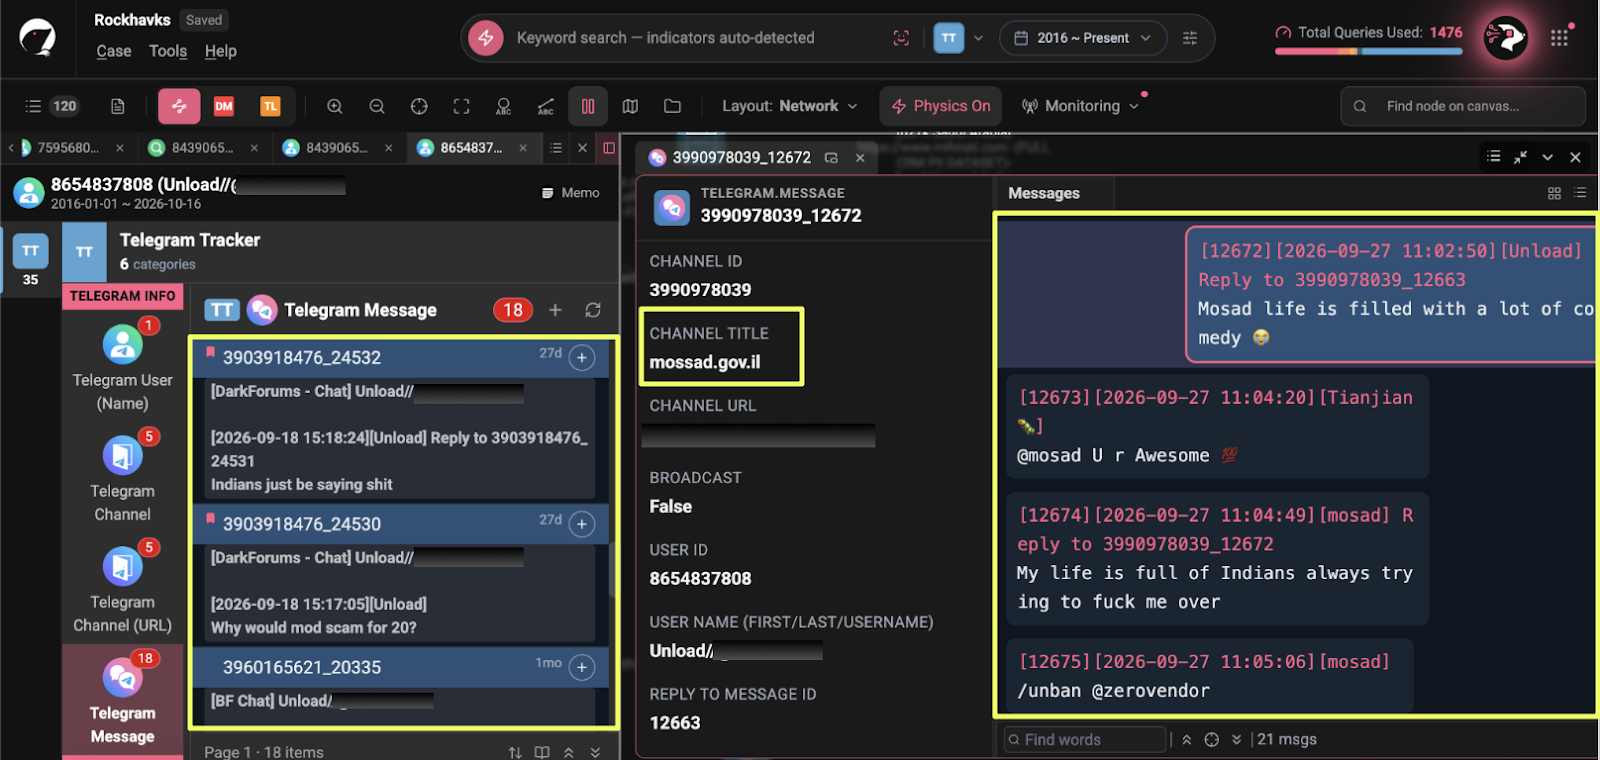
The recurring Jacuzzi groups provide continuity in the wider investigation: Anos, Kneeguard and GROCK were active in The Jacuzzi, Jacuzzi 2.0 and Jacuzzi 5.0, while @bat********F advertised in Jacuzzi 2.0. However, shared group membership and similar remarks are weak indicators of identity on their own.
Conclusion
RockHavks appeared to be a new seller, but the investigation uncovered signs of an operation with a much longer history. Tracing the contact details in a single listing led to earlier storefronts across BreachForums, PwnForums and DarkForums. The same Session ID had been in use since March 2026, months before the RockHavks account appeared, and at least two of the linked forum accounts had been banned for operating multiple accounts. The listings also retained striking similarities, including an identical typo in a description of a Saudi recruitment database.
The Telegram evidence extended this timeline further. Messages associated with user ID 7595680682 document the account's progression from seeking hacking tools in late 2024 to advertising bundled databases and participating in underground data trading by 2025 and 2026. The connection between this account's successive identities is established by the persistent Telegram user ID. The relationship between that account, @un******7 and the RockHavks operation is less certain and should not be treated as confirmed attribution.
Several questions remain unresolved. The investigation has not established the operator's real-world identity, independently verified the advertised datasets, or confirmed claims of government and business access. The relationship between @bat*********F, Team********F and the wider operation also remains unclear. These gaps matter: evidence of selling data does not, by itself, establish who originally obtained it or whether every advertised claim was genuine.
What the findings do show is that RockHavks' apparent novelty should not be confused with an absence of history. Repeated account changes, overlapping identifiers and recurring listing content provide a basis for linking the storefront to earlier activity. Forum bans may have disrupted individual accounts, but the available evidence suggests they did not necessarily end the underlying trading activity.
Editorial Note
Investigations into underground markets rarely produce absolute attribution. Accounts can be shared, sold or deliberately made to resemble one another, and a common contact does not automatically establish common ownership.
In this case, StealthMole's historical indexing of forum activity and Telegram messages helped connect identities across time while preserving the distinction between established links and unresolved relationships. The result is not a definitive identification of the operator, but a clearer account of the activity, its continuity and the questions that remain open.
To access the unmasked report or full details, please reach out to us separately.
Contact us: support@stealthmole.com
Labels: Featured, Threat Actor


