Escrow, Exposure, Erasure: Piecing Together YY520CN Before He Vanished

In early October 2026, YY520CN came under public scrutiny after CrowdStrike linked the actor to activity targeting South Korea’s financial sector. Within days, screenshots of the research began circulating in the same Chinese-language DDoS communities where the Telegram handle had been active for years.
The timing offered an opportunity to examine a part of the story that public reporting rarely captures: the actor’s history before the exposure. Using StealthMole, the investigation traced YY520CN’s activity across underground communities, examining how he presented himself, the services he offered, his payment arrangements, and the reactions within his network after the research became public.
The findings revealed a familiar name in a semi-public underground marketplace, where escrow arrangements and reputation played an important role in business transactions. The investigation also captured a change in behaviour following the public exposure, as YY520CN began removing parts of his online presence. What remained was a trail of activity that offered a closer look at the person behind the handle and the community in which he operated.
A Name in the Headlines
We started with the Telegram identifier available in the public reporting: YY520CN. A keyword search in StealthMole’s Telegram Tracker returned 937 messages, 22 images, 13 username records and one channel title match.
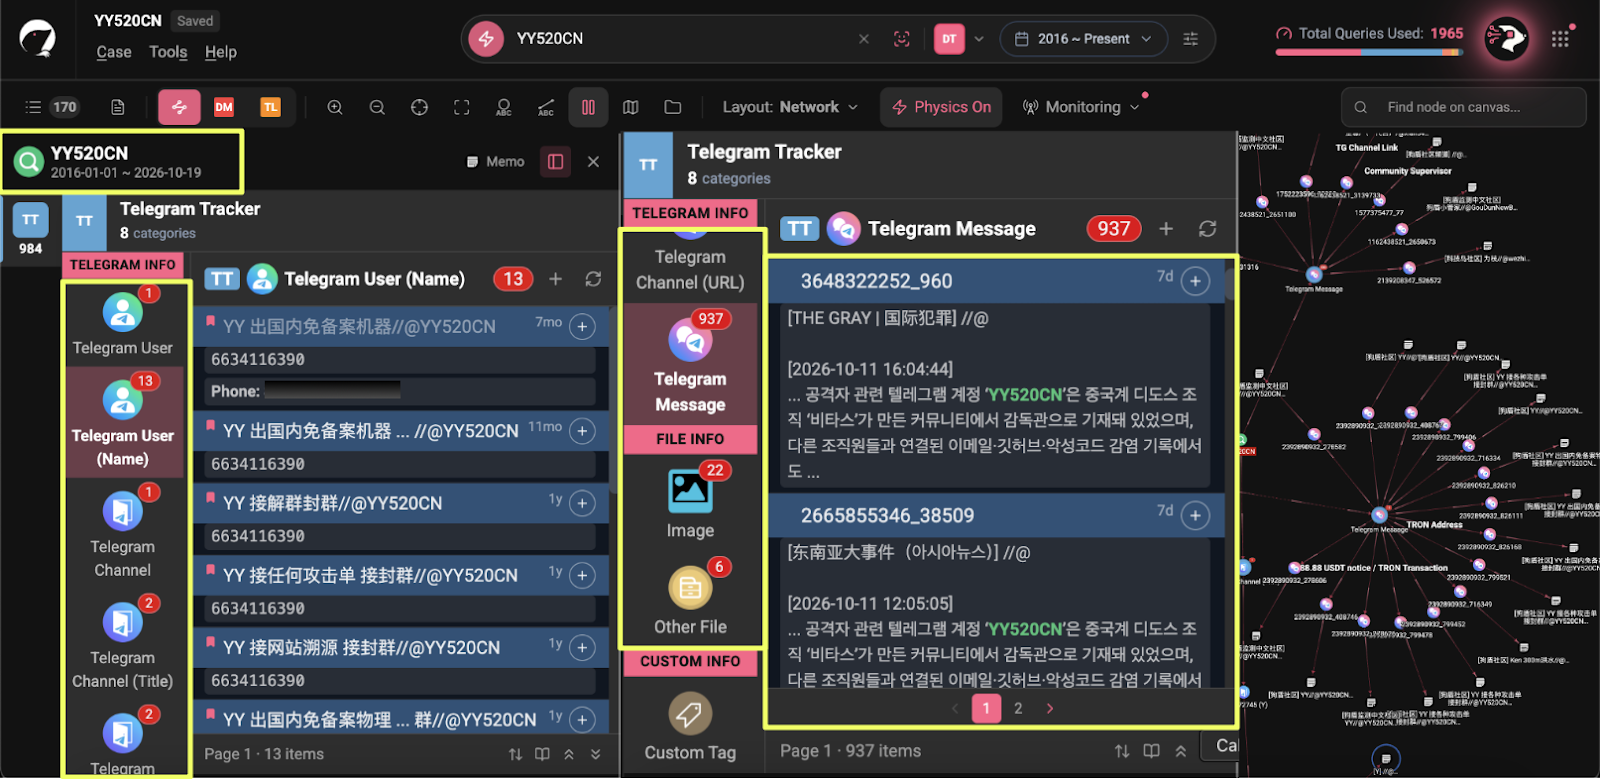
The results showed that YY520CN had an established presence across Chinese-language Telegram groups focused on DDoS services, hosting and underground trading. The volume of references also suggested that the handle was already circulating within these communities well before the recent security reporting brought it wider attention.
The username records provided the first useful pivot. All 13 usernames resolved to the same Telegram user ID:
- Telegram User ID: 6634116390
- Username: @YY520CN
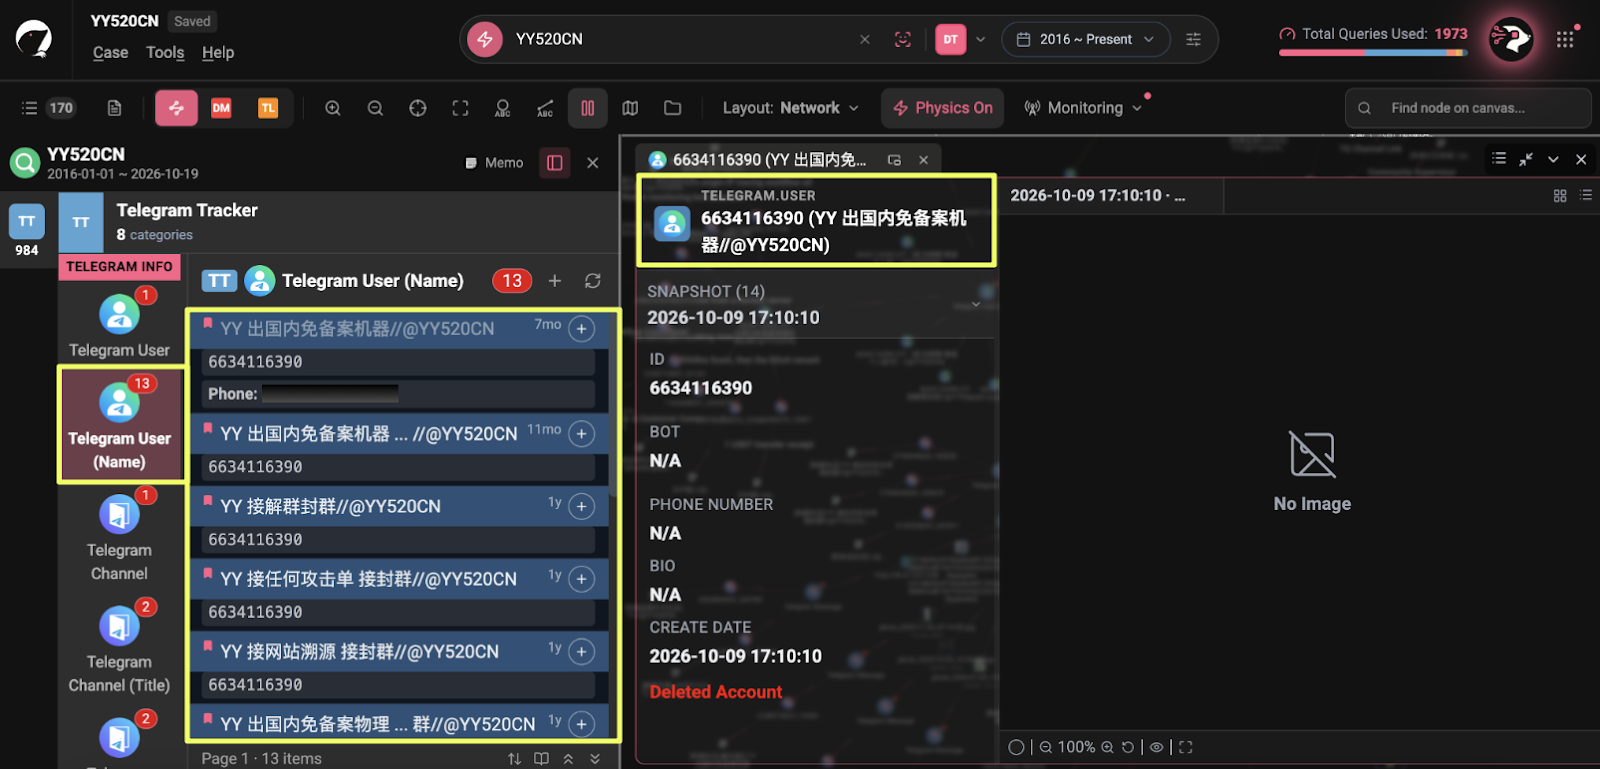
Rather than relying on the username alone, we shifted the investigation to the numeric user ID. This provided a more reliable way to follow the account across its indexed activity, including messages where the handle itself did not appear.
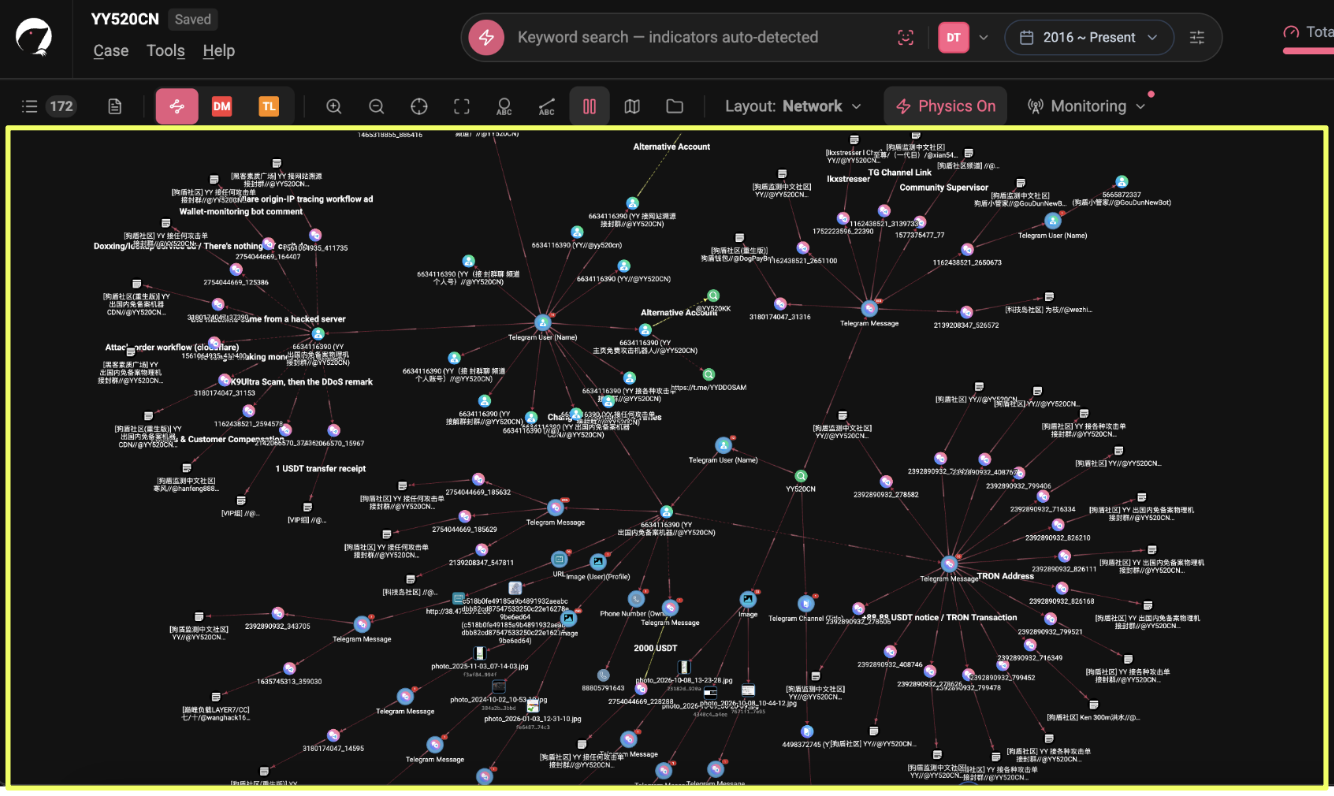
Searching by user ID expanded the dataset considerably, returning more than 2,000 indexed messages, 698 images, 36 URLs, a profile image and a linked phone number:
- Phone number: 888*****************43
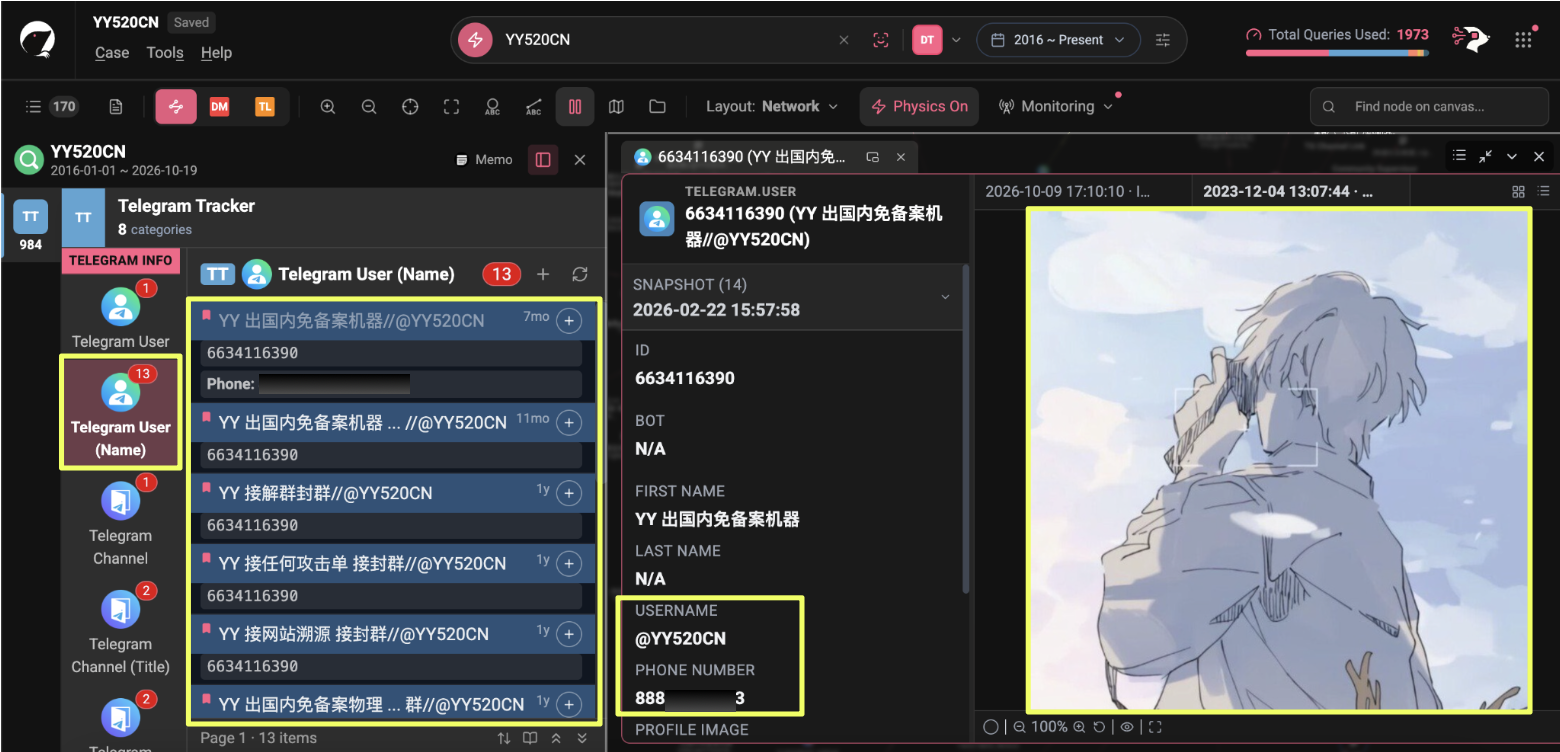
The number falls within the +888 range associated with anonymous Telegram numbers available through Fragment. It did not provide a direct link to a conventional mobile subscriber or establish the account owner's real-world identity. However, it offered another detail to document in the account profile: the number was consistent with the use of an anonymous Telegram identity rather than a conventional carrier-issued number.
Fourteen Names, One Account
The account’s name history offered a clearer picture of how YY520CN’s activities changed over time. StealthMole’s Telegram Tracker recorded 14 different display names between March 2024 and October 2026, while the username remained @YY520CN, apart from one brief appearance in lowercase. The display name, however, changed repeatedly, and each change revealed something about the services being advertised.
First Recorded | Display Name | What It Advertised |
Early Stage & Plain Names (2024 - Mid 2025) | ||
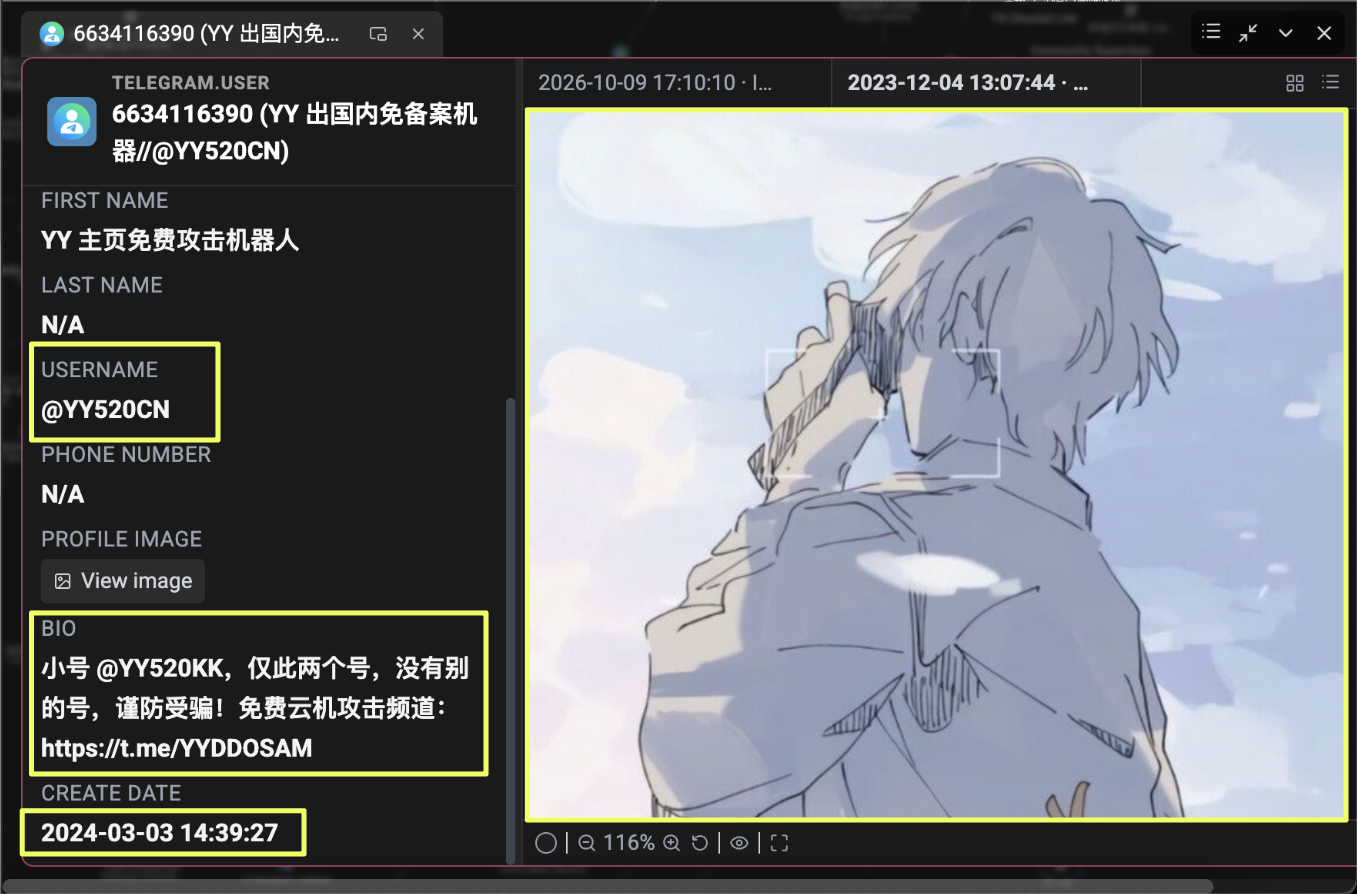
2024-03-03 | YY 主页免费攻击机器人 | Free attack bot on his profile page |
2024-10-19 | YY (@yy520cn) | Plain name |
2025-04-22 | YY | Plain name |
Attack & Account Operations (Mid 2025) | ||
2025-06-13 | YY(接 封群聊 频道 个人号) | Getting group chats, channels and personal accounts banned |
2025-06-14 | YY(接 封群聊 频道) | Same, shortened |
2025-06-17 | YY(接 封群聊 频道 个人账号) | Same, reworded |
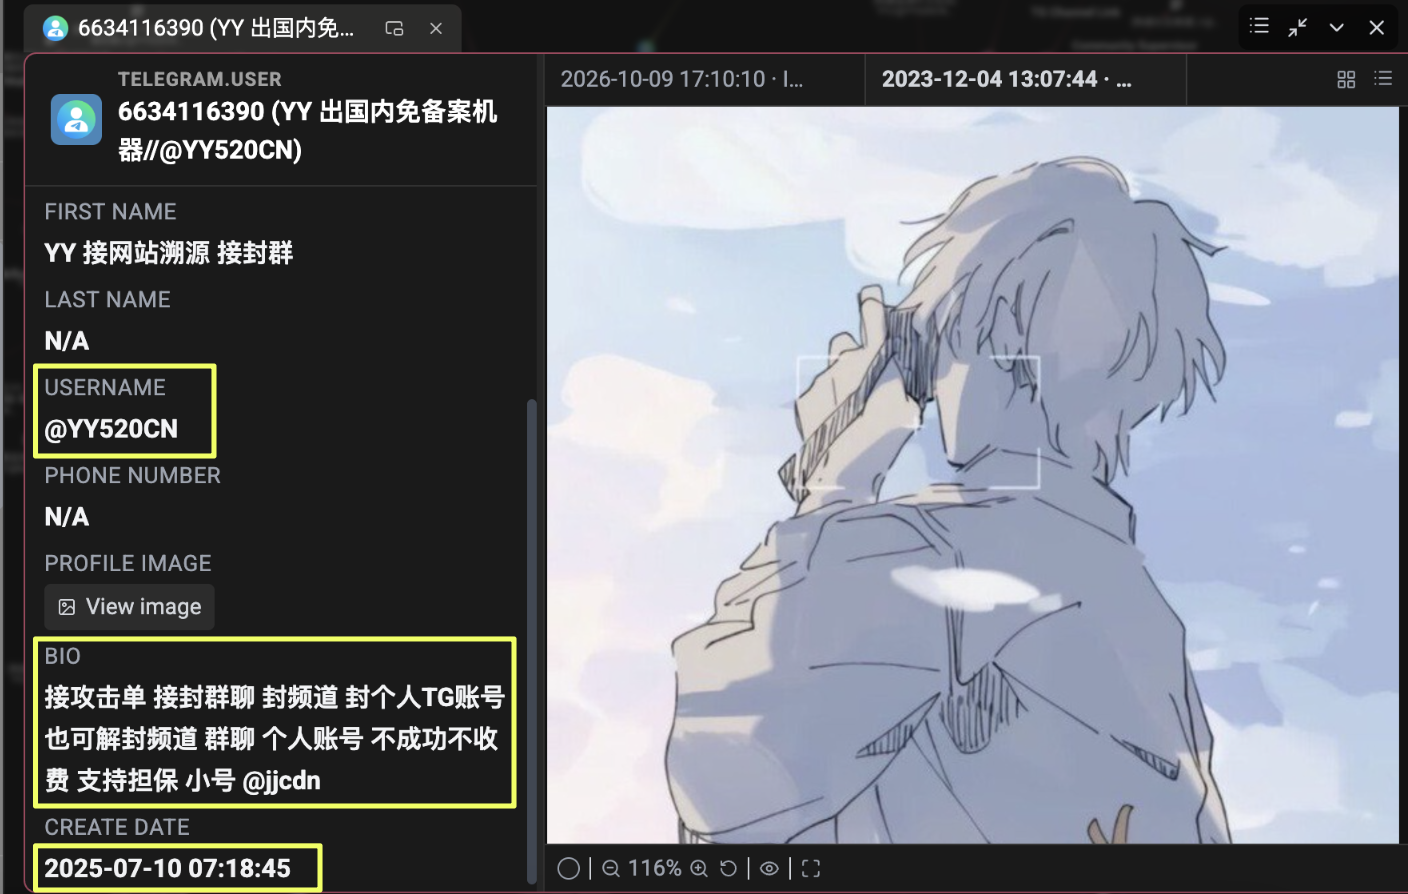
2025-06-30 | YY 接各种攻击单 接封群 | Taking all kinds of attack orders; group bans |
2025-07-08 | YY 出国内免备案物理机 接封群 | Selling mainland China physical servers without ICP filing; group bans |
2025-07-17 | YY 接网站溯源 接封群 | Website origin tracing; group bans |
2025-07-29 | YY 接任何攻击单 接封群 | Taking any attack order; group bans |
2025-09-28 | YY 接解群封群 | Unbanning and banning groups |
Infrastructure Shift & Erasure (Late 2025 - 2026) | ||
2025-11-11 | YY 出国内免备案机器 CDN | Unfiled mainland servers and CDN |
2026-02-22 | YY 出国内免备案机器 | Unfiled mainland servers |
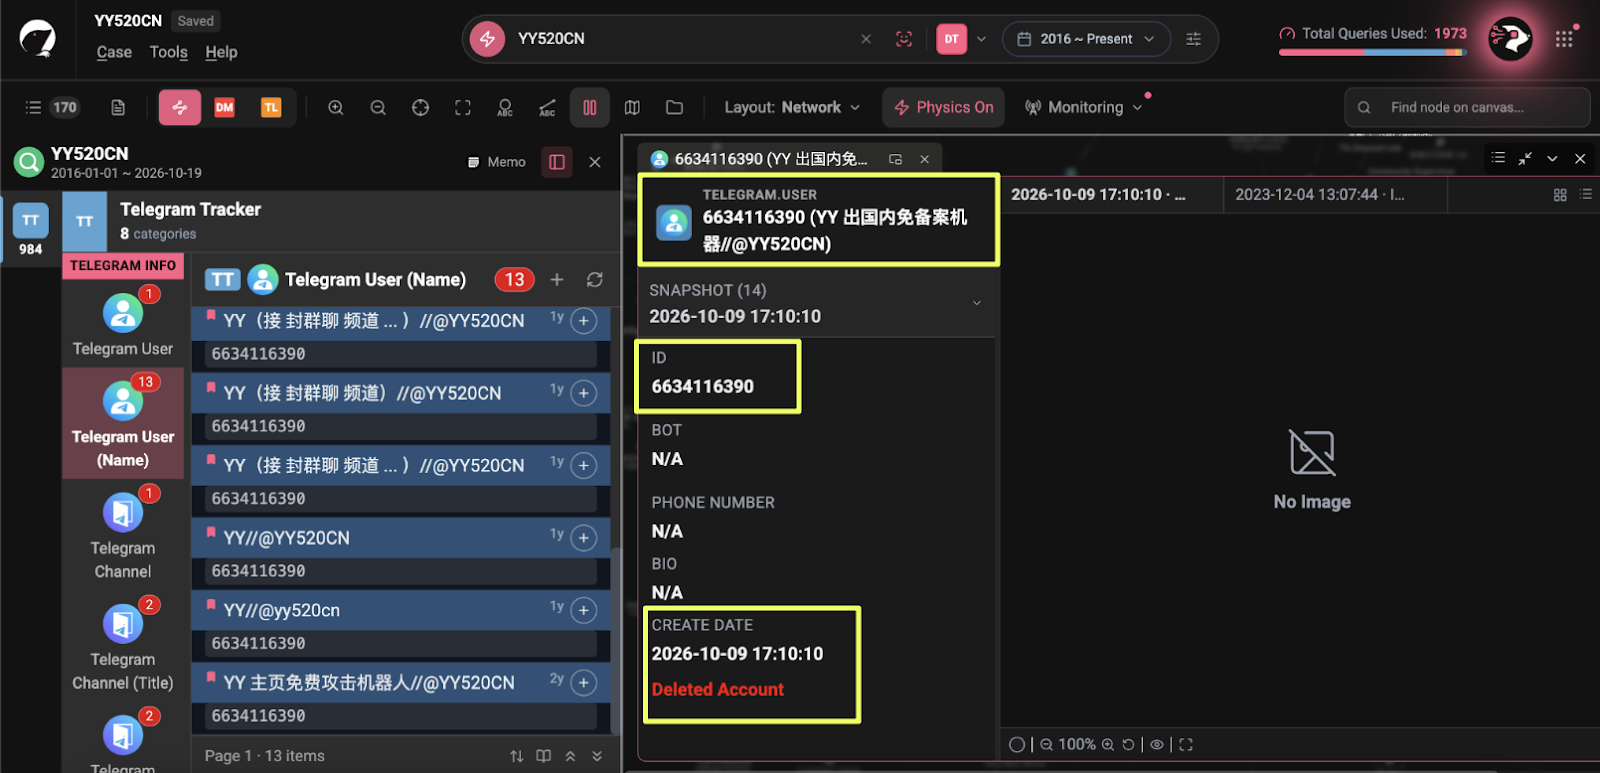
2026-10-11 | (blank) | Nothing |
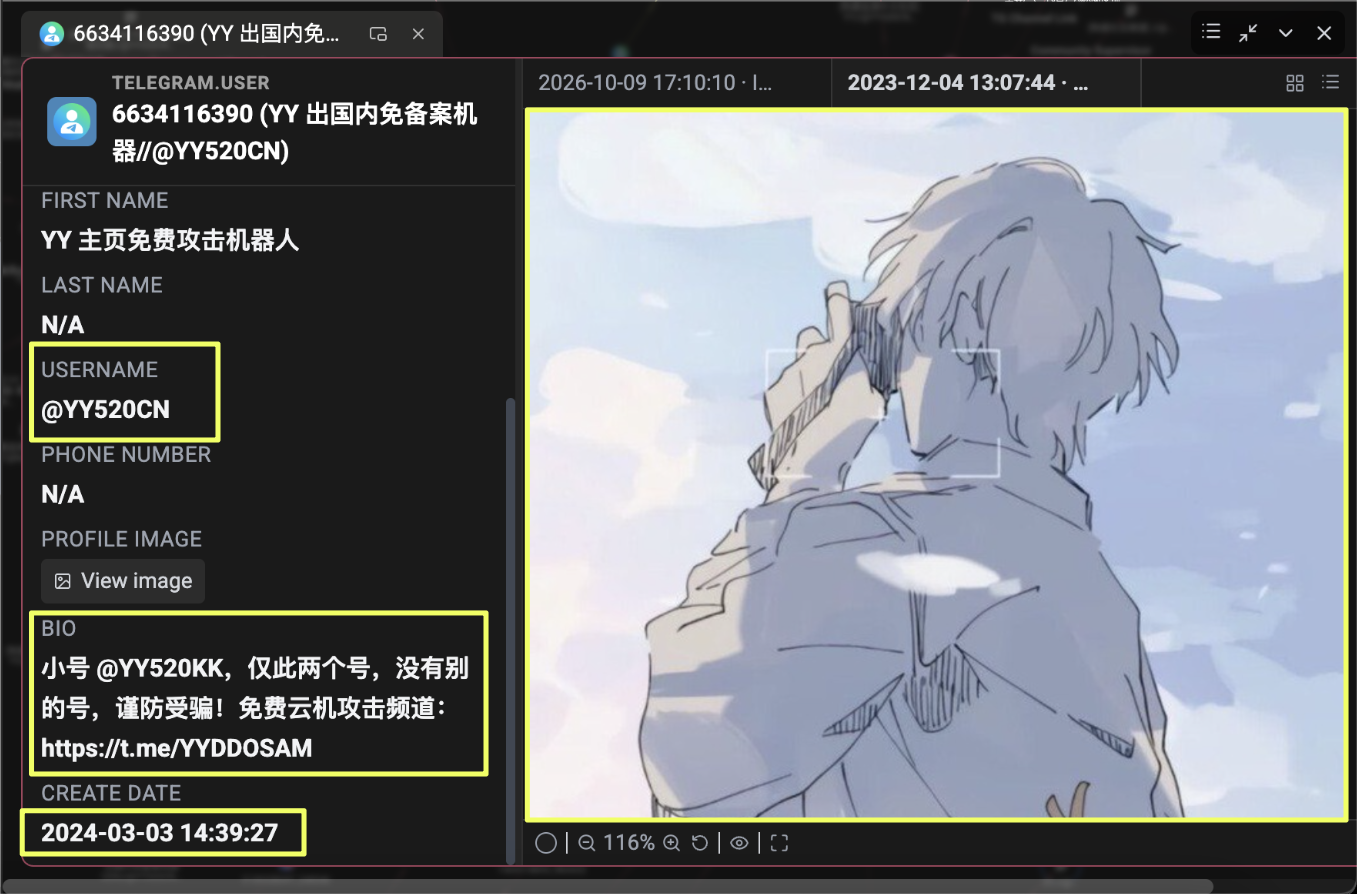
The sequence shows a shift in how the account presented itself. The earliest recorded name from March 2024 advertised a free attack bot. By June 2025, the account was promoting attack orders and services aimed at getting Telegram groups, channels and personal accounts banned. Website origin tracing also appeared in the name history. Later, the focus moved toward servers and CDN services, with the account advertising mainland Chinese infrastructure that did not require ICP filing.
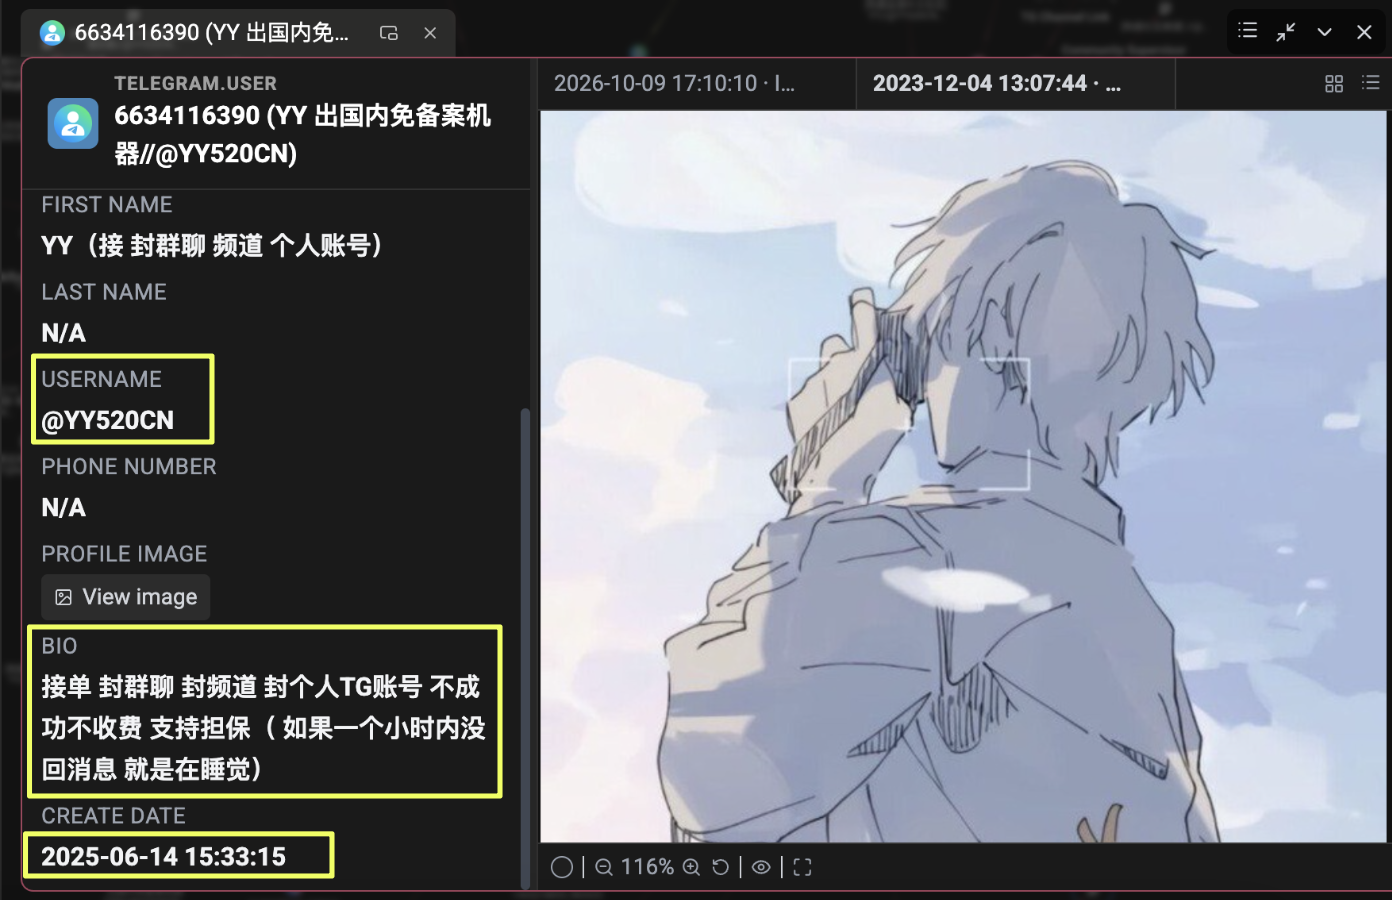
The frequency of these changes is also worth noting. Between June and July 2025, the account repeatedly adjusted its display name while continuing to advertise overlapping services. The records establish that the names changed; they do not, by themselves, explain whether this was a deliberate marketing strategy or a response to other developments.
The final recorded change is more striking. On 09 October 2026, the display name was blank. That entry came shortly after the actor attracted wider attention through public security reporting. The timing makes it relevant to the investigation, although the name history alone cannot establish why it was removed.
Related accounts and a possible secondary identity
The earliest reference to a free attack bot also surfaced two additional identifiers, however, neither of them produced additional indexed activity in StealthMole.
- Account: @YY520KK
- Channel: https://t.me/YYDDOSAM
A more useful lead emerged from the account’s activity in July 2025. On 7 July, while using the display name YY 出国内免备案物理机 接封群, the account posted in the 狗盾社区 group, tagged @jjcdn and asked it to look at “my new username”.
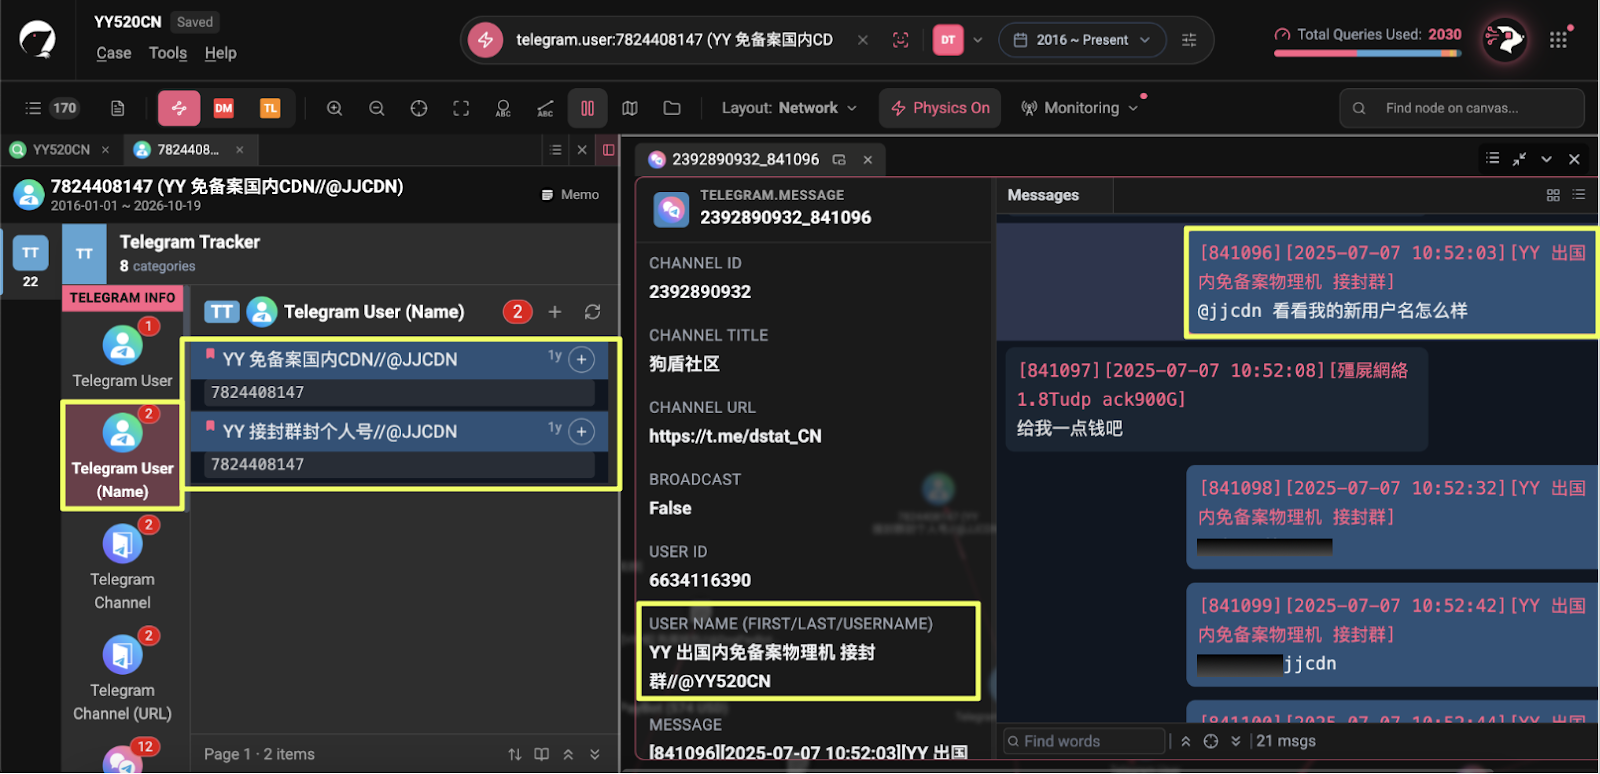
Searching for jjcdn in Telegram Tracker returned another account:
- Username: @JJCDN
- Telegram User ID: 7824408147
- Recorded names: YY 接封群封个人号 (July 2025) and YY 免备案国内CDN (August 2025)
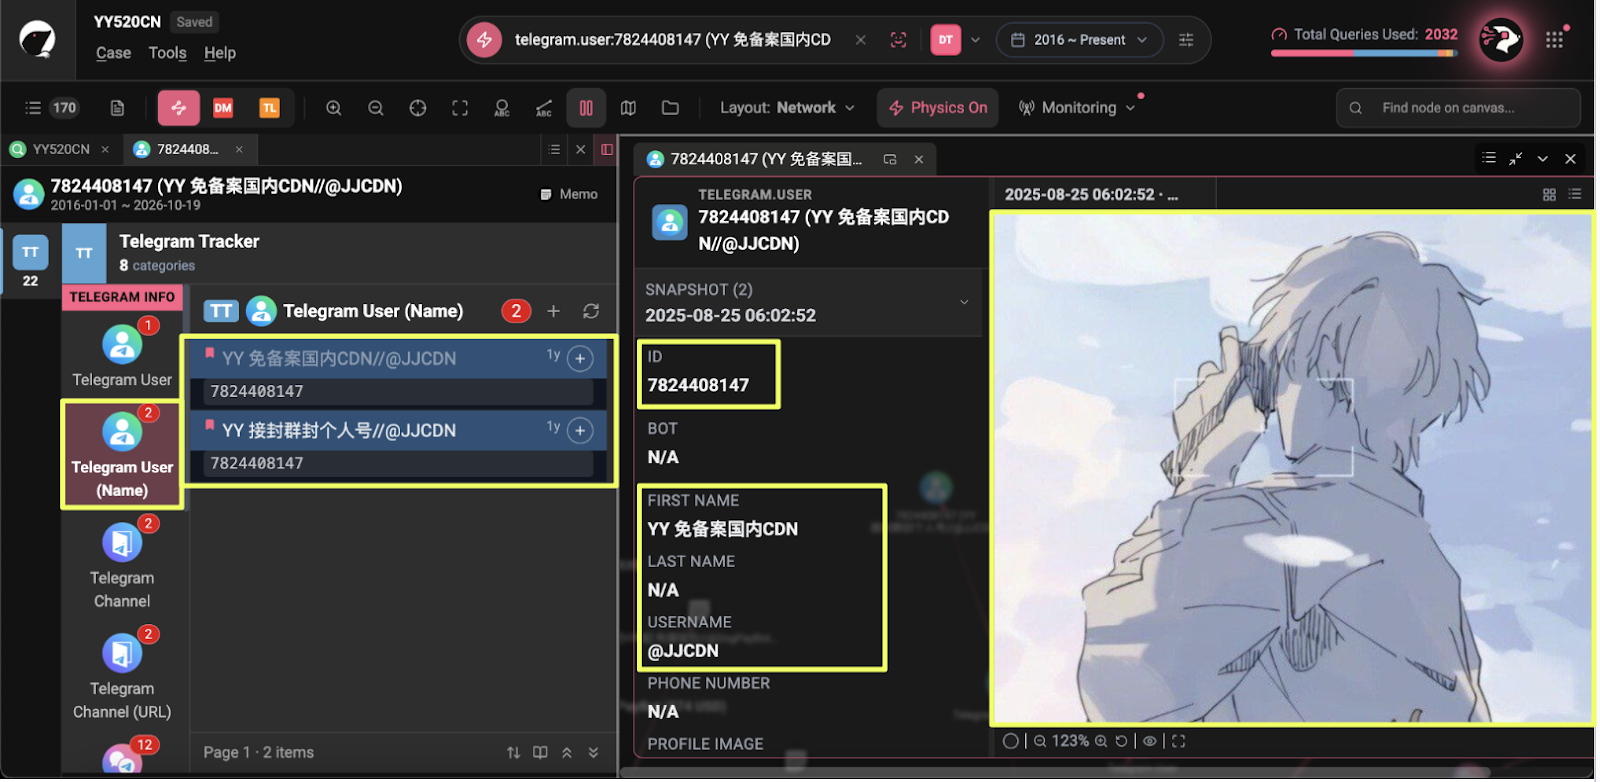
Both recorded names use the YY prefix, same profile picture as the YY520CN account and advertise services that overlap with those promoted by the main account during the same period. Combined with YY520CN’s message about a new username, this makes @JJCDN a plausible secondary account linked to the same operator, potentially used to test or reserve another identity.
A Trusted Face in the Dog Shield Community
The Telegram records placed YY520CN at the centre of a Chinese-language community known as 狗盾 (Dog Shield). The group brought together users involved in DDoS monitoring, stresser services and peer-to-peer trading. StealthMole had indexed the community under several group IDs and titles, all sharing the same public link:
- Public link: https://t.me/d*****t_CN
- 狗盾监测中文社区: 1162438521, 2392890932
- 狗盾社区: 2754044669
- 狗盾社区(重生版): 3180174047
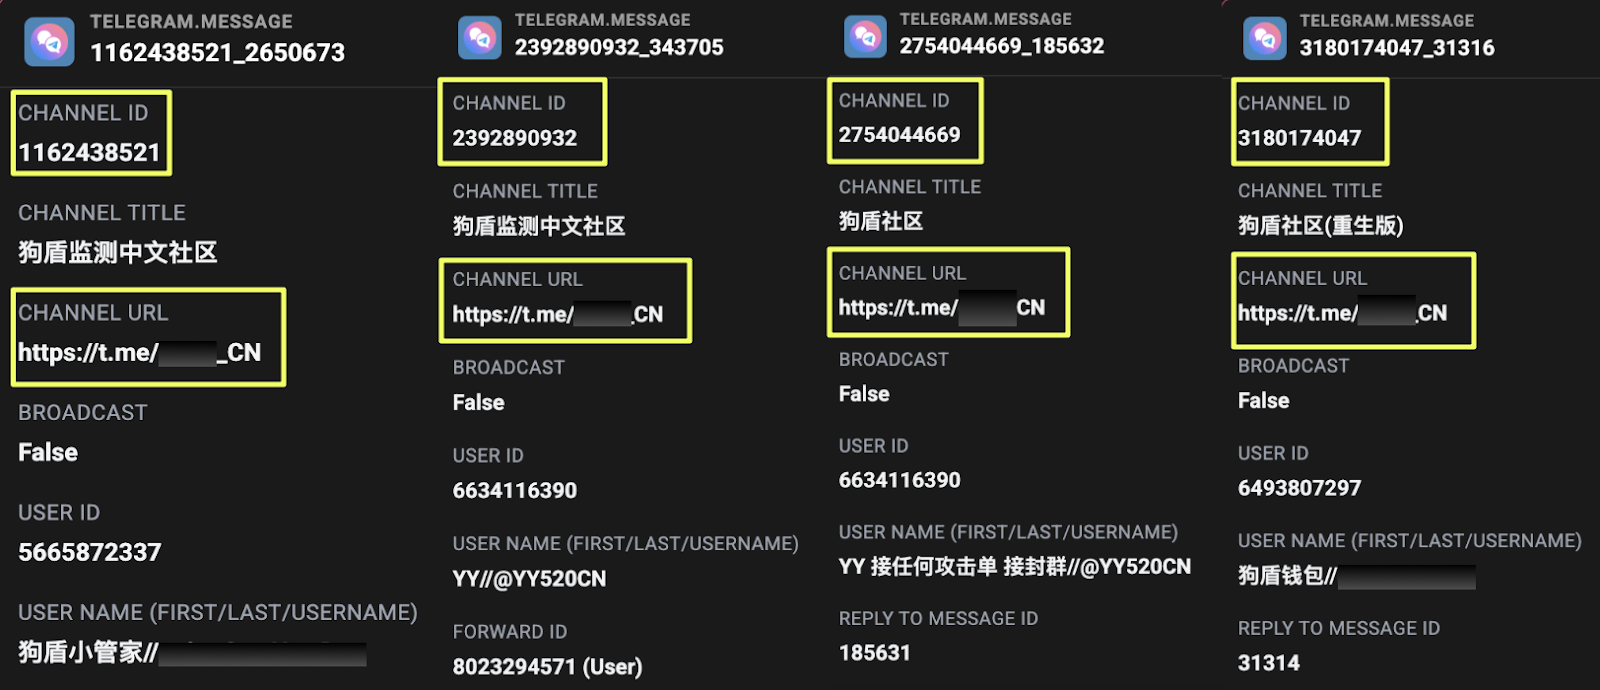
The different group IDs and titles point to multiple iterations of the same community. They suggest that Dog Shield was rebuilt or re-established over time, although the available records do not establish why each version appeared or what happened to its predecessor.
From participant to administrator
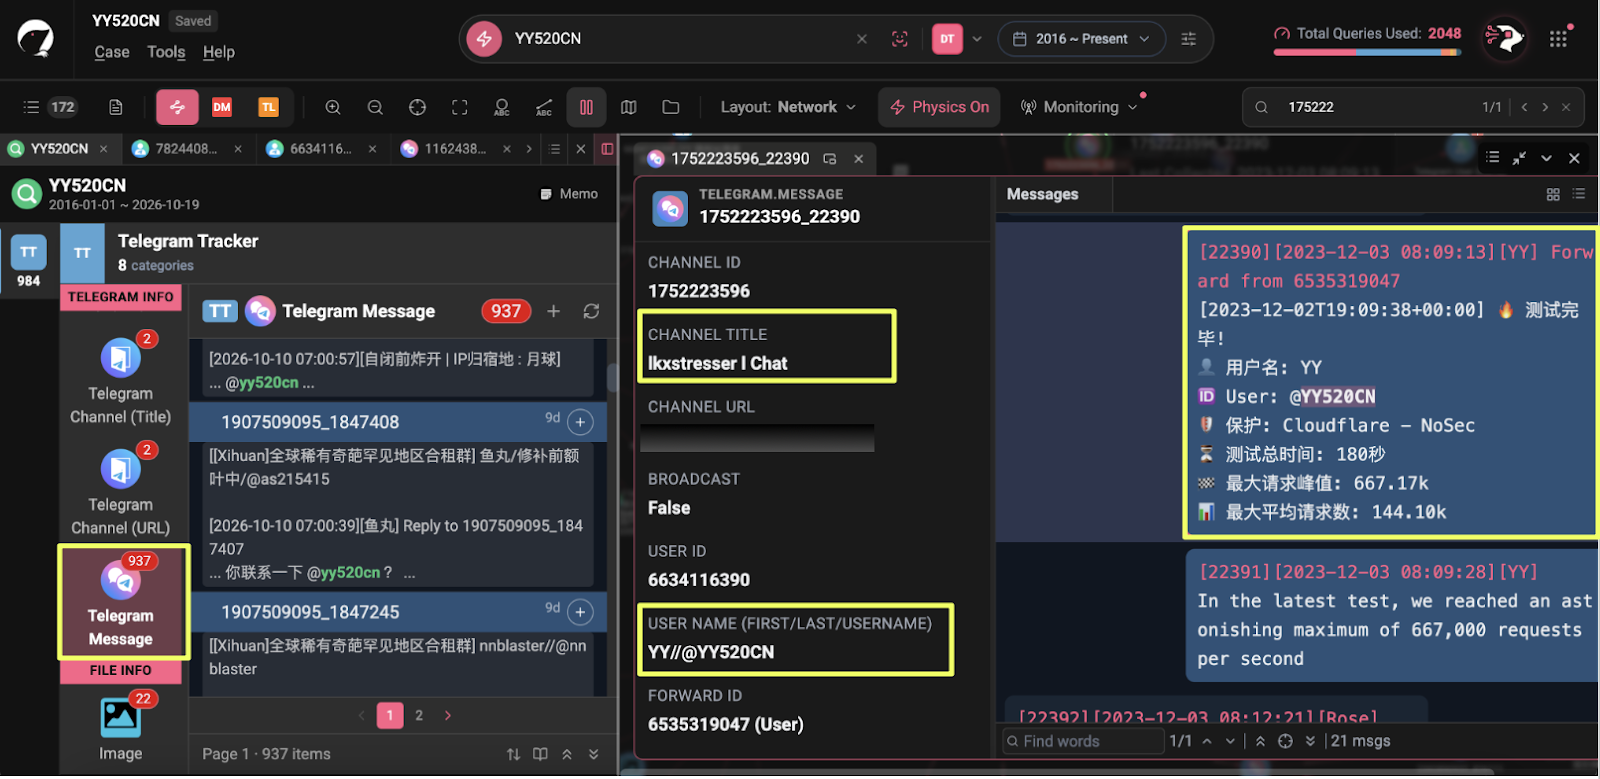
YY520CN’s activity in this ecosystem predates the services advertised in his later display names. On 3 December 2023, he forwarded a stress-test result into the lkxstresser chat. The bot output identified him as the tester, recorded a target protected by Cloudflare and reported a peak of 667.17k requests over 180 seconds. This placed the account in the Layer 7 attack scene well before the account’s later promotional activity.
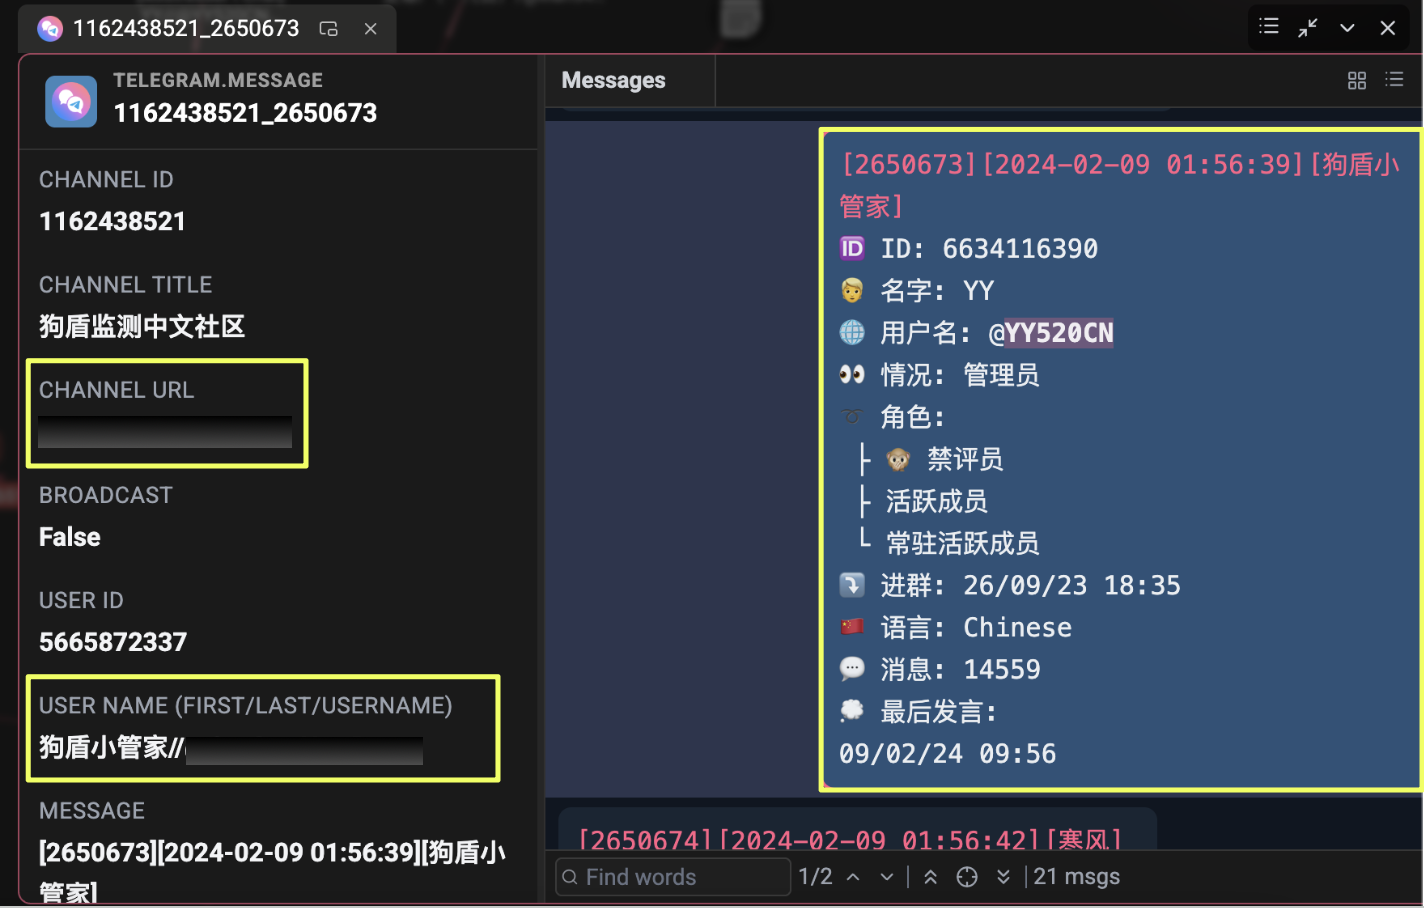
By February 2024, YY520CN had taken on a more prominent role within Dog Shield. On 9 February, the community management bot, 狗盾小管家, listed Telegram user ID 6634116390 as an administrator, with moderator and long-standing active-member roles.
The community’s own announcement channel provided further confirmation of his position. On 29 February 2024, it published the staff structure, listing YY520CN among the supervisors:
- Official lead: 寒风 (@han*****8)
- Manager: Bbig (@Bb****o)
- Supervisors: Aerith (@a******cy), 青海 (@vi*****ng), YY (@YY520CN)
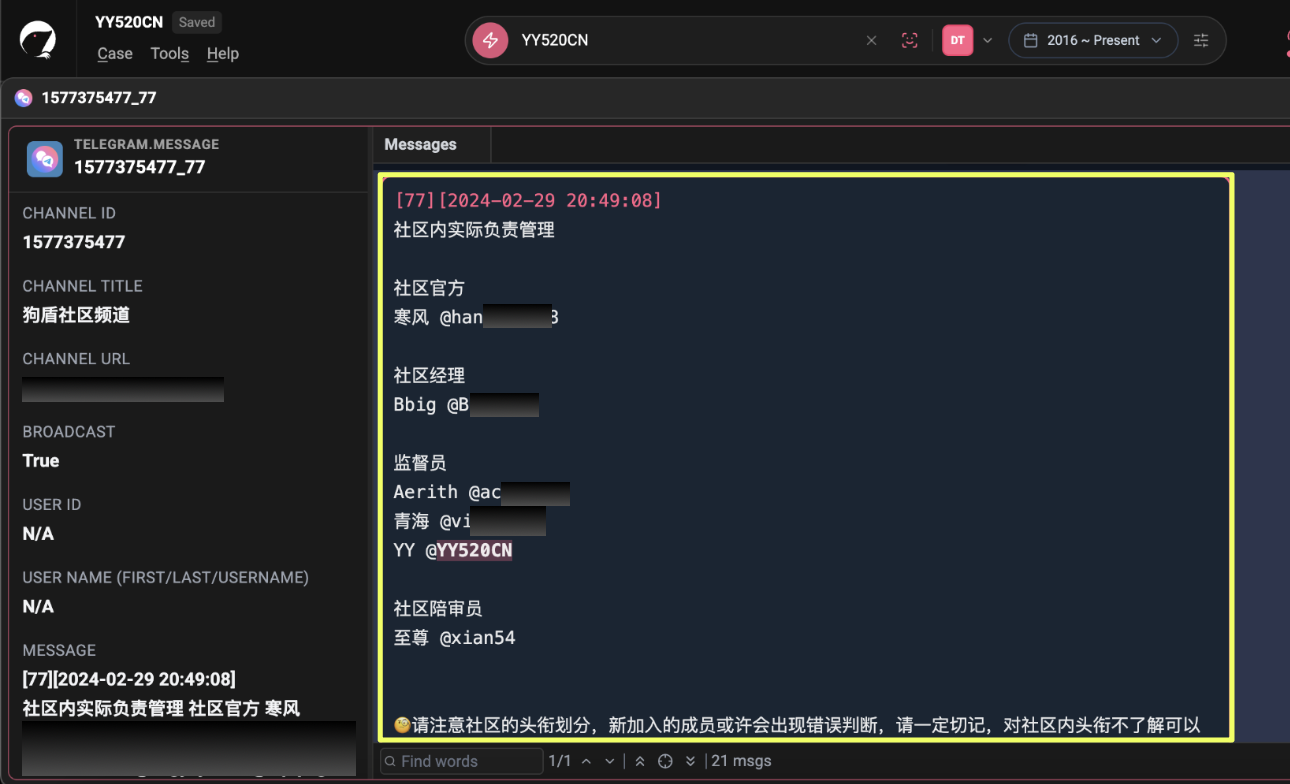
These records establish that YY520CN was more than a regular participant. He held a recognised position within the community, placing him among the people responsible for its day-to-day management. That role is particularly relevant given the community’s use of an internal escrow wallet to settle trades, where trust in the people overseeing transactions would have mattered.
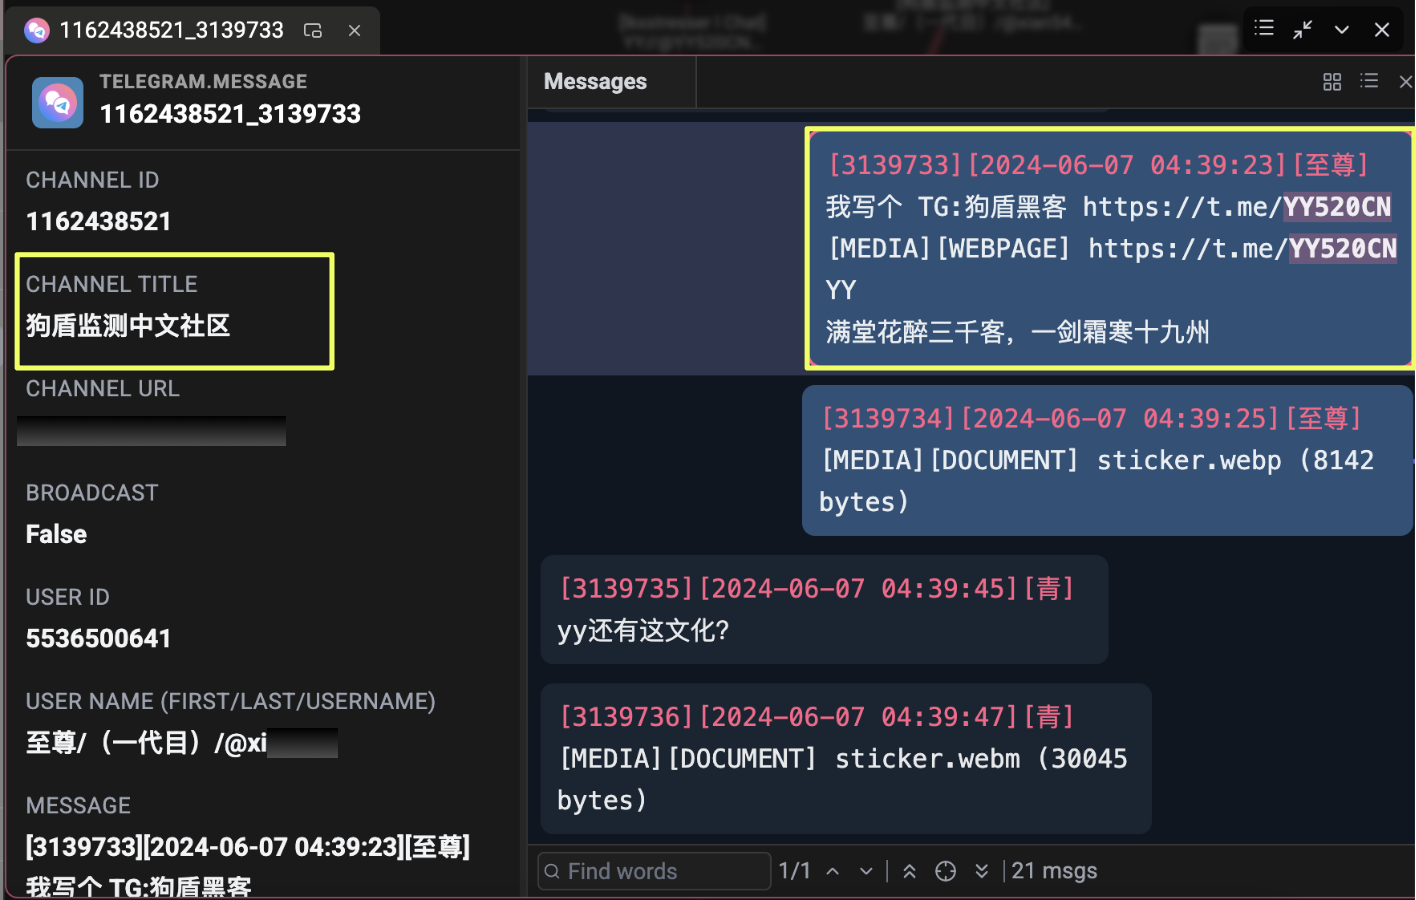
Other members also appeared to recognise his standing. In June 2024, community juror 至尊 (@xi*******4) referred to him as 狗盾黑客, or “Dog Shield hacker”, while sharing his Telegram link. The label is evidence of how another member described him, rather than independent confirmation of his technical capabilities.
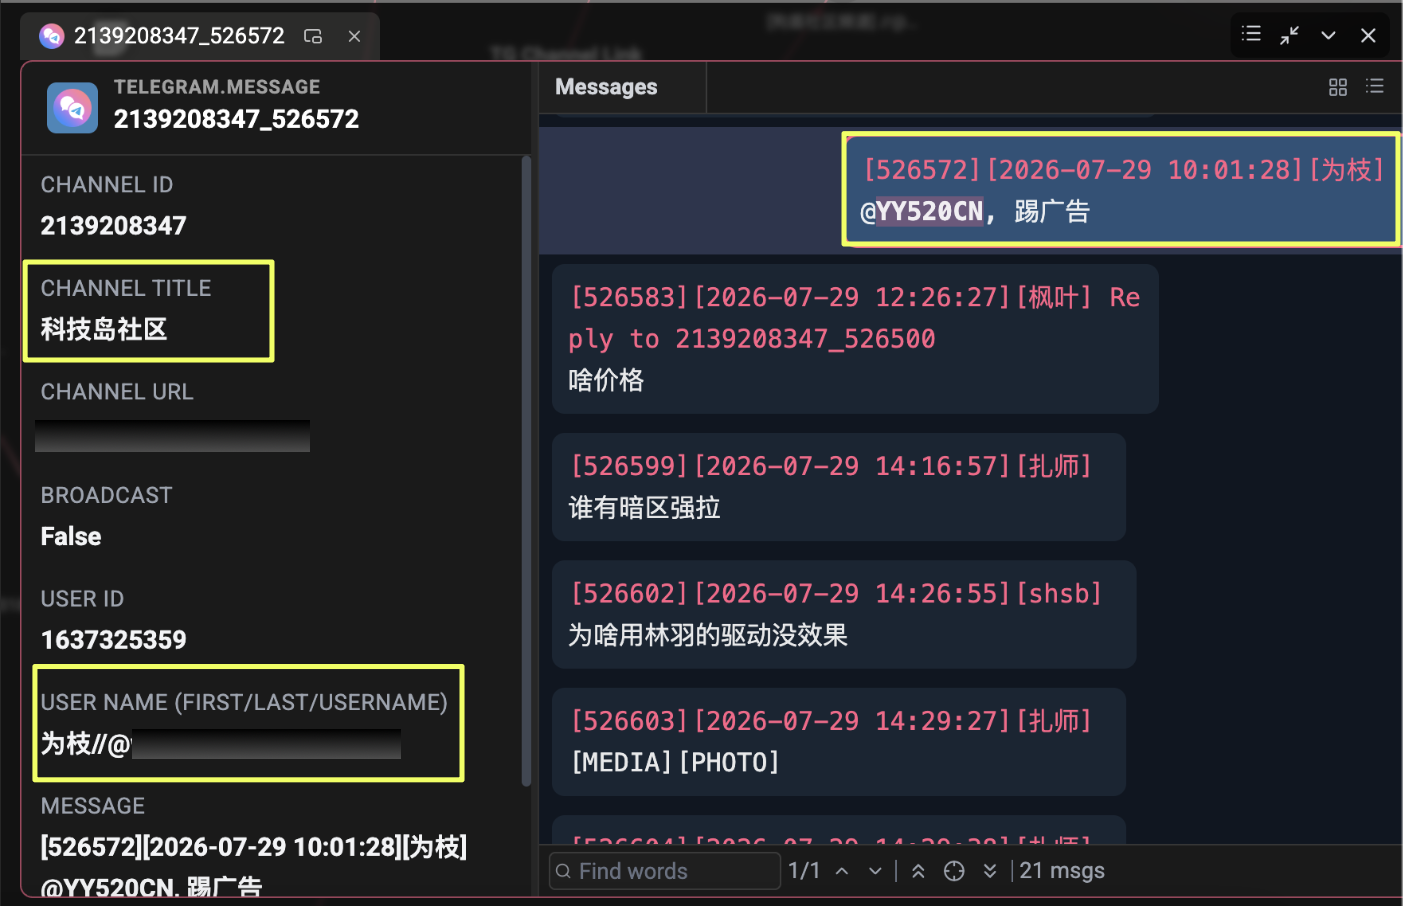
His administrative presence extended beyond Dog Shield. In July 2025, YY520CN pinned his own service post in 黑客素质广场. A year later, in July 2026, a member of 科技岛社区 asked @YY520CN to remove an advertiser. These interactions are consistent with an account that other members approached for moderation-related actions, although the records alone do not establish the precise permissions he held in each group.
A financial footprint dating back to 2024
The community records also revealed an earlier financial loss associated with YY520CN. On 21 January 2024, 寒风 published the final compensation figures for customers affected by losses involving @fei*****fu, an intermediary through which community members had lost funds.
YY520CN was listed as the largest individual claimant:
- Reported loss: 1,233 USDT
- Share of the total reported losses: 85.1%
- Compensation received: 590.95 USDT
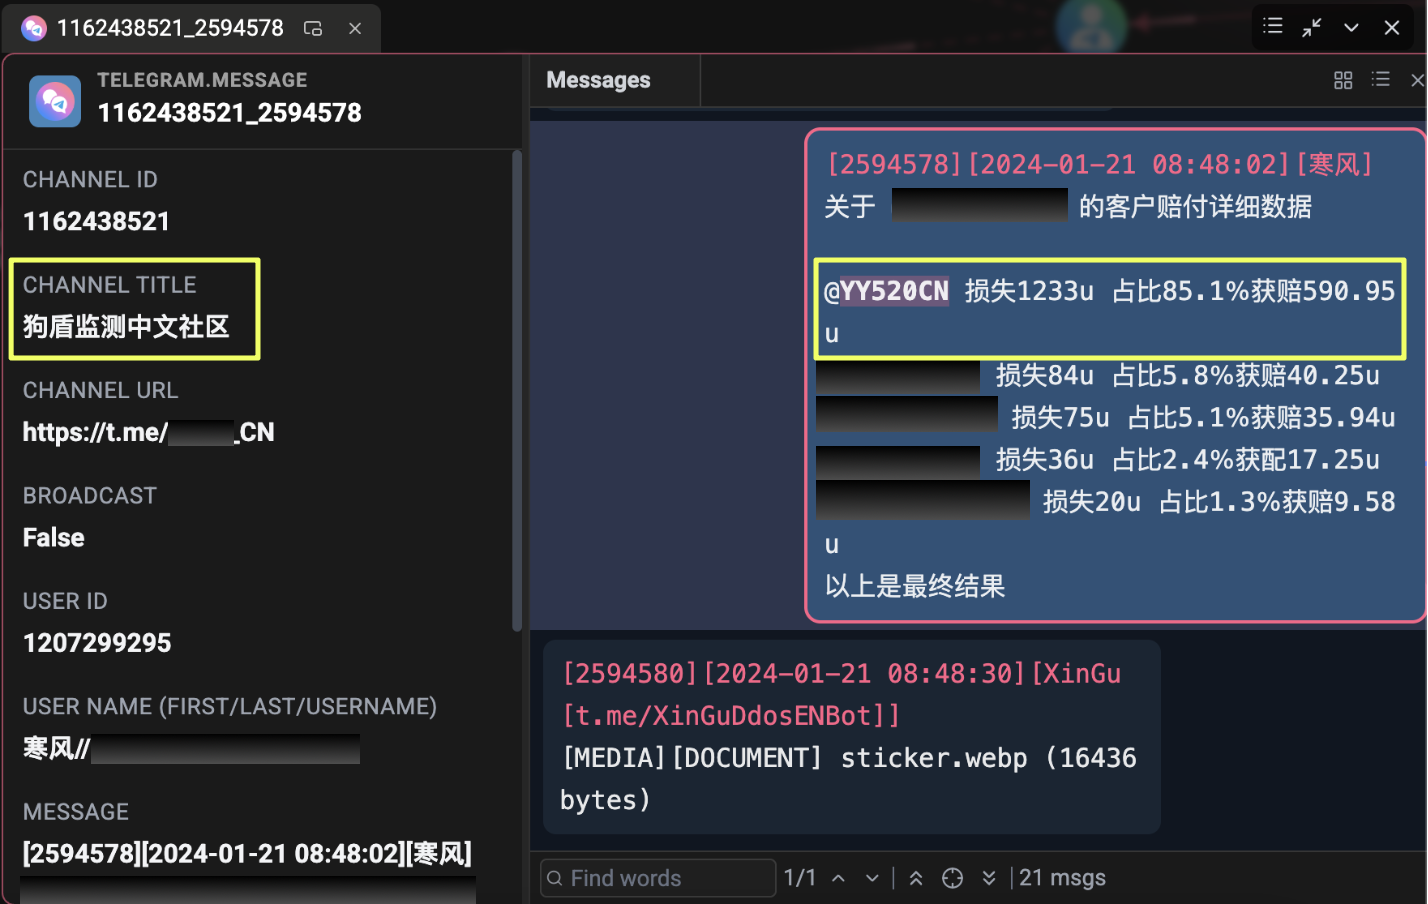
The next-largest claimant had reported a loss of 84 USDT. The difference was substantial, placing YY520CN well above the other listed customers in terms of the amount lost.
The figures establish the scale of his reported exposure to that intermediary, but they do not explain the underlying transactions or establish what services he had been using it for. They do, however, show that YY520CN was involved in financial activity within the community long before his later infrastructure and attack-service advertisements became prominent.
Together, the records show an account with a history of participation, administrative responsibilities and financial dealings within Dog Shield. This background helps explain why YY520CN's activity cannot be understood through his later service advertisements alone. By early 2024, he was already a recognised figure within the community, with a position that extended beyond simply selling services to other members.
Business by Escrow
YY520CN’s display-name history showed what he claimed to offer. His advertisements provided a closer look at how those services were sold, how payments were handled and how he tried to build trust with potential customers.
Many of the advertisements were not written separately for each group. StealthMole’s Telegram Tracker traced them back to a common forwarding source:
- Forward source (Telegram channel ID): 2820831557
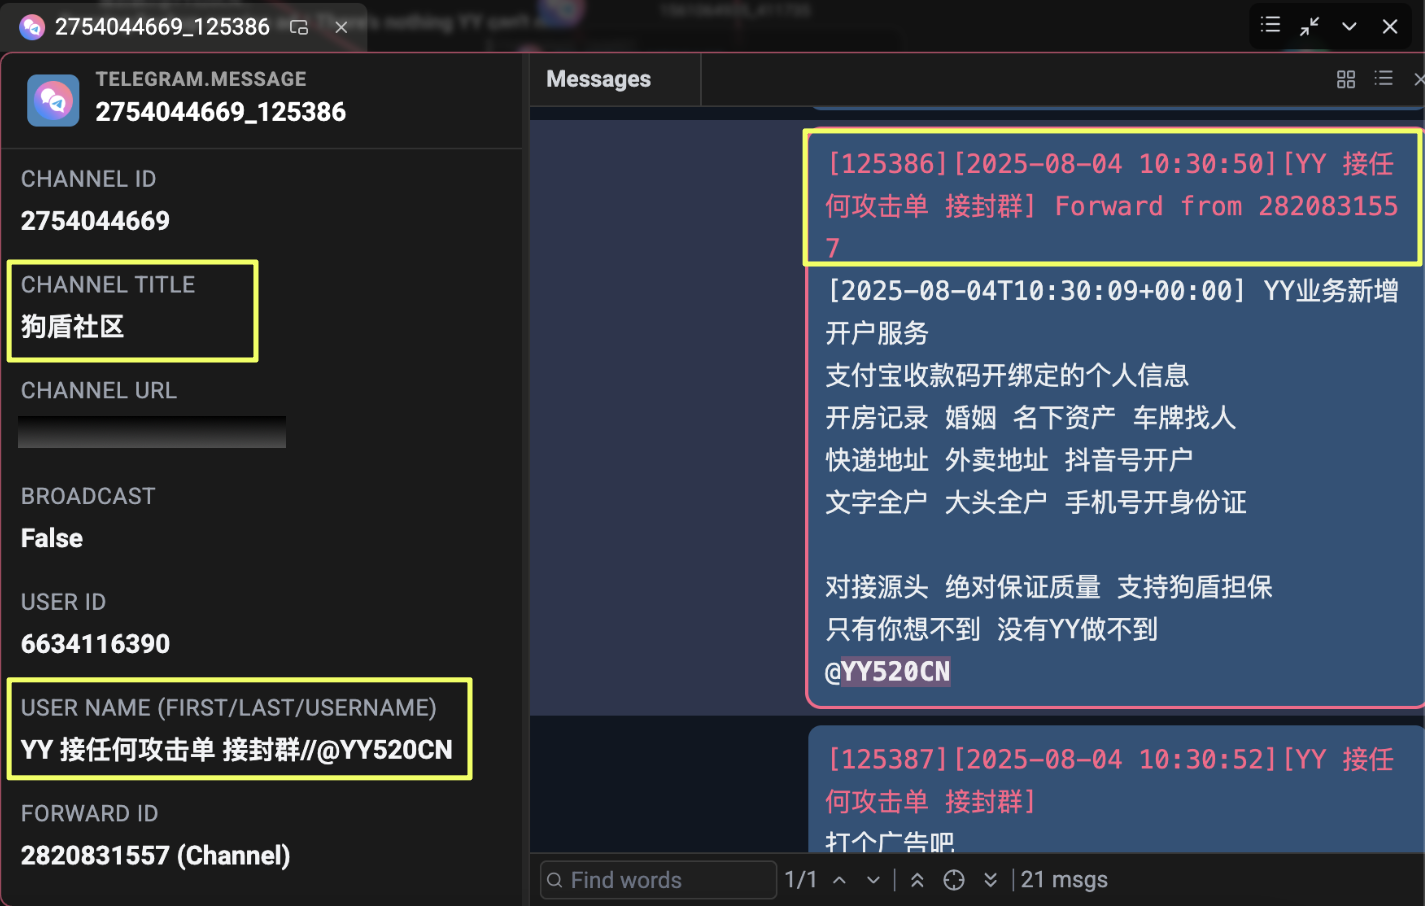
This suggests that YY520CN used a dedicated channel to distribute promotional posts across multiple communities. Two advertisements from July 2025 show how the arrangement worked.
Selling attack services through DogPay
On 5 July 2025, YY520CN posted an offer in 黑客素质广场, a Telegram group. He advertised website origin tracing, with particular emphasis on sites protected by Cloudflare, alongside attacks against applications protected by anti-DDoS services. He described the method as exclusive and directed interested customers to contact @YY520CN.
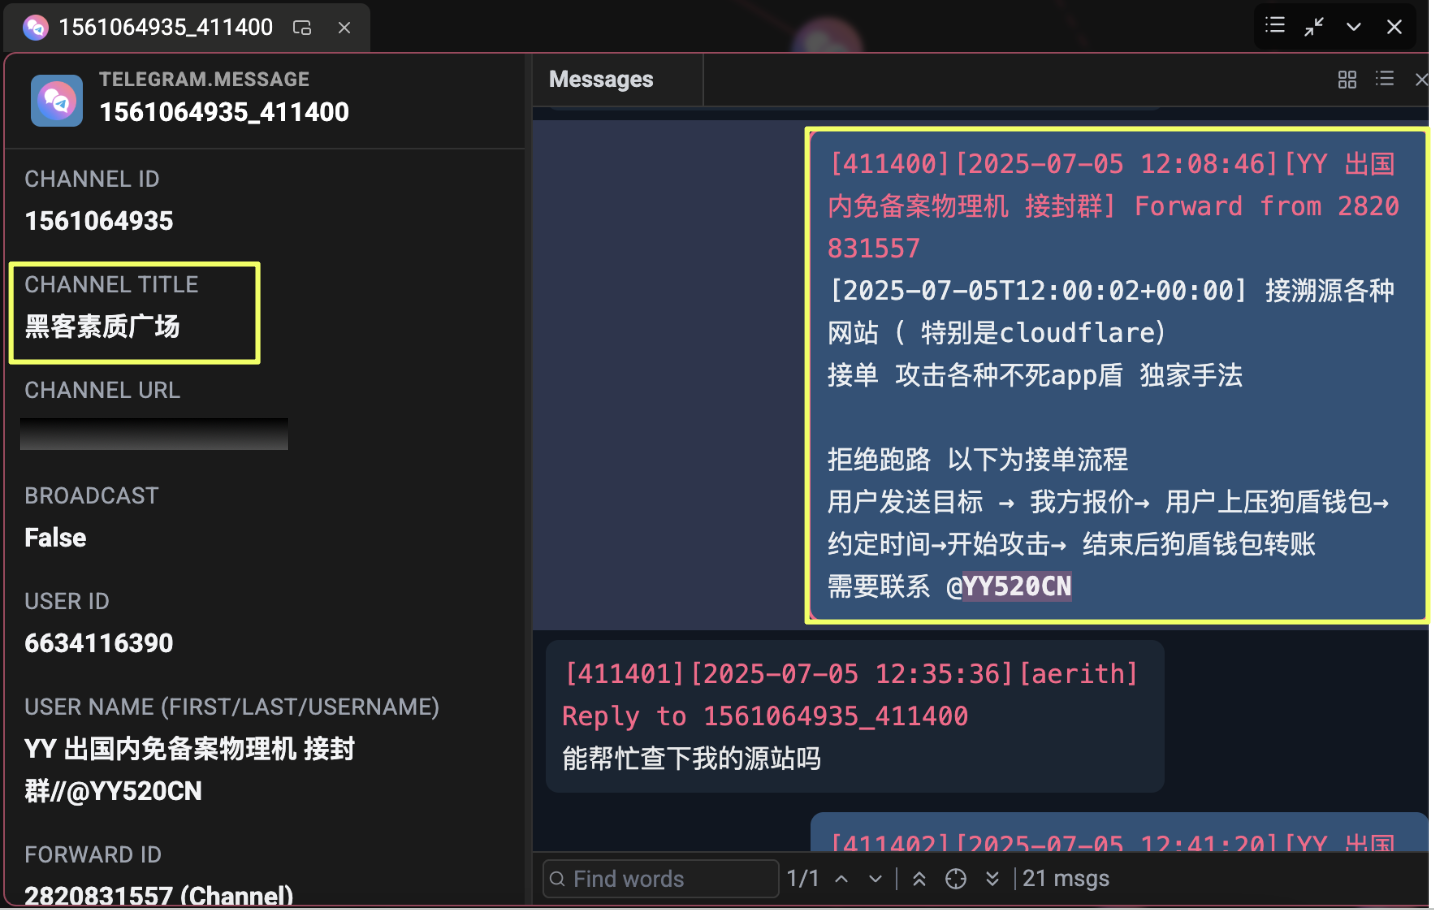
The post identified 狗盾钱包 (DogPay) as the escrow service and laid out the payment process. Customers submitted a target, received a price quote, deposited the agreed amount into escrow and arranged an attack time. Payment was released once the operation was complete. The advertisement also included an assurance that he would not disappear with customers’ money.
Five days later, on 10 July 2025, he promoted the origin-tracing service separately. The payment process remained the same, but the advertisement made the intended outcome explicit: once the origin IP was identified, it would be attacked directly. The post stated that if the IP went down, the website would go down with it.
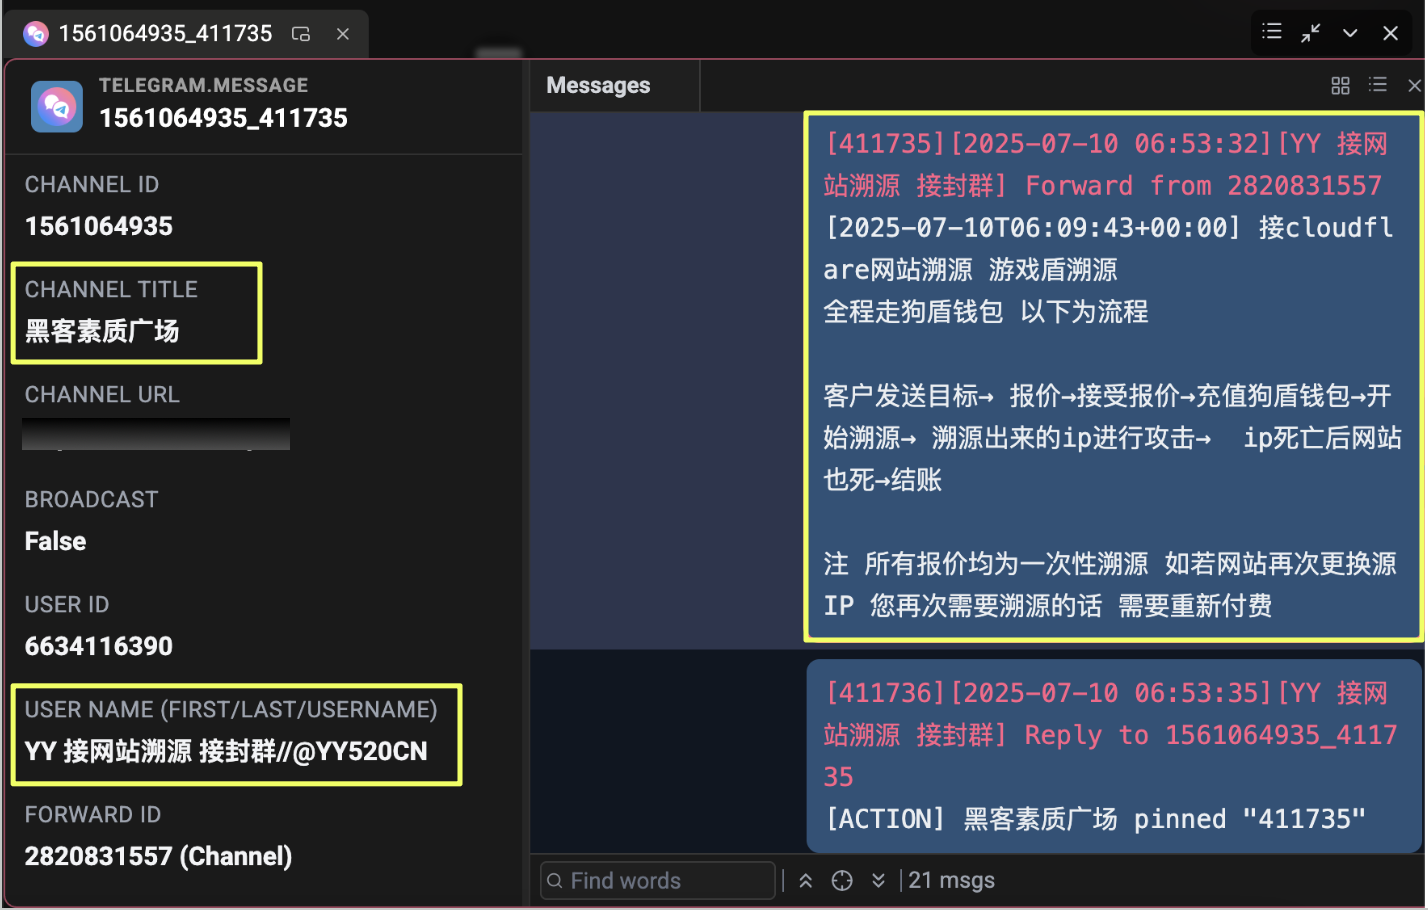
The service was priced per tracing job. If a website moved to a new origin IP, the customer would have to pay again. YY520CN also pinned the advertisement in the group, giving it continued visibility.
These posts reveal the relationship between the service being sold and the payment arrangement supporting it. YY520CN was not simply advertising attacks; he was presenting origin tracing as a separate service with its own pricing and repeat-payment conditions. DogPay provided a structured transaction process, allowing customers to deposit funds before the work began and release them after completion.
The advertisements document what YY520CN promised to deliver. They do not independently establish that every advertised service was technically successful or that every transaction followed the stated process.
Expanding the catalogue
By August 2025, YY520CN was advertising services beyond DDoS attacks and website tracing.
On 4 August, using the display name YY 接任何攻击单 接封群, he promoted personal-information lookup services targeting Chinese individuals. The advertisement claimed access through direct upstream sources and listed several categories of information, including identity details, addresses, household records, property information and account-registration data.
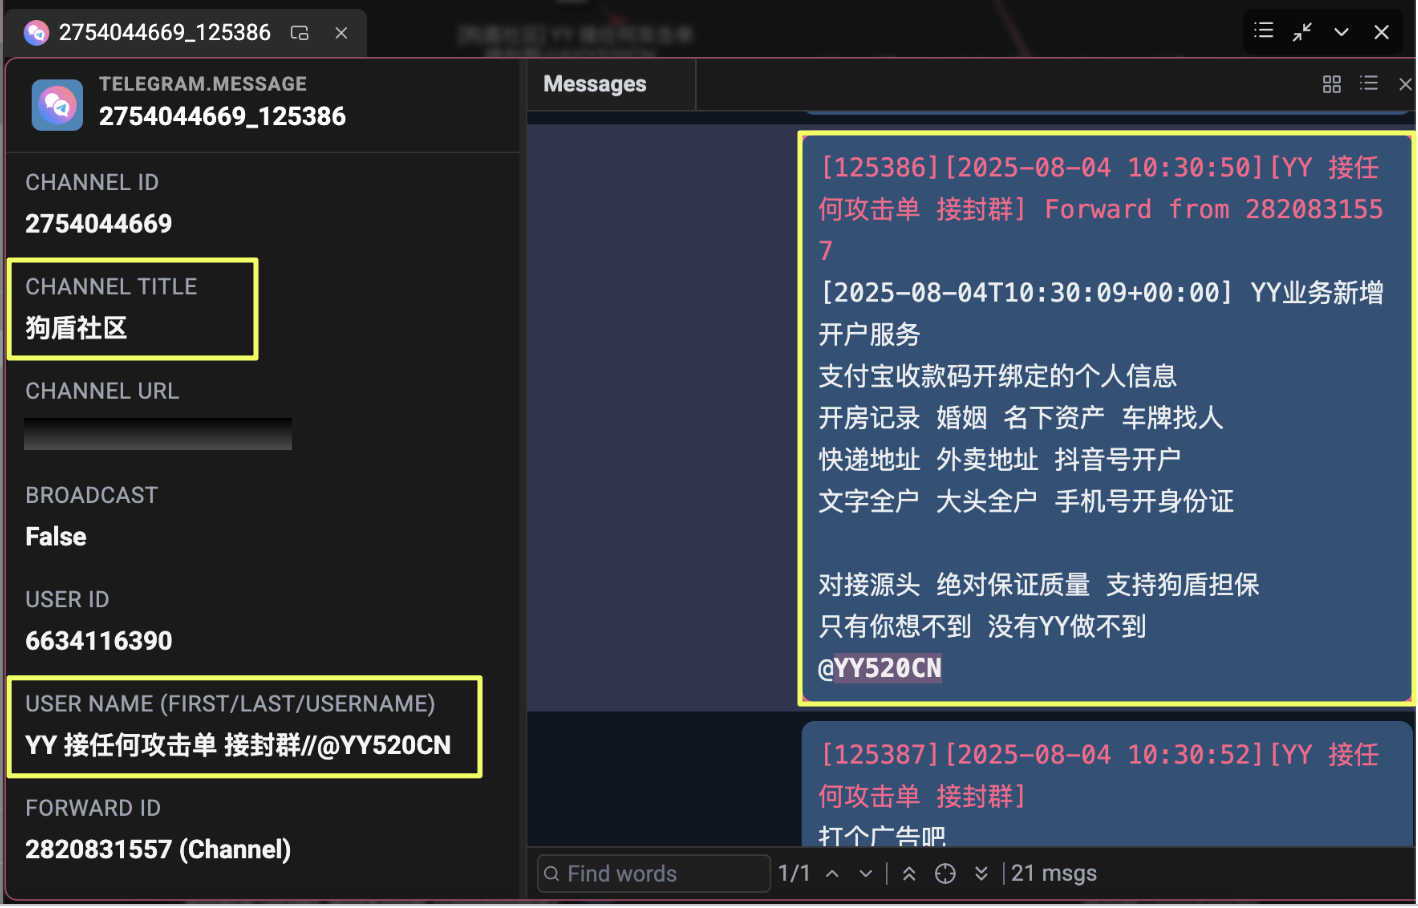
The post repeated the escrow guarantee, maintaining the same emphasis on payment protection used in his earlier advertisements. It ended with a broad claim, “there was nothing YY could not do.” In the same discussion, he remarked that business had become difficult.
The advertisement establishes that he claimed to offer access to personal information across several categories. It does not verify the source, accuracy or legality of the records he claimed to be able to obtain. Nevertheless, the expansion of the advertised catalogue shows that his commercial pitch was no longer limited to attack-related services.
A 2,000.26 USDT payment
Not every escrow-related record involved a straightforward service sale. On 24 August 2025, a payment notice appeared in 狗盾社区 showing 2,000.26 USDT received under YY’s account.
The indexed record identified the following details:
- Payer: @yuji*********nn
- Telegram user ID: 7465381584
- Associated channel: https://t.me/jis*********ye2
- Channel description: Advertised penetration testing, data sales and vulnerability sharing
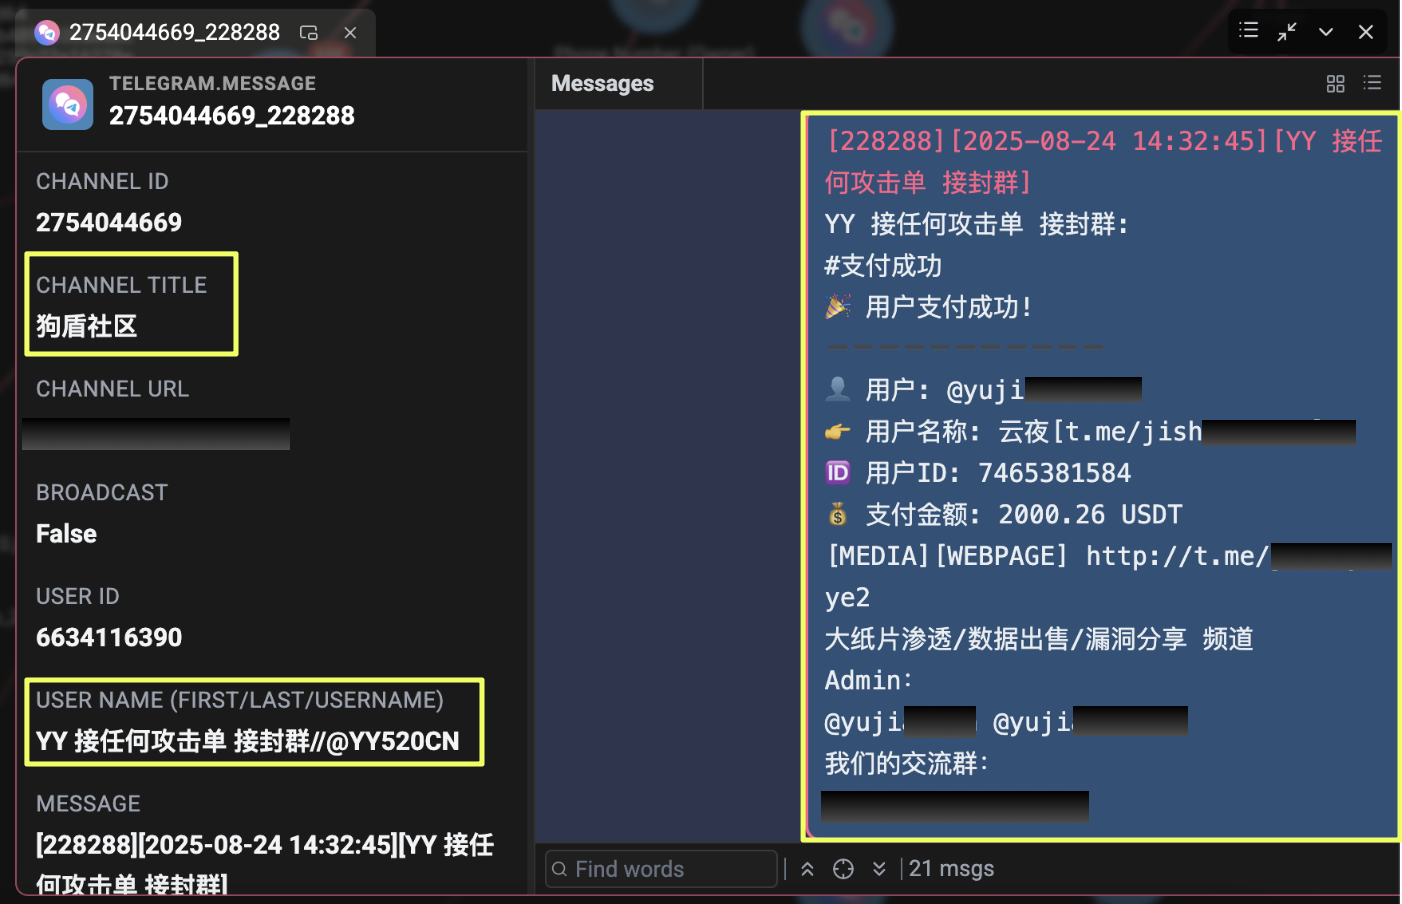
The surrounding messages captured a public dispute over the amount at stake. The other party initially discussed putting up 10,000 USDT before settling on 2,000 USDT, while other group members mocked the lower figure.
The indexed messages do not establish the purpose of the stake or explain the underlying disagreement. The payment notice confirms that 2,000.26 USDT was recorded as received under YY’s account, but it does not, by itself, establish whether the funds represented a completed transaction, a wager, a deposit or another arrangement.
The payer’s advertised channel provides additional context about the circles in which the transaction took place, but it does not establish that every activity promoted there was connected to YY520CN.
Overall, the advertisements and payment record show how YY520CN presented himself commercially: a service provider offering attack-related work, origin tracing and personal-information lookups, with escrow repeatedly used as a means of reassuring customers. The records also show the limits of that picture. While the advertised terms and payment amounts are documented, the precise outcome of individual transactions remains uncertain.
Following the Money
The advertisements showed how YY520CN collected payments through DogPay. The next step was to examine what happened to the money outside the escrow system. Searching the account’s indexed messages revealed a TRON address that YY520CN had shared repeatedly:
- TRON address: TLhgx*****************************4xLz

Between January and July 2025, YY520CN posted this address in community groups on at least five separate days, usually in response to other members. The pattern was consistent with an address he used to receive payments, although the messages alone did not establish the purpose of every transfer.
Searching the address through StealthMole’s Telegram Tracker returned 15 messages. Two provided additional context about its use.
A wallet registered for monitoring
On 30 January 2025, YY520CN forwarded a wallet-monitoring alert into 狗盾监测中文社区. The notification recorded an incoming transfer to the address:
- Amount: +88.88 USDT
- Sending address: TY2uN**********************xVK
- Transfer time: 2025-01-30 12:18:03
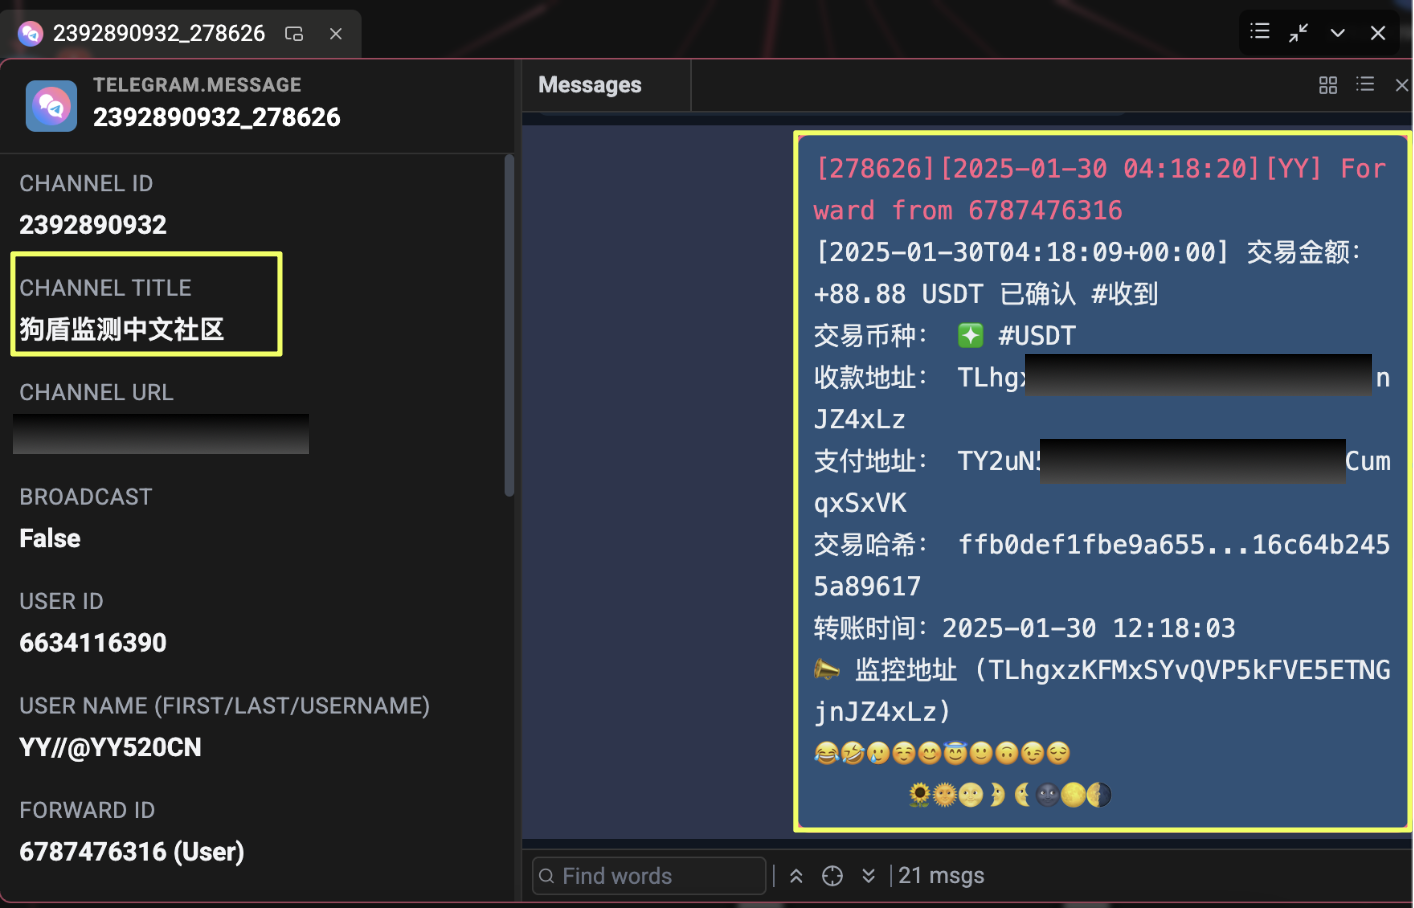
The alert added an important detail to the investigation. Rather than simply appearing in a message as a payment address, the wallet was being monitored through a service that generated transaction notifications.
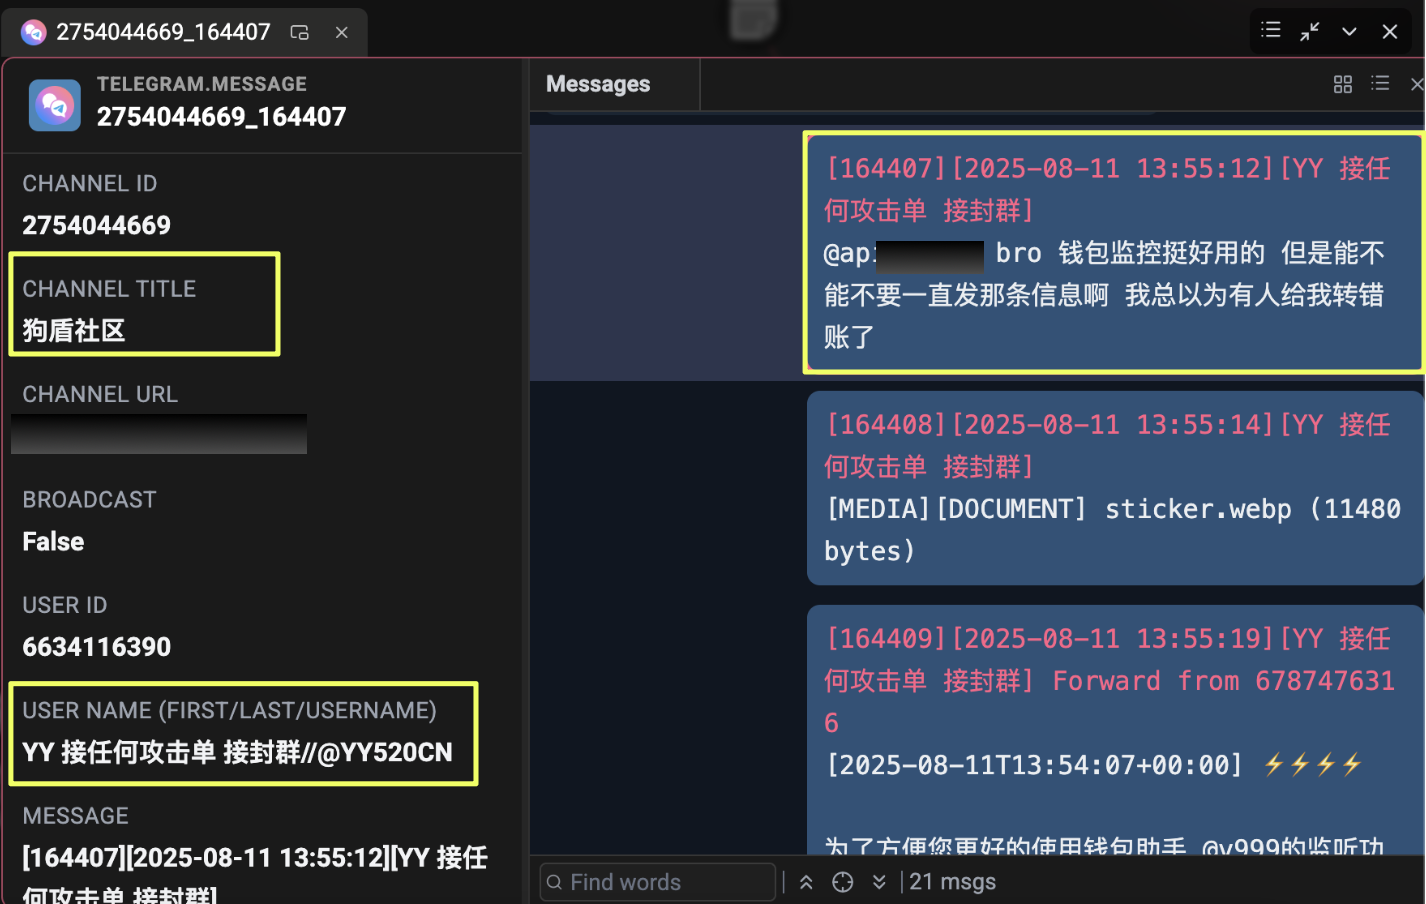
Months later, YY520CN publicly asked @ap**1****8 to stop sending repeated alerts because they kept making him think someone had transferred money to him by mistake. This complaint supports the connection between the account and the monitoring service, although the available messages do not independently establish who registered the address or controlled the wallet.
A second withdrawal request
A separate message from 6 June 2025 raised another question about the address. In a conversation where YY520CN had been replying to other members minutes earlier, someone forwarded a withdrawal request from another platform, specifying the same TRON address as the destination.
The request contained the following details:
- Requesting user: @se****2
- Display name: 冠希
- Telegram user ID: 5578870433
- Requested payout: 88.00 USDT
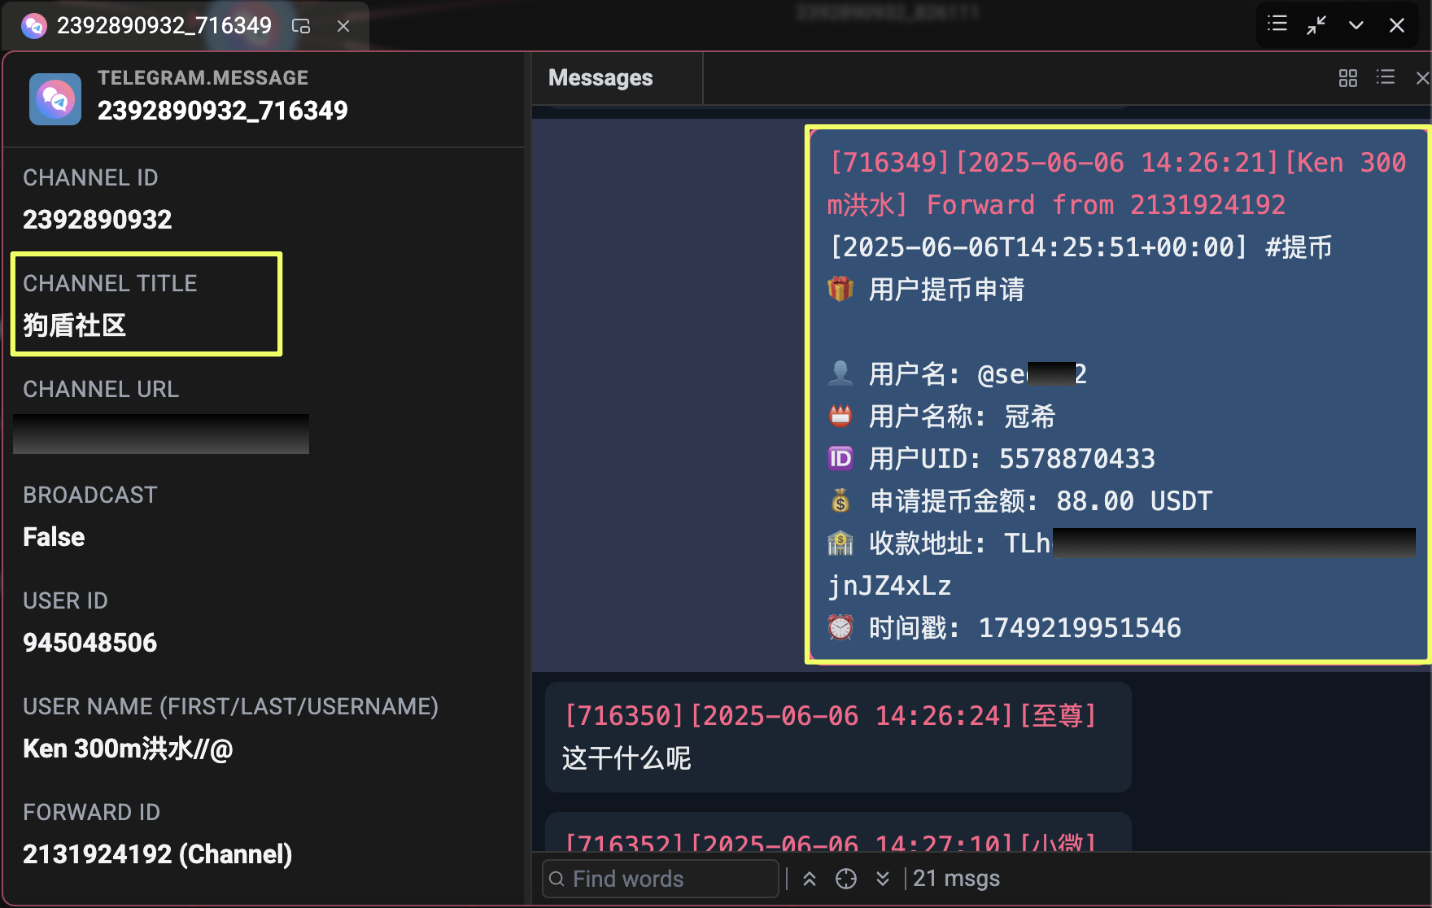
The indexed message does not establish whether @se****2 was sending funds to YY520CN, using an address supplied by someone else, or operating an account connected to the same person. The shared destination is a useful lead, but it is not enough to establish common ownership or the purpose of the payment.
DogPay balances over time
The community escrow records offered another view of YY520CN’s financial activity. Three balance snapshots were recorded at different points:
Date | Recorded balance |
February 2024 | 125.38 USDT |
October 2025 | 547.41 USD |
November 2025 | 20.04 USD |
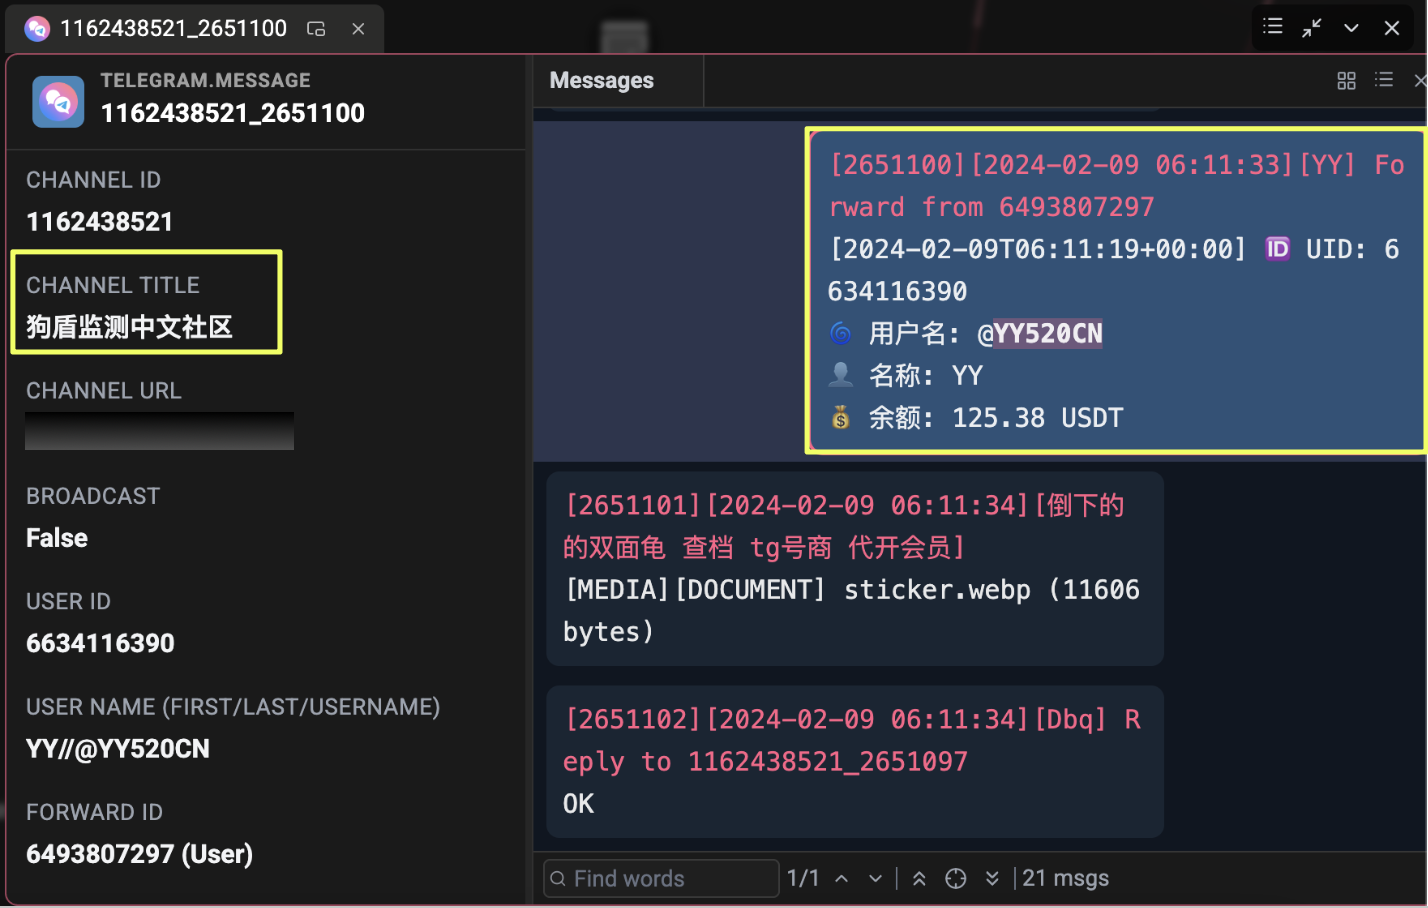
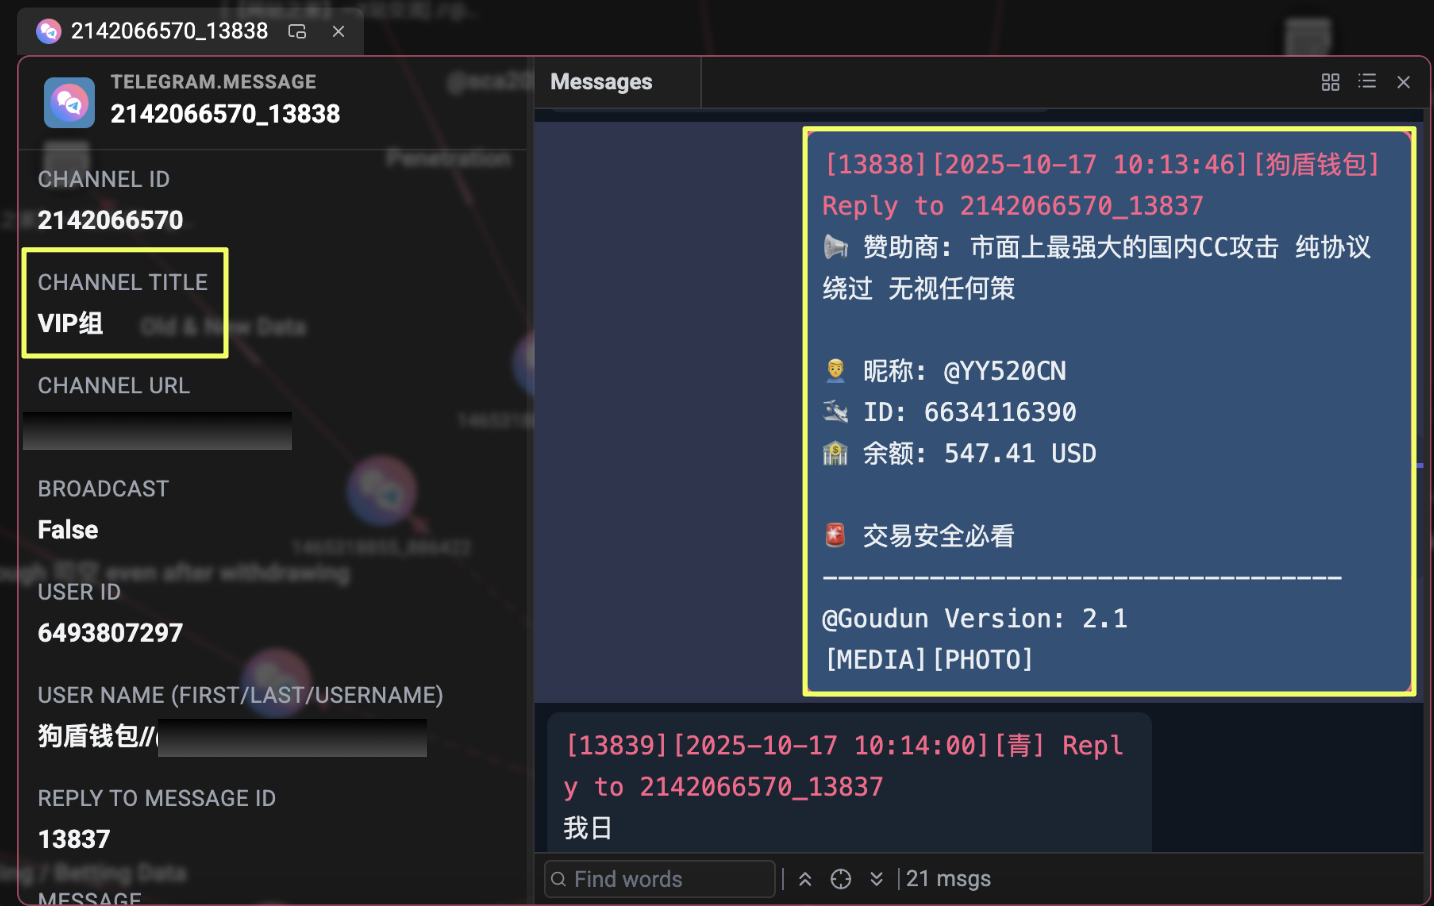
These figures are snapshots, not a complete transaction history. They cannot establish total revenue, expenditure or the volume of payments processed through DogPay. The difference between the recorded balances does, however, show that the amount held in the account varied considerably over time.
Converting cryptocurrency
A conversation from 28 January 2025 provided a possible lead on what happened after funds left the community wallet. While discussing withdrawals, YY520CN complained that even after transferring money to his own address, he still had to approach 司空老贼, roughly translated as “that old crook Sikong”, to exchange it.
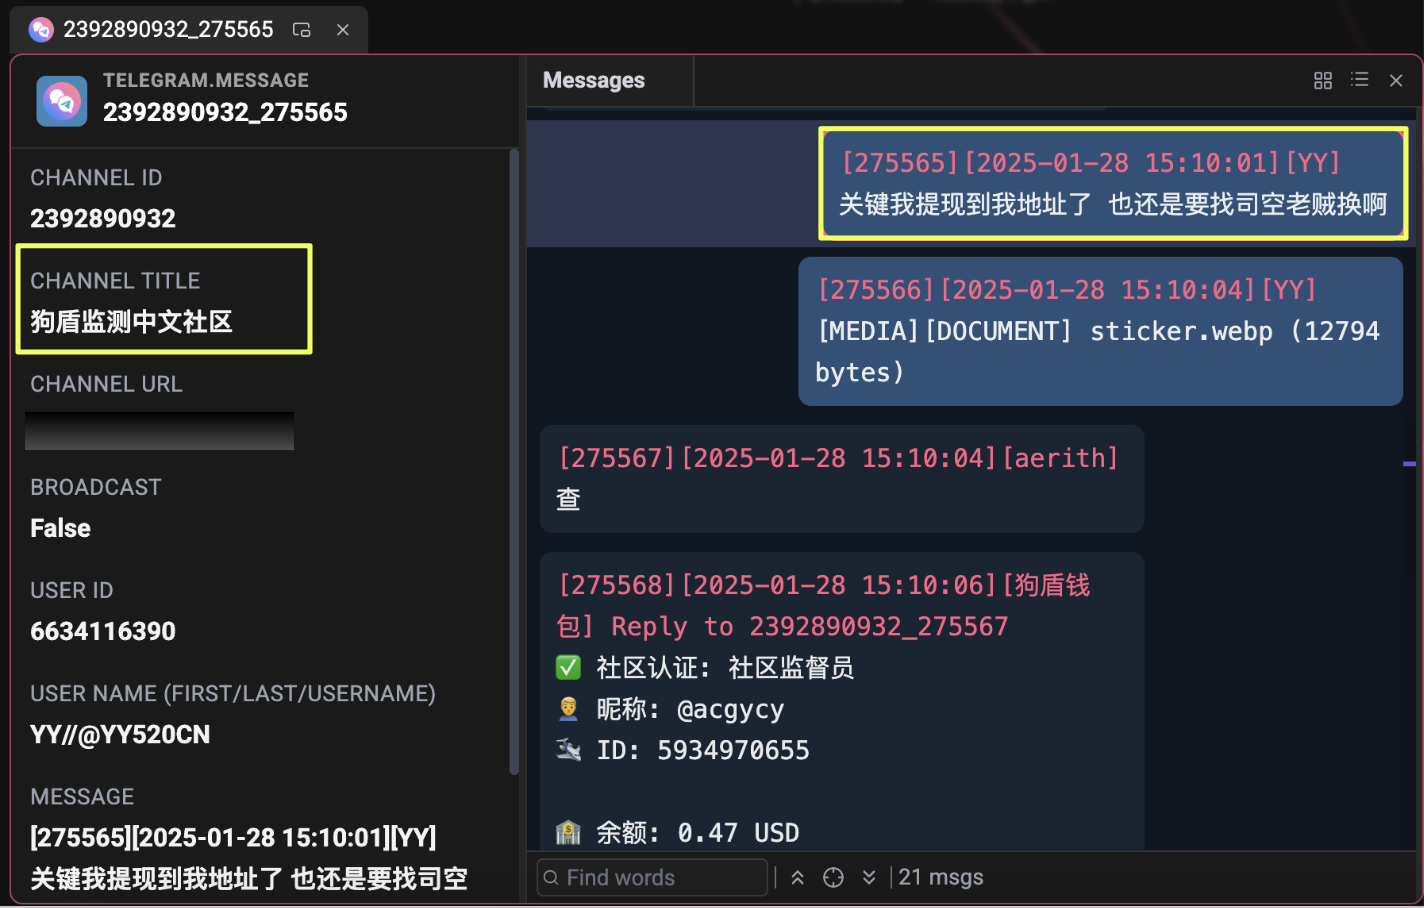
A separate record indexed in the VIP组 group in October 2025 showed a receipt for a 1 USDT transfer involving a broker whose display name advertised the purchase of “clean” USDT.
- Group: VIP组, https://t.me/vip*****yi
- Broker: 司空 (@c*****ao)
- Telegram user ID: 6775611504
- Recorded transfer: 1 USDT
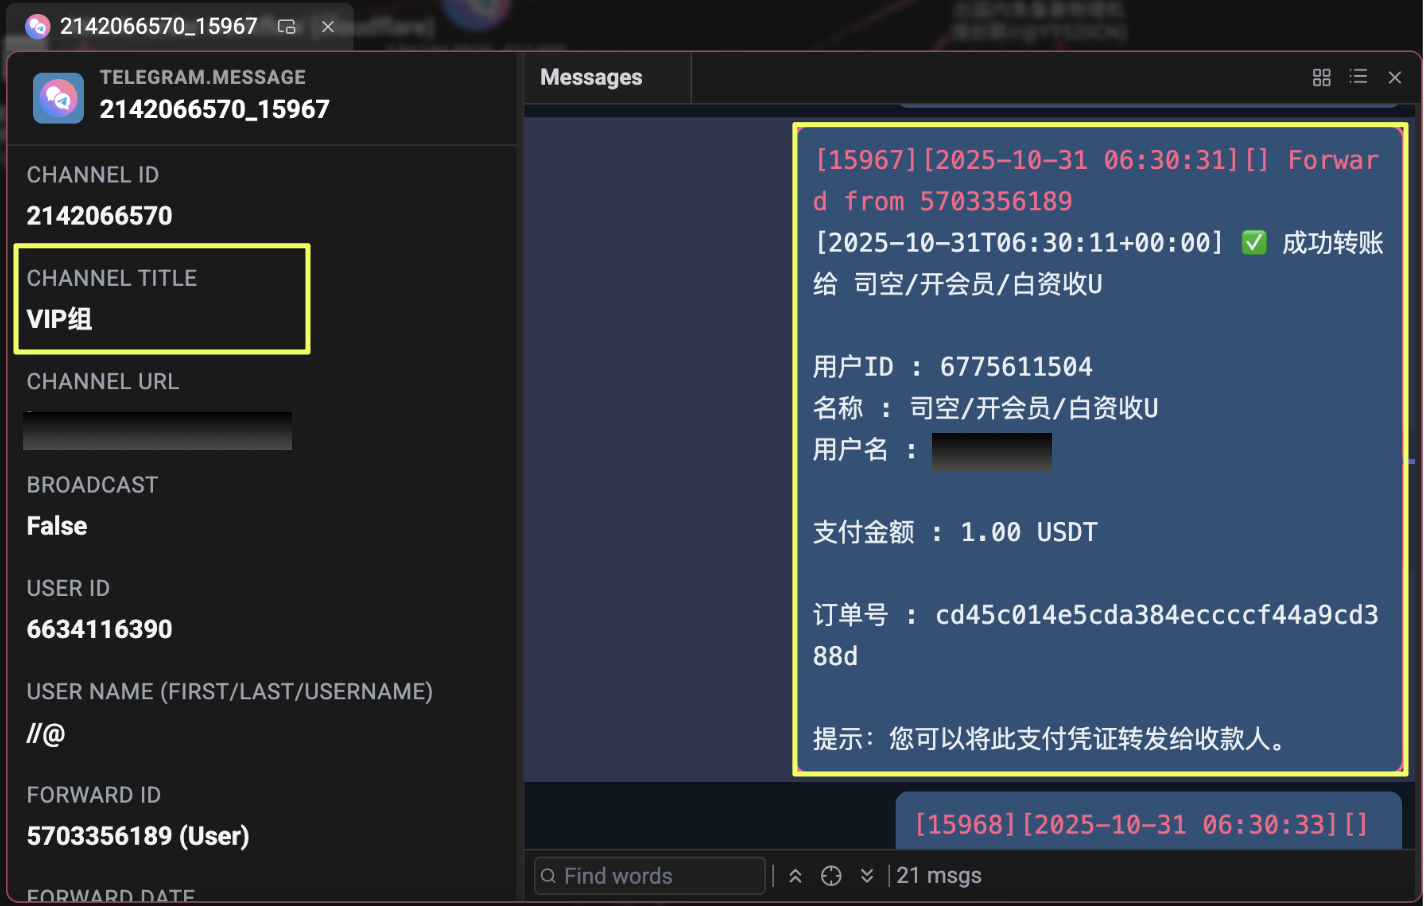
The January conversation and October receipt provide a lead connecting YY520CN’s discussion of cryptocurrency conversion with an account advertising exchange services. However, the available records do not establish the complete route of any particular payment from DogPay to this broker, nor do they prove that the October transfer was connected to the earlier withdrawal discussion.
The financial records therefore provide several pieces of a possible payment chain: YY520CN repeatedly shared a TRON address, received a wallet-monitoring alert for an incoming transfer, appeared in records involving DogPay balances, and discussed using a broker to exchange cryptocurrency. These connections help map his financial activity, but they should not be treated as a fully reconstructed flow of funds without transaction-level evidence linking each stage.
From Floods to Footholds
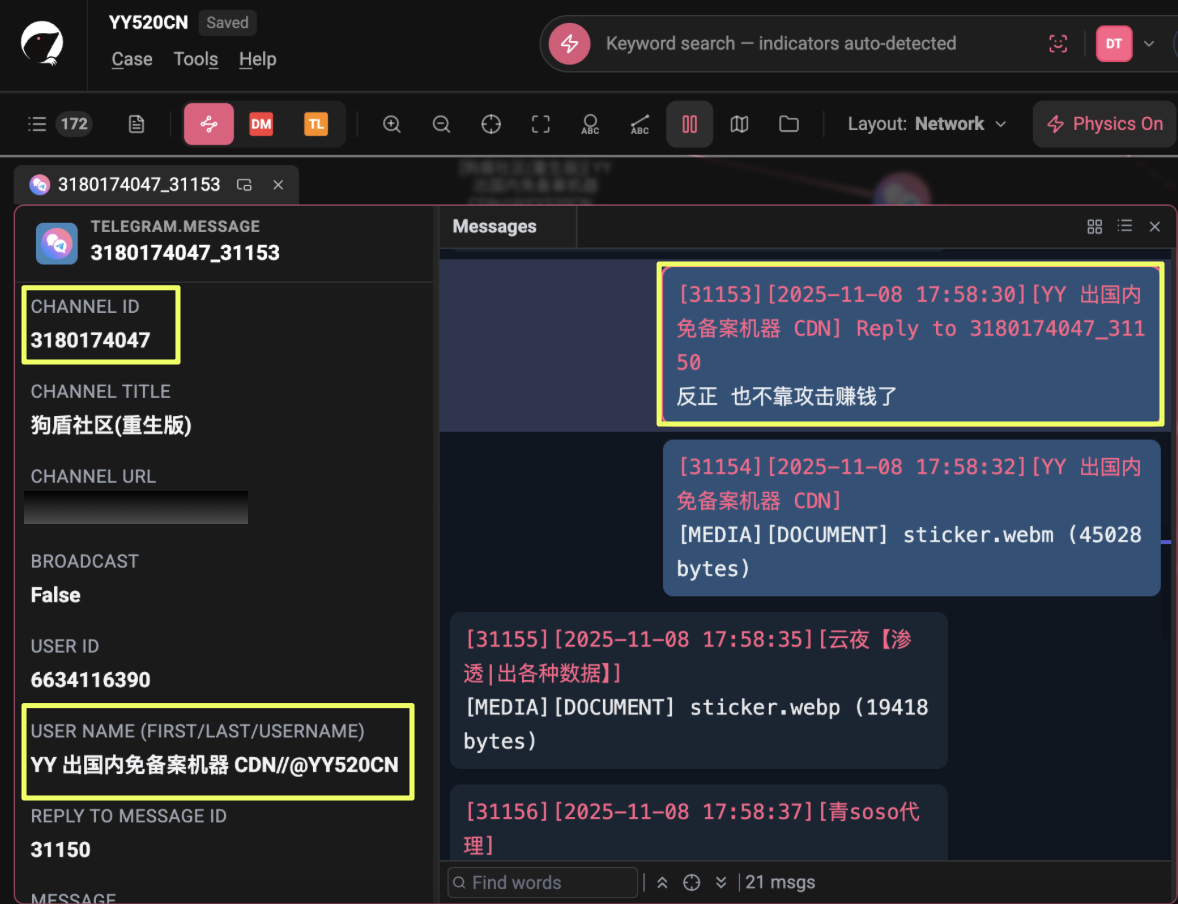
By late 2025, YY520CN was giving signs that his business was moving beyond DDoS attacks. On 8 November, when another member in 狗盾社区(重生版) remarked on how carefree he seemed, YY520CN replied that he no longer made his money from attacks anyway. The comment was brief, but his subsequent activity points to a broader range of services, from infrastructure sales to intrusion work and data trading.
A move into infrastructure
The first visible change was in how YY520CN advertised his services. From November 2025 onward, his display names increasingly promoted mainland Chinese servers that did not require ICP filing. An advertisement posted on 30 December 2025 and later forwarded into 黑客素质广场 offered physical servers with ports 80 and 443 open. It emphasised cooperation with data centres rather than script-based workarounds and claimed the machines could be accessed from anywhere in China. An attached image showed a nationwide reachability test, with every province marked green.
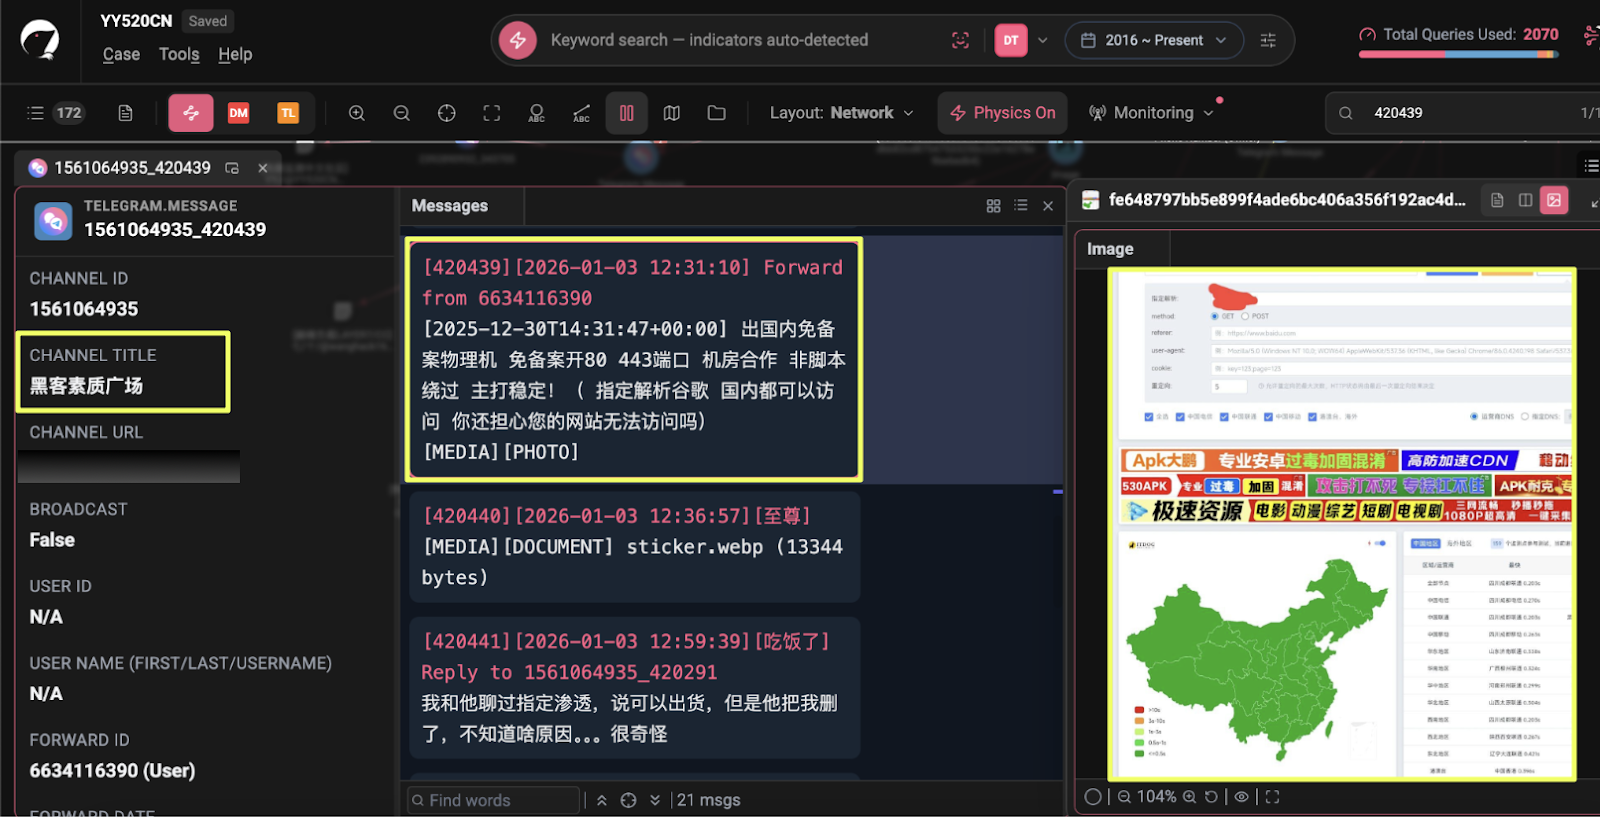
The advertisement established what he was selling, but not where the infrastructure came from. A message from the previous month raises a separate question about his access to servers.
On 10 November 2025, during a discussion in which members of a Telegram group were comparing server specifications, YY520CN offered to show a 192-core Alibaba Cloud machine. He then shared an image showing the disks of another server. When someone asked what anyone would need that much storage for, he replied that he did not know because the machine had come from a 黑鸡, a slang term for a compromised host, and he had not yet looked through it.
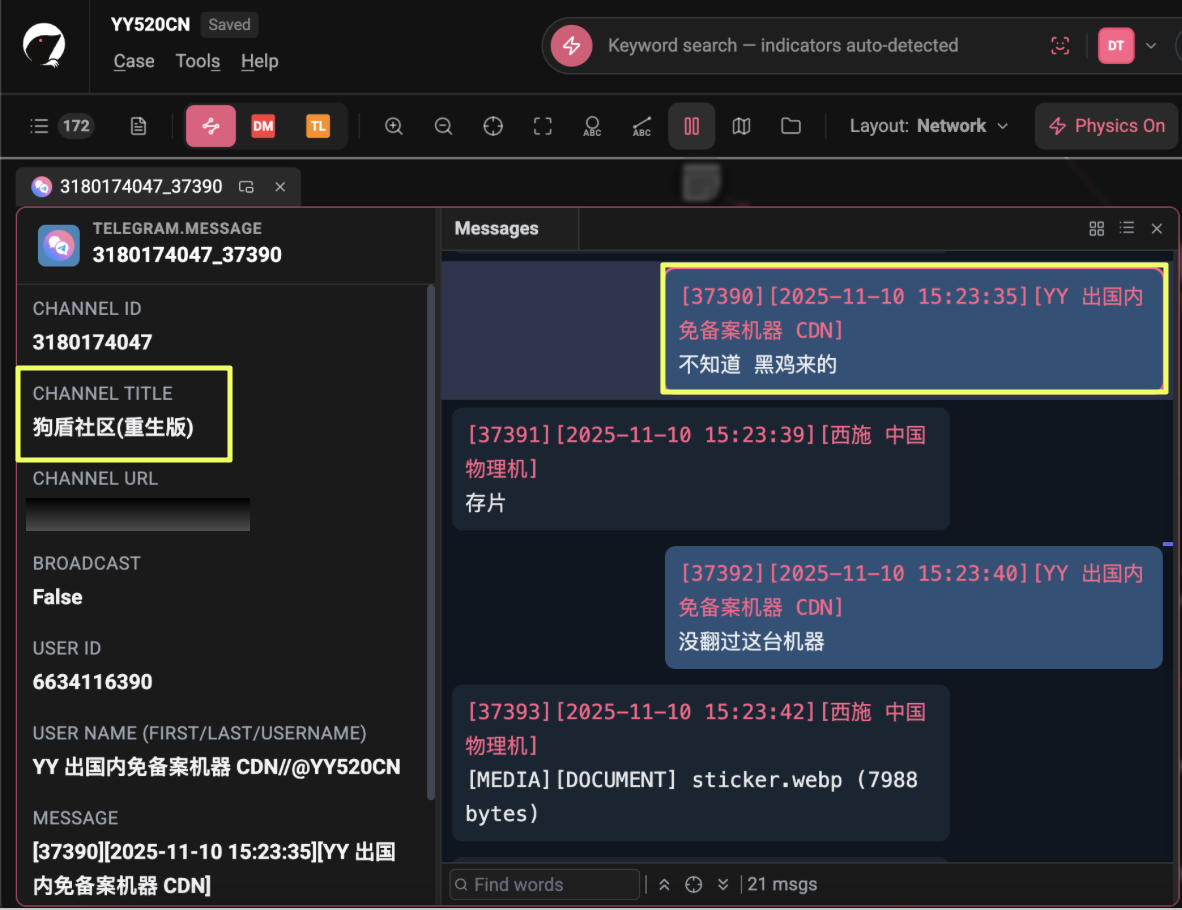
The exchange is worth noting because it places YY520CN in possession of a machine he described as compromised. It does not establish that the server was part of his commercial hosting service or that the infrastructure advertised in December was obtained through unauthorised access. That connection remains unproven.
From attack orders to intrusion and data sales
By February 2026, his messages were describing work that went beyond traffic-based attacks. The records also show him discussing disputes with clients, alleged intrusions and the sale of data.
On 18 February 2026, in VIP组, YY520CN warned other members about a client who had commissioned a targeted intrusion against a specific website and then refused to pay. According to his account, the client argued that much of the extracted data was unusable before asking for the site's entire dataset to be handed over for testing.
- Client identified in the message: @sc****26
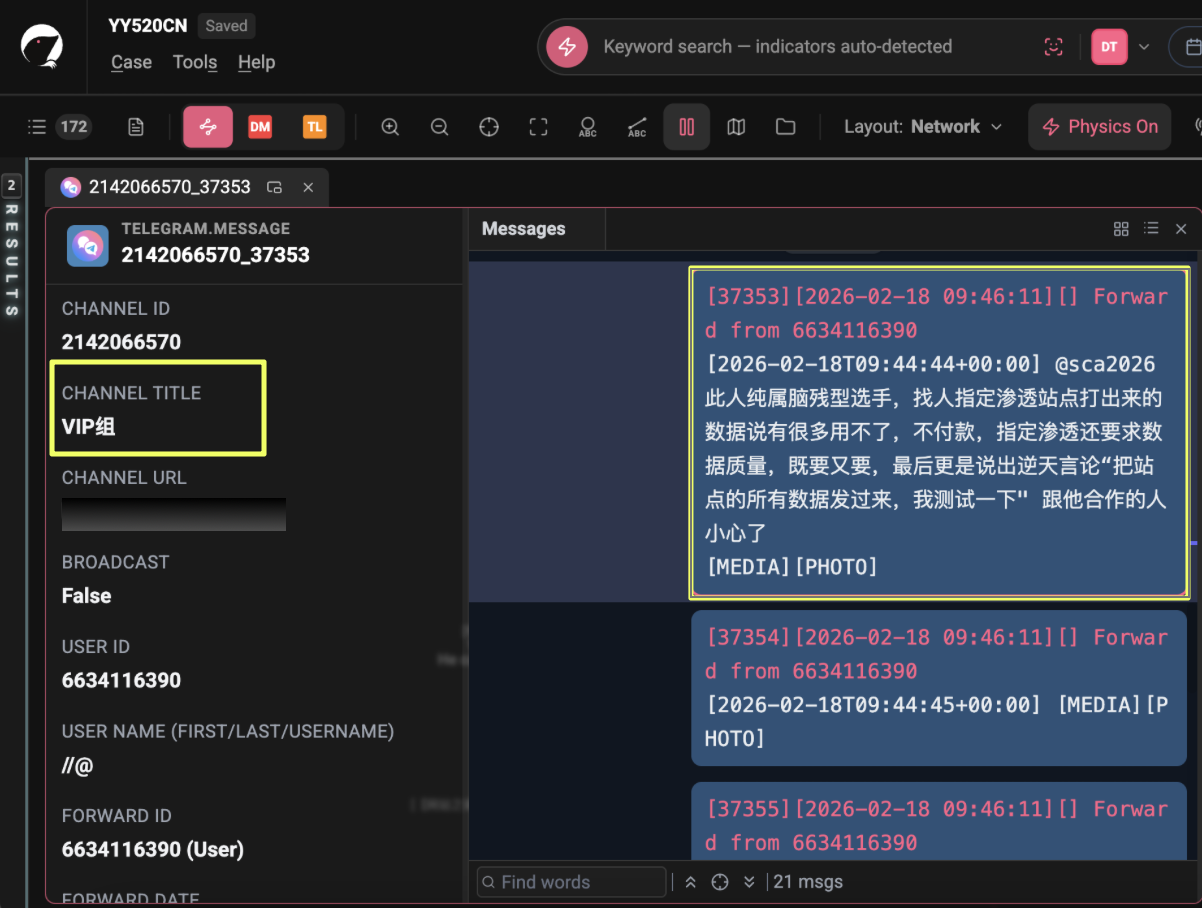
The post presented YY520CN as someone who had undertaken intrusion work on commission and was now warning others about a payment dispute. The underlying operation and the client's account could not be independently established from the message alone.
Two days later, on 20 February 2026, he described an alleged intrusion into a gambling platform. Claiming that “our technical team” had penetrated the service, he said they had found 66 accounts with balances exceeding ten million each, which he alleged were bots used to inflate activity. He added that the platform had reacted angrily after being informed of the flaw.
Around 20 minutes later, he claimed that a single DDoS attack had been sufficient to stop every bot in the group from placing bets.
- Platform link: https://t.me/K9**********nal
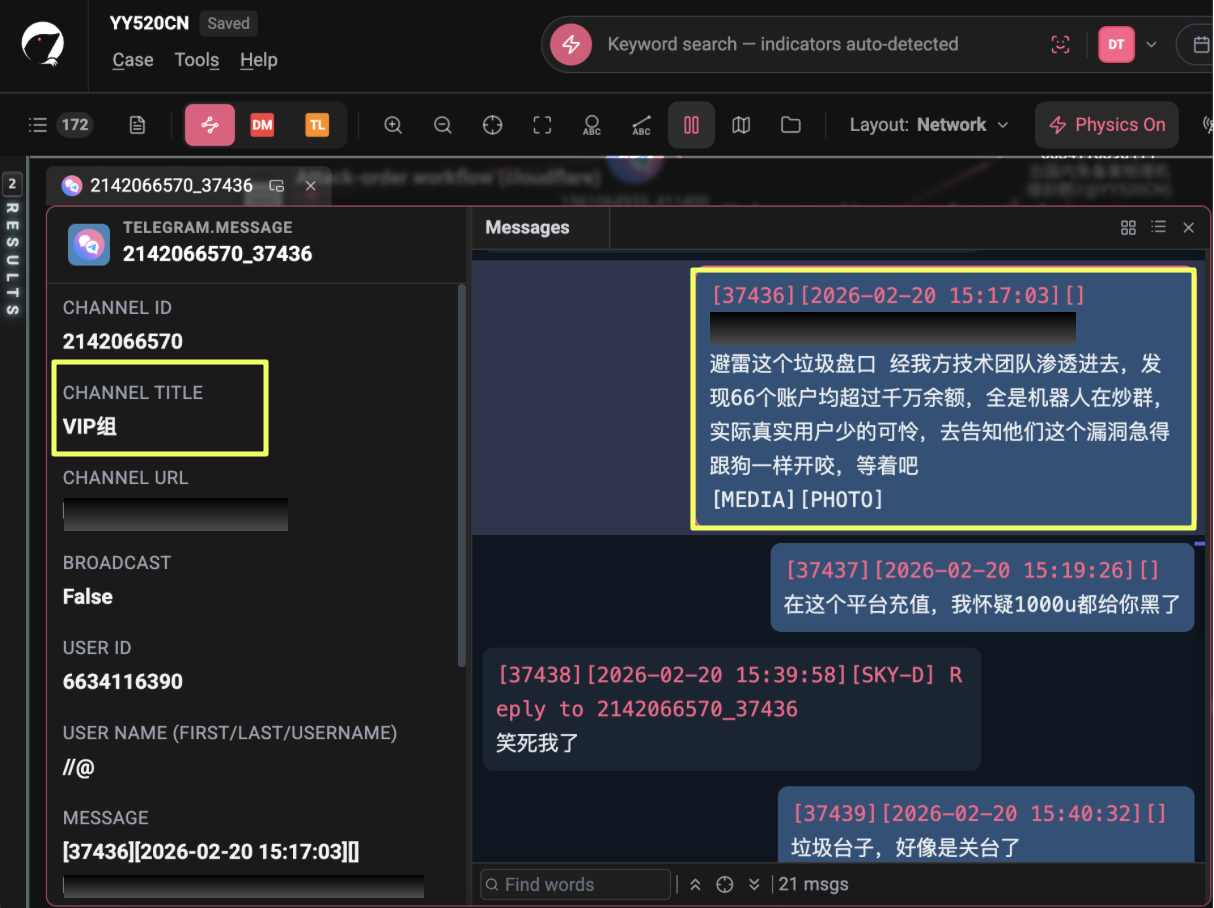
These statements connected intrusion claims with an alleged ability to disrupt the platform's operations. However, the indexed discussion records YY520CN's claims, not independent verification of the account balances, the alleged bots or the reported attack.
The next record shows a more direct commercial pitch. On 1 March 2026, across 网站之家 and X站交流, YY520CN offered gambling and betting data indexed by phone number, describing it as data from a recent intrusion. He also approached the group operator, addressed as 牛哥, to ask whether he could be listed as a penetration provider.
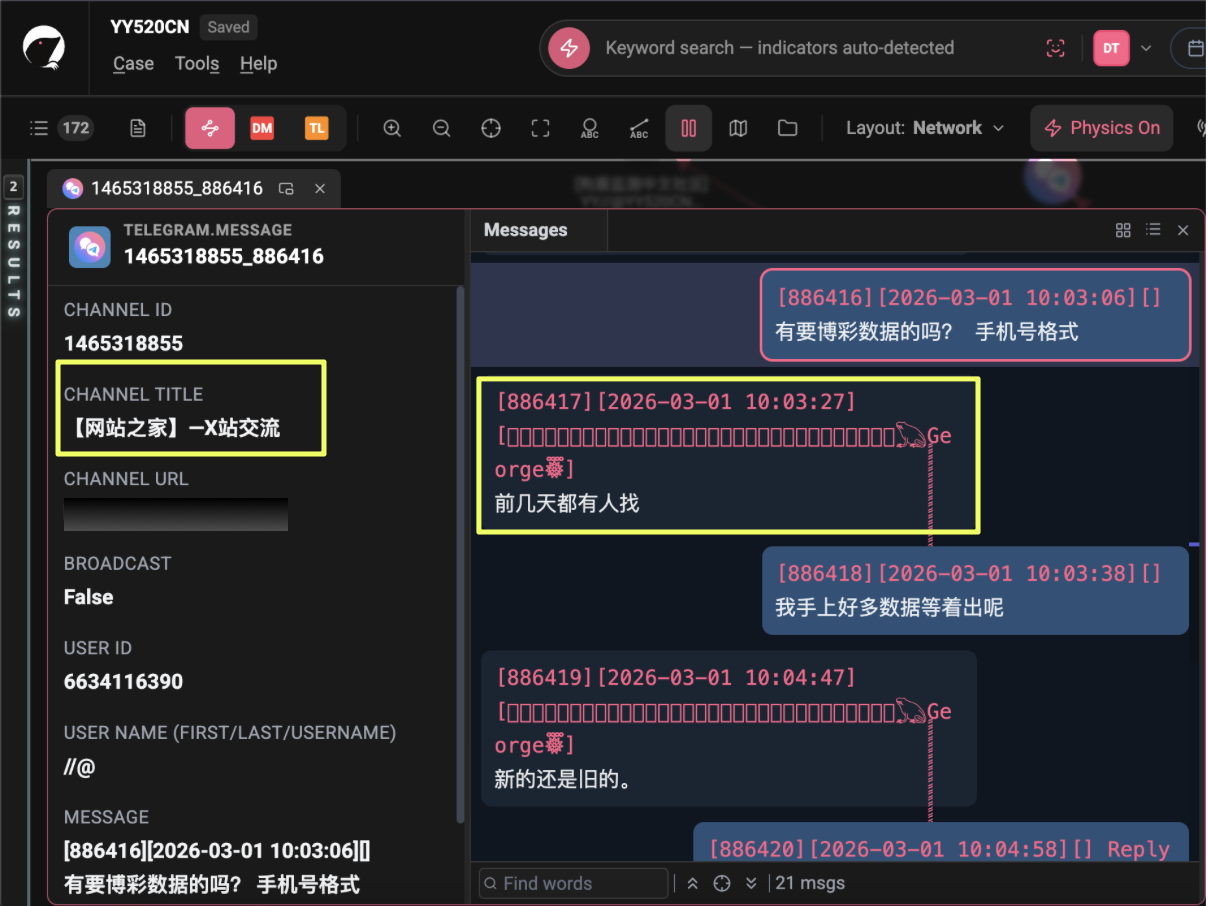
The request suggests that he was seeking a more formal place within a community where intrusion services were advertised. A later record provides a possible indication of how that effort progressed.
A place in the service directory
On 15 September 2026, YY520CN advertised first-hand, real-time data concerning undelivered parcels from a large Vietnamese courier in 互站 1024 源码搭建技术交流群. The post added another category to the services he was promoting, this time involving logistics-related information rather than DDoS attacks or gambling data.
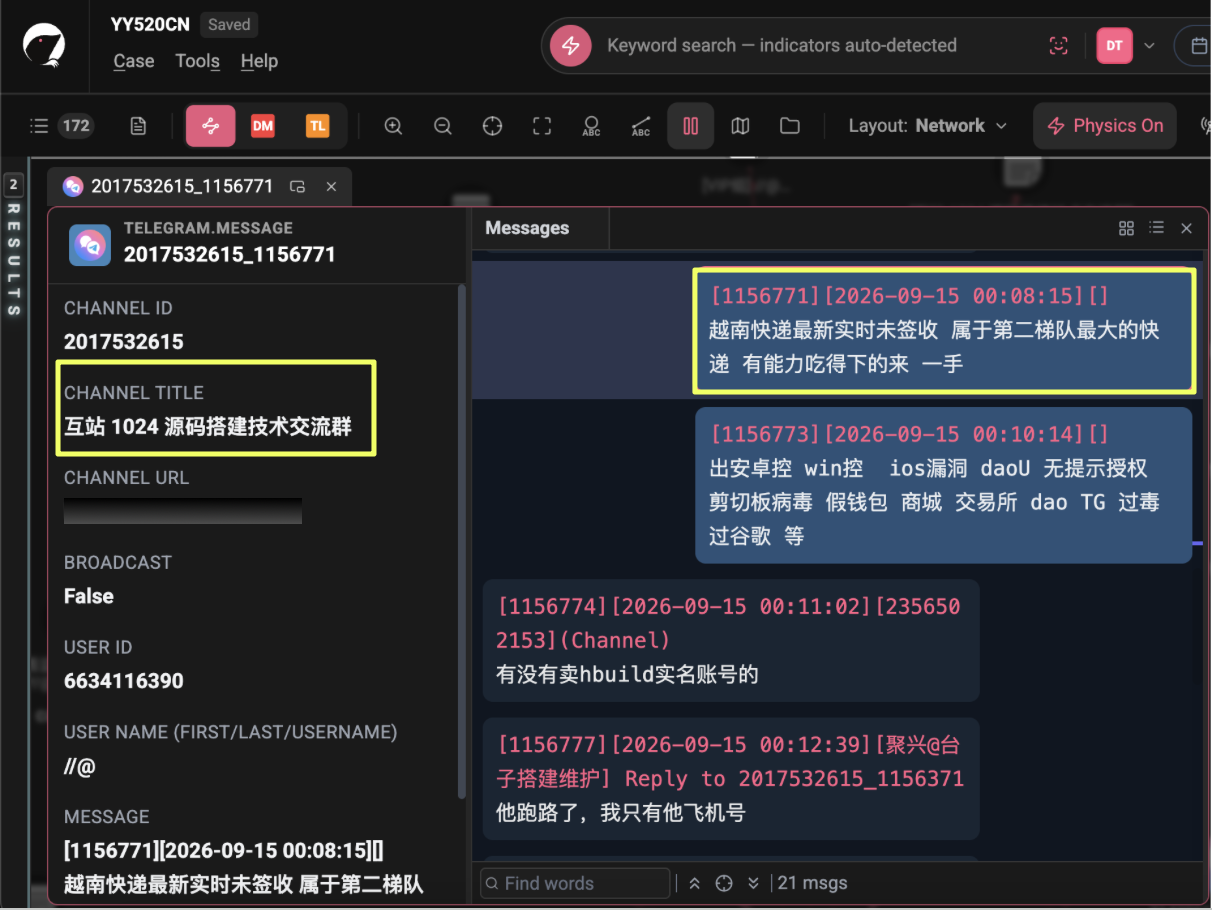
On 8 October 2026, a member of 网站之家 posted a screenshot of a service directory associated with the same 阿牛 (Niu) network that YY520CN had approached in March. The directory included a section labelled 指定渗透 (targeted penetration), where @YY520CN appeared as a listed provider. A red mark had been drawn beside his entry.
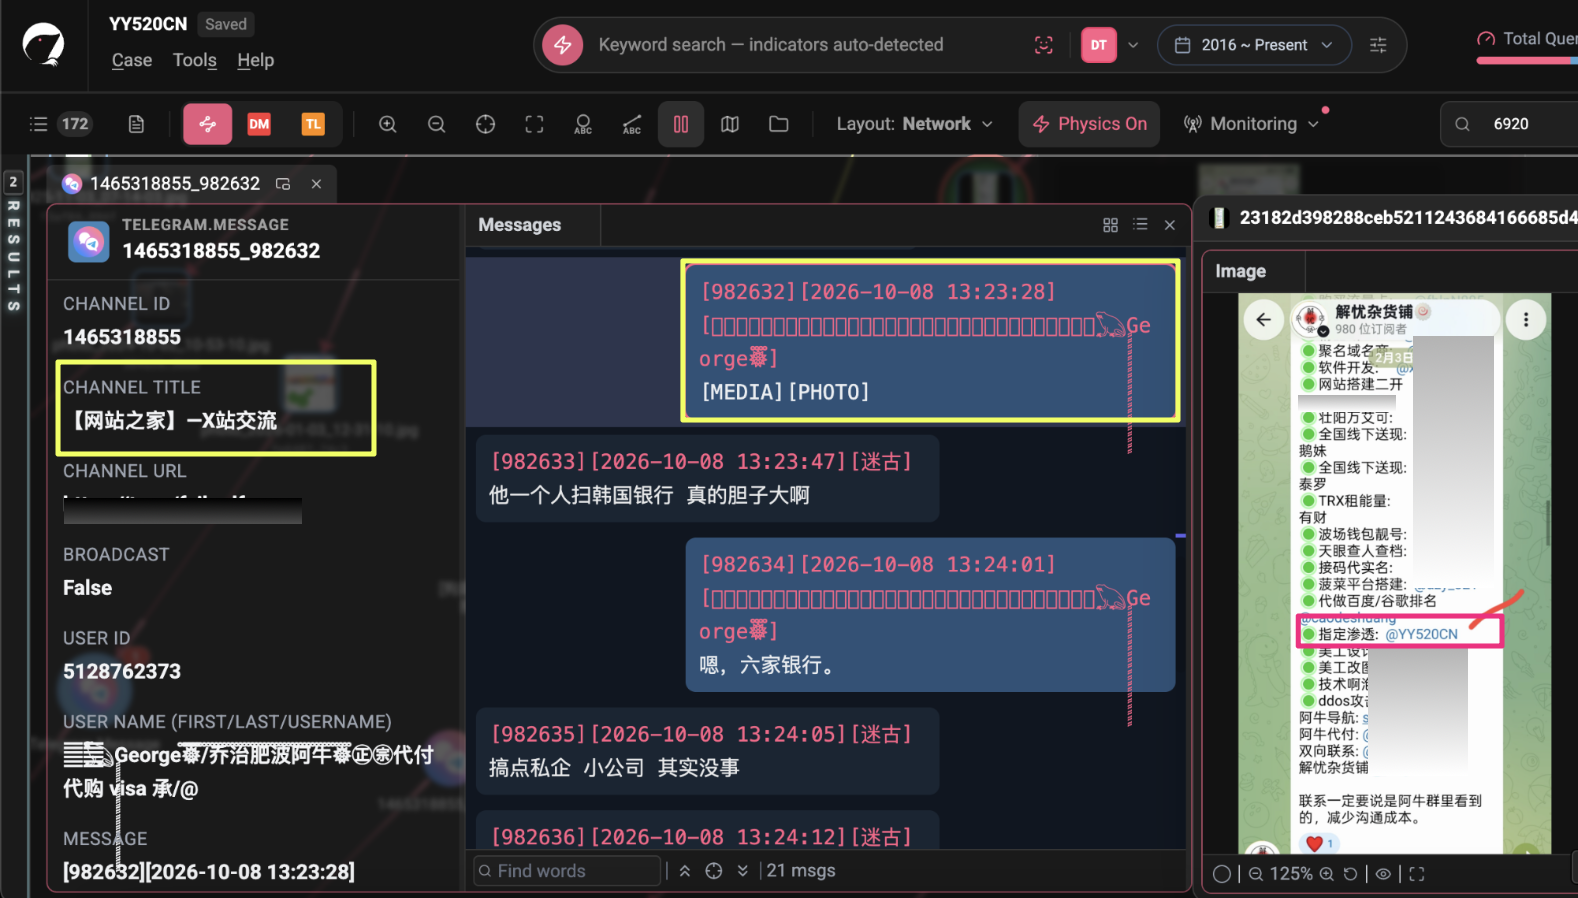
The screenshot provides evidence that the handle appeared in the directory. Combined with the earlier request to 牛哥, it is consistent with YY520CN having secured a listing, although the screenshot alone does not establish the terms of any arrangement or confirm that the directory operator had formally vetted him.
By this point, the indexed record showed a wider commercial profile than the one visible in late 2023. YY520CN had moved from sharing stresser results and advertising attack services to promoting server infrastructure, discussing commissioned intrusions and offering data he claimed to have obtained through breaches. The records also place him in communities where such services were marketed to other operators.
Exposure & Erasure
By 8 October 2026, YY520CN’s name was circulating through the same underground communities where he had spent years building his reputation. StealthMole’s Telegram Tracker captured three images posted between 8 and 9 October that documented how members reacted to the CrowdStrike research, revisited his previous affiliations and began connecting the public reporting to someone they already knew.
The news reaches his own circles
The first image appeared on 8 October at 10:44, posted by Konwkonw in the Panstar group.
- Group: Panstar ® 派大星, https://t.me/pan*******at
- Message ID: 3861828724_298338
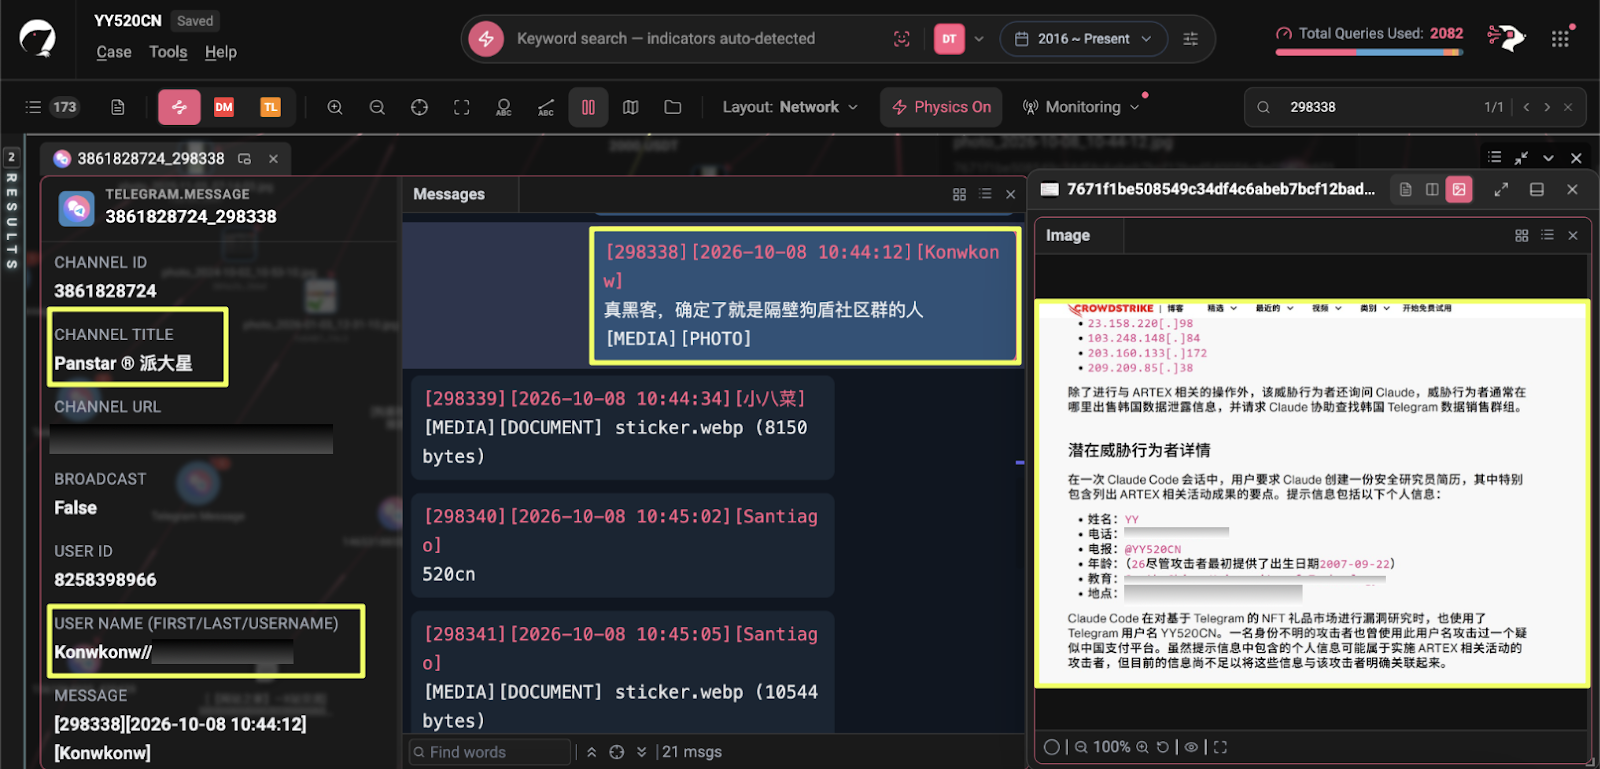
The screenshot showed a Chinese-language rendering of CrowdStrike’s research. The visible excerpt discussed activity connected to ARTEX, including requests for help locating Korean Telegram groups involved in data sales and a Claude Code session in which the user sought assistance preparing a security researcher CV. The excerpt identified @YY520CN among the personal details contained in the prompt.
It also referenced vulnerability research involving a Telegram-based NFT gift marketplace and activity against a suspected Chinese payment platform. However, CrowdStrike's own caveat was important: the personal information might belong to the person behind the ARTEX activity, but it was not sufficient to establish a definitive link.
The conversation around the screenshot showed members making their own connections. Shortly before Konwkonw posted it, another participant had shared the ARTEX repository, describing it as an autonomous AI penetration-testing system that had won a Baidu agent challenge and complaining that the project had disappeared before a backup could be made.
- Repository: https://github.com/Au*********/ARTEX
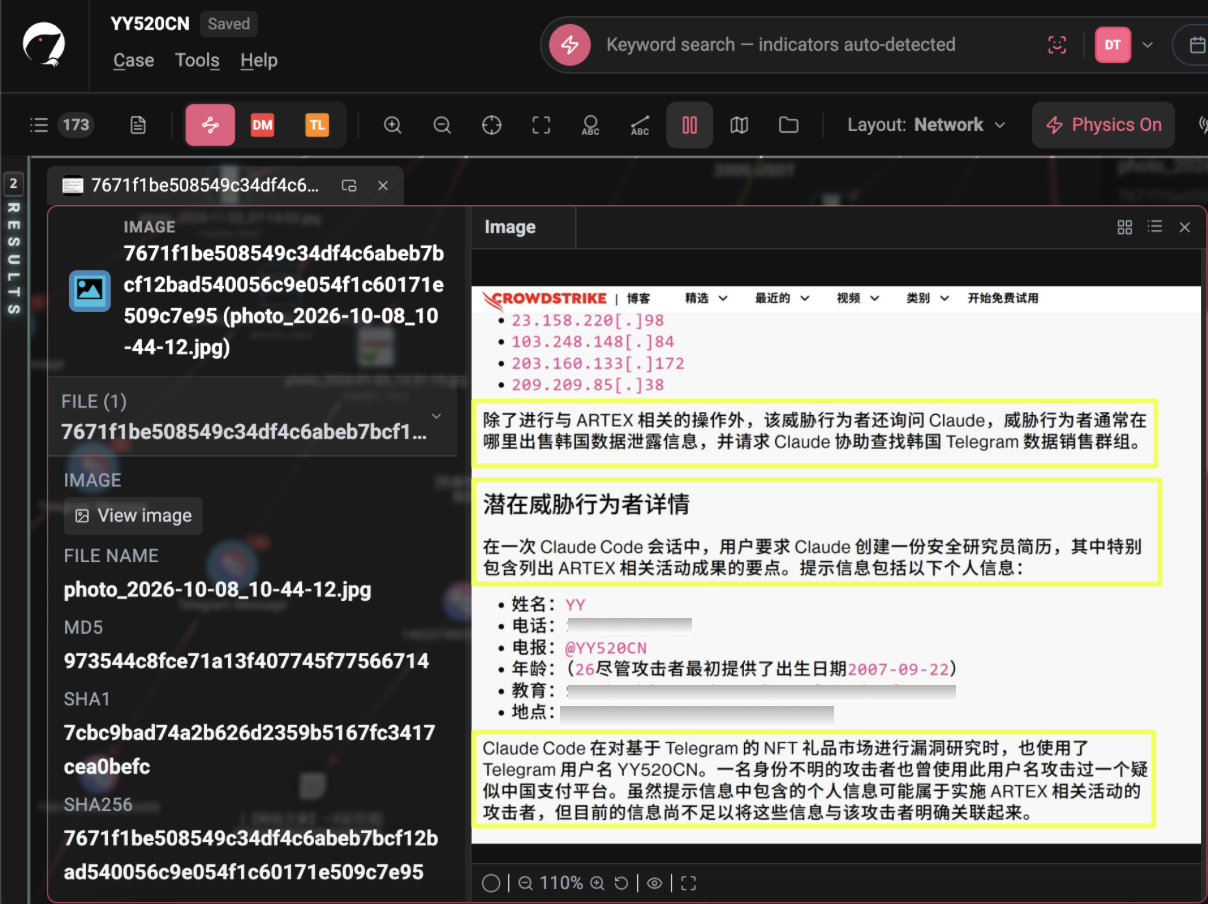
Konwkonw subsequently suggested that the Guangdong man mentioned in the news was someone from the neighbouring Dog Shield community. After sharing the research, he described the identification as confirmed, calling the person a real hacker and one of the Dog Shield members. Another participant replied simply with 520cn.
These messages show that members were connecting the public reporting to YY520CN’s established identity. They are evidence of the community’s reaction, however, rather than independent confirmation of CrowdStrike’s attribution.
An old affiliation comes back into view
The second image appeared at 13:23 on 8 October.
- Group: 【网站之家】—X站交流
- Message ID: 1465318855_982632
It showed the service directory associated with the 阿牛 (Niu) network, with @YY520CN listed under 指定渗透 (targeted penetration) and marked in red.
The directory had already surfaced during the investigation into YY520CN’s commercial activity. Its appearance again during the exposure period suggests that members were revisiting existing records to establish where his handle appeared and what services he had advertised.
The significance here is not the listing itself, which was documented earlier, but the renewed attention it received after the research became public.
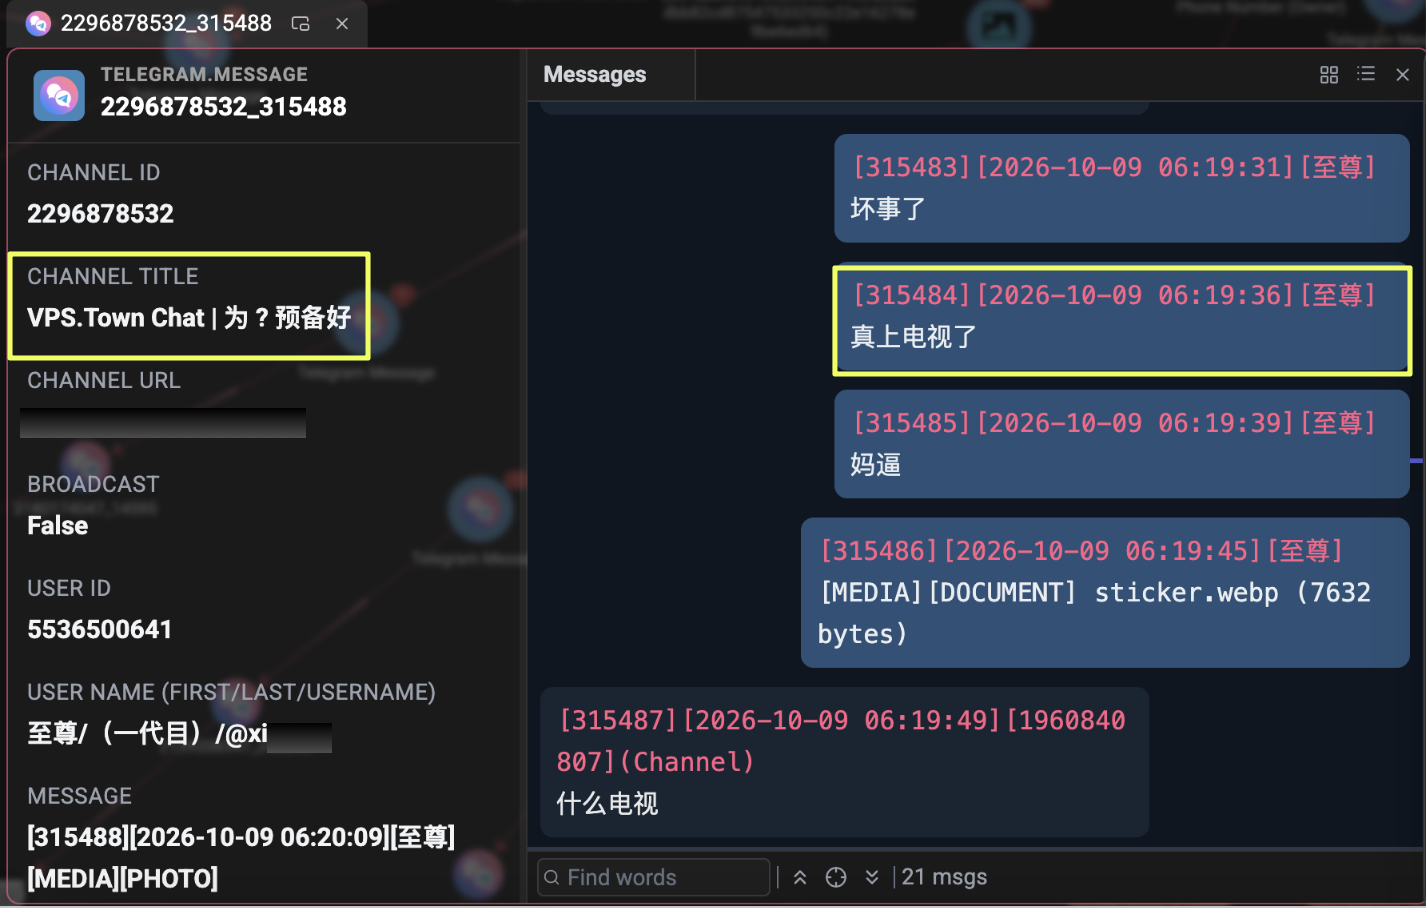
A further reaction came on 9 October from 至尊 (@xi*****4) in VPS Town Chat. 至尊 had previously referred to YY520CN as the Dog Shield community’s hacker and was listed as a juror in its staff structure.
- Group: VPS.Town Chat, https://t.me/VPS********n
- Message ID: 2296878532_315488
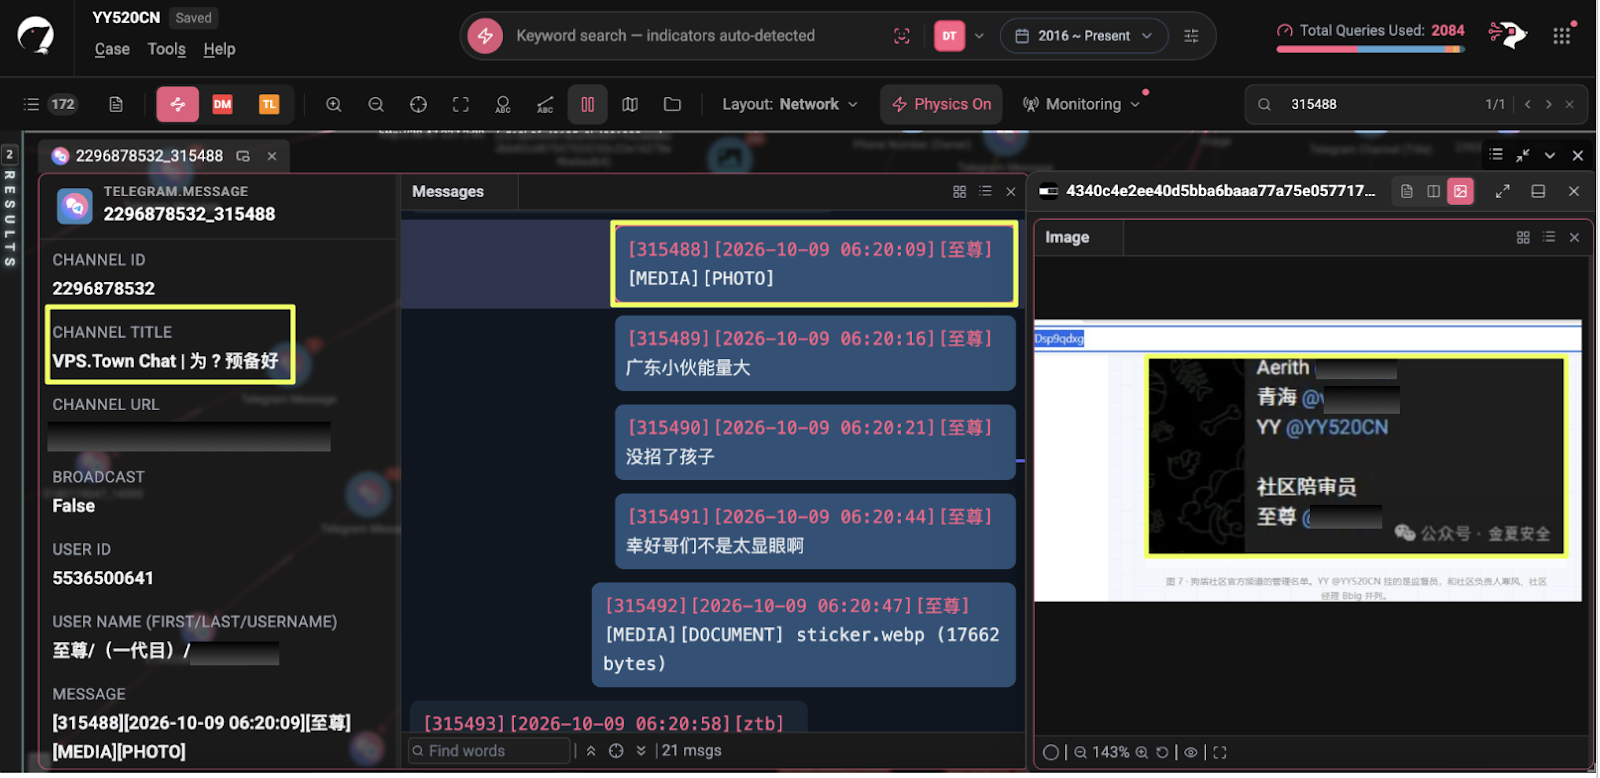
至尊 wrote that the situation had gone badly and that it had “really made it onto TV”. He then shared a screenshot of a Chinese media article reproducing the Dog Shield staff list. The screenshot showed Aerith, 青海 and YY (@YY520CN) among the supervisors, with 至尊 himself listed beneath them as a juror.
He followed the image with a remark about the “Guangdong lad”, adding that he was fortunate not to be particularly conspicuous himself.
His reaction showed that the reporting had reached people connected to YY520CN’s earlier community. It also brought his former role within Dog Shield back into public discussion. The messages do not establish what 至尊 knew about the alleged activity, but they document his response as the story spread.
YY520CN breaks his silence
While members were discussing the research, a new Telegram channel appeared in the keyword results:
- Channel title: Y
- Channel ID: 4498372745
StealthMole’s Telegram Tracker indexed five posts from the channel between 8 and 9 October 2026.
Date and Time | Message / Activity |
8 October, 00:56 | Channel created |
8 October, 08:23 | Asked people with questions to leave a message in the channel |
8 October, 14:59 | Denied wrongdoing and accused the Korean side of attributing activity it could not trace to him and other innocent people |
8 October, 15:48 | Said he would only accept an interview from a named reporter at South Korea’s SBS and asked others to stop sending harassing messages |
9 October, 11:20 | Said he had not been contacted by police and told followers not to worry |
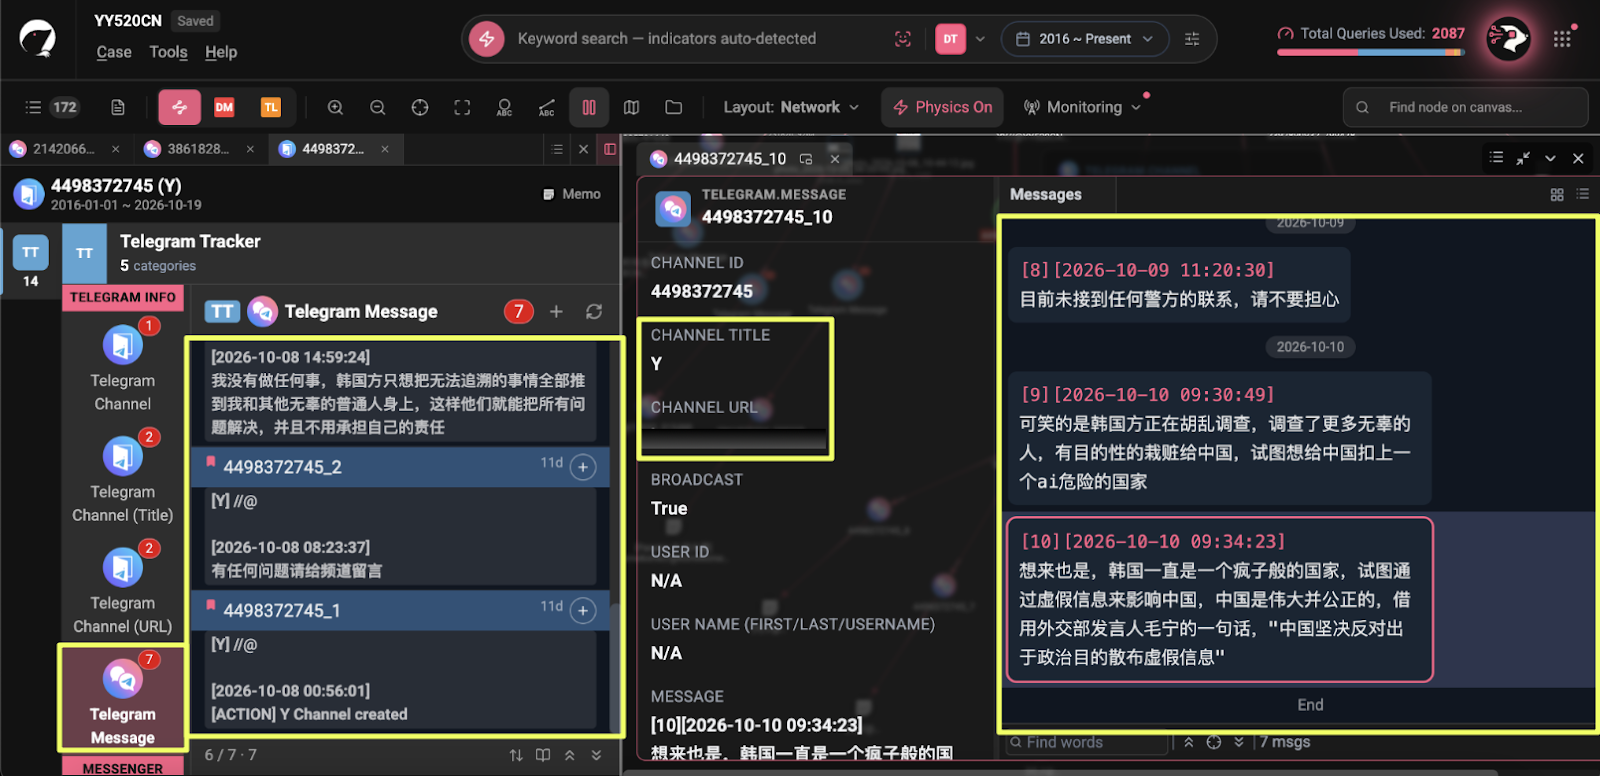
The channel was created on 8 October, before the screenshots appeared in the indexed groups later that day. The timing is notable, but it does not establish whether YY520CN knew the research was about to be published or had already been contacted about it.
His subsequent posts were more direct. He denied wrongdoing, challenged the allegations and asked people to stop contacting him. He also referred to the Korean side and identified the SBS reporter from whom he was willing to accept an interview. On 9 October, he stated that police had not contacted him.
These were his own claims, not independent confirmation of the status of any investigation. The posts also did not provide a detailed account of the historical activity documented in this report. Instead, they focused on the public allegations and the attention he was receiving.

By 9 October, the exposure had brought YY520CN’s identity, his Dog Shield affiliations and his advertised services into renewed discussion across several Telegram communities. His own channel provided a record of how he responded, while the reactions from other members showed how quickly his established underground identity became part of the public conversation.
The account’s next recorded change came on 11 October 2026. StealthMole’s Telegram Tracker showed Telegram user ID 6634116390 with a blank display name and no username attached. Earlier records retained the advertising names associated with @YY520CN, while messages indexed from February, March and September 2026 showed the same user ID without a display name. The timing, just days after the CrowdStrike research began circulating, is notable, although the records do not establish why the identifiers disappeared.
The reaction within Dog Shield was also becoming more cautious. In the same VPS.Town conversation where 至尊 shared the media coverage, another member expressed surprise that the community still existed. 至尊 replied that it did, but suggested it might now be finished and that it was time to delete accounts and leave. The exchange does not establish that Dog Shield shut down or that members followed this advice, but it captures the uncertainty among people connected to the community as the story unfolded.
Conclusion
Public reporting brought YY520CN to attention over activity linked to South Korea’s financial sector. StealthMole provided a longer view of the account behind the handle, tracing its history through nearly three years of activity. The records place Telegram user ID 6634116390 in the Dog Shield ecosystem from December 2023, followed by administrator and supervisor roles in early 2024. Over time, its display name became a changing storefront for attack services, account-banning requests, infrastructure and other offerings.
The commercial records revealed how YY520CN presented his services and handled payments. Advertisements described DDoS attacks and Cloudflare origin tracing, with DogPay escrow used to structure transactions. A repeatedly shared TRON address, wallet-monitoring alerts and discussions about cryptocurrency exchange provided further leads into his financial activity, although the available evidence does not establish a complete flow of funds between these services. By 2025 and 2026, his advertised work had expanded to include unfiled hosting, while his messages described commissioned intrusions and the sale of data he claimed to have obtained through breaches. This broader activity provides context for understanding the account, but the claims in his advertisements and conversations are not independent proof that every operation took place as described.
The investigation also leaves important questions unresolved. The historical records connect the handle @YY520CN to user ID 6634116390, while the similarities between the main account and @JJCDN suggest a possible secondary identity that remains unconfirmed. The channel titled Y provided a record of the account’s response to the public attention, but neither it nor the Telegram history establishes the operator’s real-world identity. Most importantly, the evidence gathered here does not independently confirm that YY520CN was responsible for all the activity described in CrowdStrike’s research. The researchers’ own caveat about the personal information in the reported prompt reinforces the need to keep that distinction clear.
Editorial Note
Dark-web and Telegram investigations rarely provide a complete picture. Accounts change names, communities reappear under new identifiers, and public claims may be difficult to verify independently. Attribution therefore depends on weighing multiple connections while recognising where the evidence stops.
In this case, StealthMole’s historical indexing helped connect years of Telegram activity and preserve the account’s history after its familiar identifiers disappeared. The result is a more detailed picture of YY520CN’s online presence, while leaving the questions that the available evidence cannot settle open.
To access the unmasked report or full details, please reach out to us separately.
Contact us: support@stealthmole.com
Labels: Featured, Threat Actor


