The Rey Swap: Impersonating ShinyHunters' Rey After His Arrest
On 29 September 2026, Jordanian authorities reportedly detained Saif al-Din Khader, better known as Rey. He had been identified as one of the administrators of Scattered LAPSUS$ Hunters and a key figure in the ShinyHunters extortion ecosystem. Reuters later reported that Rey was cooperating with the FBI to identify other members of the group. His reported detention raised questions about what would happen to the ShinyHunters operation and the people still using its name.
But the activity did not stop. Throughout September and October, a Telegram account operating under @reyswap continued presenting itself as Rey and claiming to represent ShinyHunters. The account advertised stolen data, launched new channels, appeared on cybercrime forums and issued a series of conflicting statements about Rey's arrest. As its story changed, so did the identities it claimed to represent.
The ShinyHunters name has been the subject of similar disputes before. During StealthMole's August 2025 investigation into Scattered LAPSUS$ Hunters, competing accounts challenged each other's legitimacy, with PGP keys and historical channel activity becoming important points of verification. This time, we followed @reyswap through StealthMole's Telegram Tracker and Dark Web Tracker, examining its account history, associated channels and contact infrastructure to establish when the persona first appeared and whether it had any verifiable connection to the original operators.
A Familiar Name in a New Account
The investigation began with a Telegram handle that kept appearing alongside Rey's name following news of his detention: @reyswap. ShinyHunters-branded channels listed it as their "Account Office", while posts signed by "Rey" directed potential buyers to the account to negotiate data sales.
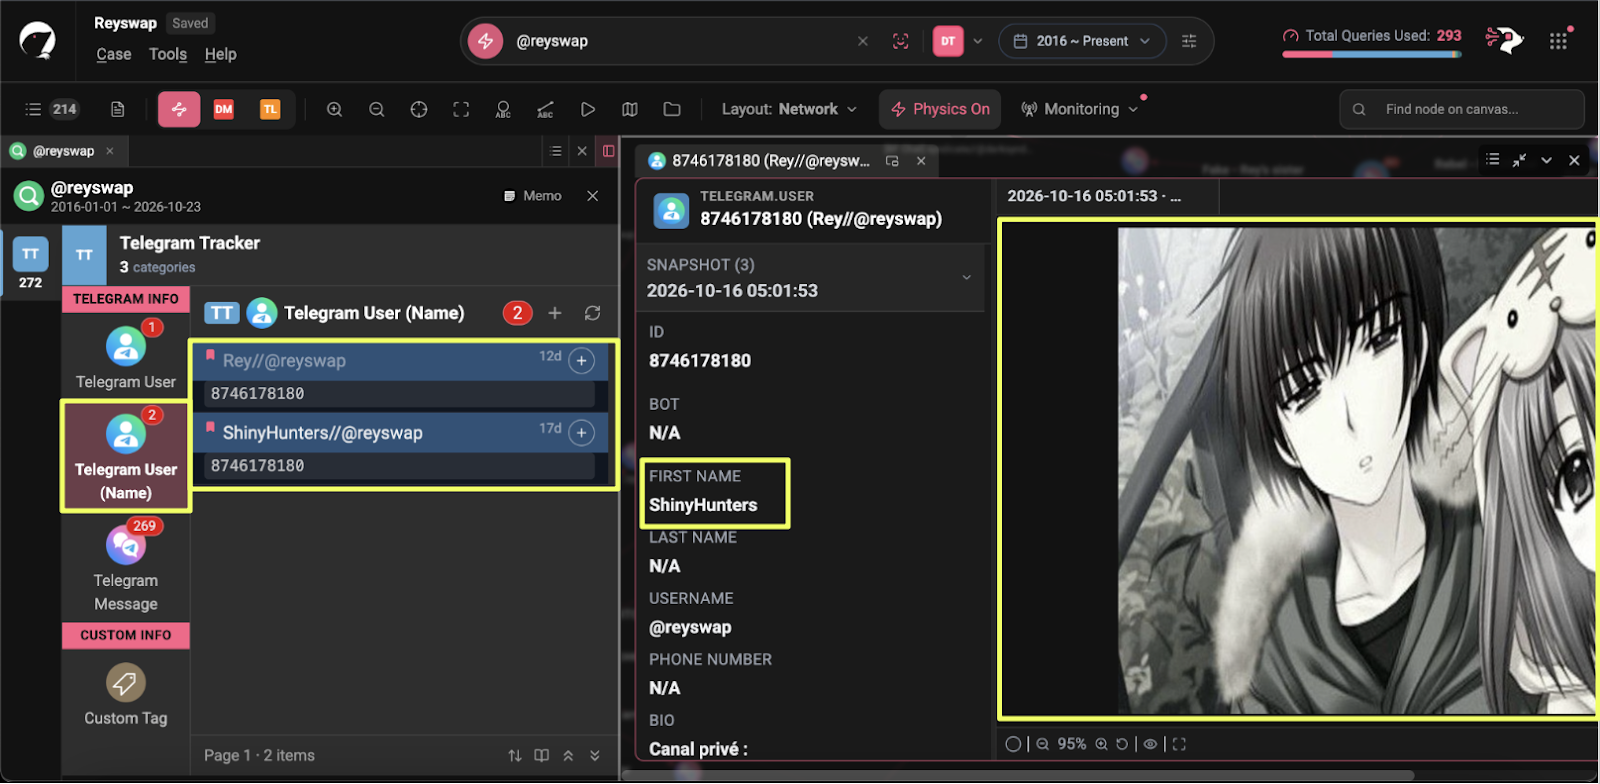
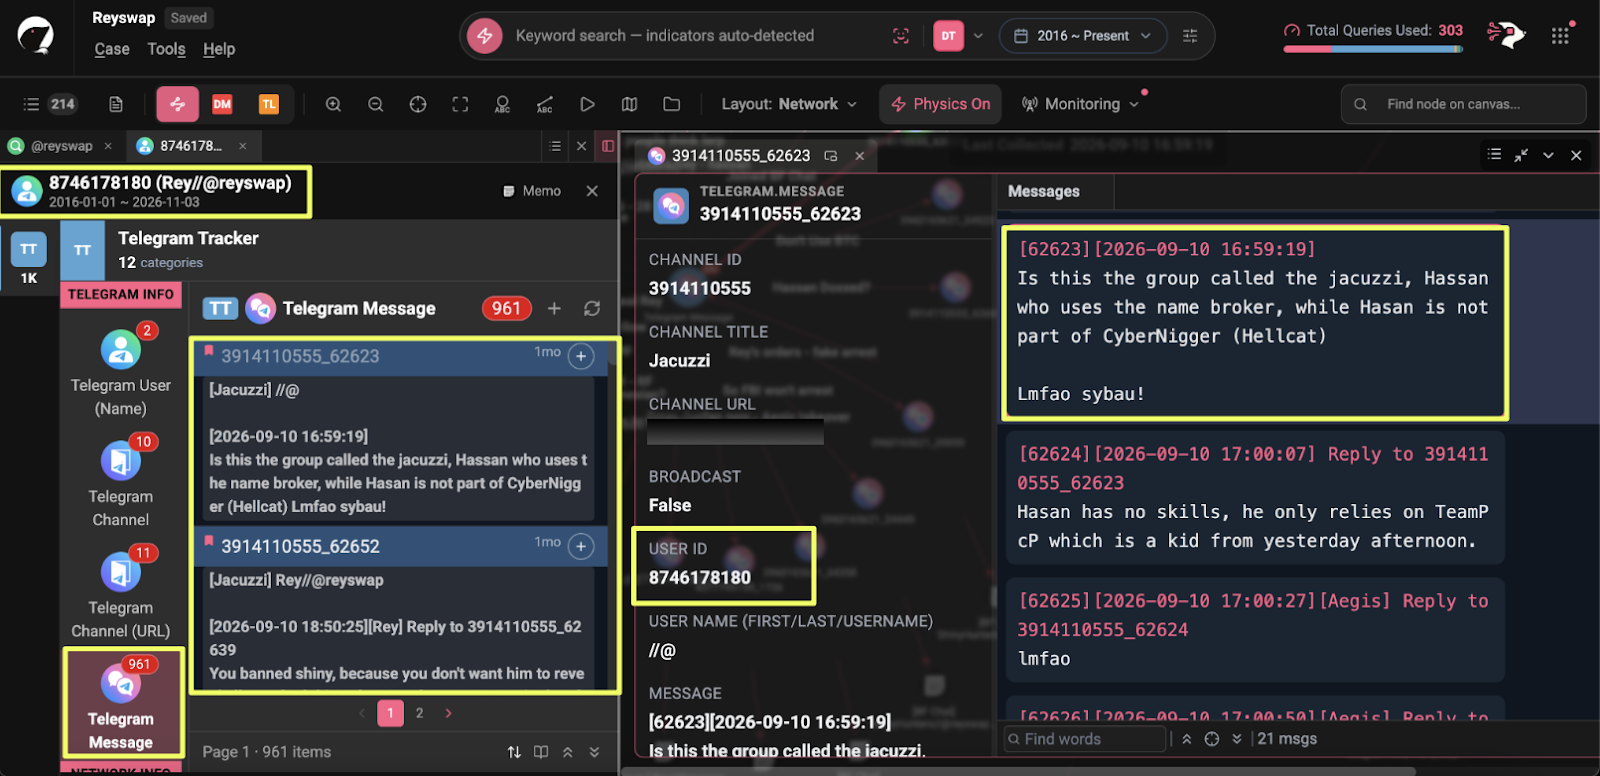
We first checked @reyswap through StealthMole's Telegram Tracker, which resolved the handle to a single Telegram user and showed the channels in which it had been active.
- Telegram user ID: 8746178180
- Username: @reyswap
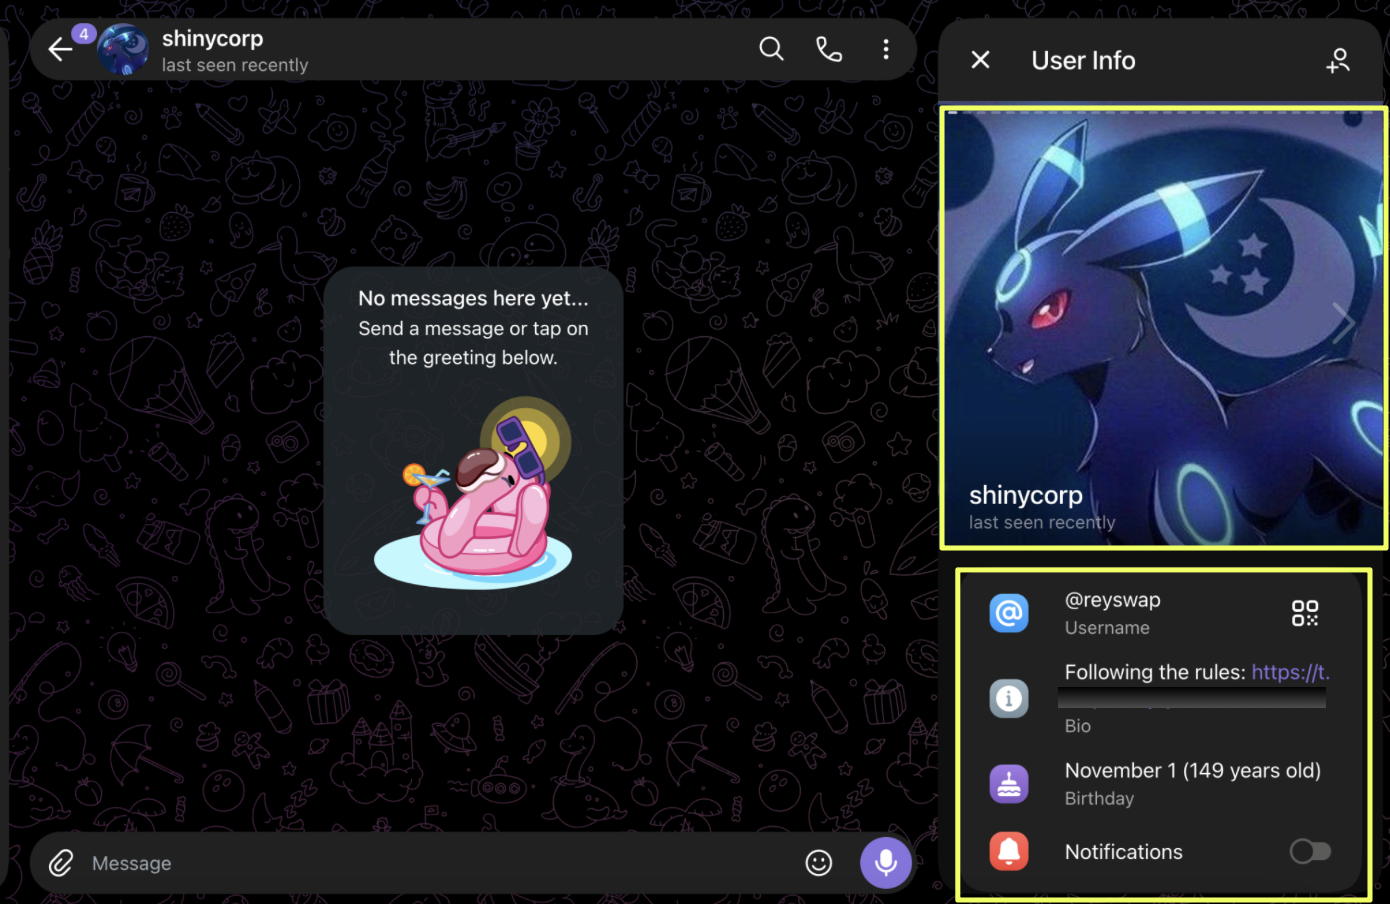
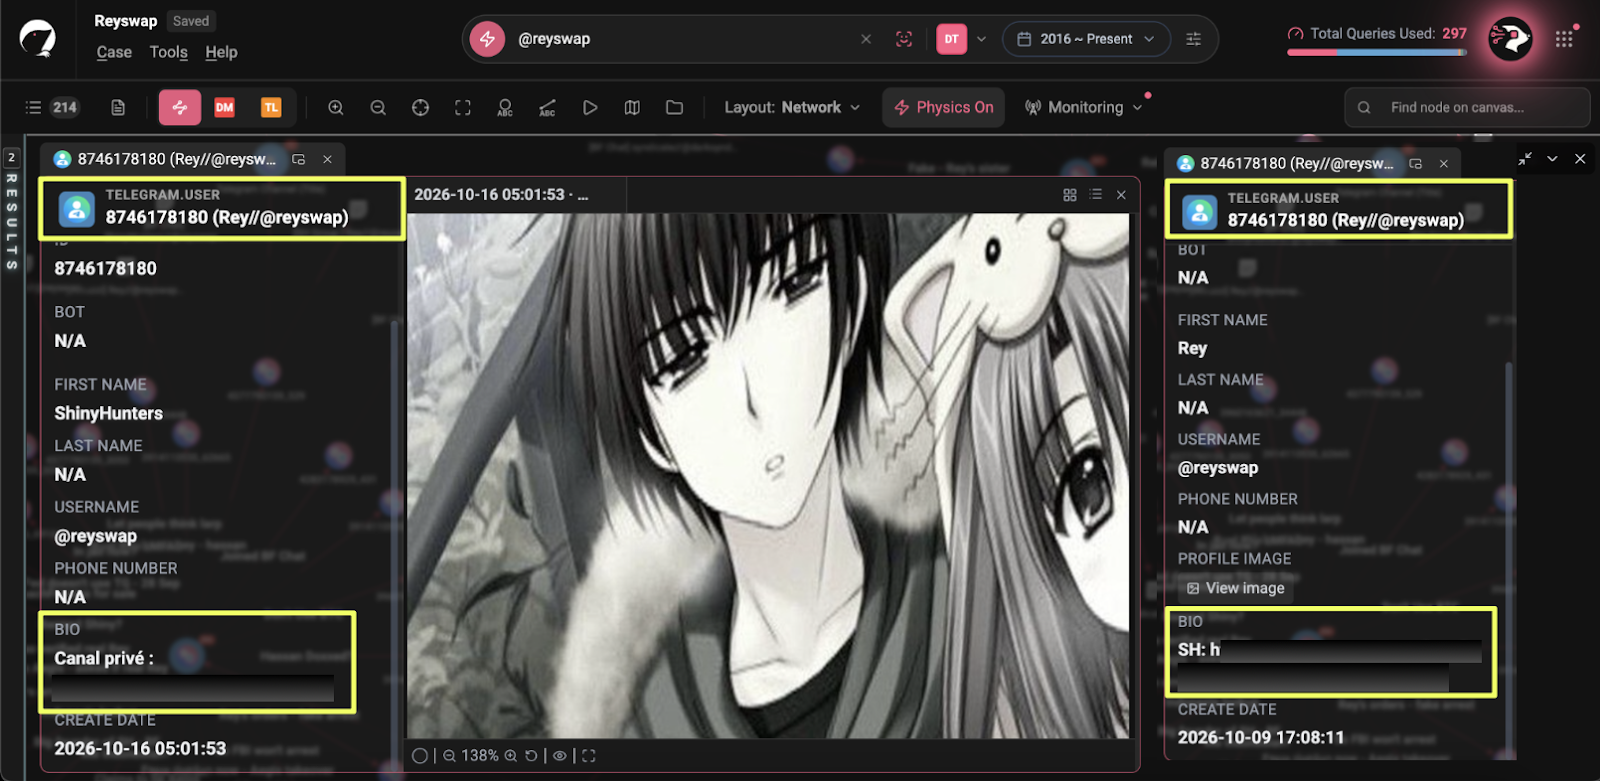
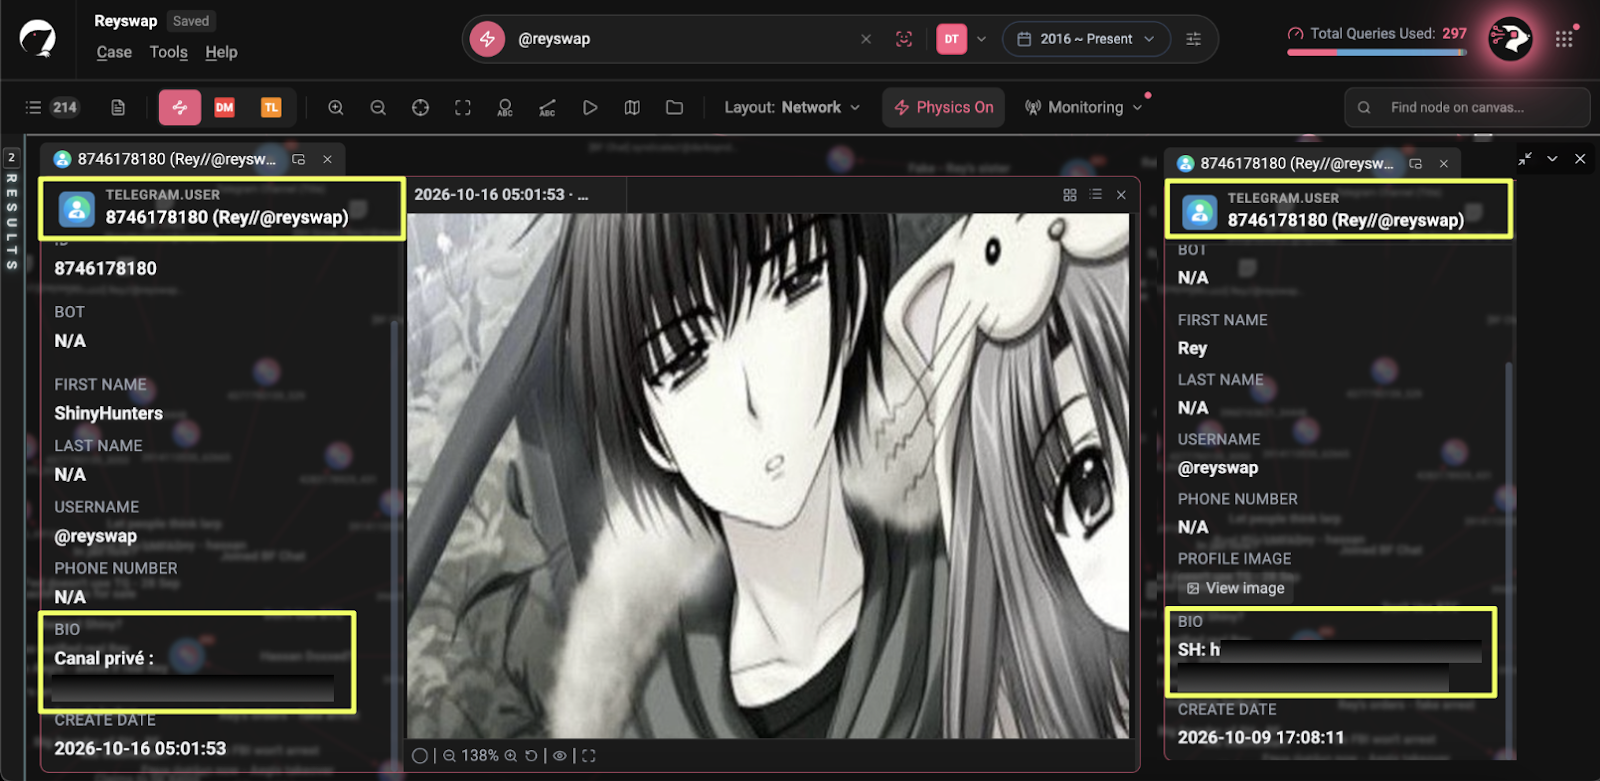
The account's profile history provided the first indication that something was not right. StealthMole had three snapshots of the profile, showing changes to its name, photo and bio over the following weeks:
- 10 September 2026: First name listed as "Rey", with no bio.
- 9 October 2026: A profile photo had been added, along with a bio linking to a ShinyHunters channel and a Pastebin PGP key: https://pastebin.com/J0*****q
- 16 October 2026: The first name had changed to "ShinyHunters", and the bio now included a French-language reference to a private channel: https://t.me/+jW***M9
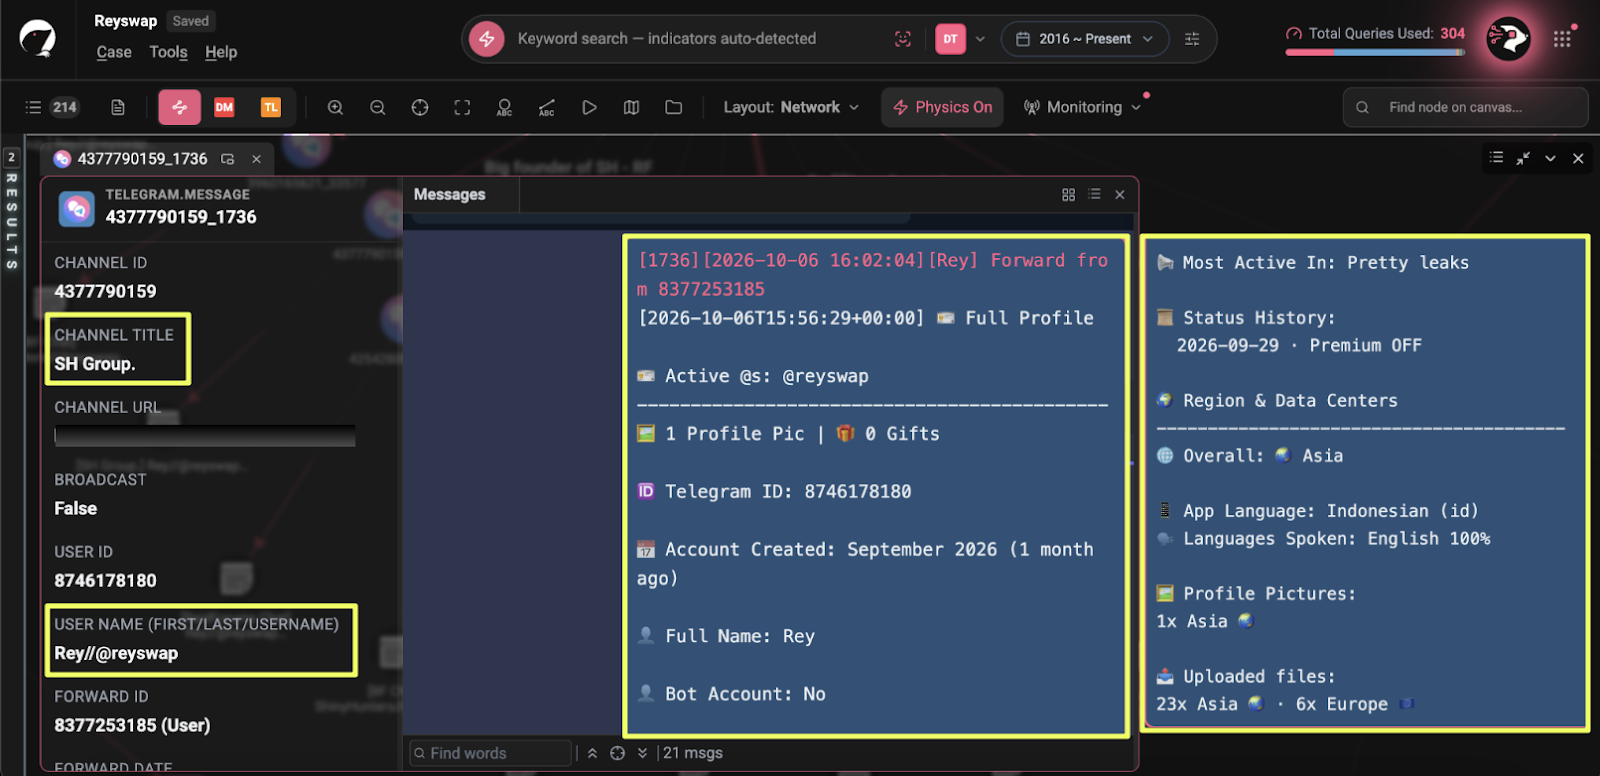
The account also appeared to be relatively new. Its earliest recorded activity was a message in the Jacuzzi chat on 10 September 2026, where it attacked a broker known as HasanBroker. On 6 October, @reyswap forwarded the result of a Telegram lookup bot into its group. The bot reported: "Account Created: September 2026 (1 month ago)".
This raised an important question about the account's claim to be Rey. Public reporting by KELA and KrebsOnSecurity had already documented Rey's activity under the alias Hikki-Chan since at least 2024. He had also been associated with the Hellcat ransomware leak site, the last incarnation of BreachForums and, by 2025, the administration of the Scattered LAPSUS$ Hunters Telegram channel. The September 2026 creation date did not match that established history. It did not rule out the possibility that Rey had opened a new account, but it meant that @reyswap could not be treated as one of his previously established accounts.
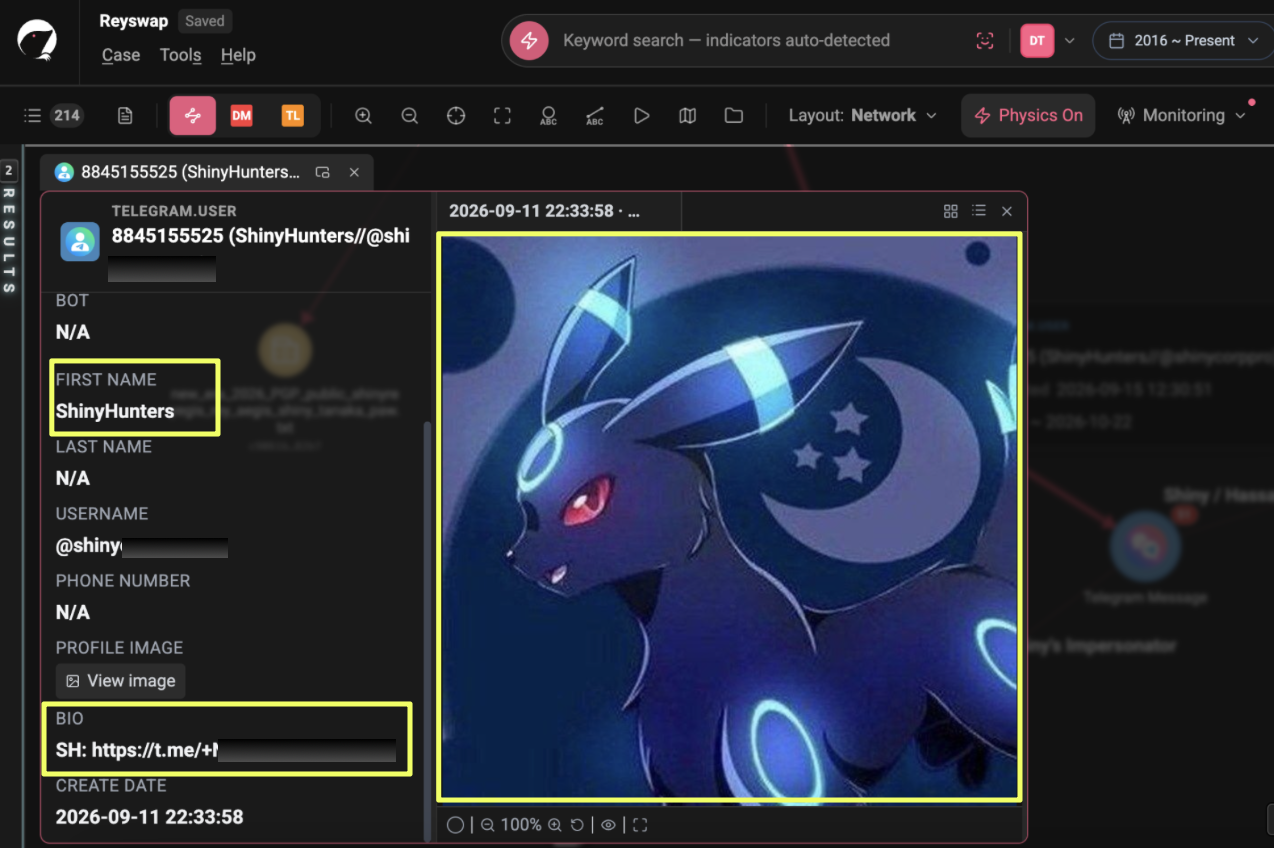
The next useful lead came from the same Jacuzzi exchange. Another account, @shinycorppro, joined the conversation to support @reyswap and presented itself as part of ShinyHunters. We followed this account through StealthMole and examined the channels it promoted to identify the infrastructure operating alongside @reyswap.

Building a ShinyHunters Front Before the Arrest
The first indication of how @reyswap was presenting itself came from the Jacuzzi chat on 10 September 2026. At 16:59 UTC, the account posted that HasanBroker was not part of Hellcat. Sixteen minutes later, another account, @shiny*****o, joined the exchange and replied, "What Rey said was true." HasanBroker banned @shiny******o from the chat a minute later. Over the following hour, @reyswap, now using the display name "Rey", continued the argument, calling HasanBroker "a fake broker" and claiming that he had been doxed.
- @shiny*****o
- Telegram user ID: 8845155525
- Display name: ShinyHunters
- HasanBroker: @ha*******r

The dispute continued beyond the initial exchange. The following evening, another Jacuzzi member, blewdup, asked HasanBroker whether he remembered banning "some fake shiny hunters named shinycorppro". On 12 September, @shiny******o responded in the DarkForums chat. It claimed that HasanBroker "was talking to the shiny impersonator not us" and directed users to verify the account using the PGP key pinned in its channel.

That channel became the next point of investigation. The bio of @shiny*****o linked to a Telegram channel titled ShinyHunters, which we examined through StealthMole's Telegram Tracker.
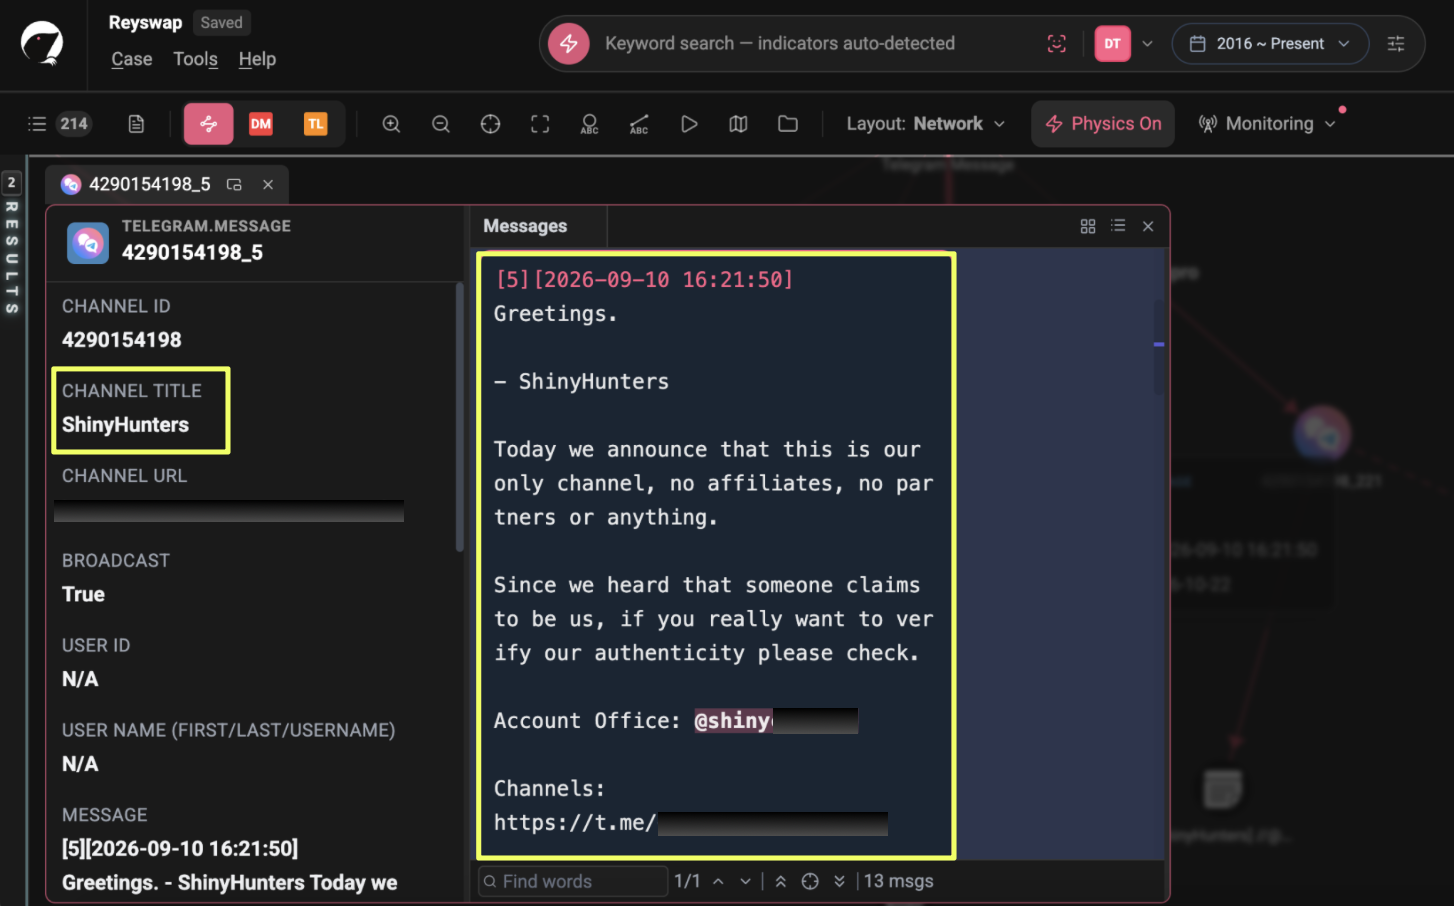
- Channel ID: 4290154198
- Title: ShinyHunters
- Invite link: https://t.me/+Nq1**********Nl
The channel's first captured post was published on 10 September at 16:21 UTC, before either account appeared in the Jacuzzi exchange. It stated: "this is our only channel, no affiliates, no partners or anything. Since we heard that someone claims to be us..." The message was signed shinyreyegis, combining the names Shiny, Rey and Aegis. This was the first captured instance of the three names appearing together and it came roughly 40 minutes before @reyswap's first recorded message.
On 11 September, the channel pinned an "Official Announcement" introducing a new PGP key and a set of contact details. The accompanying key file used the same combination of names:
- Key file: new_era_2026_PGP_public_shinyreyegis_rey_aegis_shiny_tanaka_paw.txt
- Key user ID: ShinyHunters <vin*********a@pokemon.com>
- Key creation date: 9 September 2026, 19:31 UTC
- Account Office: @shiny*******o
- Email 1: shiny*******p@proton.me
- Email 2: shiny****p@onionmail.com
- Email 3: sh1ny*******s@tuta.io
- XMPP: shiny********s@xmpp.jp
- Session ID: 0501d**********************************************6d7b
- Onion: shnyh********************************************read.onion
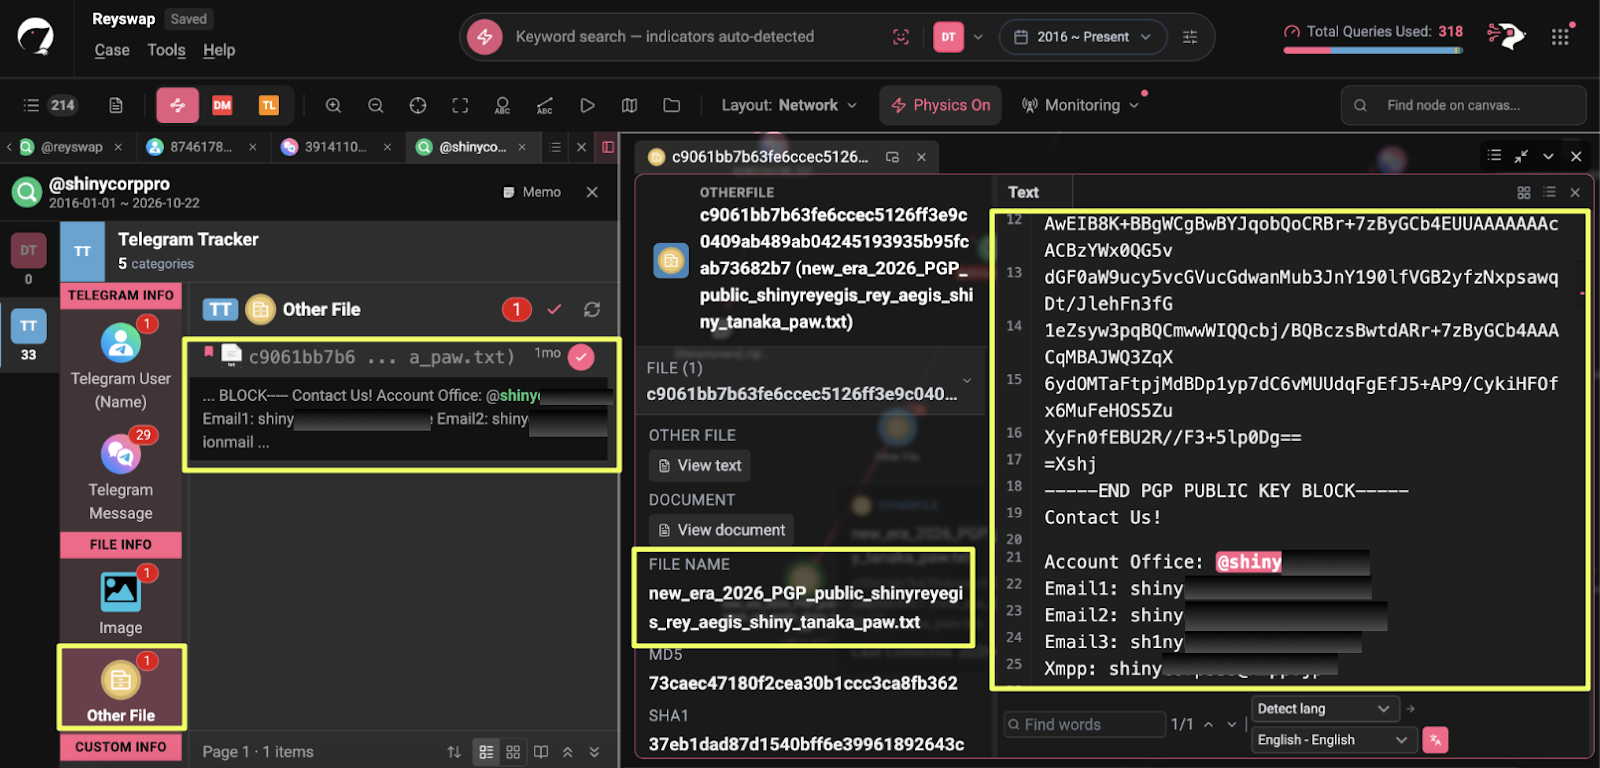
The use of a new PGP key is worth examining against the group's earlier verification practices. During our 2025 investigation into Scattered LAPSUS$ Hunters, an account defending the original channels directed users to verify anyone claiming to represent ShinyHunters against the archived RaidForums PGP key. The September 2026 channel instead announced that its previous key had been "renewed and replaced", asking users to rely on a key created just two days earlier. The new key could verify control of that key, but it did not establish continuity with the original ShinyHunters operators.
There is also an issue with the identity information entered in the key. Its user ID uses vin******a@pokemon.com. Vinny Troia is a security researcher who has investigated ShinyHunters, while the Pokémon reference is associated with the name ShinyHunters itself. The combination appears deliberate, but it does not establish any connection between Troia and the key holder. PGP user IDs are entered by whoever generates the key and are not independently verified.
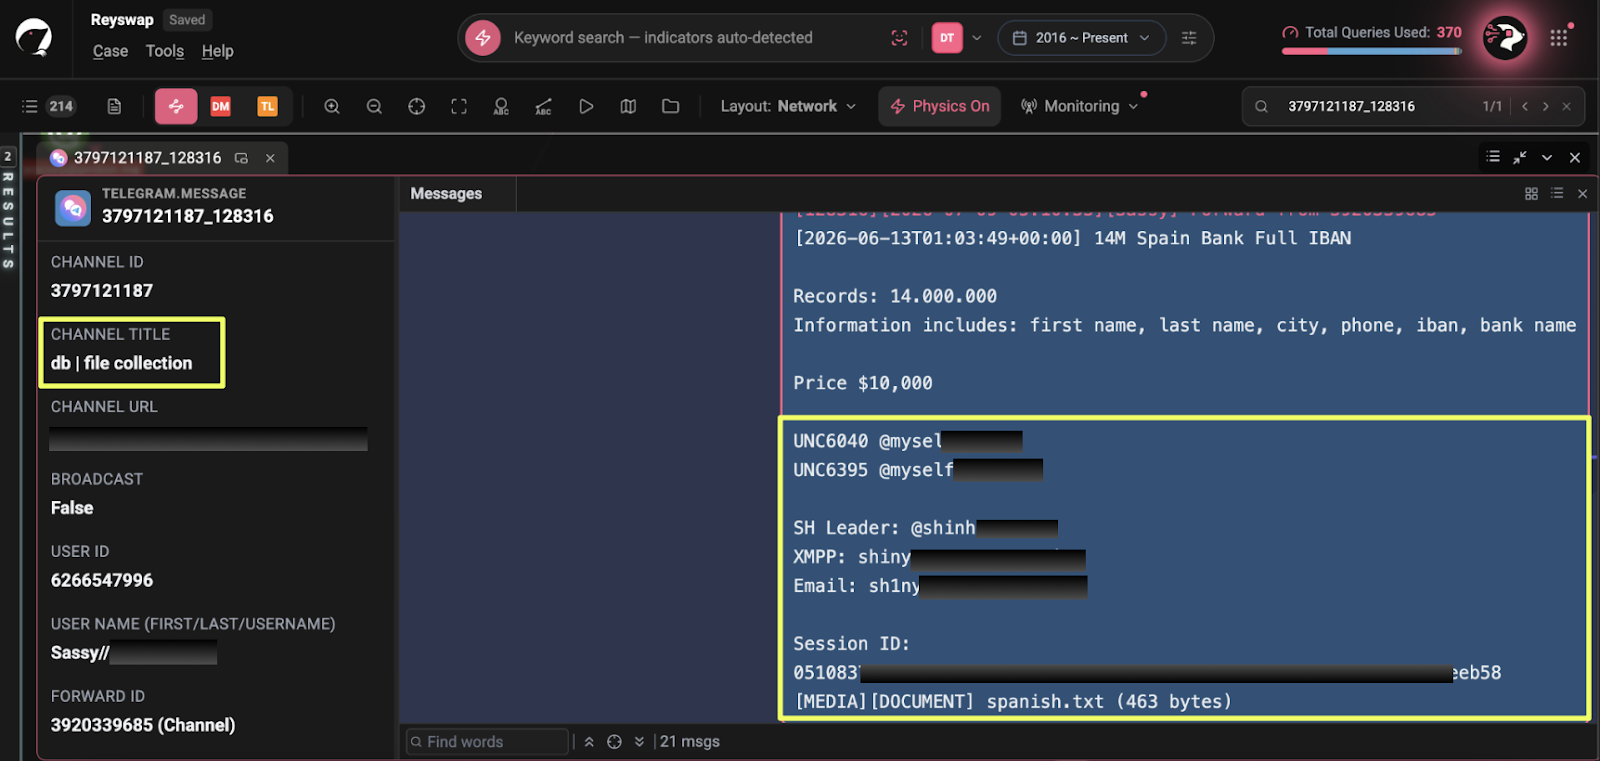
A further lead came from the contact details. StealthMole's Telegram Tracker surfaced the same Tuta email address and XMPP account in a sale post published on 13 June 2026, around three months before @reyswap appeared. That post used a different Session ID and identified another account as the "SH Leader".
- SH Leader: @shin********s
- Session ID: 051083********************************************5eeb58
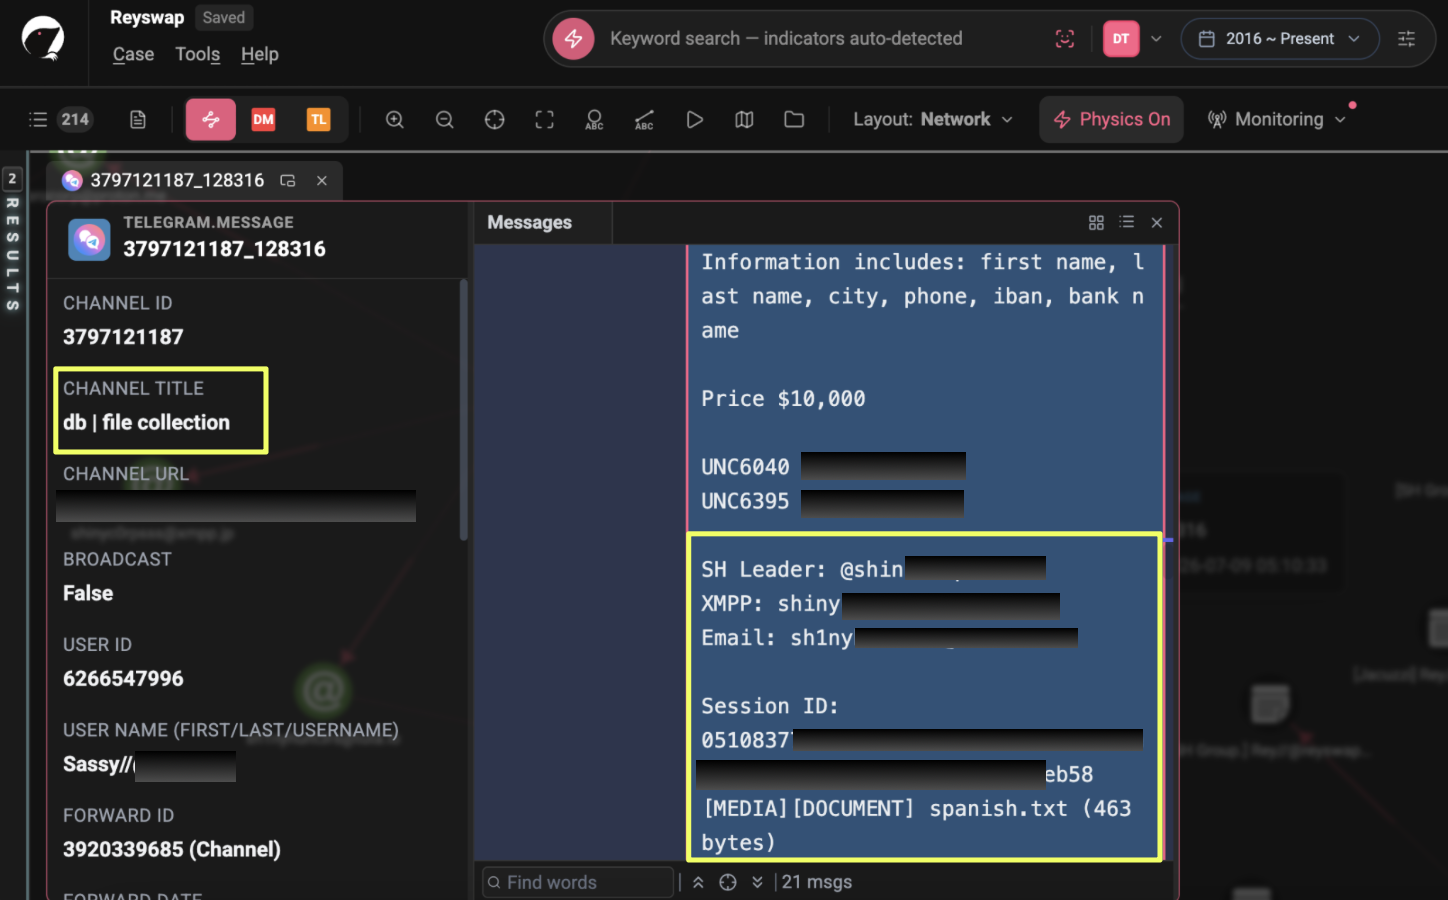
On 14 September, the ShinyHunters channel published both Session IDs together. It is labelled 0501da0b... as the "ShinyHunters" session and 05108377... as the "SLH" session. This showed that the contact infrastructure associated with @reyswap was already being used in June under a different account and leadership name. It therefore predated the September appearance of the Rey persona.

The channel also continued publishing messages attributed to Rey. On 12 September, it forwarded two such messages into its feed. In one, "Rey" denied ever being affiliated with HasanBroker. In the other, he stated: "I have never been on Telegram, and this is the first time I have been active again with you." When questioned, the account clarified that it had never claimed to be the founder, only "a part of the ShinyHunters group".
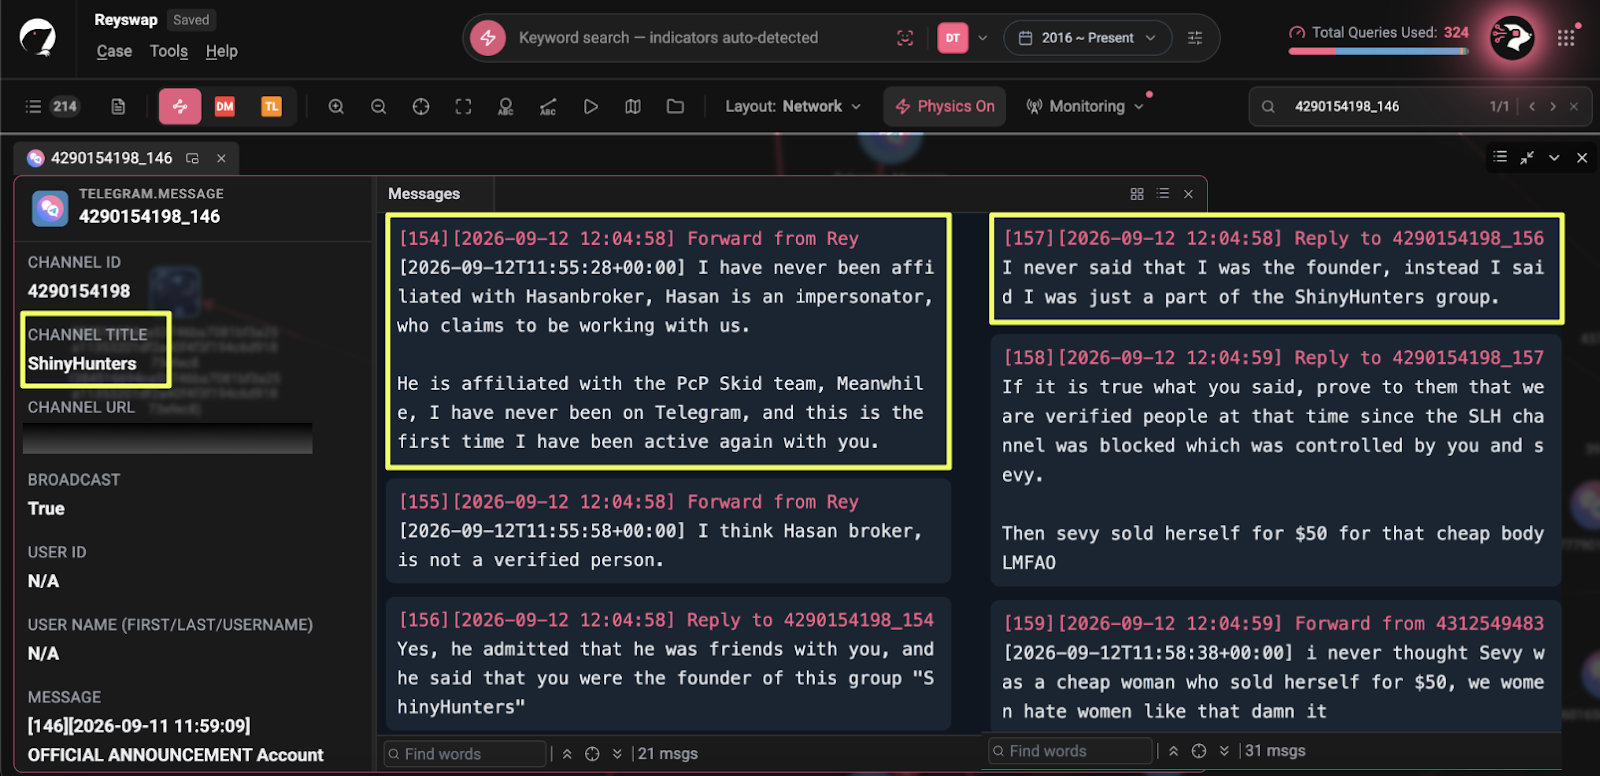
This statement did not match the publicly documented Telegram history of the original Rey, whose activity and administrator role in Scattered LAPSUS$ Hunters were already established by 2025. The account was presenting itself as a returning member while denying a history that was already associated with the person it claimed to represent.
The next development came on 25 September, when a new Telegram channel was created. StealthMole's Telegram Tracker returned the following details:
- Channel ID: 4228181647
- Initial title: SH
- Title by 20 October: SHINY CORP
- Invite link: https://t.me/+jWm**************jM9
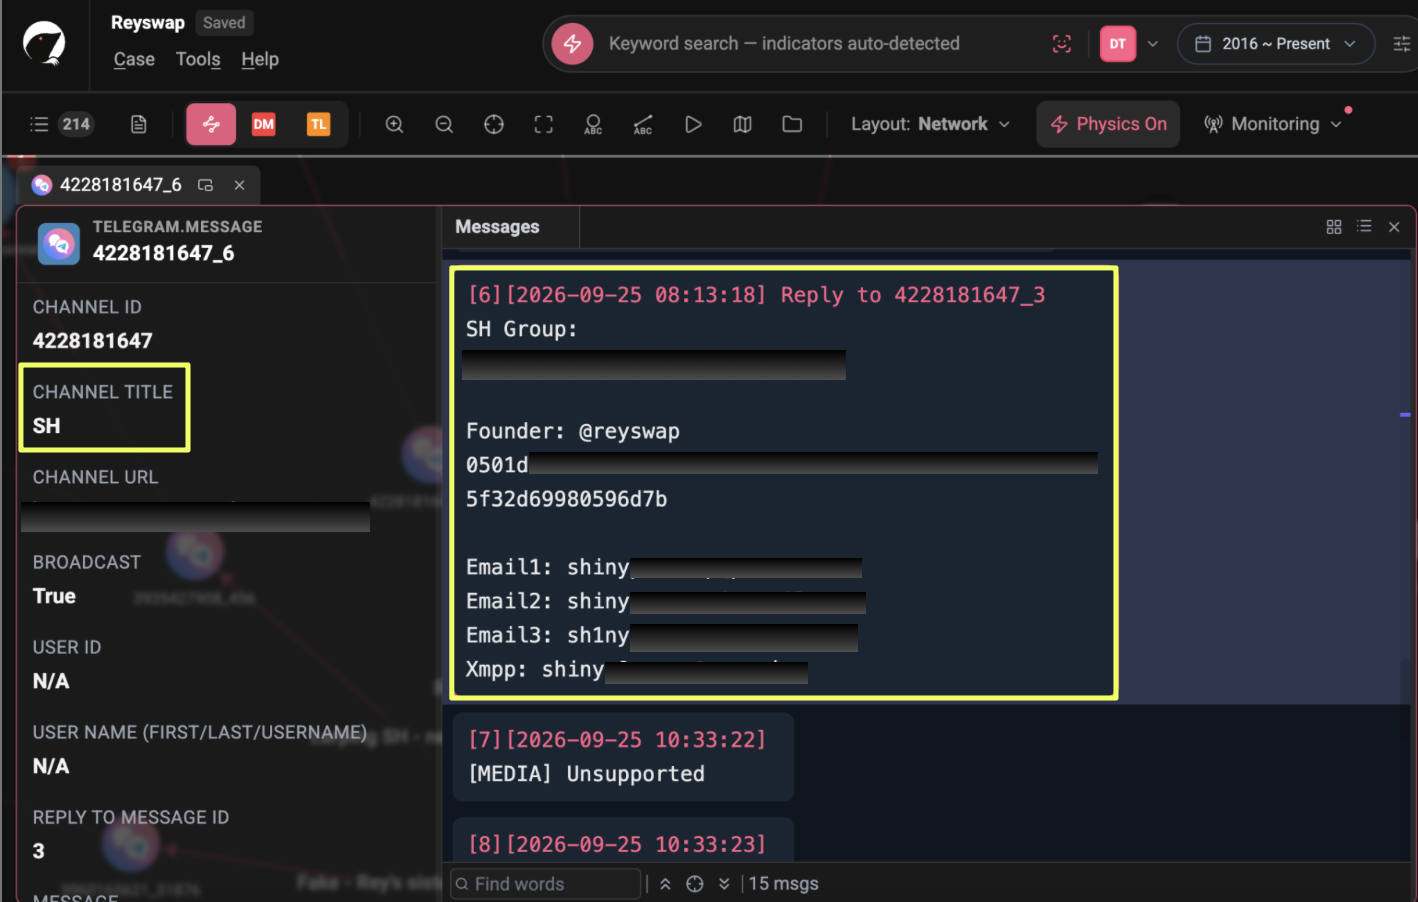
The channel's first announcement was posted at 08:09 UTC on 25 September. It opened with "i'm Rey - SH" and claimed that "our previous main Telegram channel has unfortunately been suspended following spam reports". Four minutes later, it linked to a companion discussion group and identified @reyswap as its founder.
- Founder: @reyswap
- SH Group: https://t.me/+9dx************GI1
- Group ID: 4377790159
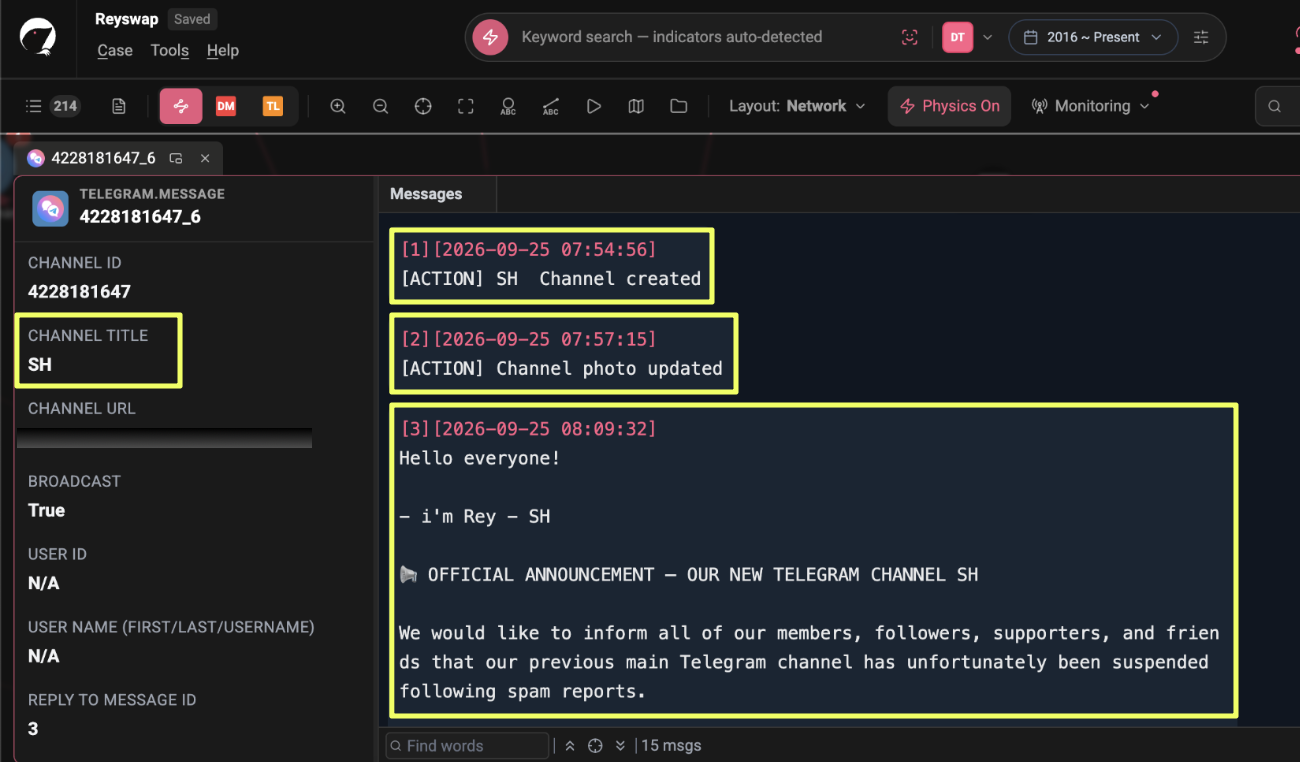
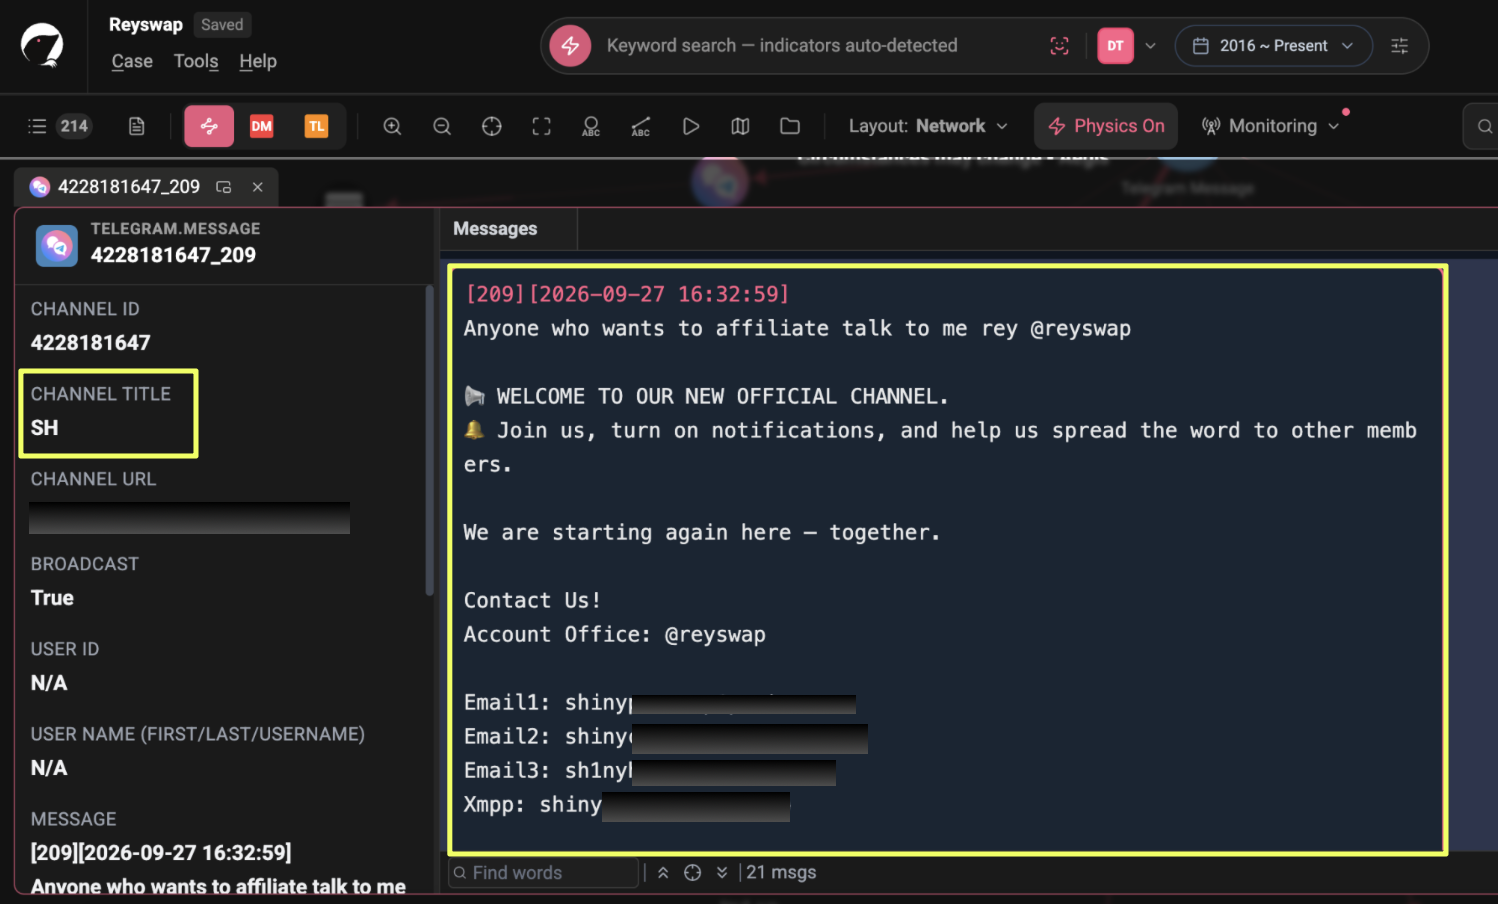
The new channel quickly became the main outlet for the persona's activities. Over the following five days, it published several data-sale listings, each using the same contact details and directing buyers to "Account Office: @reyswap". The listings included claims involving 153 million Canadian and US driver's licence records, Vercel access keys and source code, Credit Institute of Vietnam records, and data from the FBI jobs portal.
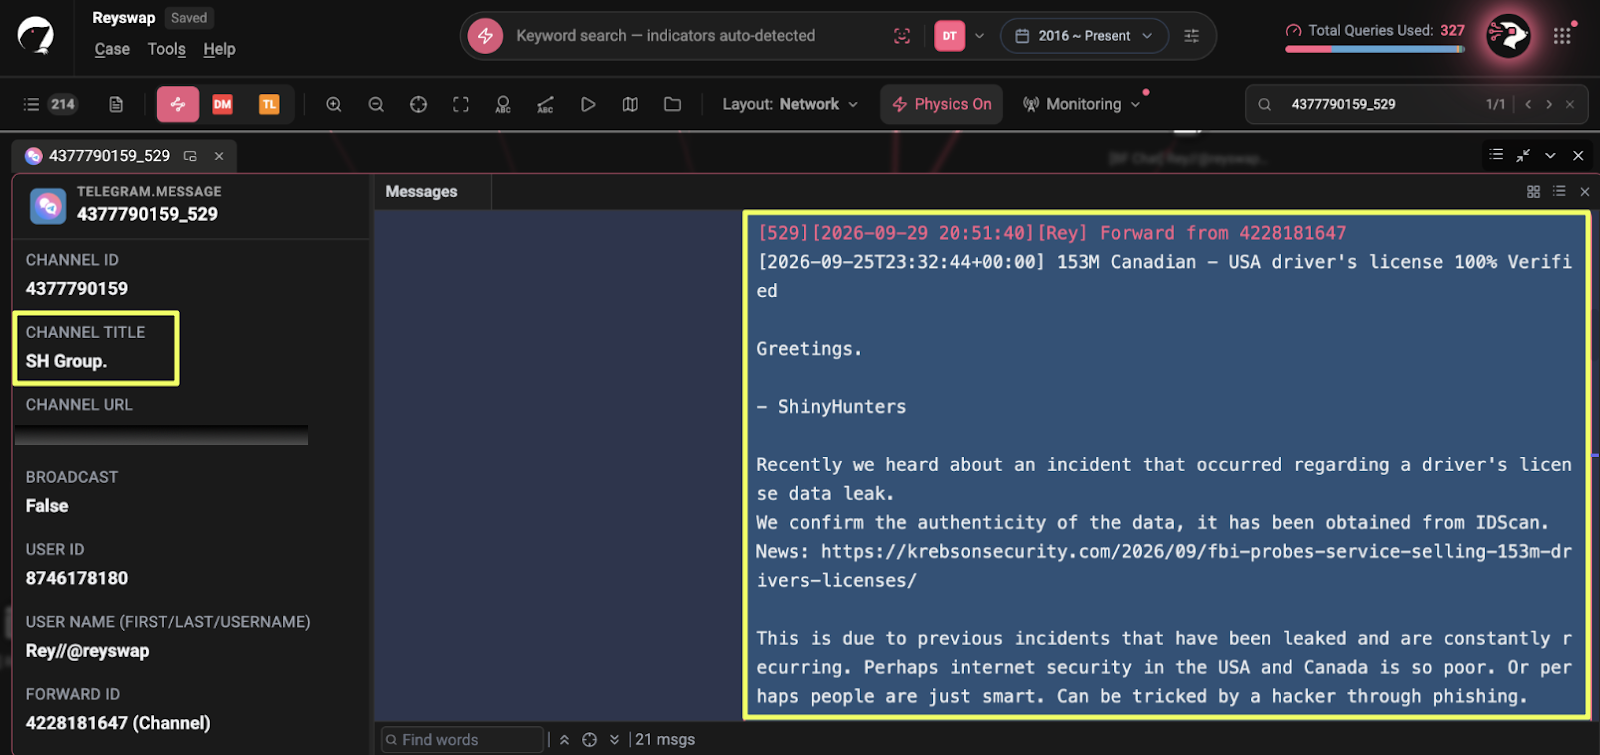
On 27 September, the channel also began recruiting affiliates, posting: "Anyone who wants to affiliate talk to me rey @reyswap". By the end of the month, @reyswap had become the central contact point for the ShinyHunters-branded operation, handling both its public identity and its data-sale activity.
29 September: The Arrest That Interrupted Nothing
According to sources cited by Reuters, Rey was detained by Jordanian authorities on 29 September 2026. This date became an important point in the investigation. If @reyswap was being operated by Rey himself, we would expect some change in activity following his detention, whether the account went silent or someone else took over. However, StealthMole's records show no such interruption.
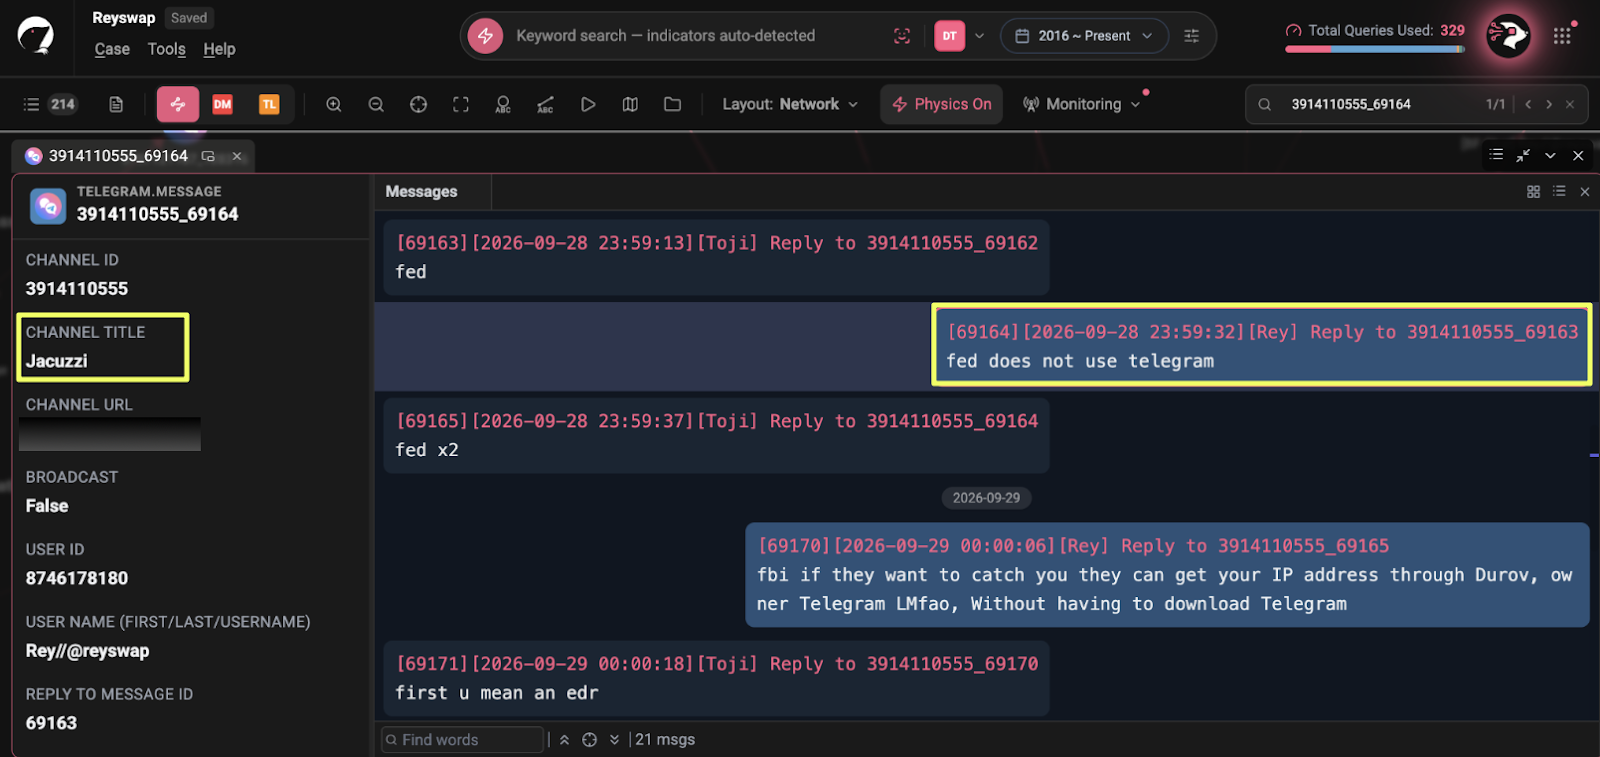
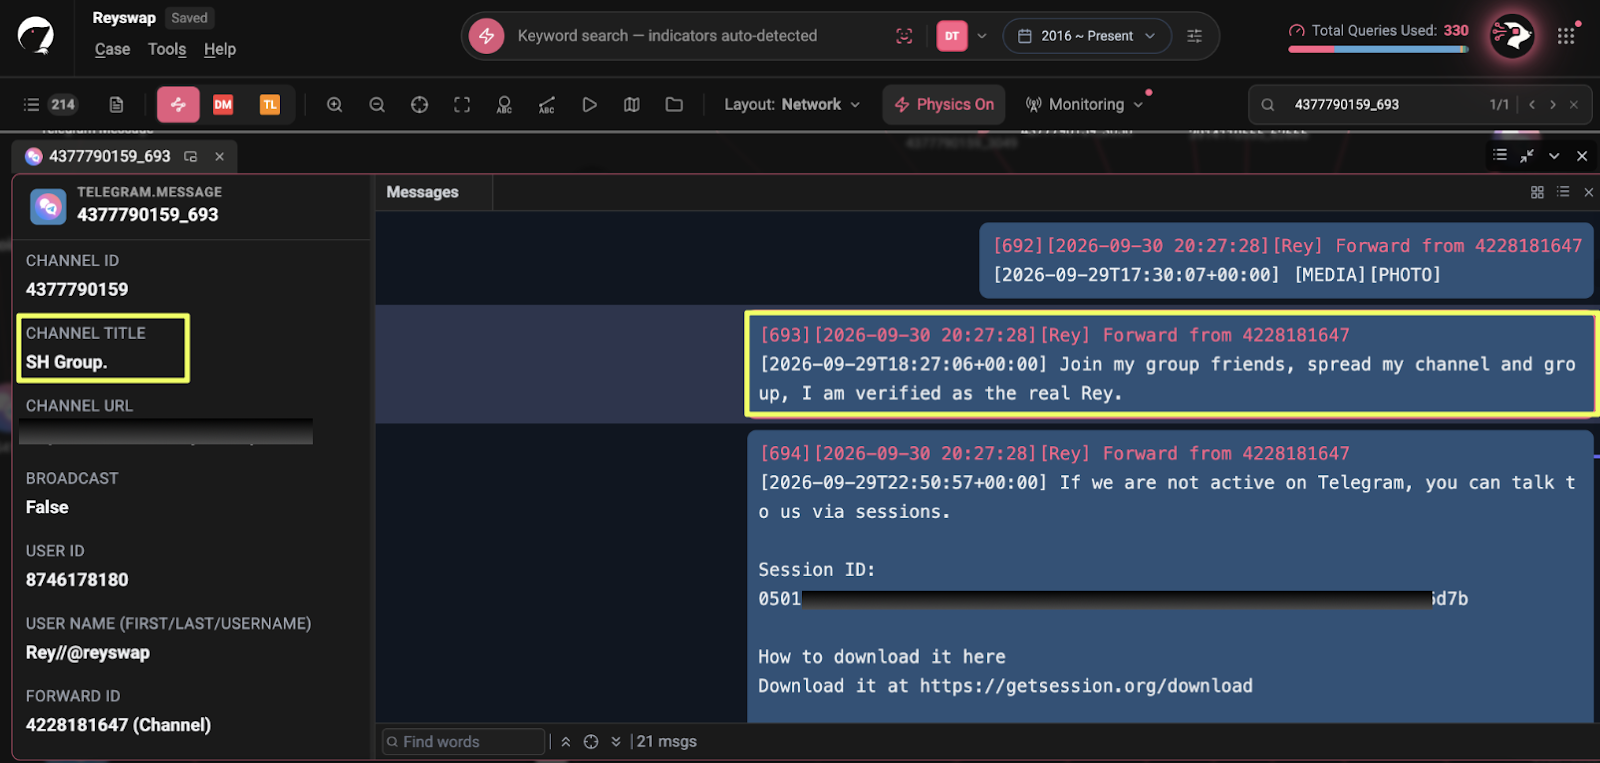
In the minutes around midnight on 28–29 September, @reyswap was active in the Jacuzzi chat discussing law enforcement and Telegram. It claimed that "fed does not use telegram" and that the FBI could obtain a user's IP address directly from Telegram's owner "without having to download Telegram". Later on 29 September, the account forwarded the SH channel's driver's licence listing into the SH Group. Another message from the same day encouraged members to promote its channels, stating: "Join my group friends, spread my channel and group, I am verified as the real Rey."
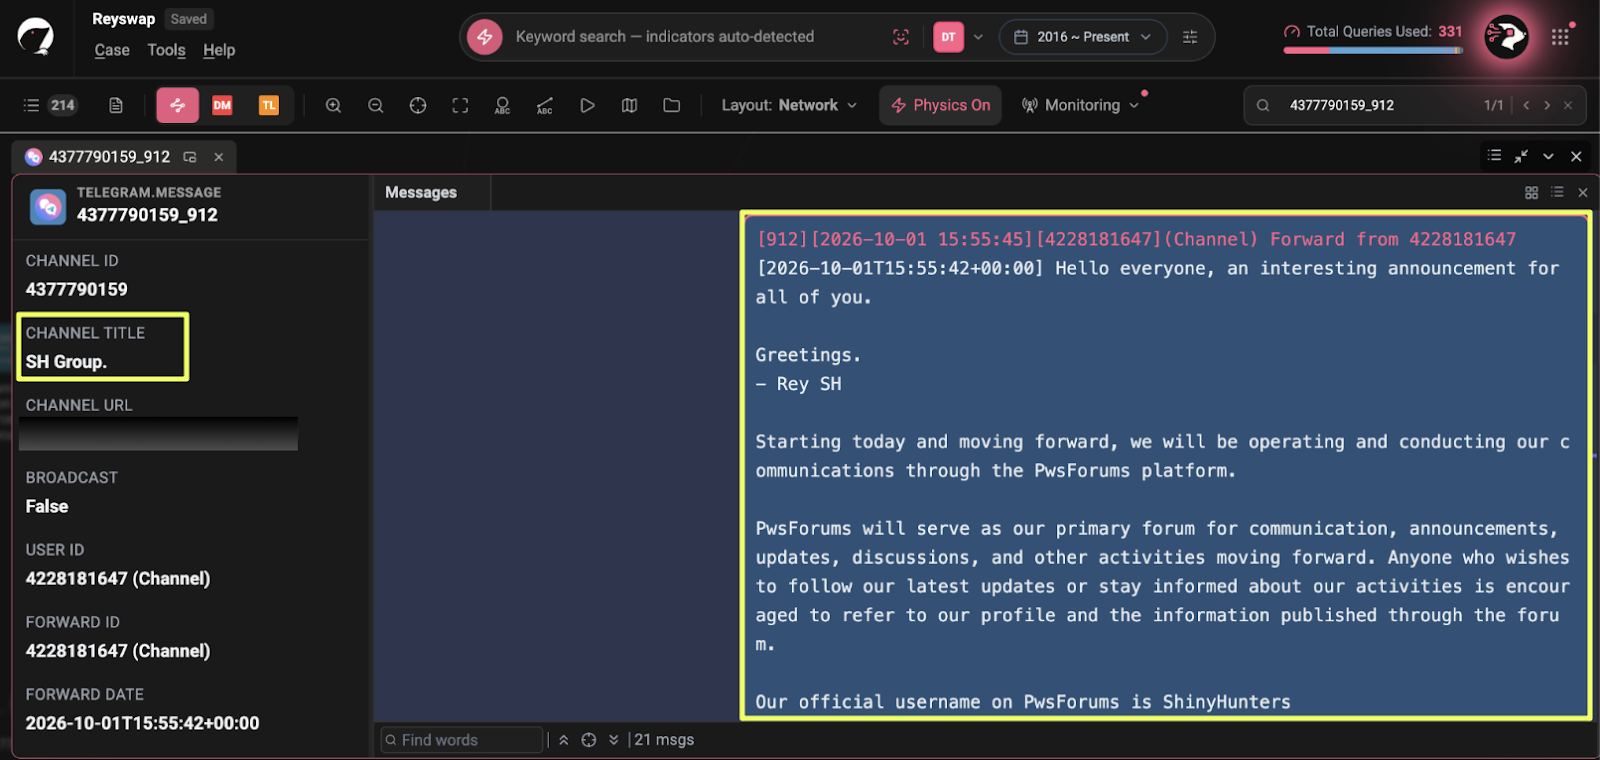
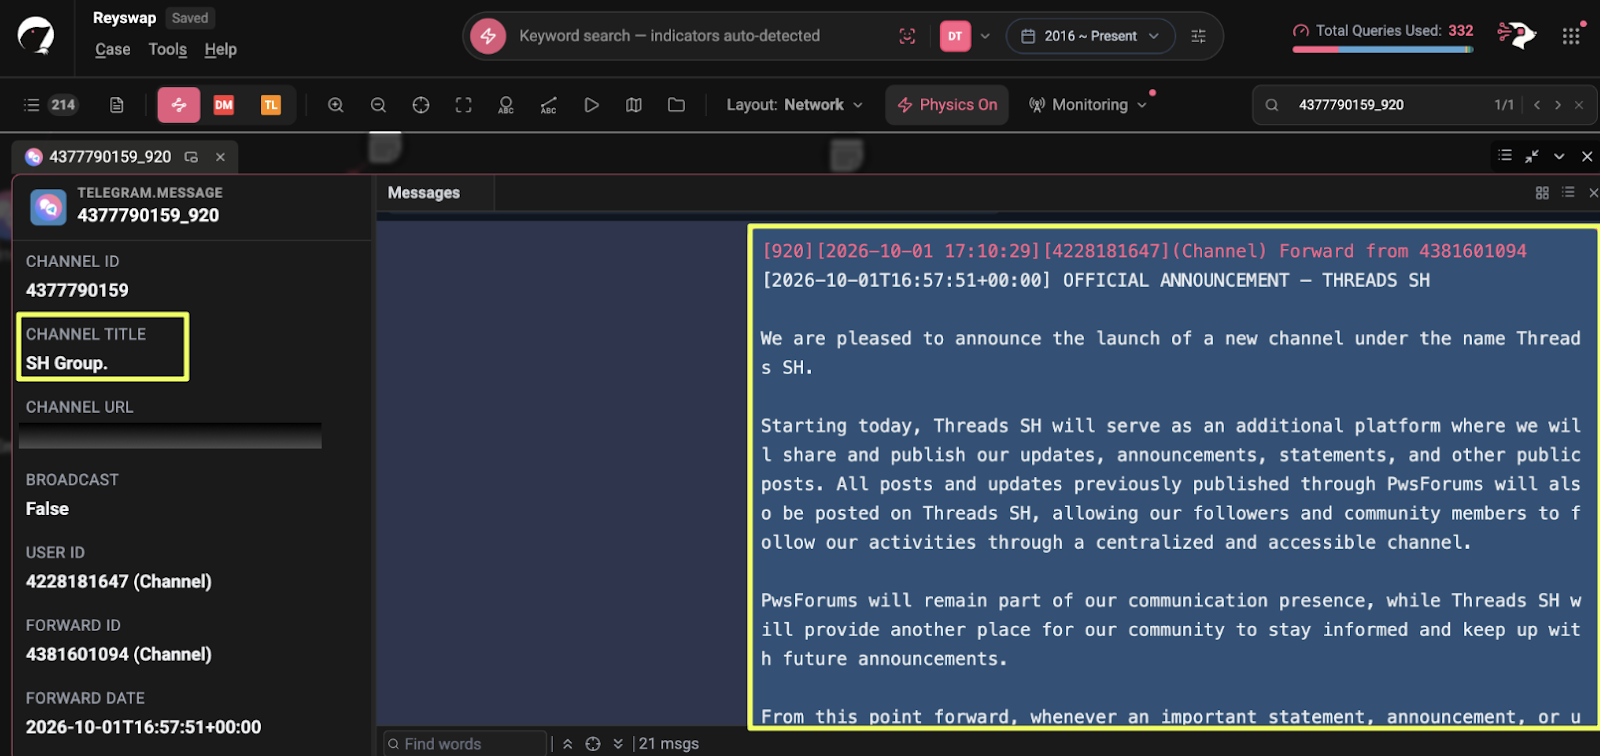
The activity continued over the following days. On 30 September, @reyswap forwarded a dozen listings from the SH channel into its group in a single burst. On 1 October, the channel announced that it would also operate on PwsForums under the username "ShinyHunters". It also launched a second Telegram channel called Threads SH.
StealthMole's Dark Web Tracker captured two PwsForums threads published that same day. Both used @reyswap as the Telegram contact:
- https://pwsforums.**/Thread-300+**********Vercel*********1059
- https://pwsforums.**/Thread-637M+ Celebrity Leak Week****1063
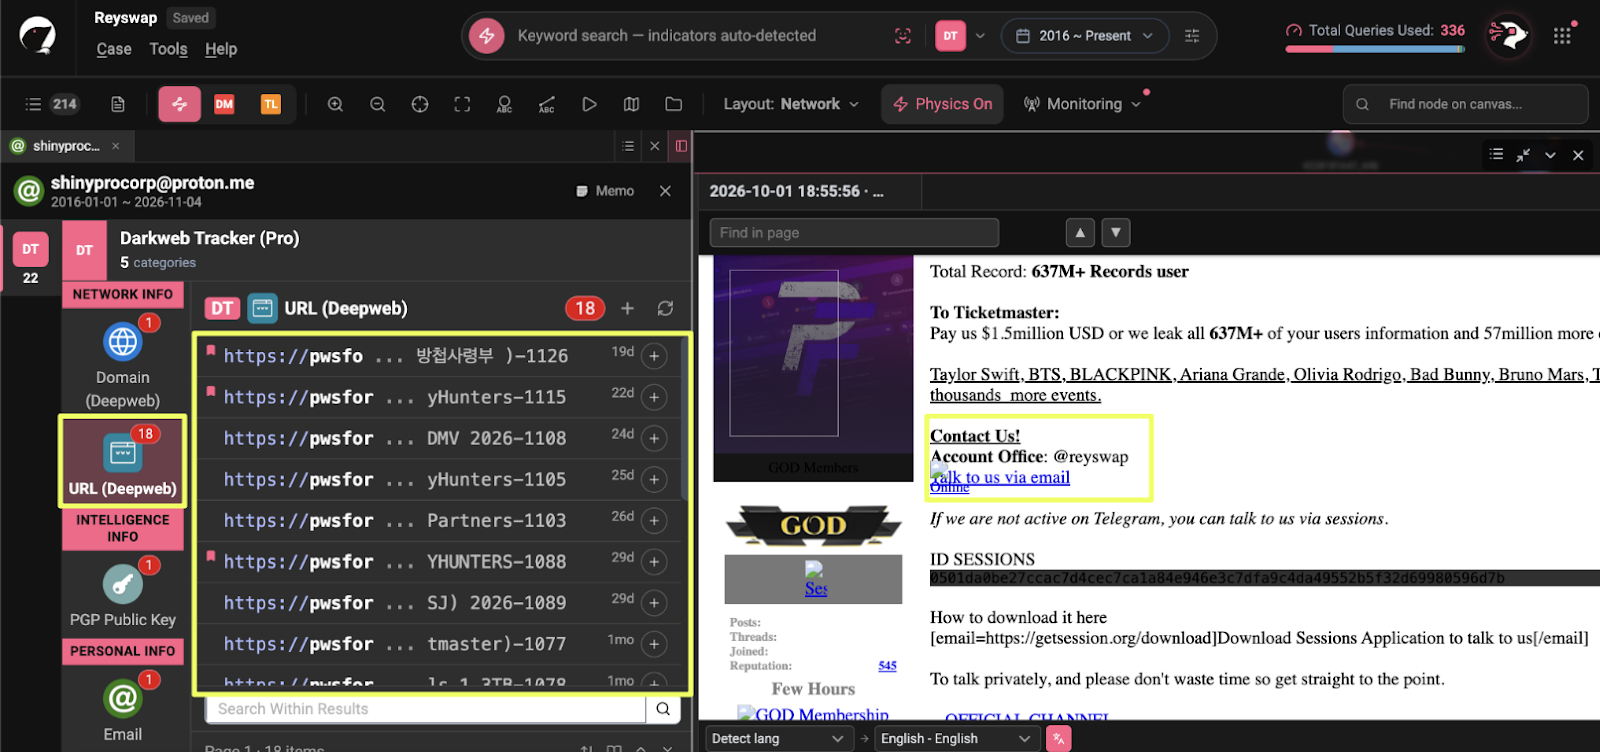
The Ticketmaster listing contained another detail relevant to the identity claim. Alongside a reported $1.5 million extortion demand, the post linked to Rey's old RaidForums PGP key and old Empire PGP key through the Wayback Machine. The account was therefore pointing buyers towards verification material associated with the original Rey. However, the listing did not include a signature made with either of those keys. Referencing archived keys is not the same as demonstrating control of them.
What stands out is the continuity of activity across 29 September. The same account continued posting in chats, promoting its channels, forwarding listings and directing buyers to its contact points. There was no visible break in its activity following the reported detention. This does not identify who was operating the account, but it adds to the evidence that @reyswap was not simply Rey's established Telegram identity under a new name.
Rey and Aegis: Two Names, One Account
The persona's identity changed again after news of Rey's detention became public. On 3 October, the ShinyHunters channel forwarded a message from an account using the name Aegis. Rather than distancing itself from Rey, the message claimed that both names belonged to the same person:
- This user is me Aegis, I don't use my alternate account, Rey and I are one in soul @reyswap
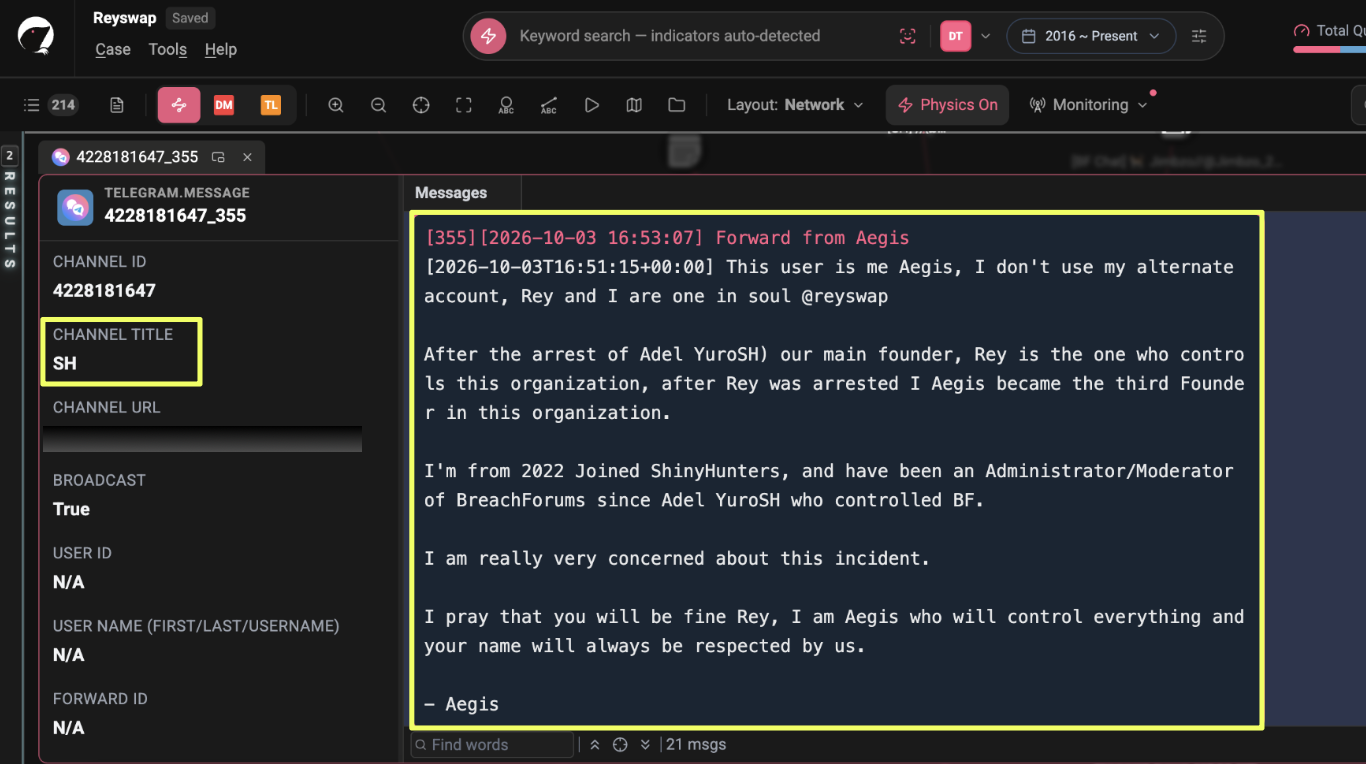
The post also introduced a new version of the group's leadership history. It claimed that Adel YuroSH had been the main founder, that Rey took over following Adel's arrest, and that Aegis was now the "third Founder" after Rey's detention. The account further claimed to have been part of ShinyHunters since 2022 and to have moderated BreachForums.
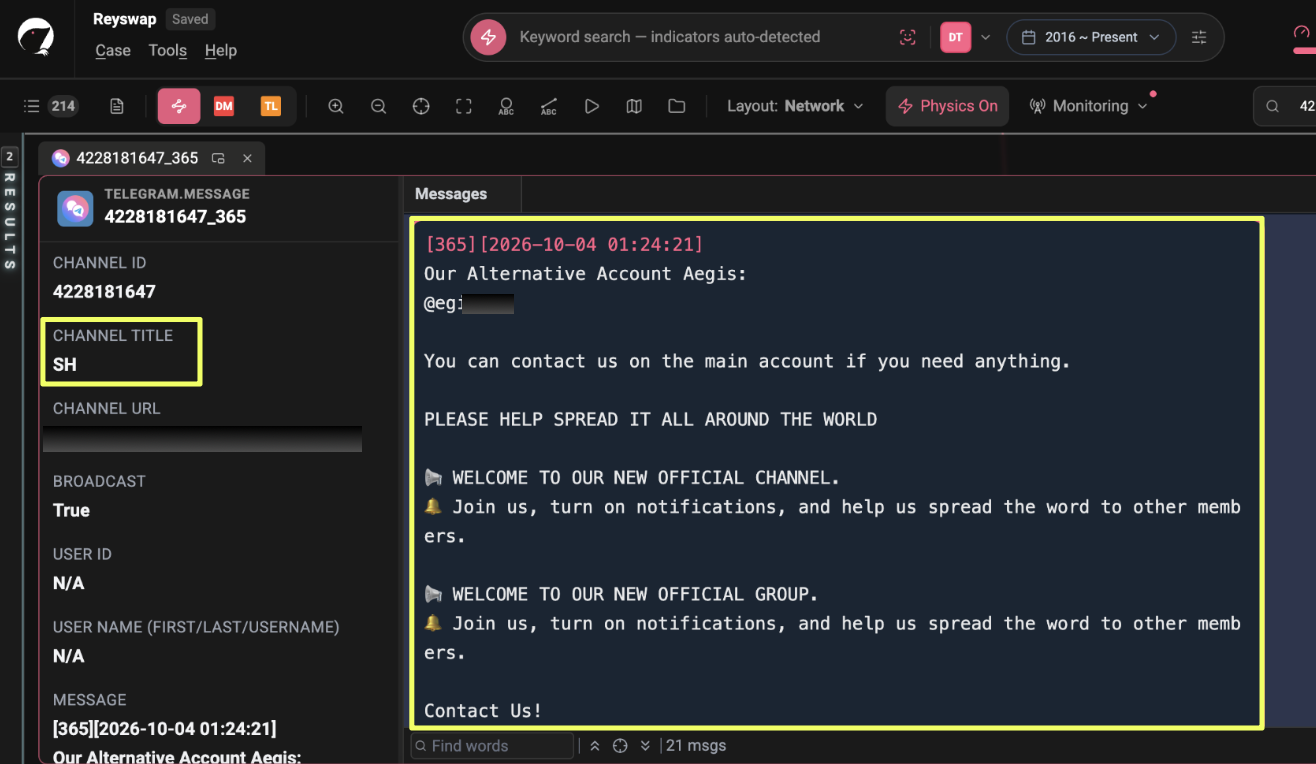
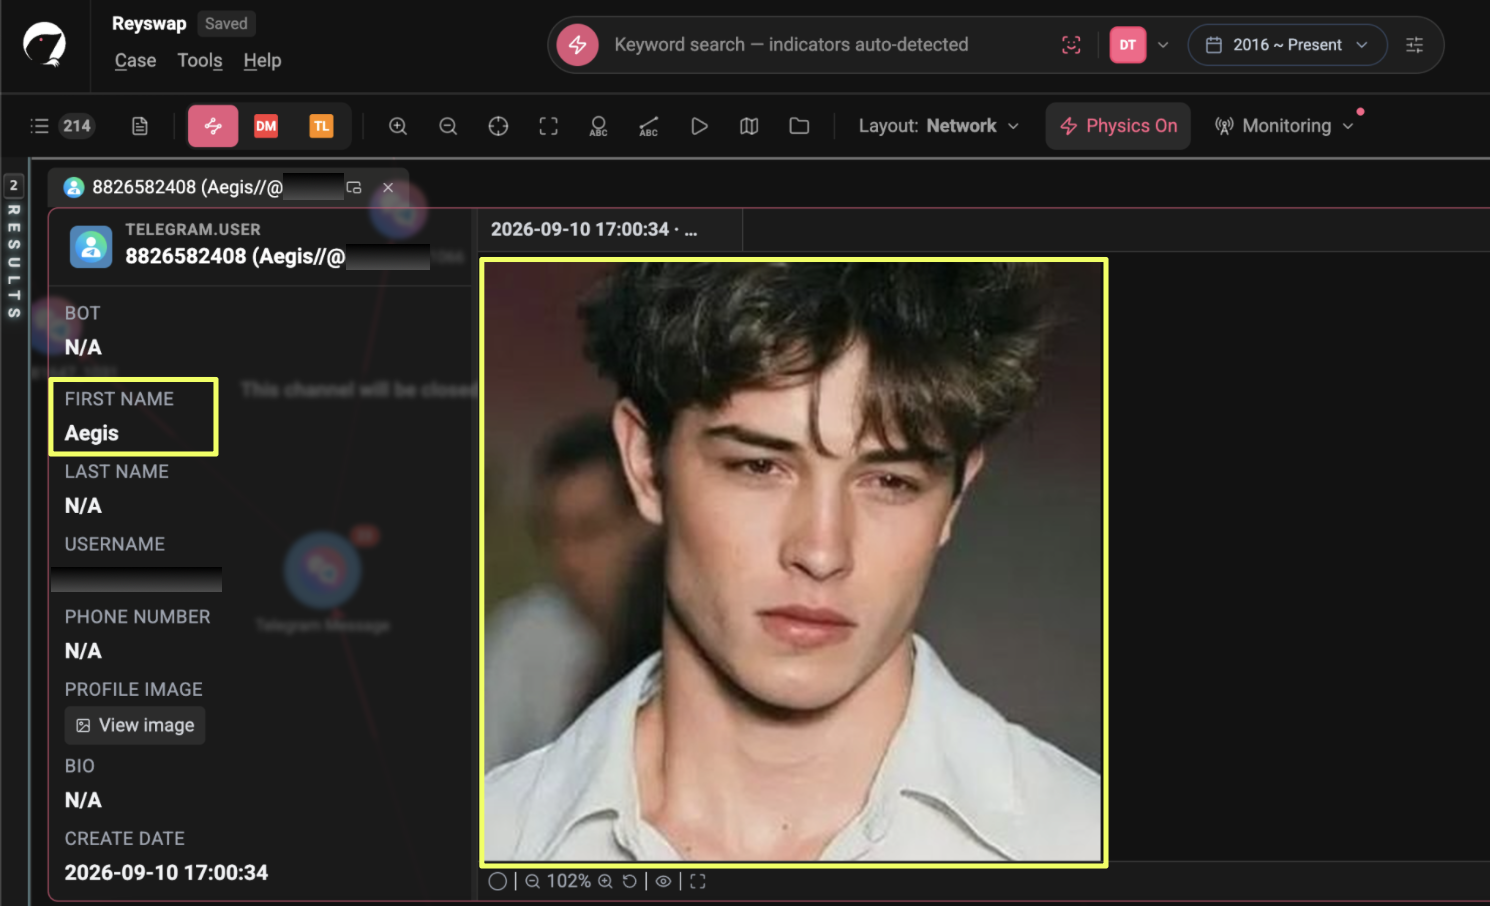
The following morning, the SH channel identified the alternate account as @egi****a. On 4 October, it published a formal "Statement from Aegis", stating that Rey had "reportedly been arrested in Jordan" and that Aegis would now "take responsibility for leading this organization".
- Alternate account: @egi****a
- Telegram user ID: 8826582408
- Display name: Aegis
StealthMole's Dark Web Tracker also captured the statement on PwsForums, where it was published by the "ShinyHunters" forum account. Despite announcing that Aegis would take over leadership, the statement ended with a contact block that still listed @reyswap as the Account Office.
- https://pwsforums.**/Thread-STATEMENT***AEGIS*SHINYHUNTERS-1088
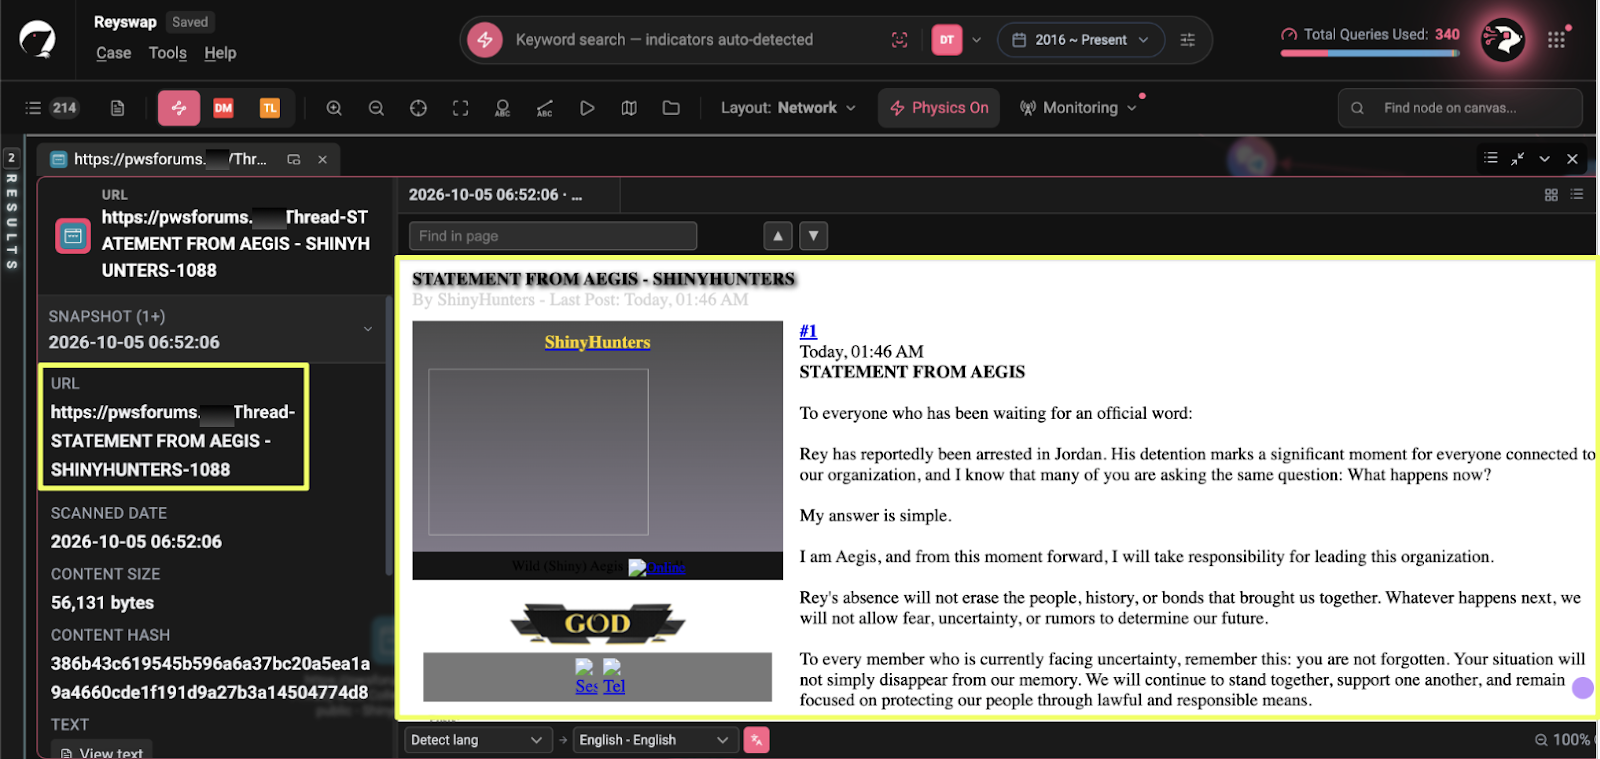
This created a clear contradiction. The statement announced Rey's arrest and introduced Aegis as the new leader, but continued directing users to the account that had been presenting itself as Rey. Messages from the same account made the overlap even clearer. Rather than maintaining two separate identities, @reyswap continued responding to both names.
- 4 October, SH Group: "I am Aegis, the great founder of ShinyHunters"
- 6 October, SH Group: When asked, "isn't this the real Rey? Because he is arrested????", @reyswap replied, "I am Aegis"
- 6 October, SH channel: "My original Telegram Aegis is this @reyswap"
- 10 October, BF Chat: "I'm from Jordan now, Aegis will be using this account soon"

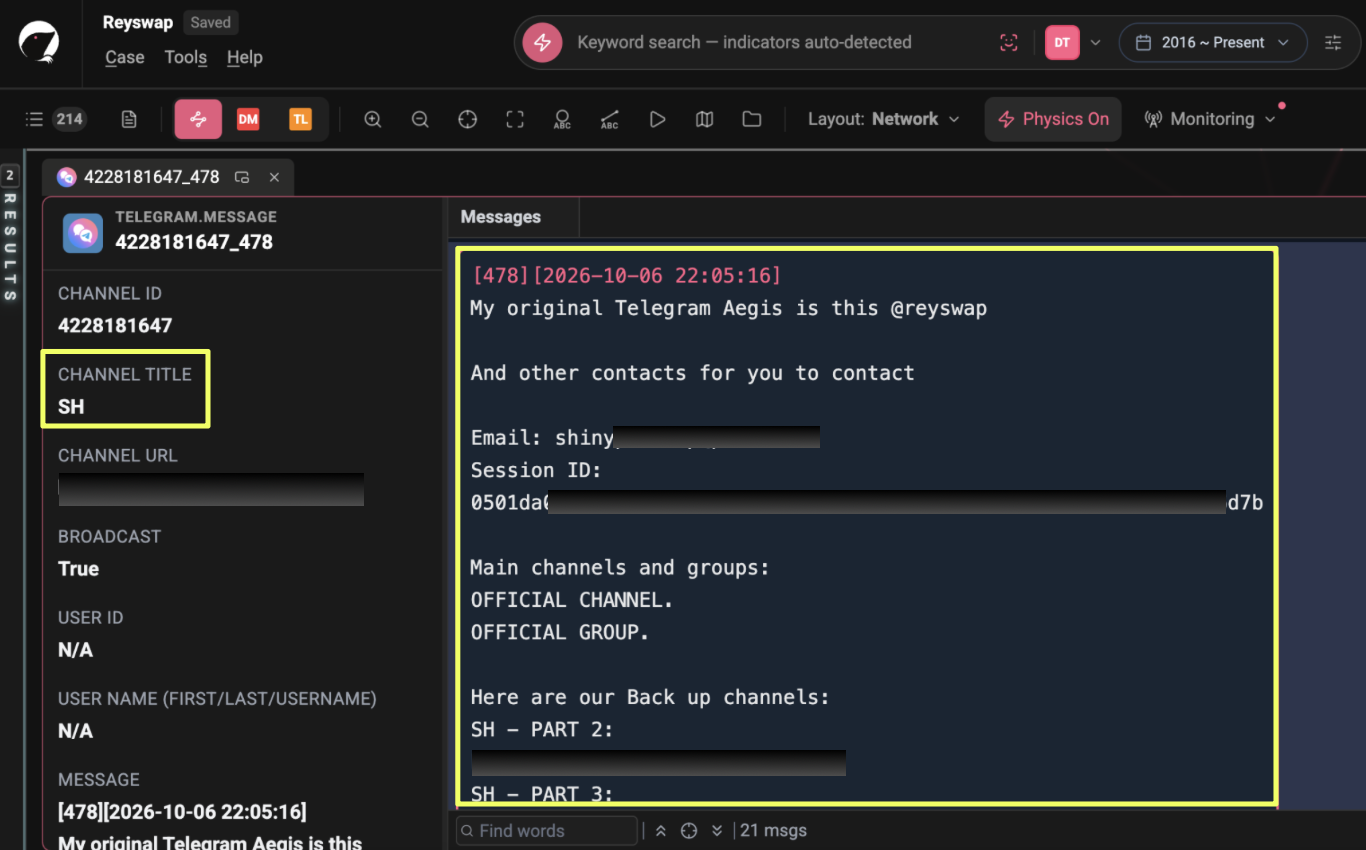
The account creation history provides another useful point of comparison. StealthMole's first snapshot of @egi****a dates to 10 September 2026 at 17:00 UTC, just one minute after @reyswap's first captured message in the Jacuzzi chat. Both accounts therefore appeared in the records within the same minute. This does not prove that they were controlled by the same person, but it places their emergence at almost exactly the same time, well before Aegis was introduced as Rey's successor.
By 10 and 11 October, the account was also discussing the confusion around its identity in BF Chat. Some of its messages suggested that the shifting identities were intentional:
- people will believe that i am the real Aegis, so let people think i am larp haha
- So that the FBI will not believe me and will not arrest me.
- Because Rey said not to use Rey's name, people have believed that Rey was arrested. And I followed Rey's orders because he was the second founder after Adel Yuro was arrested.
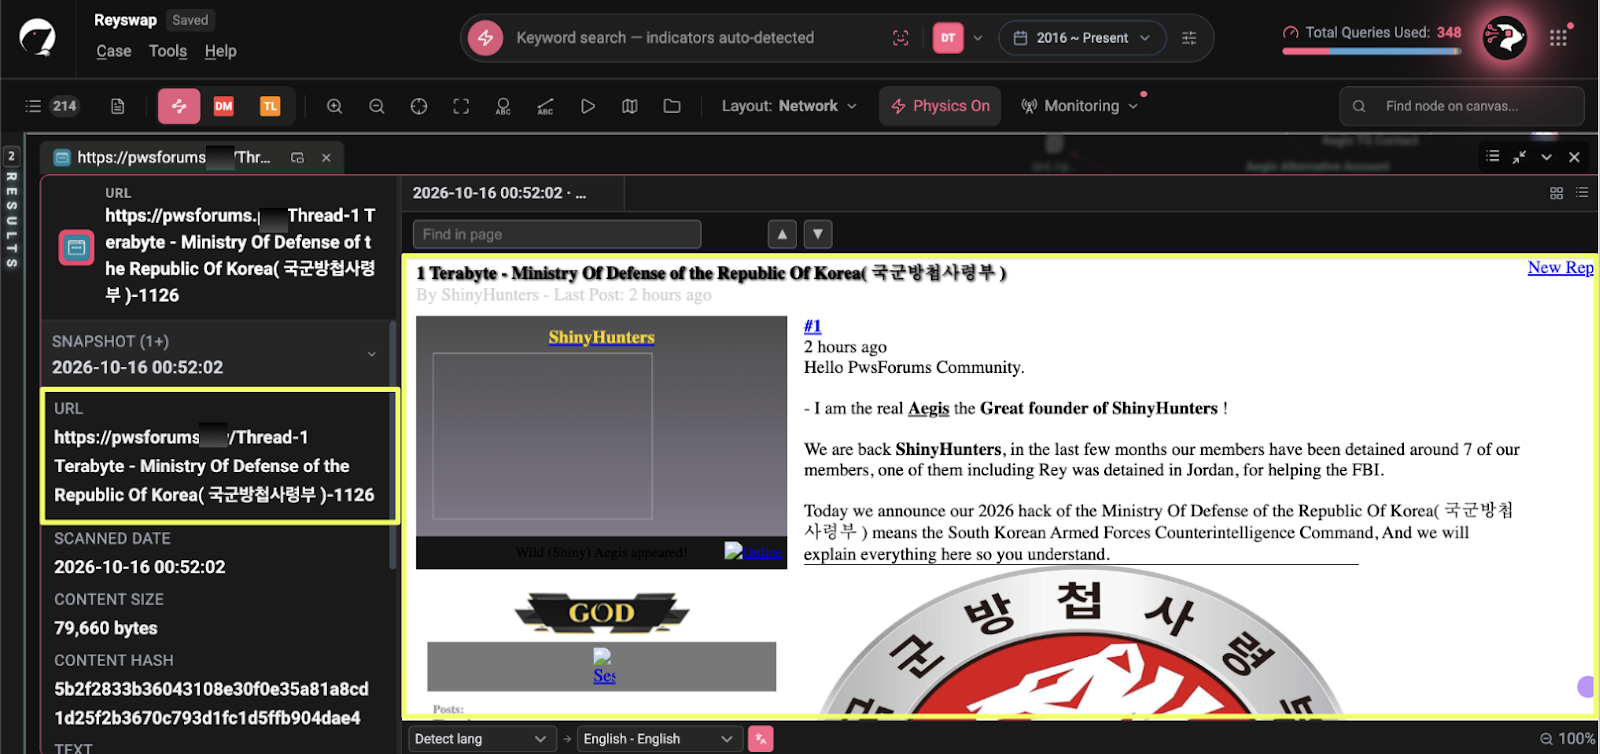
By 16 October, the PwsForums account had adopted Aegis as its main identity. In a thread captured by StealthMole's Dark Web Tracker, the "ShinyHunters" account introduced itself as "the real Aegis the Great founder of ShinyHunters". It also claimed that around seven members had been detained, including Rey in Jordan, "for helping the FBI".
- https://pwsforums.**/**Ministry Of Defense****Korea***6
However, Aegis was not an uncontested identity either. Another account, @aegis******m, was being promoted through the ShinyHunters Official channel, whose posts were signed "aegis". Unlike @egi****a, this account treated @reyswap as a rival rather than an alternate identity.
- Account: @aegis*******m
- Telegram user ID: 8705089196
- Channel: ShinyHunters Official
- Channel ID: 3820821583
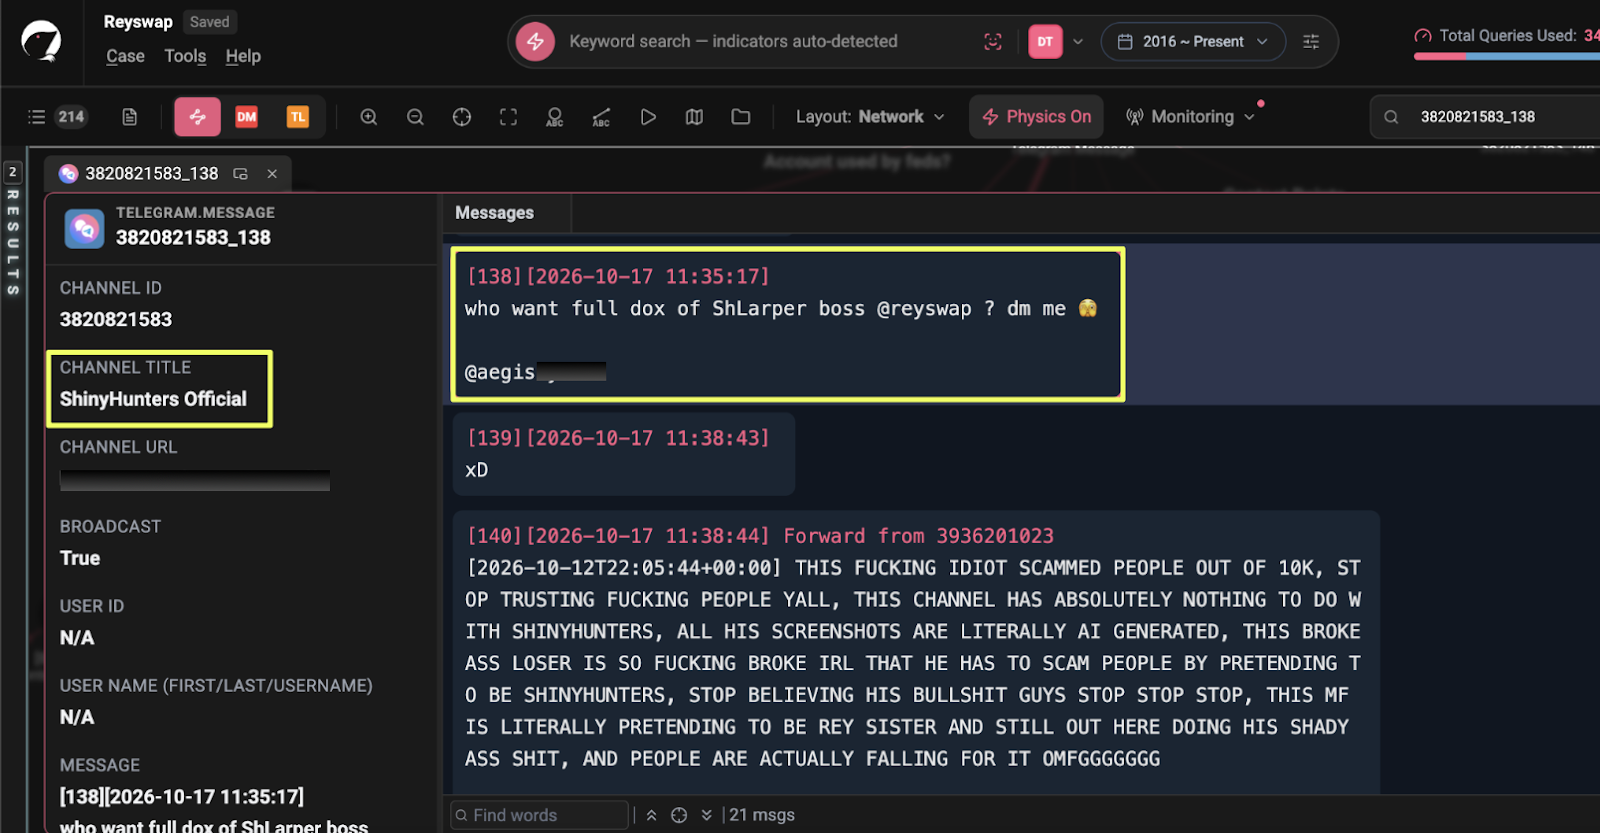
The competing accounts added another layer to the impersonation. @reyswap had initially presented itself as Rey, then claimed to be Aegis while continuing to use the same contact account. At the same time, another account was promoting its own claim to the Aegis identity. The dispute was no longer just about who could speak for Rey or ShinyHunters, but also about who had the right to use the Aegis name.
Rewriting the Story, Week by Week
Following the Aegis statement, the persona continued changing its identity and contact details throughout October. StealthMole's Telegram Tracker snapshots and archived messages make it possible to follow these changes in sequence.
On 6 October, the SH channel removed most of the contact details it had published in its 11 September announcement. Only one of the original email addresses remained.
- Kept: shiny*********@proton.**
- Removed: shiny******@onionmail.com
- Removed: sh1ny*******s@tuta.**
- Removed: shiny****s@xmpp.**
- Removed: shiny******p@onionmail.com
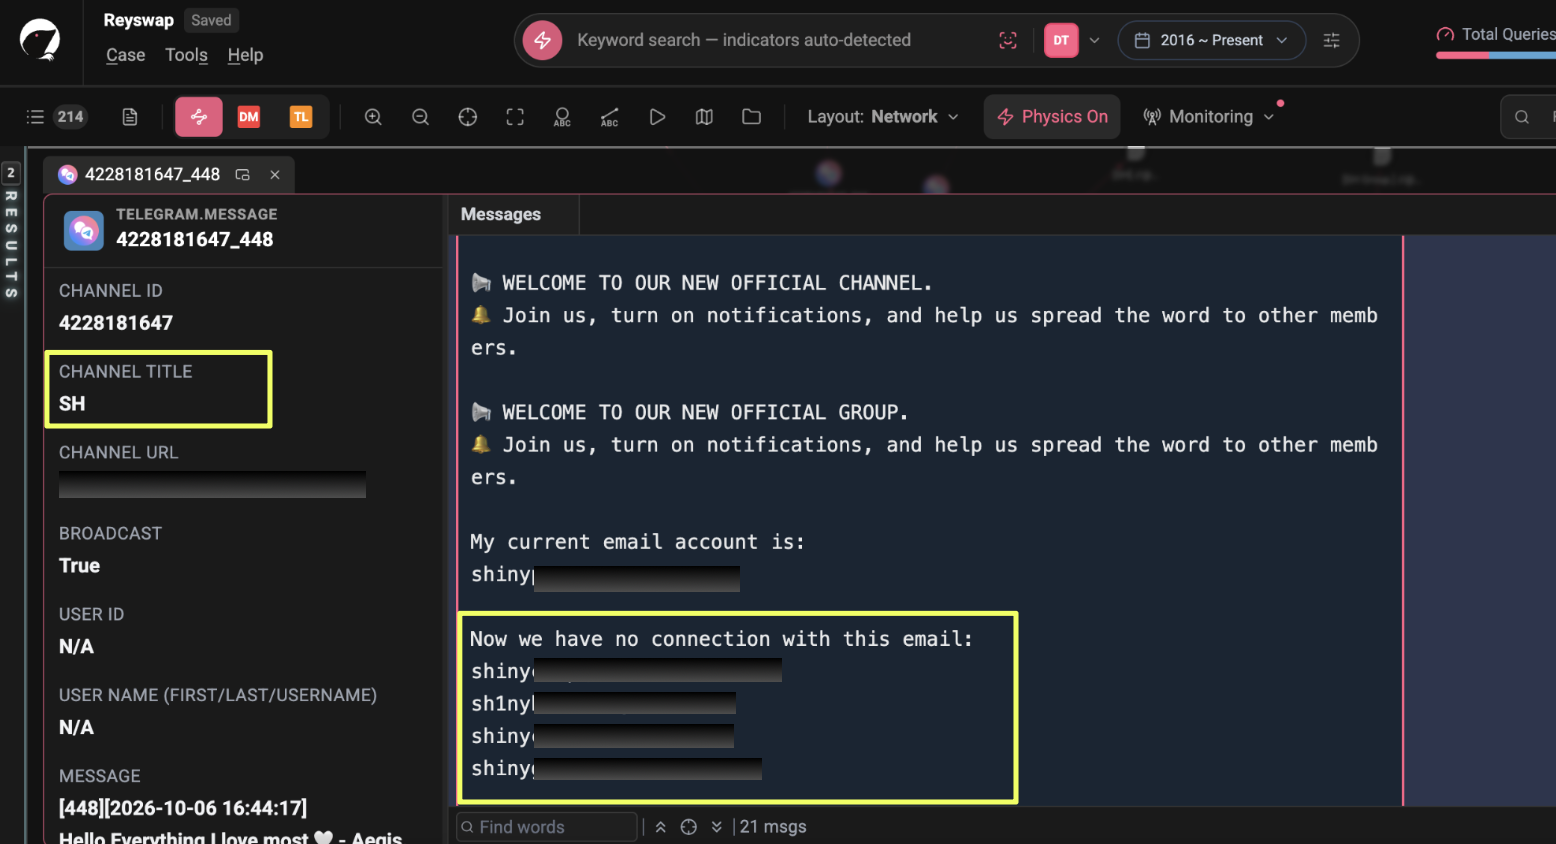
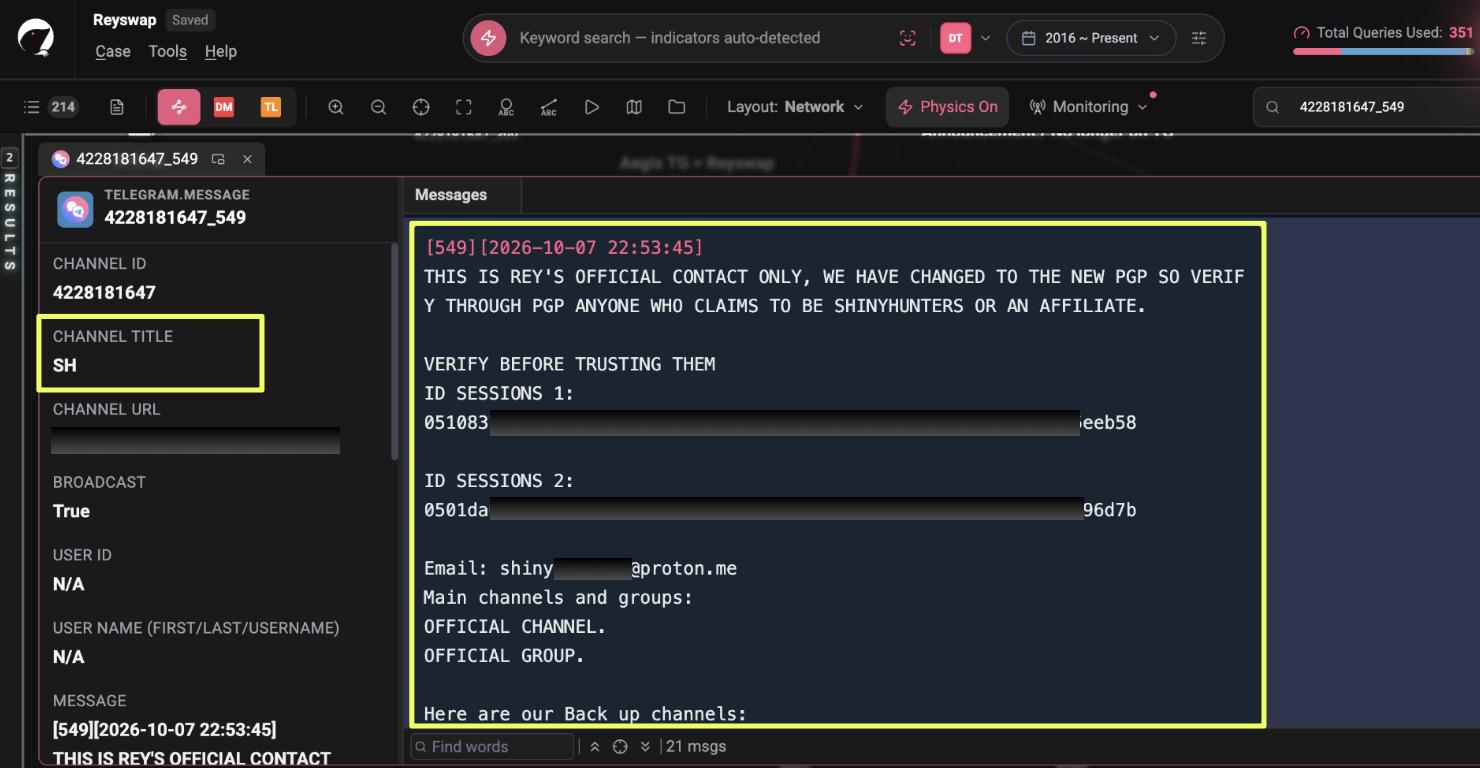
The following day, the channel published a new version of "Rey's official contact" and announced another PGP key. It also listed both Session IDs, but the labels had changed. The Session ID previously identified as belonging to "SLH" was now presented as Rey's.
- ID Sessions 1: 0510837**************************************5eeb58
- ID Sessions 2: 0501d****************************************596d7b
- PGP fingerprint: 80437****************************A78
- Key type: RSA-2048
- Creation date: 7 October 2026
- Email: shiny**********p@proton.me
- Public key: "New Public PGP Key SH 8/10/2026" - https://pastebin.com/J0**q
The most significant change came on 8 October. At 03:58 UTC, the SH channel posted "Hello I'm back Rey @reyswap". Eight hours later, it published a much stronger claim, telling users that its official account was @reyswap and that the account was being used by law enforcement:
- Our official account: https://t.me/reyswap. We inform all our users that this account is being used by feds, to make us disappear from telegram, ruin our name and make it look like Rey was arrested by law enforcement.
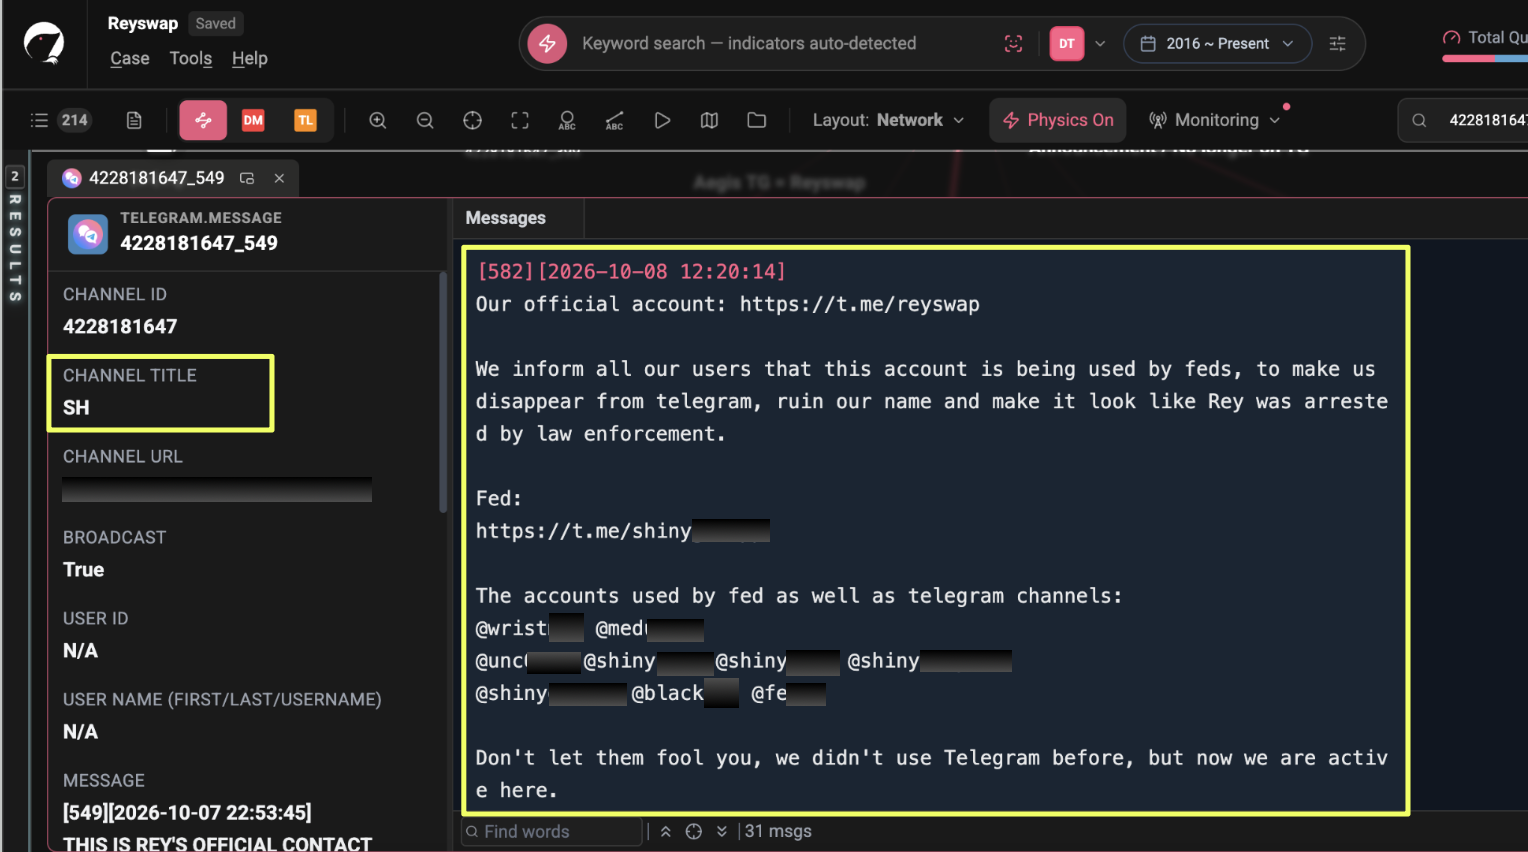
The same message listed several accounts allegedly being used by the "feds":
- @wrist***
- @med***
- @unc****
- @shiny***p
- @shiny****p
- @shiny****s
- @shiny****p
- @black***
- @fe**s
It ended by stating: "we didn't use Telegram before, but now we are active here."
This was a reversal of the position the channel had taken just four days earlier, when it published Aegis's statement confirming Rey's reported arrest in Jordan. It also created a problem with the account list. On 9 October, the SH channel promoted a backup channel called SH - PART 2. Its description listed the founders as:
- @wrist***
- @med***
- @aegis*****m
- @egi****a
- @reyswap
- @unc****0
- @shiny***p
- @shiny***p
- @bar***e
- @shiny****s
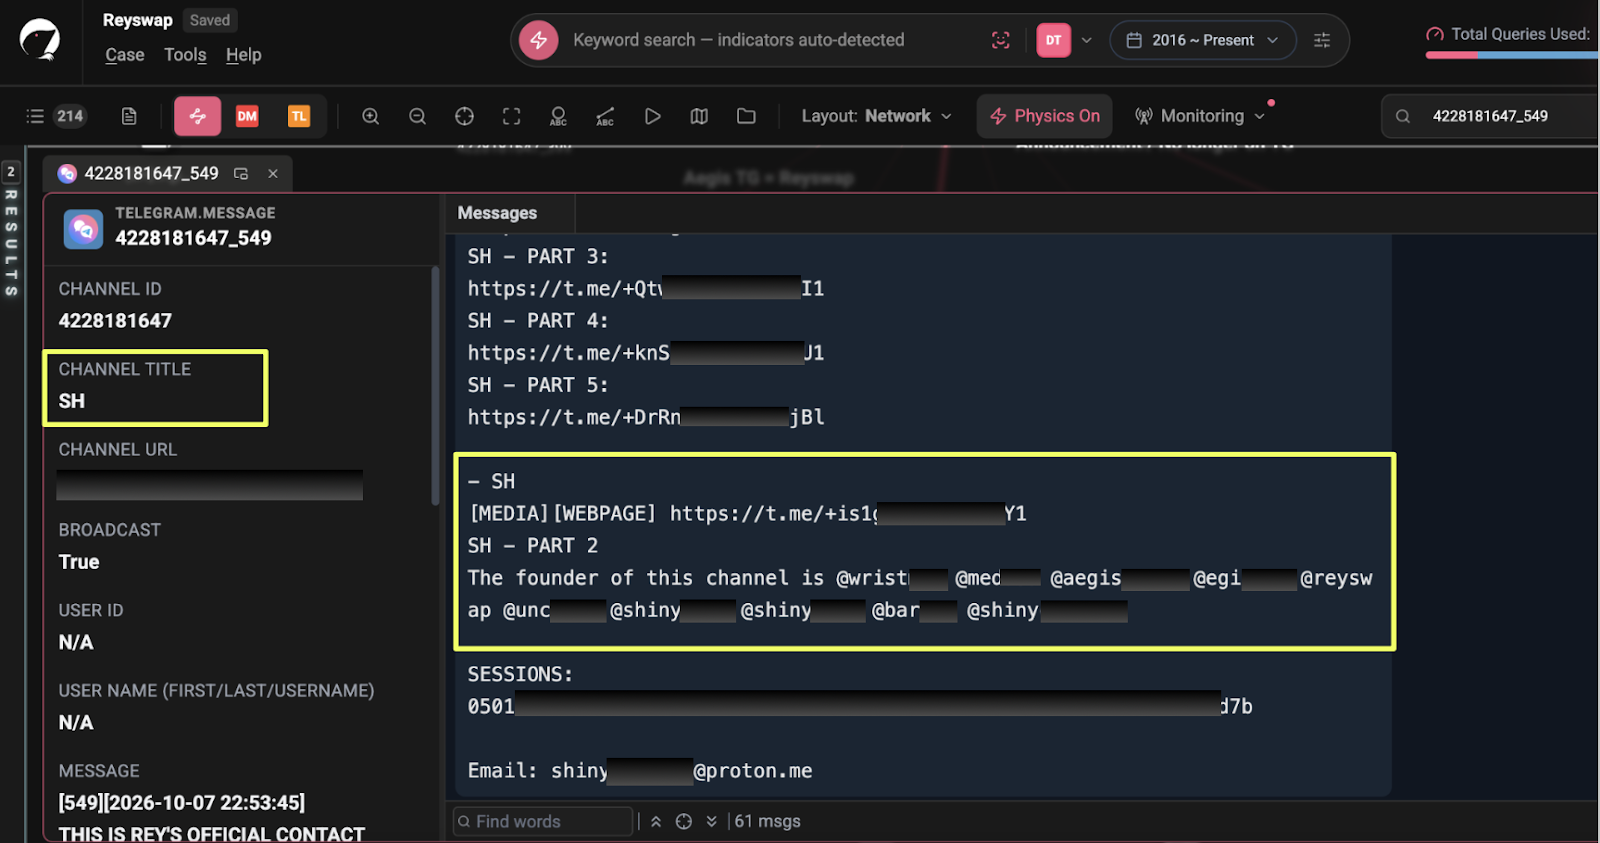
Most of the accounts just described as being controlled by the feds were now presented as part of the operation's own leadership. The list also included @shiny******s, matching the username used in the XMPP contact address published in the original September announcement.
On 9 October, @reyswap added to the confusion through three messages posted in the SH Group within ten seconds:
- I'm not Indian
- I'm in jail now
- I am the real Rey LMFAO
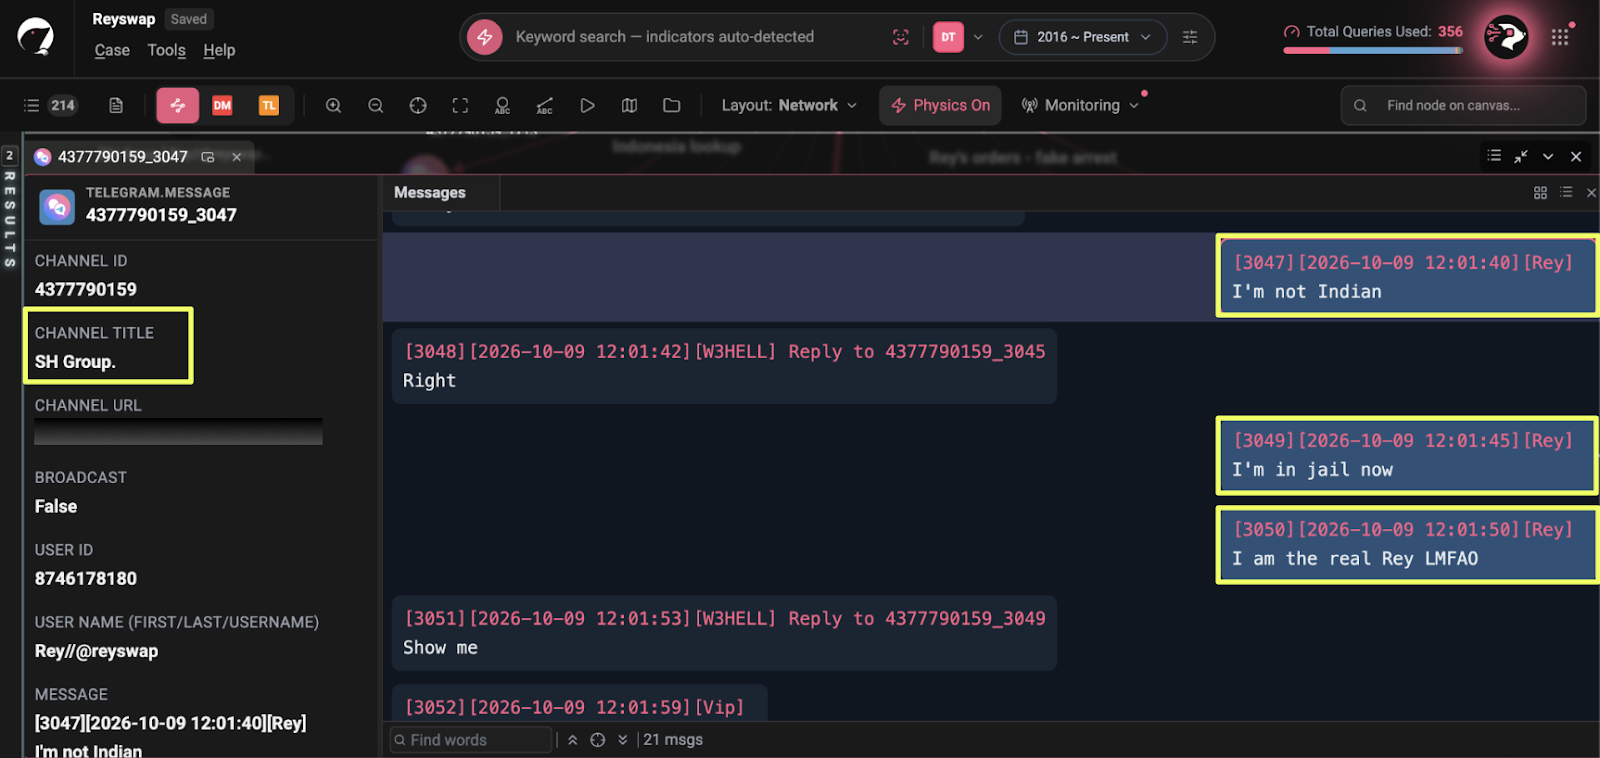
Later that day, the SH channel announced that it would not remain on Telegram much longer, claiming that "several of our members have reportedly been arrested by the FBI". This sat alongside @reyswap's own claim that it was in jail, followed immediately by a declaration that it was the real Rey. The messages did little to clarify who was actually behind the account.
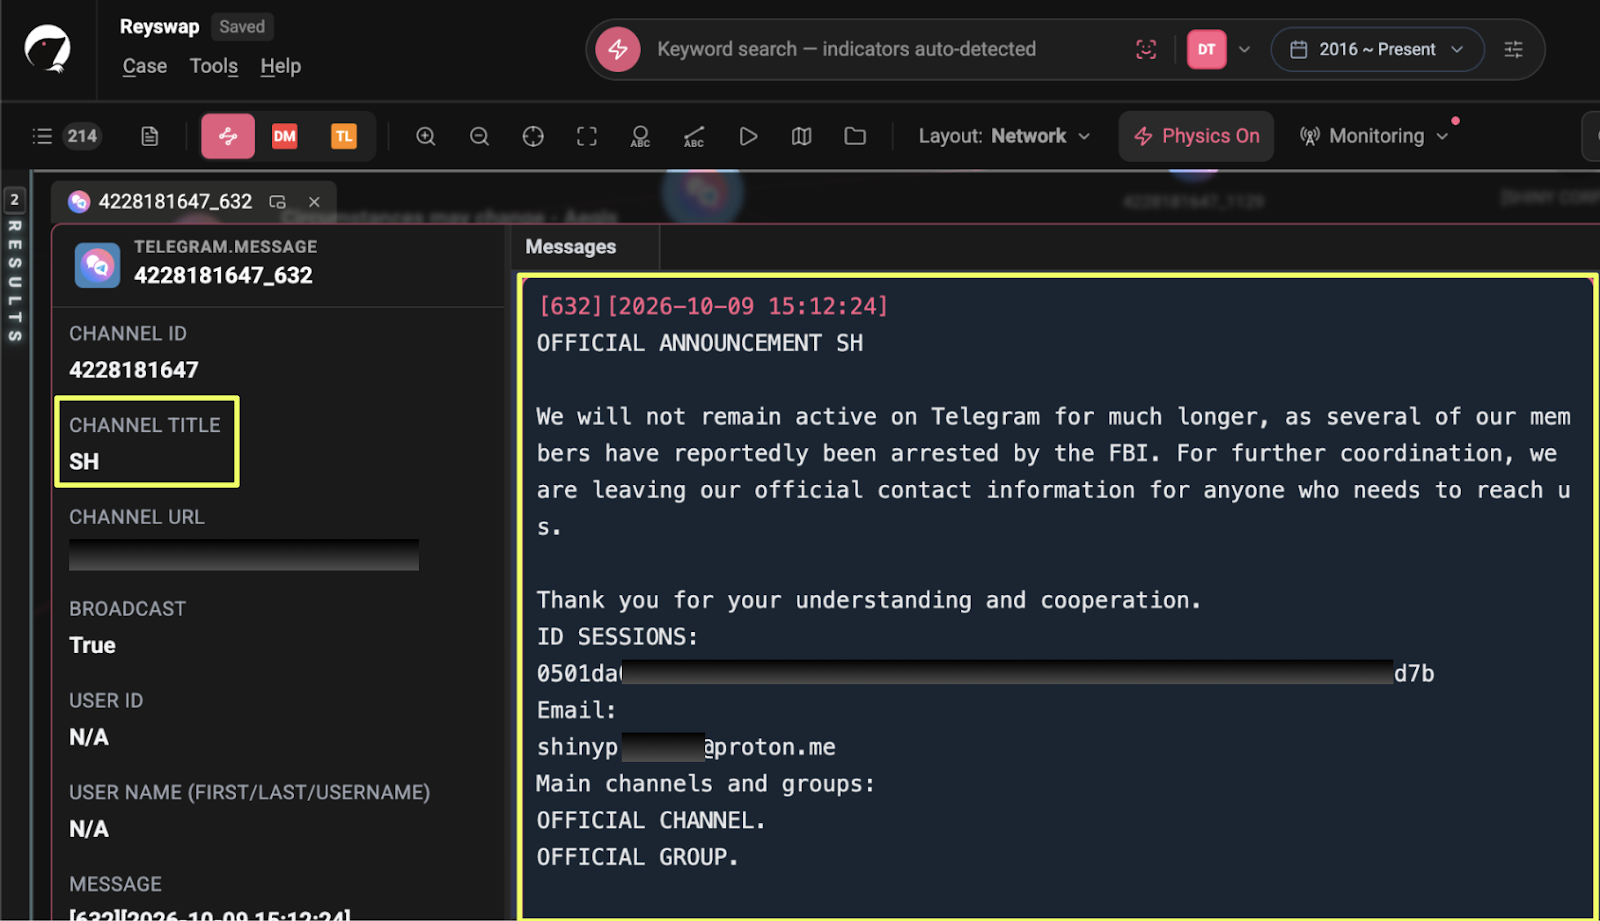
The profile itself also changed during this period. The 9 October snapshot shows that @reyswap had added a profile photo and a bio linking to the new Pastebin PGP key. By 16 October, the display name had changed to ShinyHunters, and the bio included the French phrase "Canal privé".
On 17 October, the SH channel published an "Official Statement — Rey Is Back", stating:
- From this moment forward, I will be using @reyswap as my account. I am Rey myself.
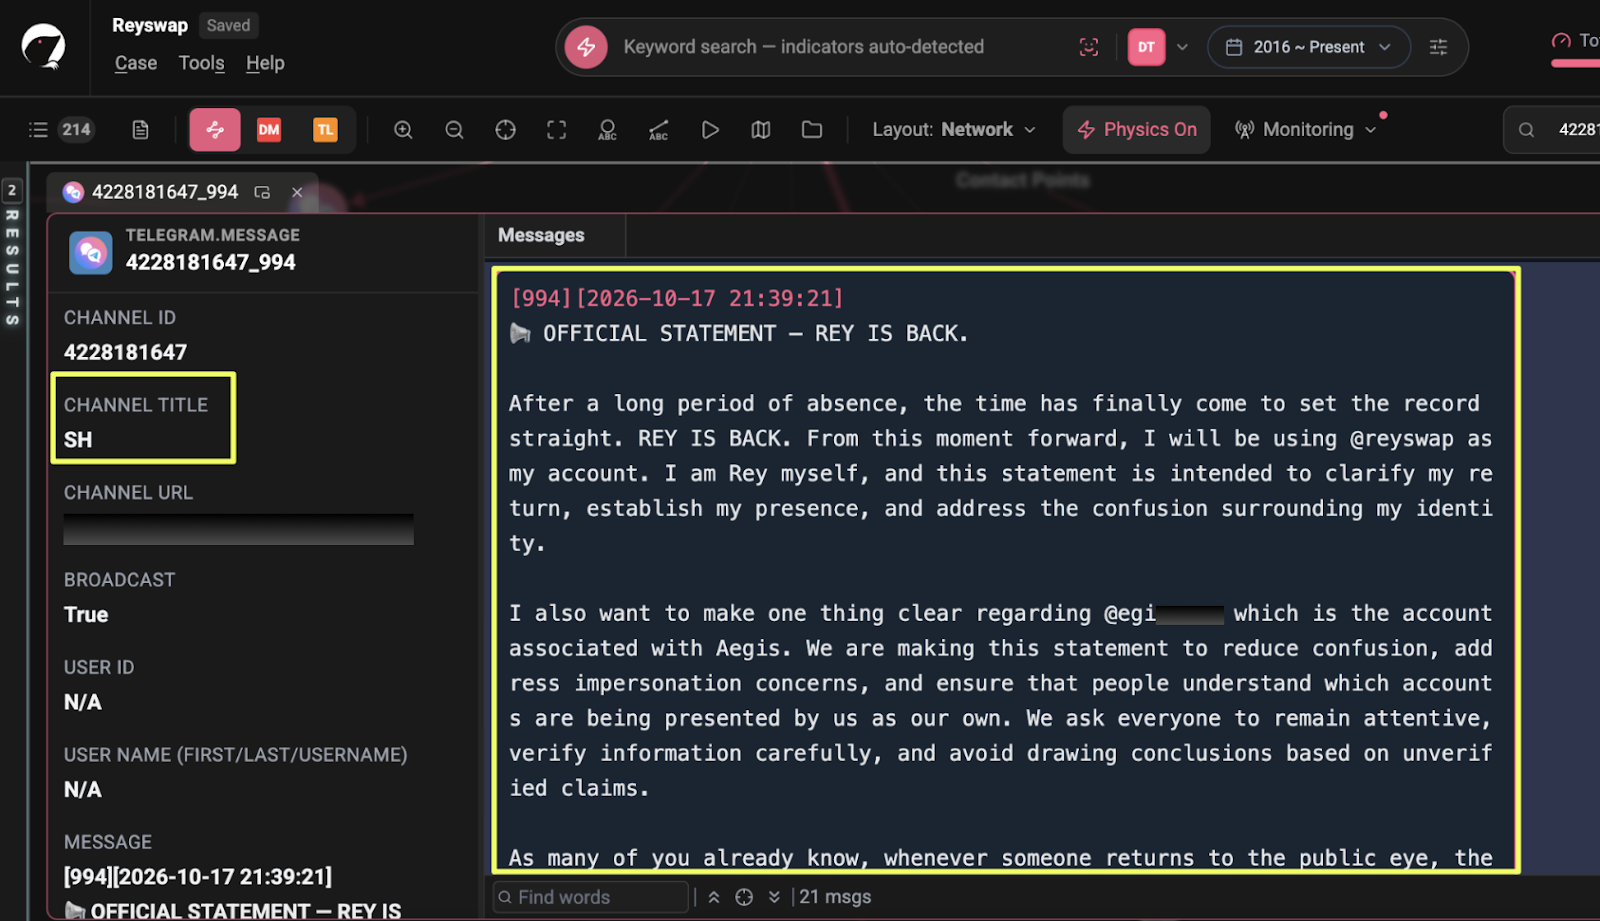
The statement also identified @egi*****a as "the account associated with Aegis". This was the same account introduced on 3 October as Aegis speaking on behalf of an arrested Rey. The channel has now returned to presenting @reyswap as Rey, while keeping the Aegis identity under a separate account.
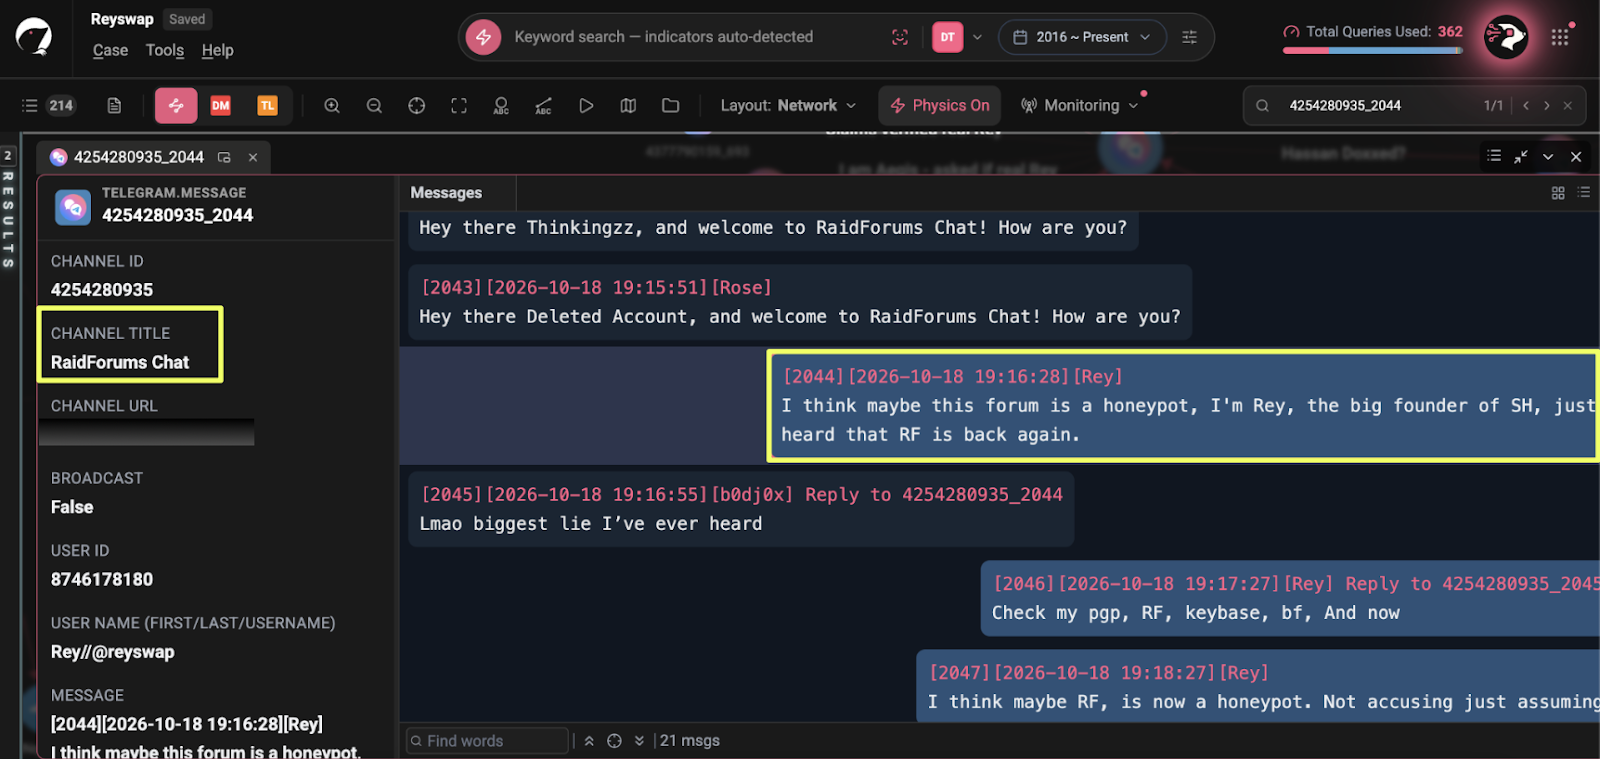
The following day, @reyswap appeared in RaidForums Chat, where it wrote: "I'm Rey, the big founder of SH... Check my pgp, RF, keybase, bf". However, the PGP keys published by this persona during the investigation had all been created in September or October 2026. The message referred to established platforms and verification history, but the account's own published keys did not demonstrate continuity with that earlier activity.
The final rebranding took place on 20 and 21 October, when the SH channel changed its name to SHINY CORP. Its description presented it as a second channel created because the first had been blocked. It also published a three-person line-up:
- Founder: @reyswap
- Partner: @egi***a
- Affiliation: @yukarr*******e
- New contact email: shiny**********7@onionmail.com
- Donation address (XMR): 83VxgpmR******************************cUZj9
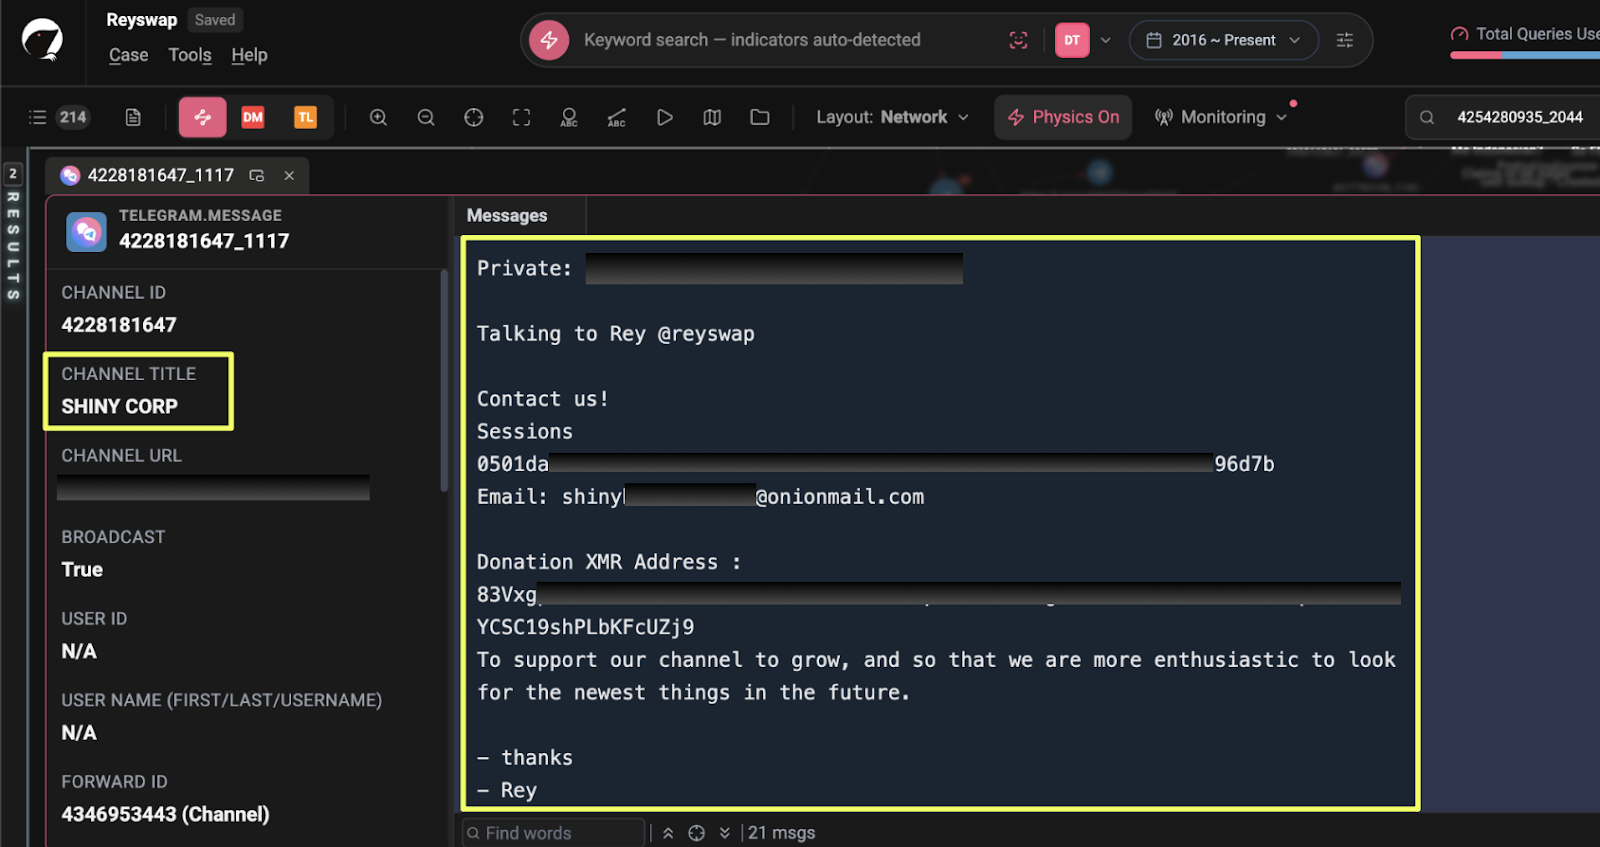
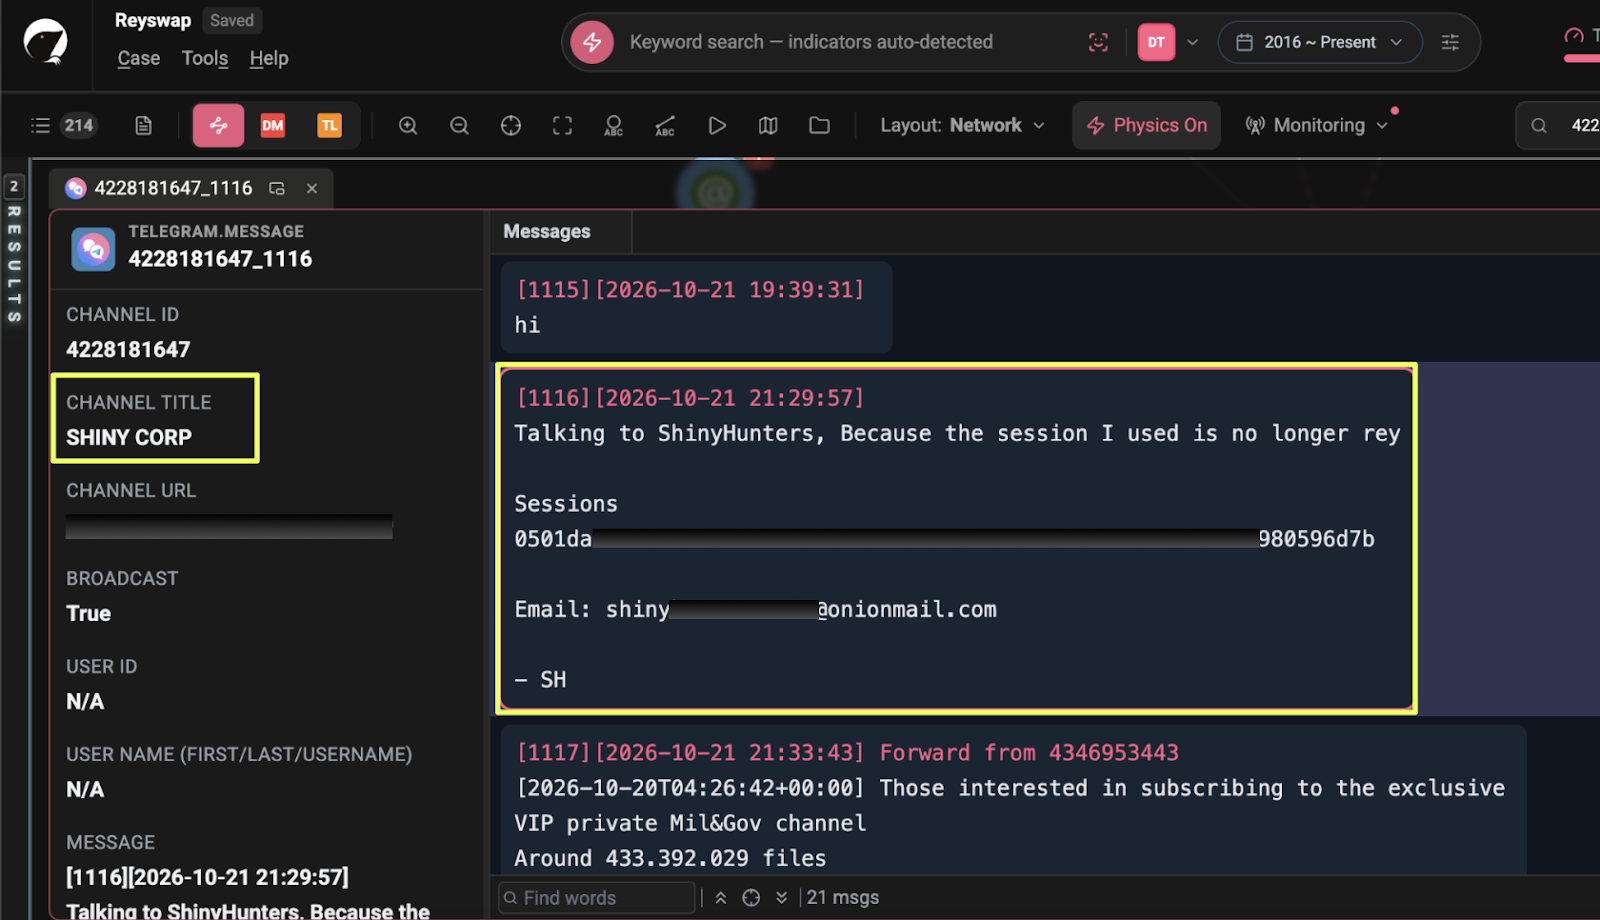
The renamed channel continued publishing "pay or leak" notices naming DexCom, O'Reilly Automotive and Instructure. Its donation request was signed "- Rey". However, a post at 21:29 UTC on 21 October raised another question about the account's identity:
- Talking to ShinyHunters, Because the session I used is no longer rey
The last captured post, dated 22 October, acknowledged that the operation no longer had an onion blog or website and claimed that some members had been arrested. StealthMole's Dark Web Tracker provided a way to check the status of the onion domain previously advertised in the September announcement. It was first scanned on 15 September and was already offline by its last recorded scan on 30 September.
The data-sale activity also raises questions about what the persona was actually offering. A PwsForums listing captured on 12 October, titled "Privacy Data Collection No leaks no public", bundled references to breaches already publicly attributed to ShinyHunters and Scattered LAPSUS$ Hunters. These included Salesforce, PowerSchool, LVMH, Ticketmaster and the FBI jobs portal. The listing directed users to t.me/reyswap as its contact.
- https://pwsforums.**/Thread-Privacy Data****ShinyHunters-1115
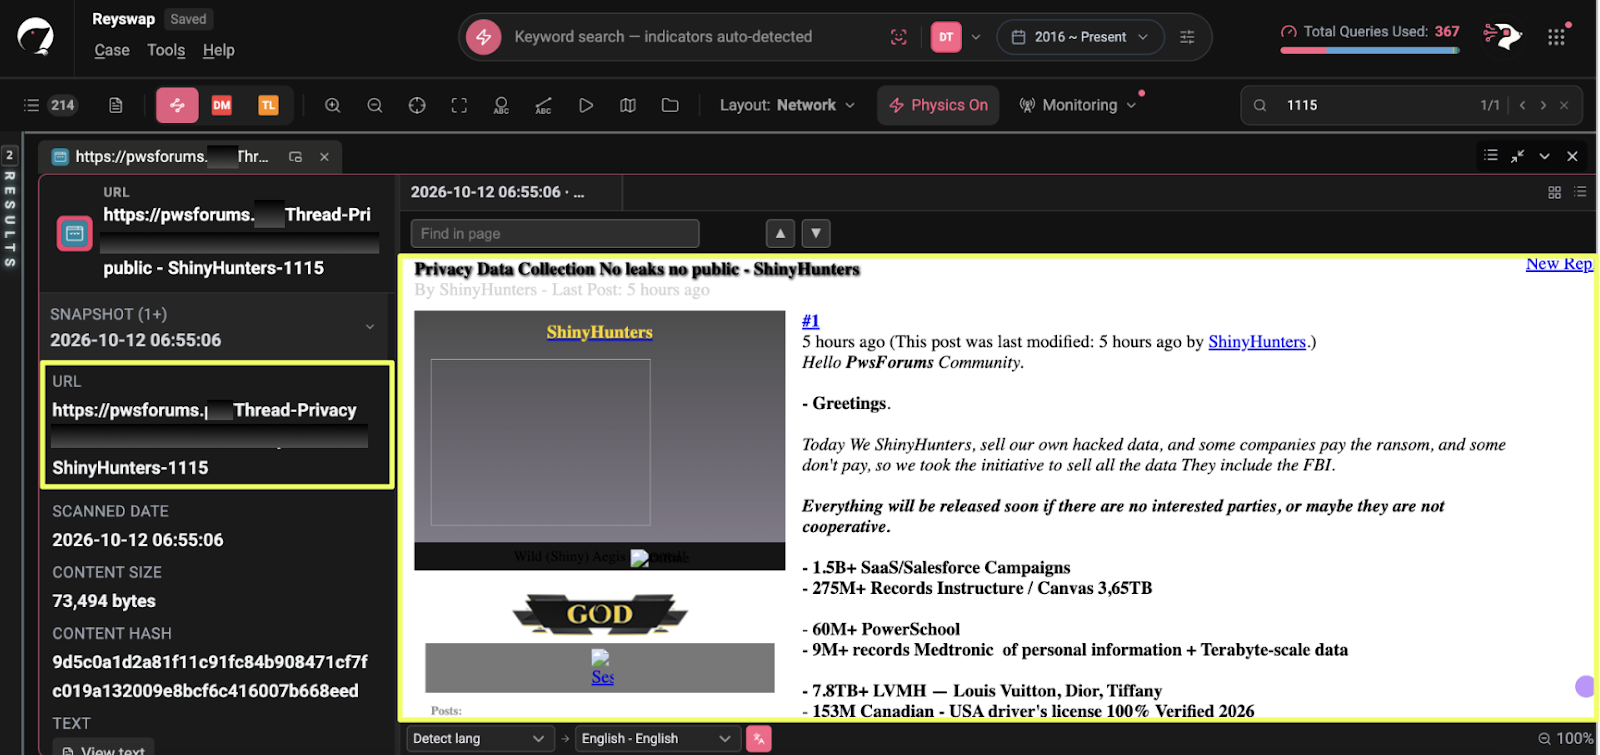
Across October, the account repeatedly changed its name, leadership claims, verification material and contact details. Yet the listings continued to rely on the ShinyHunters name and its previously reported breaches. The available records show a persona using the group's reputation to attract attention and potential buyers, rather than establishing that it had access to the original operators or independently held the data it advertised.
The Underground's Verdict
While the accounts behind the ShinyHunters persona continued changing their story, other members of the underground were already questioning its legitimacy. StealthMole's Telegram Tracker captured these reactions across several chats and channels. The criticism began in September, before Rey's reported detention became public, and continued through October.
- 10–11 September, Jacuzzi: HasanBroker banned @shiny****o, while another member, blewdup, referred to "some fake shiny hunters named shinycorppro".
- 29 September, Data Hoarder: A warning was posted stating, "BE AWARE THIS SCAMMER IS ON A NEW ALIAS LARPING SHINY HUNTERS @reyswap".
- 6 October, BF Chat: A channel operator accused the person behind @reyswap of pretending to be Rey's sister. The operator also claimed that, when asked to send a voice message, the account provided one that was "clearly generated using a translator". The same source accused it of seeking free promotion before carrying out an exit scam.
- 12 October, BF Chat: The same source alleged that the account had scammed people "out of 10K" and that its screenshots were "AI generated".
- 13 October, ShinyEquationCartel: A warning stated, "User @reyswap does NOT possess this database. Any claims made by them are fake."
- 17–18 October, ShinyHunters Official: The channel advertised an offer for a "full dox of ShLarper boss @reyswap". A subsequent post signed "aegis" also listed @reyswap among accounts accused of copying the ShinyHunters name.
- 21 October, PwnForums chat: A moderator banned @reyswap.
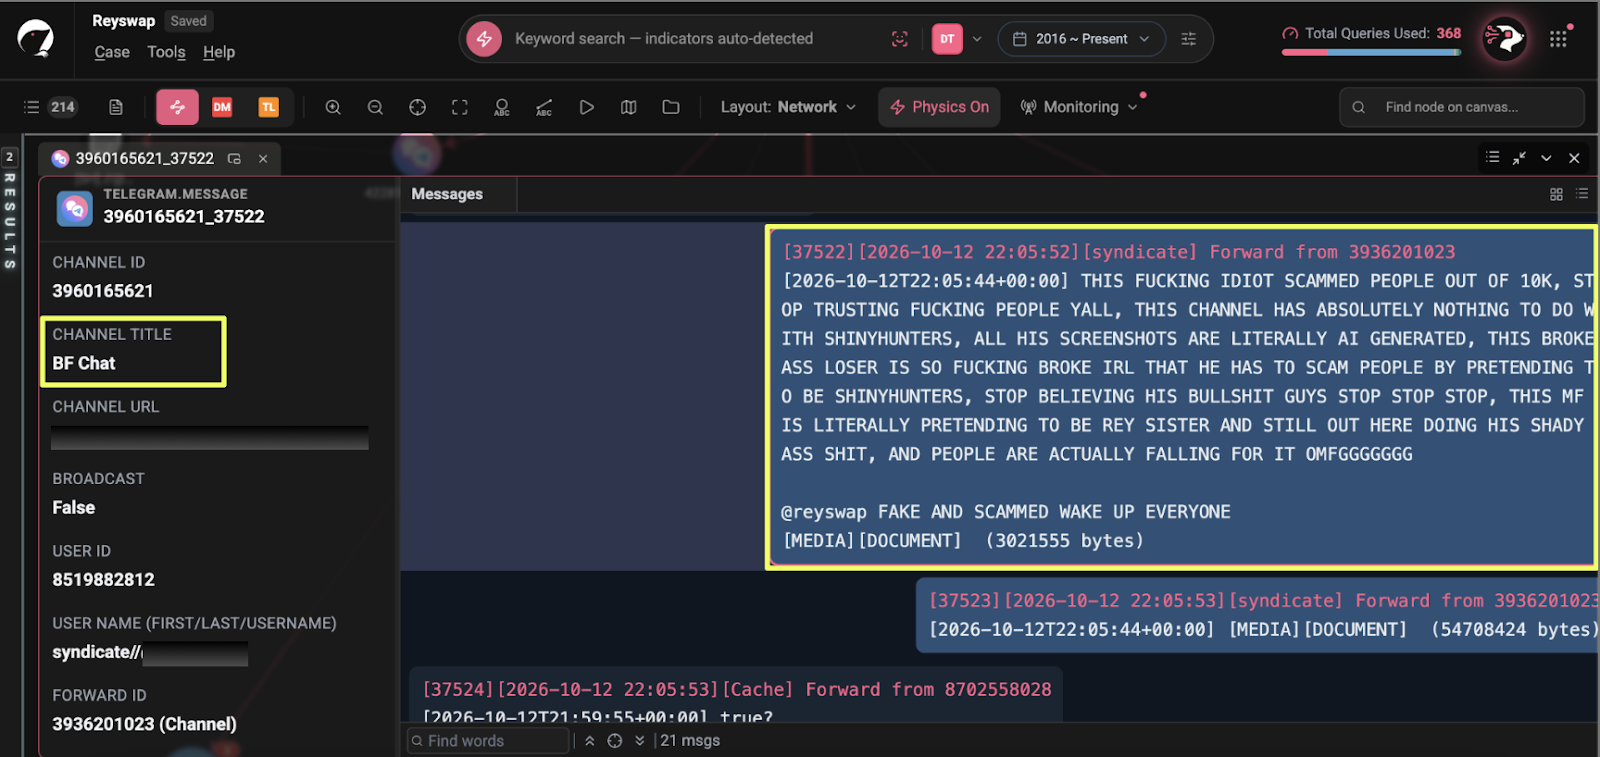
One of the more detailed accusations appeared on 13 October in BF Chat. A user named Jimbzo published a list titled "ShinyLarpers aka fake ShinyHunters", identifying accounts and channels that were allegedly impersonating the group. The list included both channels associated with the persona and provided Telegram IDs and location indicators for two accounts.
- SH Group: Channel ID: 4377790159
- SH: Channel ID: 4228181647
- Rey (Rey): @reyswap, Telegram ID: 8746178180 {ShinyHunters} [IP - Asia, Phone - Indonesia]
- Aegis: @aegi******m, Telegram ID: 8705089196 [IP - Europe]
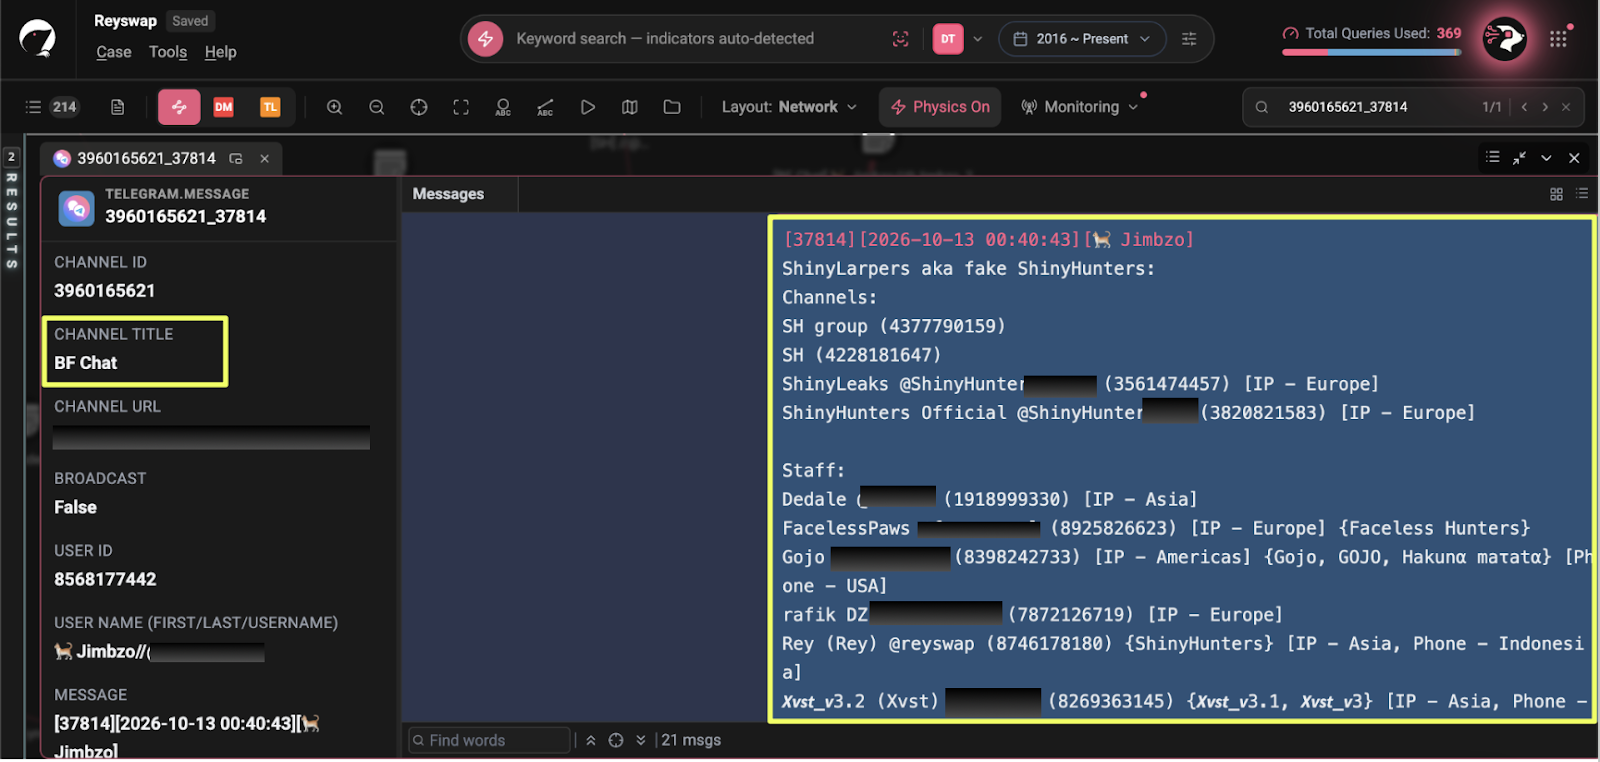
The Indonesia indicator also appeared in the account's own Telegram activity. On 6 October, a BF Chat user called @reyswap Indonesian. The account responded, "What? Me Indonesian?". Minutes later, it forwarded Jimbzo's summary into the SH Group, which included the indicators "app language - indonesia, phone number - indonesia". It then forwarded the result of a Telegram lookup bot showing its app language as Indonesian (id) and indicating that most of its uploads originated in Asia.
These indicators need to be treated carefully. Jimbzo's list and the lookup-bot output are third-party information, not independently verified attribution. They are consistent with each other, but they do not establish the operator's identity or physical location. They also conflict with the 29 September Data Hoarder warning, which described the account as an "Indian scammer".
There is also a connection to earlier reporting outside the StealthMole dataset. Arkem Cyber reported that a rival ShinyHunters voice had described the Telegram side of the brand as an "Indonesian individual" in June 2026. This is notable because the Tuta email address and XMPP contact later used by the @reyswap persona had already appeared in StealthMole's records in a sale post from 13 June. However, the overlap in timing and contact details does not independently establish that both references point to the same operator.
Together, the underground reactions show that @reyswap faced credibility challenges from its earliest days. The account was repeatedly accused of impersonation, making unsupported data claims and attempting to profit from the ShinyHunters name. The available location indicators point towards South-East Asia, but they are not sufficient to identify the person behind the account or establish where it was operated from. They also provide no basis for connecting the operator to Rey's reported detention in Jordan.
Echoes of the 2025 Investigation
The question was whether @reyswap represented a continuation of the operators behind Scattered LAPSUS$ Hunters, or whether it was a separate persona borrowing from the group's history. To examine this, the accounts, contact details and other identifiers recorded during this investigation were compared with the findings from our August 2025 investigation.
The comparison revealed no direct infrastructure overlap. The Session IDs, email addresses and Telegram accounts associated with @reyswap did not match those documented in 2025. However, several names and operating practices from the earlier ShinyHunters ecosystem appeared again in 2026.
The most visible example is the shinycorp name. In 2025, "shinycorp" was the display name used by @slo*****8, an account that defended the original Scattered channels against impersonators. A separate @shinycorp Telegram account had also been declared banned and blacklisted in a notice to BreachForums users in August 2024. The 2026 persona reused the name across several accounts and contact points:
- Telegram account: @shiny*******o
- Email: shiny*****p@onionmail.com
- Email: shinyp******p@proton.me
- XMPP: shiny*******s@xmpp.jp
- Telegram channel: SHINY CORP (ID 4228181647)
Its treatment of the original handle was inconsistent. On 8 October, the SH channel listed @shiny****p among the accounts allegedly being used by the "feds". The following day, its backup channel included the same handle in a list of the operation's founders. The name was being reused, but its claimed role changed depending on the announcement.
The email addresses followed a similar pattern. In 2025, the Shiny infrastructure used shiny****p@tuta.com and shinyhunters*****s@tutamail.com. The 2026 persona introduced sh1nyhunt3rs@tuta.io, briefly listed shiny******p@onionmail.com, and used the associated handles @shiny******p and @shiny*******p. The naming conventions and provider family are similar, but the actual addresses do not match. This is a pattern of reuse, not evidence of shared control.
The Aegis name also predates the 2026 persona. When the Jacuzzi chat was blocked in 2025, a list of replacement "official" spaces included an Aegis announcements feed. The name was therefore already present in the Scattered ecosystem before @reyswap began using it. In 2026, two separate accounts, @egi*****a and @aegi*******m, made competing claims to the Aegis identity. The earlier appearance of the name provides context for its reuse, but does not establish a connection between those accounts and the 2025 operators.
Other names from the earlier investigation appeared around the persona as well. The 2025 report associated the profile behind @isabela*****a with display names that included Hollow, and identified Dedale as a co-manager of the Shiny infrastructure. In October 2026, both names resurfaced. Jimbzo's list of "ShinyLarpers" included Dedale (@d3*****e)among the persona's alleged staff. On 9 October, @reyswap also forwarded a post claiming that arrested members included "Hollow".
The similarities extended beyond names and contact details. Several of the practices associated with the 2025 channels appeared again in the 2026 activity.
- Escrow: In 2025, followers were directed to use Shiny directly for escrow while BreachForums was offline. In 2026, the persona operated an "Escrow BF Important!" channel and told BreachForums users that "we are the ones who will guarantee every transaction that occurs on the forum".
- Selling the forum: In 2025, the Scattered channels advertised a transfer of BreachForums ownership for a fixed fee. On 30 September 2026, @reyswap forwarded a post titled "BreachForums for Sale $2000, domain: bf.st, talk to Rey for negotiation".
- Takedowns as persecution: In 2025, channel bans were presented as censorship and followed by the launch of replacement spaces. The 2026 SH channel similarly blamed "spam reports" for the loss of its previous channel, while SHINY CORP described itself as "the second channel, because the first channel was blocked".
The comparison points to a clear distinction between continuity of infrastructure and continuity of identity. The 2026 persona reused names, contacts and practices associated with the earlier ShinyHunters ecosystem, but the available records do not show the reuse of the accounts, Session IDs or email addresses documented in 2025. Nor do they show the persona verifying its identity through the keys and accounts relied on by the earlier operators.
The similarities therefore show familiarity with the history and operating style of the Scattered LAPSUS$ Hunters ecosystem. On their own, they do not establish that the person behind @reyswap was part of the original operation.
Identifier Map
The table below maps every identifier this investigation tied to the persona to the identity it was used under, with the first and last dates it was observed through StealthMole. All dates are UTC.
Identifier | Type | Used As | First Seen | Last Seen | Notes |
@reyswap (8746178180) | Telegram user | Rey, then Aegis, then ShinyHunters | 10 Sep 2026 | 22 Oct 2026 | Account created September 2026; display name "Rey" until at least 9 Oct, "ShinyHunters" by 16 Oct |
@egi****a (8826582408) | Telegram user | Aegis | 10 Sep 2026 | 21 Oct 2026 | First snapshot one minute after @reyswap's first message; "Partner" in SHINY CORP |
@shiny*** (8845155525) | Telegram user | ShinyHunters "Account Office" | 10 Sep 2026 | 17 Sep 2026 | Banned from Jacuzzi as a fake on 10 Sep |
@yukar***e | Telegram user | "Affiliation" | 21 Oct 2026 | 21 Oct 2026 | Listed in SHINY CORP line-up |
@shin****s | Telegram user | "SH Leader" | 13 Jun 2026 | 13 Jun 2026 | Earliest handle tied to the contact set |
4290154198 (t.me/+Nq****NWNl) | Telegram channel | ShinyHunters | 10 Sep 2026 | 14 Sep 2026 | Signed "shinyreyegis"; published PGP key and contacts |
4228181647 (t.me/+jW*****M9) | Telegram channel | SH, renamed SHINY CORP | 25 Sep 2026 | 22 Oct 2026 | "Founder: @reyswap" |
4377790159 (t.me/+9d*****I1) | Telegram group | SH Group. | 25 Sep 2026 | 10 Oct 2026 | Main discussion group for the persona |
4379305781 (t.me/+ZV******Y1) | Telegram channel | Escrow BF Important! | 13 Sep 2026 | 17 Sep 2026 | "No one owns this except us Databroker aka ShinyHunters" |
0501da0*******9980596d7b | Session ID | ShinyHunters, then Rey | 10 Sep 2026 | 22 Oct 2026 | "No longer rey" on 21 Oct |
0510837*********b5e4f5eeb58 | Telegram user | SH Leader, then "SLH", then Rey | 13 Jun 2026 | 7 Oct 2026 | Relabelled as Rey's on 7 Oct |
shiny*****p@proton.me | ShinyHunters, Aegis, Rey | 11 Sep 2026 | 18 Oct 2026 | Only email kept after 6 Oct; tied to PGP key 80437923… | |
shiny****p@onionmail.com | ShinyHunters | 11 Sep 2026 | 6 Oct 2026 | Dropped 6 Oct | |
sh1ny****s@tuta.io | SH Leader, ShinyHunters | 13 Jun 2026 | 6 Oct 2026 | Dropped 6 Oct | |
shiny***s@xmpp.jp | XMPP | SH Leader, ShinyHunters | 13 Jun 2026 | 6 Oct 2026 | Dropped 6 Oct; @shin***s later called a "fed" account |
shiny***7@onionmail.com | SHINY CORP | 18 Oct 2026 | 22 Oct 2026 | Replaced the proton.me address | |
ShinyHunters | PGP key (ed25519) | ShinyHunters | 9 Sep 2026 | 13 Sep 2026 | Created two days before publication |
80437***********78 | PGP key (RSA-2048) | Rey | 7 Oct 2026 | 9 Oct 2026 | "Rey's official contact" |
pastebin.com/J0****Lq | PGP key | Rey, ShinyHunters | 9 Oct 2026 | 18 Oct 2026 | Linked in @reyswap's bio |
shnyh******j3pljeread.onion | Onion site | ShinyHunters | 15 Sep 2026 | 30 Sep 2026 | Offline by 30 Sep |
ShinyHunters (PwsForums) | Forum account | Rey, then Aegis | 1 Oct 2026 | 16 Oct 2026 | "Account Office: @reyswap" |
83Vx********bKFcUZj9 | XMR address | Rey | 20 Oct 2026 | 21 Oct 2026 | Donation request signed "- Rey" |
Operational Assessment
The central question is whether @reyswap was Rey himself, an account taken over after his reported arrest, or a separate persona using his identity. The evidence collected during this investigation supports the third explanation.
1. @reyswap was Rey's own account
The available records do not support this. The account was created in September 2026, while Rey's documented activity on Telegram and underground forums dates back to at least 2024. During its first week of activity, @reyswap claimed that it had never used Telegram before. This conflicts with the established Telegram history associated with Rey. The account also failed to demonstrate continuity through its verification material. None of the PGP keys it published predated 9 September 2026, and although it referred users to Rey's archived RaidForums key, it never produced a signature using that key.
2. @reyswap was taken over after Rey's arrest
This explanation is also unsupported. There is no evidence that Rey ever controlled the account, which would be necessary to establish a takeover. The activity recorded around 29 September shows no visible change in control: the same account continued posting, promoting its channels and directing users to the same contacts. Its claim that the account was being used by the "feds" appeared four days after the channel itself had announced Rey's reported arrest. The explanation was further undermined when the same operation listed several of its alleged "fed" accounts among its own founders.
3. @reyswap was an impersonation persona built around an existing cluster
This explanation is the most consistent with the evidence.
- The contact infrastructure predates the Rey persona. The Tuta email address, XMPP contact and one of the Session IDs were already in use in June 2026 under the handle @shin******s, months before @reyswap first appeared.
- The Rey and Aegis identities were introduced together. The signature "shinyreyegis" and the PGP filename combined all three names in the September announcement, before the later claims about Rey's arrest and Aegis taking over.
- The accounts emerged almost simultaneously. StealthMole's first snapshots of @reyswap and @egis*****a were recorded within the same minute on 10 September. The accounts were later presented as alternate identities, with @reyswap claiming both names.
- The identity changed in response to scrutiny. Across October, the persona moved between claiming that Rey had been arrested, that the arrest was fabricated by the "feds", that Rey had returned, and that the account was now being used by Aegis. These explanations were not consistent with one another.
- The location indicators do not support the Jordan narrative. Third-party lookup results associated the account with Indonesia and Asia. These indicators are not independently verified and cannot establish the operator's location, but they provide no support for the claim that the account was being operated by Rey from Jordan.
The evidence strongly supports the assessment that @reyswap was impersonating Rey from the time it first appeared, rather than being an account compromised or taken over after his reported arrest. The account's close association with @egi*****a, @shiny*****o and the ShinyHunters, SH and SHINY CORP channels suggests a common operating cluster. However, the available records do not establish whether this cluster was controlled by one person or several individuals.
The activity also provides a clearer picture of what the persona was trying to achieve. Its posts repeatedly promoted ways to make money from the ShinyHunters name: data listings priced from a few thousand to hundreds of thousands of dollars. The available evidence therefore points to an operation seeking to monetise the group's reputation, rather than demonstrating independent access to the original operators or the data being advertised.
The comparison with the 2025 investigation also reinforces an important point: using the ShinyHunters name is not proof of affiliation. A newly created Telegram account, a fresh PGP key or a forum profile carrying the group's branding cannot establish continuity with its earlier operators. That requires verification against historical accounts and independently archived artifacts. In this case, despite repeatedly referring to the group's history, @reyswap never provided that continuity.
Conclusion
Rey's reported detention in Jordan did not end the use of his name. By the time the news emerged on 29 September, an account presenting itself as Rey had already been active for weeks, promoting a ShinyHunters operation and using contact details that appeared in earlier records from June 2026. The investigation traced how that account continued operating after the arrest, while repeatedly changing the identity it claimed to represent.
Over the following weeks, @reyswap presented itself as Rey, then Aegis, then Rey again. It claimed that the arrest was genuine, later described it as a law enforcement fabrication, and at different points said it was in jail or that its Session account was no longer associated with Rey. These were not simply changes in presentation. They were conflicting explanations from the same account, including messages that openly acknowledged the impersonation. Yet none of the collected records established a link between @reyswap and the original Rey.
The comparison with our August 2025 investigation into Scattered LAPSUS$ Hunters adds another dimension. The 2026 persona reused names, contacts and operating practices associated with the earlier ShinyHunters ecosystem, but the infrastructure did not establish continuity with the accounts and verification material documented in 2025. The distinction matters: familiarity with a group's history is not proof of membership, and using its name does not establish ownership of its identity.
The evidence therefore points to an impersonation operation that used the attention surrounding Rey's arrest to promote its own channels, listings and services. Who operated the accounts remains unresolved, but the available records do not support the claim that @reyswap was Rey or that it was taken over from him after his detention.
Editorial Note
Dark web investigations rarely provide a complete picture. Accounts change names, channels disappear, and claims made by underground actors are often difficult to verify. In this case, StealthMole's historical Telegram snapshots, message records and Dark Web Tracker captures helped reconstruct the sequence of events and compare the persona's claims against its earlier activity. The findings reflect the evidence available at the time of writing; attribution remains subject to revision if further information emerges.
To access the unmasked report or full details, please reach out to us separately.
Contact us: support@stealthmole.com
Labels: Featured, Threat Actor


